← Back to Blog

Cybersecurity

Vulnerability Management and Attack Surface Management: Two Views, One Program

Vulnerability Management and Attack Surface Management: Two Views, One Program

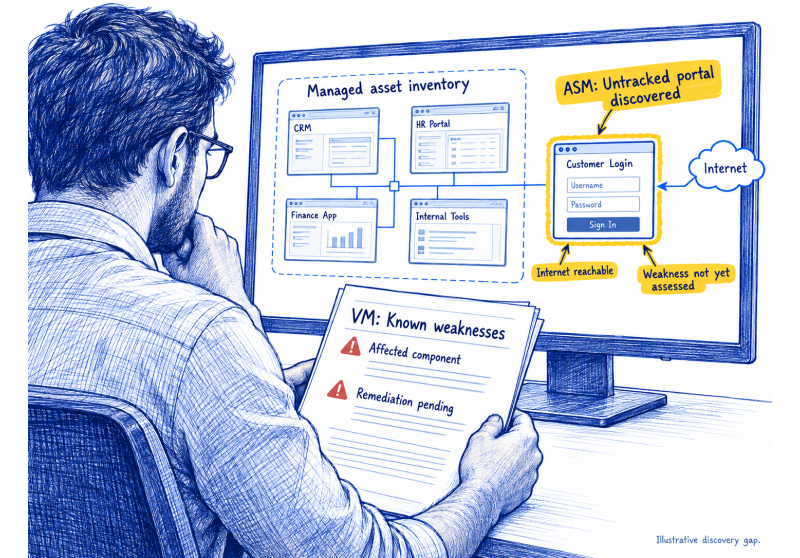
Vulnerability management confirms and treats known weaknesses; attack surface management shows where reachable assets and paths exist. Connect them to make exposure priorities actionable and verify that treatment worked. Vulnerability...

Categories: Cybersecurity, Exposure Management
Cybersecurity Control Impact Analysis: Find Control Failures Before They Spread

Cybersecurity Control Impact Analysis: Find Control Failures Before They Spread

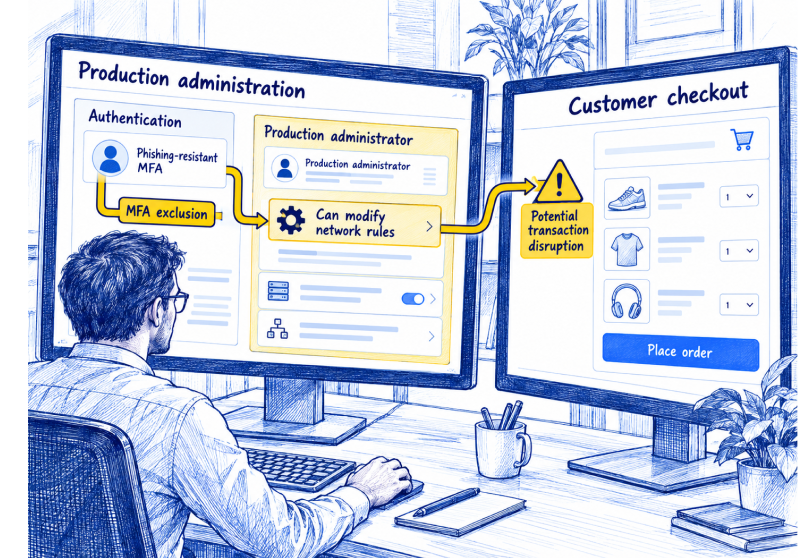
Understand what a weakened control exposes, which operations depend on it and how to verify that corrective action has restored protection. Cybersecurity control impact analysis traces a failed or weakened...

Categories: Cybersecurity, Risk Management
Data Breach Prevention: Build Controls That Protect Data Before Attackers Arrive

Data Breach Prevention: Build Controls That Protect Data Before Attackers Arrive

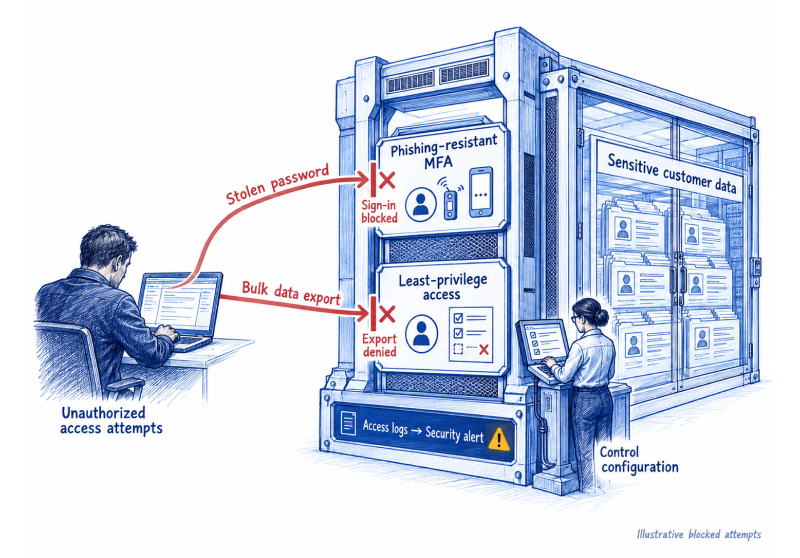
A practical guide to reducing the paths attackers can use to reach sensitive information.Build prevention around data, identity, and access decisions your teams can verify, not a checklist that looks...

Categories: Compliance, Cyber Risk, Cybersecurity
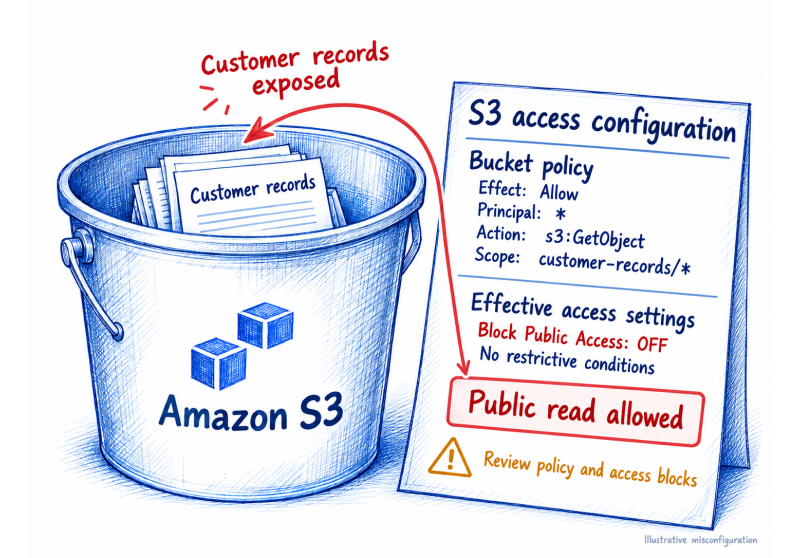
AWS Security Best Practices: Secure Multi-Account AWS Workloads With Guardrails

AWS Security Best Practices: Secure Multi-Account AWS Workloads With Guardrails

A practical guide to account boundaries, identity, guardrails, and operations in AWS.Build a secure foundation that lets workload teams move without relying on every account owner to remember every control....

Categories: Cloud Security, Cybersecurity, Risk Management
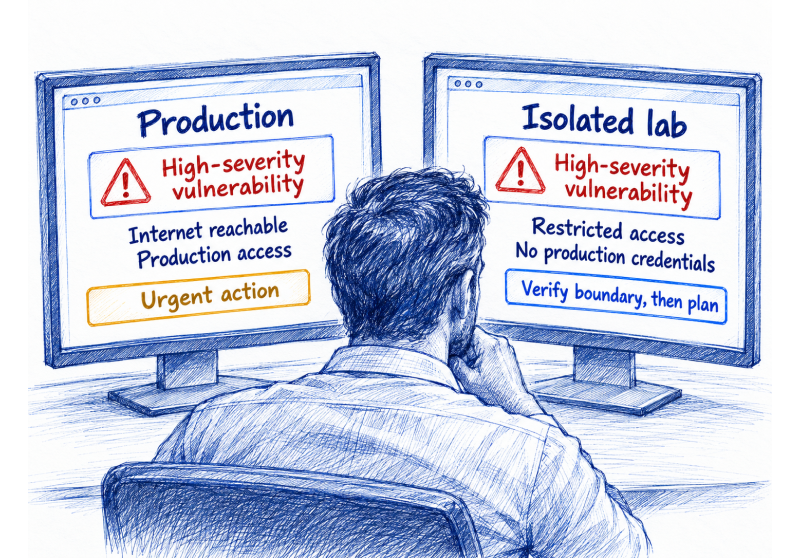
Risk-Based Vulnerability Management: Prioritize Exposure Beyond Scores

Risk-Based Vulnerability Management: Prioritize Exposure Beyond Scores

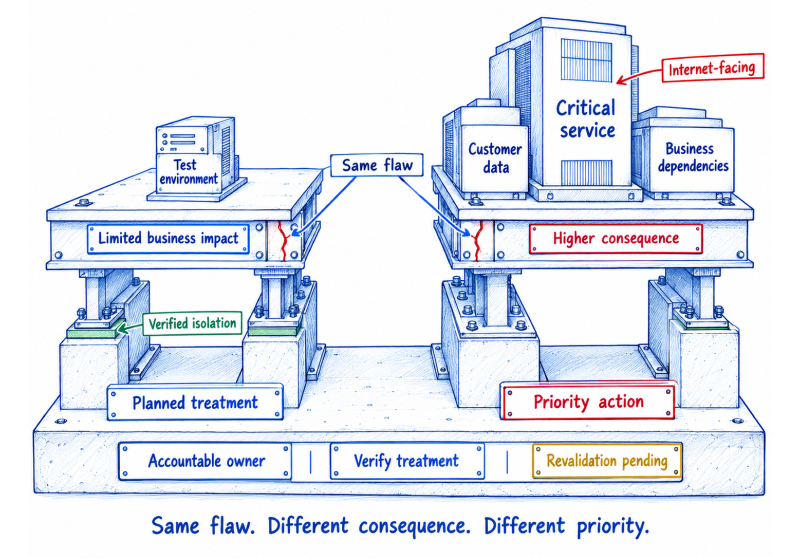
A practical guide for security and IT leaders deciding what to fix first.Use exploit evidence, real exposure, and business impact to create a defensible remediation queue. The backlog is a...

Categories: Cybersecurity, Risk Management
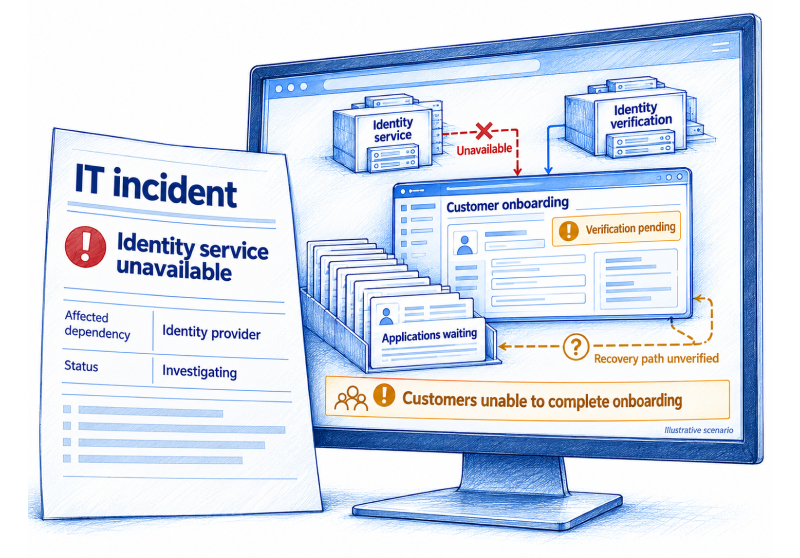
IT Risk Management in 2026: Connect Dependencies to Business Impact

IT Risk Management in 2026: Connect Dependencies to Business Impact

A practical guide for security, IT, and GRC leaders to identify concentration risk and improve portfolio decisions. IT risk management is harder to see when technology spans cloud platforms, vendors,...

Categories: Cybersecurity, Risk Management
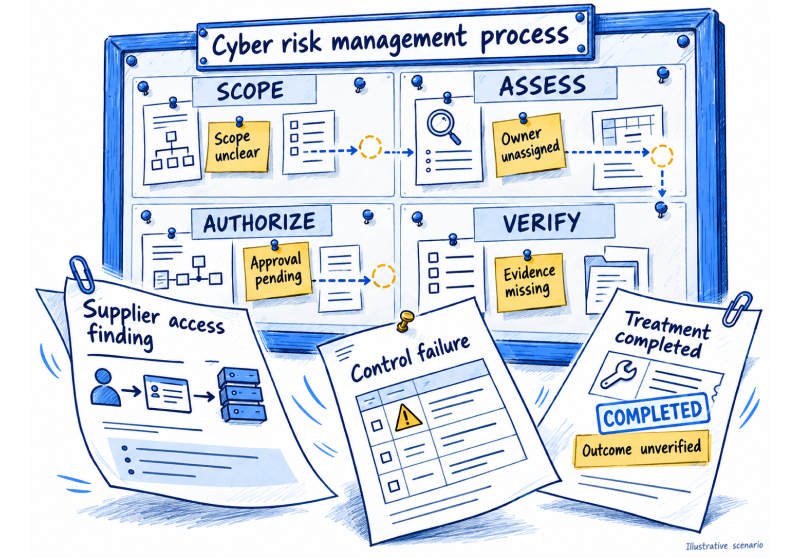
Cybersecurity Risk Management Process: A Practical Guide to Decisions

Cybersecurity Risk Management Process: A Practical Guide to Decisions

A cybersecurity risk management process should move from a defined business question to a decision, funded action, and evidence that the response worked.This guide gives security and GRC leaders a...

Categories: Cybersecurity, Risk Management
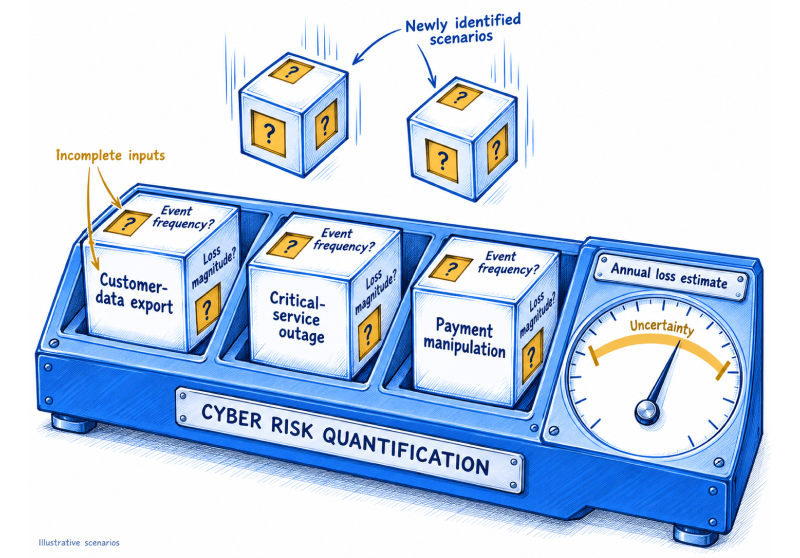
Quantitative Cyber Risk Analysis: Put Loss Ranges to Work in Security Decisions

Quantitative Cyber Risk Analysis: Put Loss Ranges to Work in Security Decisions

Quantitative cyber risk analysis can help leaders compare security choices, but a precise-looking number is only as sound as its scenario and inputs. This guide shows how to model loss...

Categories: Cybersecurity, Risk Management
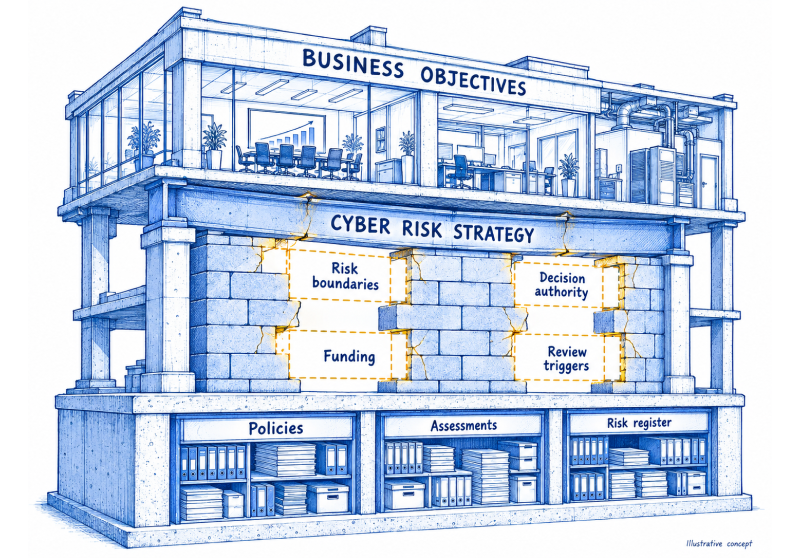
Cybersecurity Risk Management Strategy: Define Priorities, Authority and Limits

Cybersecurity Risk Management Strategy: Define Priorities, Authority and Limits

A cybersecurity risk management strategy should guide real choices about priorities, investment and acceptable exposure. This practical framework connects business objectives to decision authority, treatment and review. A cybersecurity risk...

Categories: Cybersecurity, Risk Management
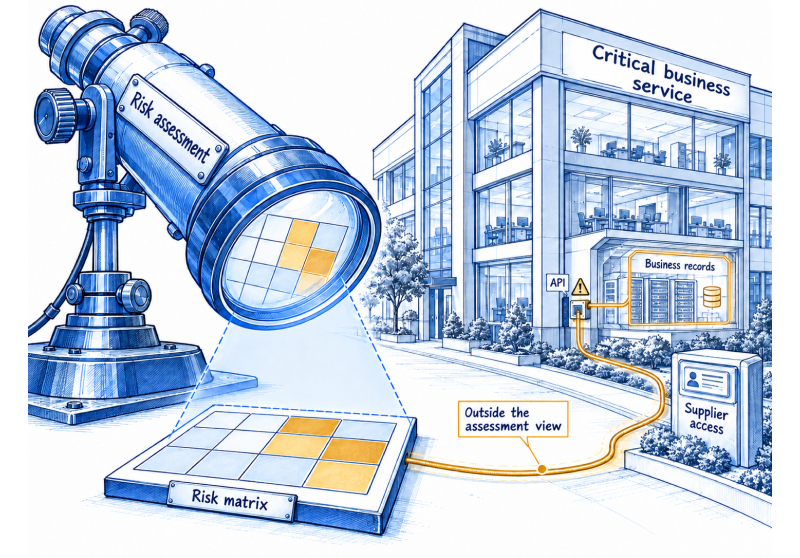
Cybersecurity Risk Management Techniques: Choose the Right Method

Cybersecurity Risk Management Techniques: Choose the Right Method

Different risk questions need different methods. Compare practical techniques, see how two methods reach different decisions on the same supplier scenario, and choose an approach that fits the evidence and...

Categories: Cybersecurity, GRC, Risk Management
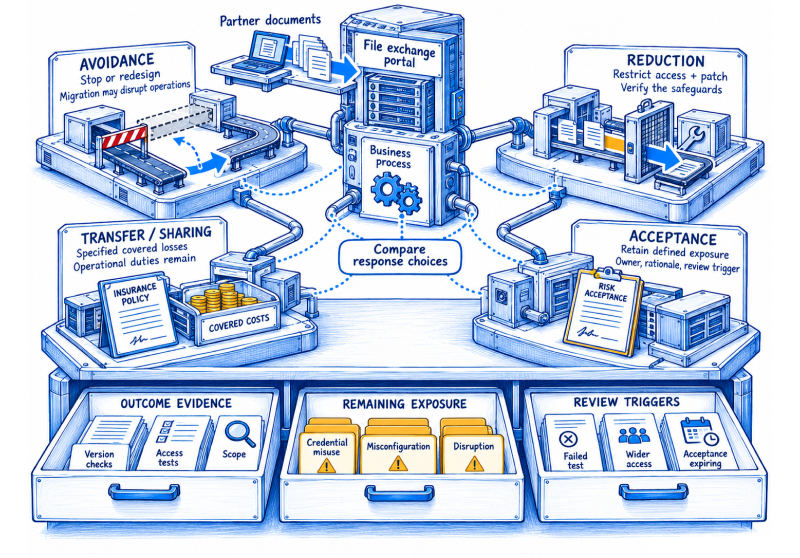
Risk Mitigation Strategies: Comparing Treatment Choices and Trade-offs in Practice

Risk Mitigation Strategies: Comparing Treatment Choices and Trade-offs in Practice

Risk mitigation is often used to mean reducing exposure, while risk treatment covers the full set of response choices. Learn how to compare avoidance, reduction, transfer and acceptance, then verify...

Categories: Cybersecurity, GRC, Risk Management
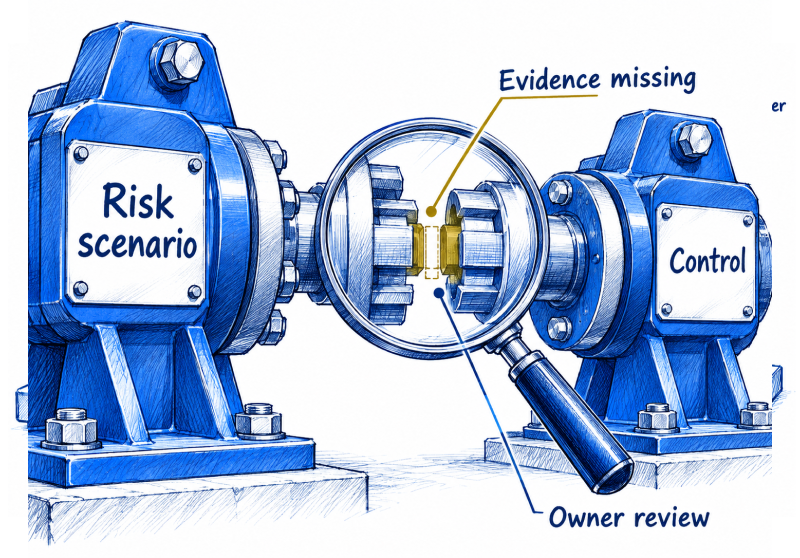
Risk Control Matrix: Connect Cybersecurity Risks to Controls and Useful Evidence

Risk Control Matrix: Connect Cybersecurity Risks to Controls and Useful Evidence

A risk control matrix makes clear how a defined business risk is addressed, who owns the response, and what evidence shows the control works. For cybersecurity and GRC teams, its...

Categories: Cybersecurity, GRC, Risk Management
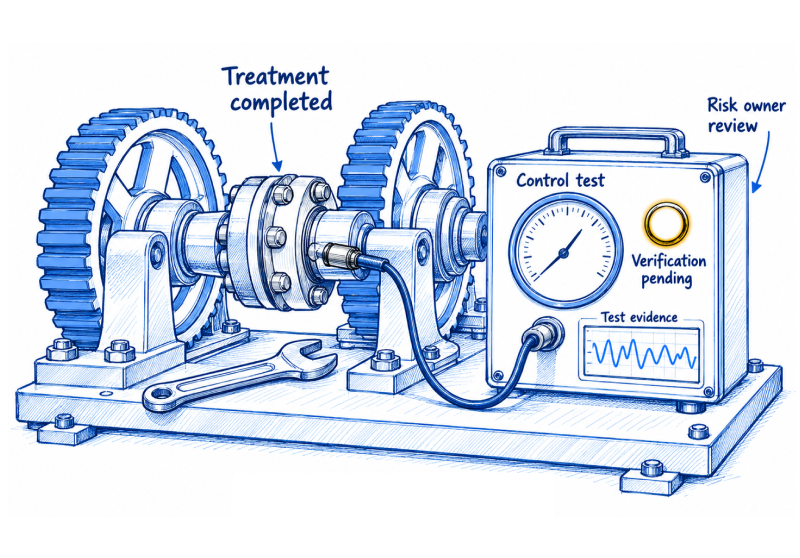
Operational Risk Management in 2026: Keep Decisions Current as Operations Change

Operational Risk Management in 2026: Keep Decisions Current as Operations Change

Operational risk management helps leaders understand how everyday activity can disrupt critical services, and what to do before a weakness becomes a loss. A practical program connects risk scenarios to...

Categories: Cybersecurity, GRC, Risk Management
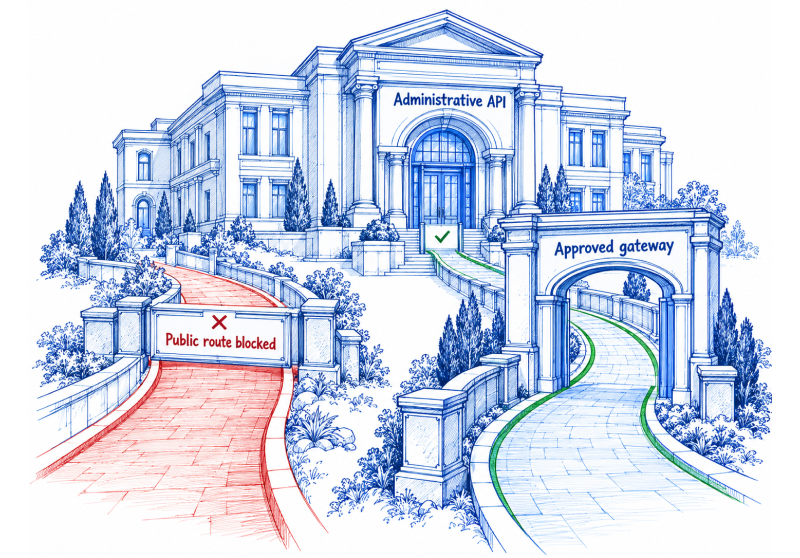
Attack Surface Management in 2026: Find Unknown Assets and Reduce Their Exposure

Attack Surface Management in 2026: Find Unknown Assets and Reduce Their Exposure

Attack surface management helps security teams discover assets and access paths their existing inventories miss. Learn how external and internal discovery, contextual prioritization and targeted remediation reduce exposure across changing...

Categories: Cybersecurity, Exposure Management
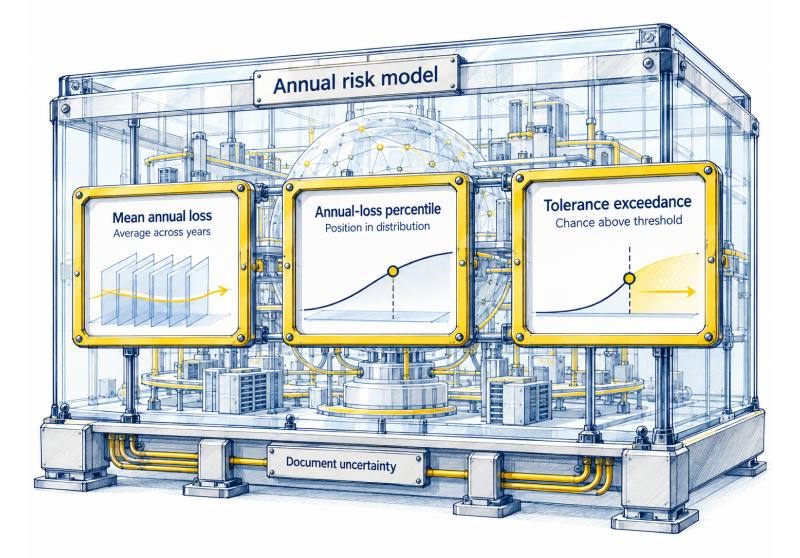
Quantitative Cyber Risk Assessment in 2026 for Better GRC Decisions

Quantitative Cyber Risk Assessment in 2026 for Better GRC Decisions

Quantitative cyber risk assessment helps teams decide which security treatments justify their cost. Defined scenarios, current evidence and explicit uncertainty make the estimates useful to security, finance and business owners....

Categories: Cybersecurity, Risk Management
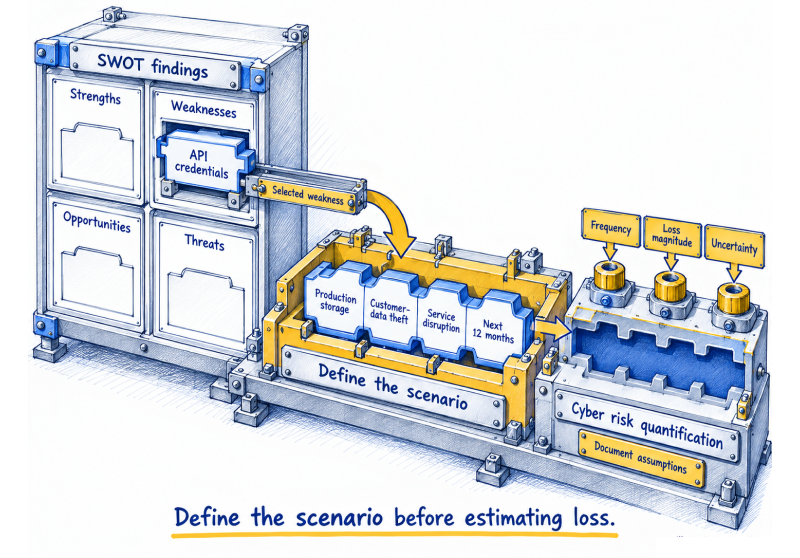
SWOT Analysis and Cyber Risk Quantification: A Practical GRC Strategy for 2026

SWOT Analysis and Cyber Risk Quantification: A Practical GRC Strategy for 2026

SWOT analysis can help security leaders identify strategic concerns, while cyber risk quantification can test how those concerns may affect the business. This article explains how to connect the two...

Categories: Cybersecurity, Risk Management
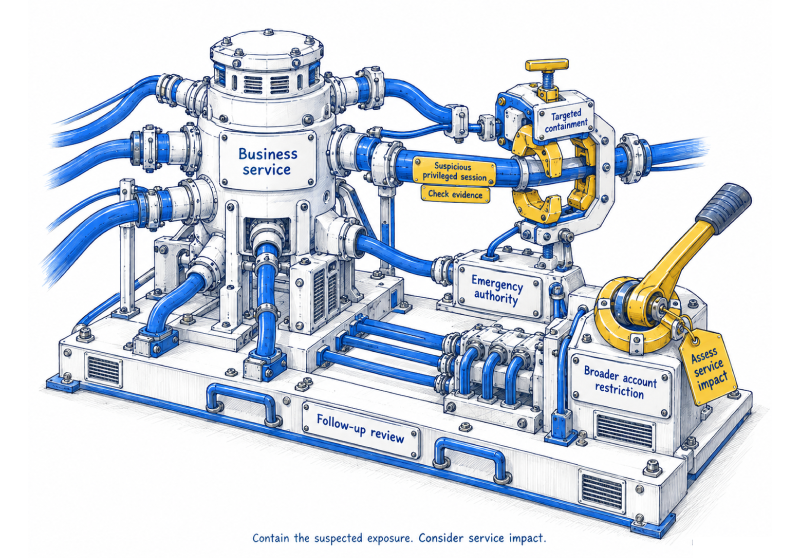
Human Factors in Incident Response in 2026: Make Safer Decisions Under Pressure

Human Factors in Incident Response in 2026: Make Safer Decisions Under Pressure

How security leaders can design roles, handoffs and decision safeguards that help people contain incidents without creating a second failure. Human factors in incident response are not a training topic...

Categories: Cybersecurity

Risk Scoring in 2026: Make Internal and External Risks Comparable Across Teams

Risk Scoring in 2026: Make Internal and External Risks Comparable Across Teams

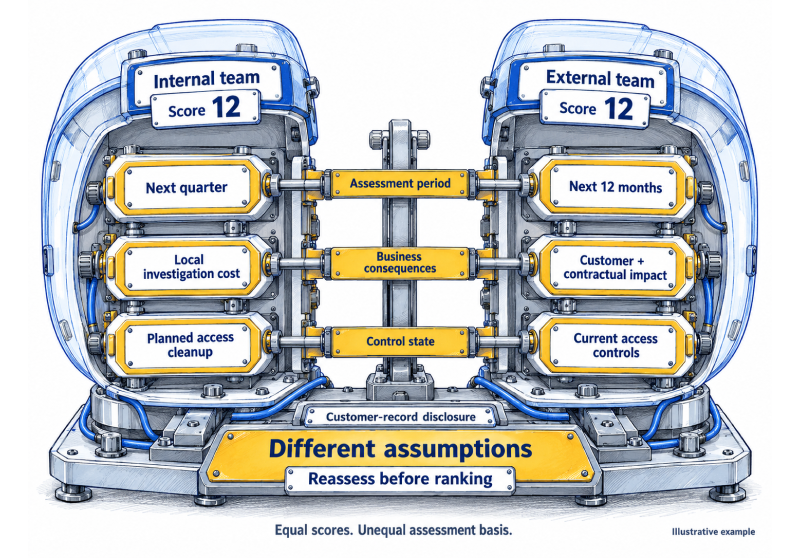
Learn how to calculate risk scores, reconcile conflicting ratings and compare internal failures with external threats without distorting management priorities. The method aligns scenarios, time horizons, impact criteria, control assumptions...

Categories: Cybersecurity, Risk Management
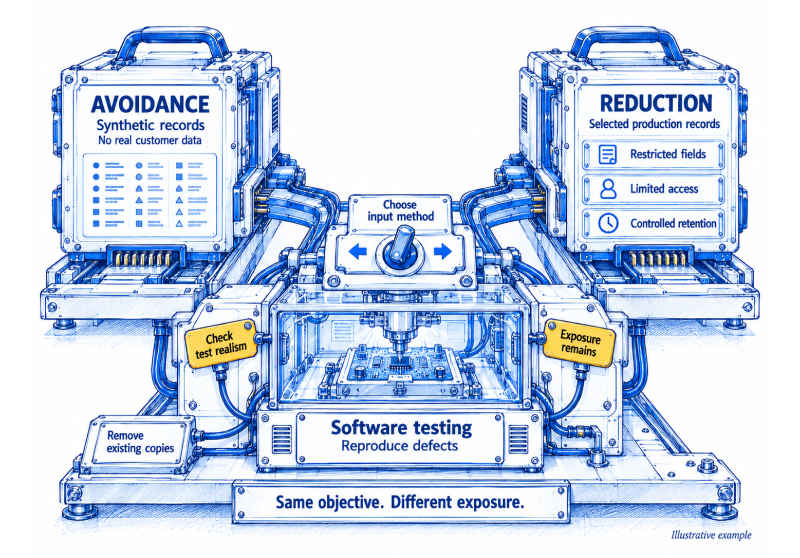
Risk Avoidance vs Risk Reduction in 2026: Choosing the Right Business Response

Risk Avoidance vs Risk Reduction in 2026: Choosing the Right Business Response

Compare the value of continuing an activity with the cost of withdrawing, and choose a response that addresses the specific exposure. Risk avoidance vs risk reduction asks a practical business...

Categories: Cybersecurity, GRC, Risk Management
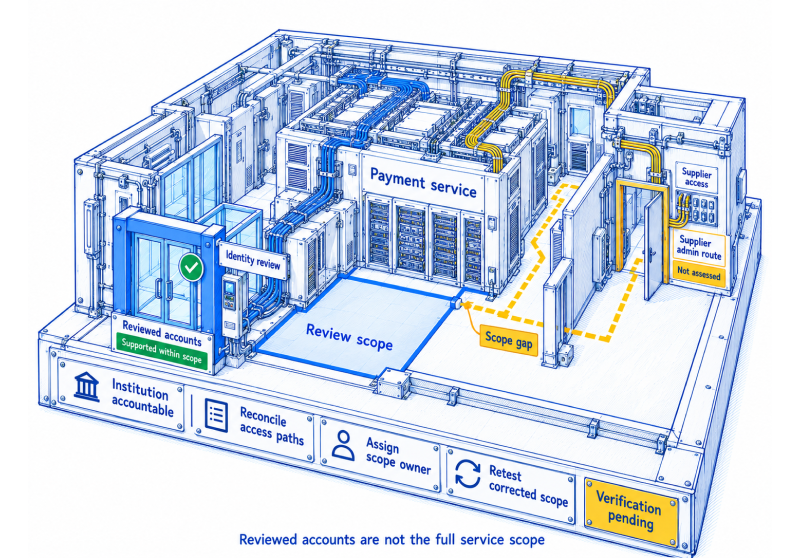
Financial Services Compliance: Can Your Evidence Support the Decision?

Financial Services Compliance: Can Your Evidence Support the Decision?

Financial services compliance needs evidence that supports decisions about critical services. Learn how to define control scope, assess supplier evidence, expose uncertainty and verify remediation while keeping institutional accountability clear....

Categories: Cybersecurity

Cybersecurity Risk Scoring: Make the Score Decision-Ready

Cybersecurity Risk Scoring: Make the Score Decision-Ready

A cybersecurity risk score should explain why an exposure matters and what action it requires. Learn how to combine threat signals, reachability, business impact and control evidence into clear priorities,...

Categories: Cybersecurity, Risk Management
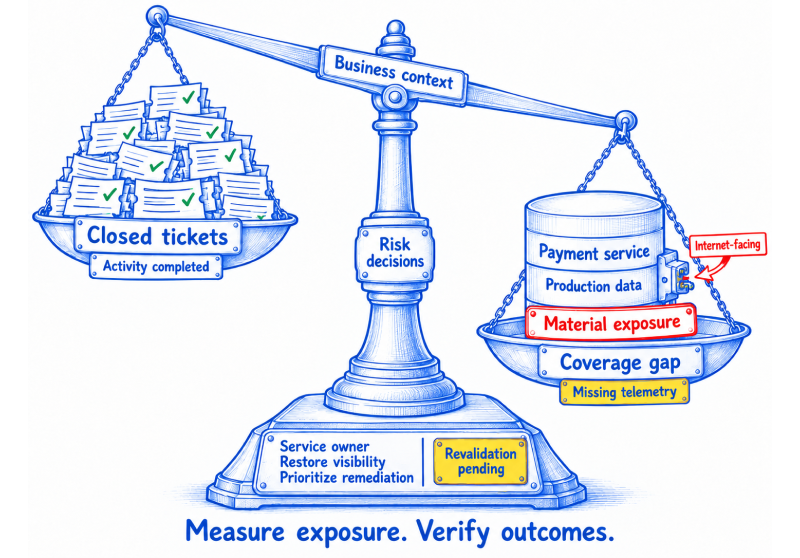
Cybersecurity Metrics in 2026: Link Control Evidence to Better Risk Decisions

Cybersecurity Metrics in 2026: Link Control Evidence to Better Risk Decisions

Useful cybersecurity metrics show where material exposure remains, who needs to act and whether corrective work reduced the risk. Learn how to define populations, keep exceptions visible and connect control...

Categories: Cybersecurity, GRC

Build a Risk Register in 2026 With Clear Evidence and Traceable Business Decisions

Build a Risk Register in 2026 With Clear Evidence and Traceable Business Decisions

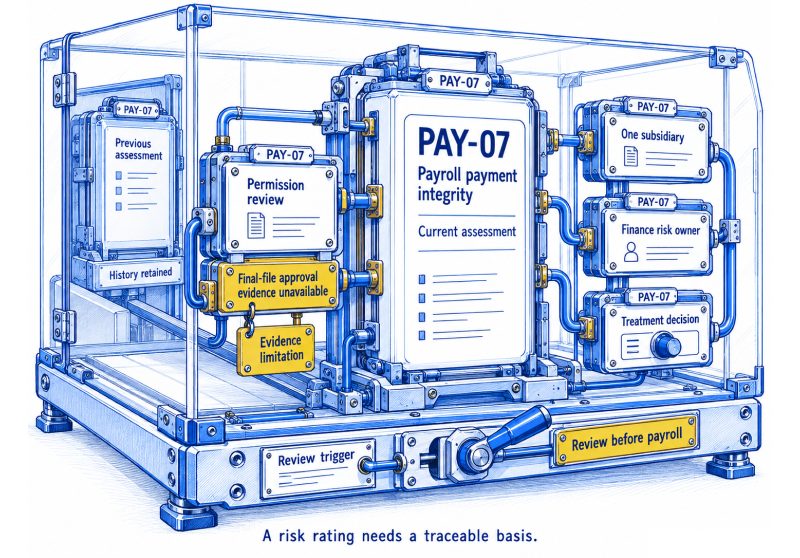
A risk rating needs a clear basis and a record of the decision behind it. Build risk entries that connect business scenarios with evidence, ownership and review triggers, keeping current...

Categories: Cybersecurity, GRC, Risk Management
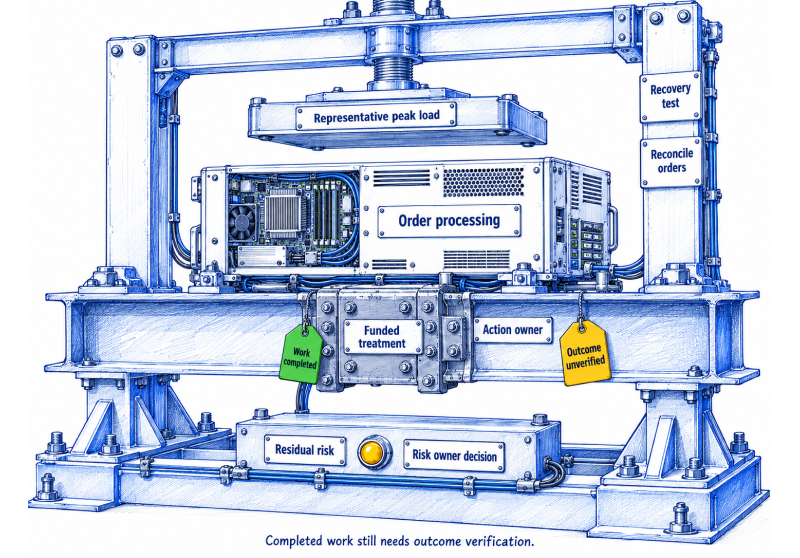
Risk Management Plan in 2026: Turn Decisions into Funded and Accountable Actions 

Risk Management Plan in 2026: Turn Decisions into Funded and Accountable Actions 

Risk decisions need funding, ownership and follow-through. Build a risk management plan that connects response choices to accountable actions, tracks delivery and keeps remaining exposure visible as conditions change. A...

Categories: Cybersecurity, GRC, Risk Management
What Is Continuous Assurance in Cybersecurity?

What Is Continuous Assurance in Cybersecurity?

Organizations invest heavily in security tools, compliance programs, and risk management processes. Yet many security leaders still struggle to answer a simple question: How do we know our controls are...

Categories: Cybersecurity

The Definitive Guide to Automated Controls Testing

The Definitive Guide to Automated Controls Testing

Every 39 seconds, a cyberattack strikes somewhere in the world (University of Maryland). At the same time, regulators are tightening rules across industries, from finance to healthcare. Leaders can no...

Categories: Cybersecurity

How Cybersecurity Asset Management Improves Risk-Based Alerting and Threat Response

How Cybersecurity Asset Management Improves Risk-Based Alerting and Threat Response

Too often, security tools treat all assets as equal. A critical alert on a decommissioned test server carries the same weight as one on a core financial system. A suspicious...

Categories: Cybersecurity

Silent Threats, Loud Consequences: Why Most Breaches Start with a Missed Signal

Silent Threats, Loud Consequences: Why Most Breaches Start with a Missed Signal

Introduction: The Breach That Wasn’t Loud — Until It Was The most dangerous breaches often don’t begin with a bang.They start with a blink—missed, ignored, or filed away for “later.”...

Categories: Cybersecurity

Top 10 Early Warning Signs of Insider Threats Every Company Should Know

Top 10 Early Warning Signs of Insider Threats Every Company Should Know

Insider threats are one of the most underestimated cybersecurity risks facing organizations today. While companies often focus on defending against external attackers, the real danger might be operating quietly from...

Categories: Cybersecurity

Cyber Security Regulatory Compliance in India: What You Need to Know

Cyber Security Regulatory Compliance in India: What You Need to Know

Introduction: When Compliance Blocks Market Entry Sometimes, a region’s regulatory compliance rules block businesses from entering a market. That’s exactly what happened with WhatsApp Pay in India. Despite having hundreds...

Categories: Cybersecurity, Governance

Cybersecurity Risk Assessment in Banking: A Strategic Guide with Risk Matrix Templates

Cybersecurity Risk Assessment in Banking: A Strategic Guide with Risk Matrix Templates

Banks today operate in a high-stakes environment, managing sensitive financial data, digital customer interactions, and a growing portfolio of online services. These innovations, while necessary, have dramatically increased their exposure...

Categories: Cybersecurity