← Back to Blog
Exposure Management
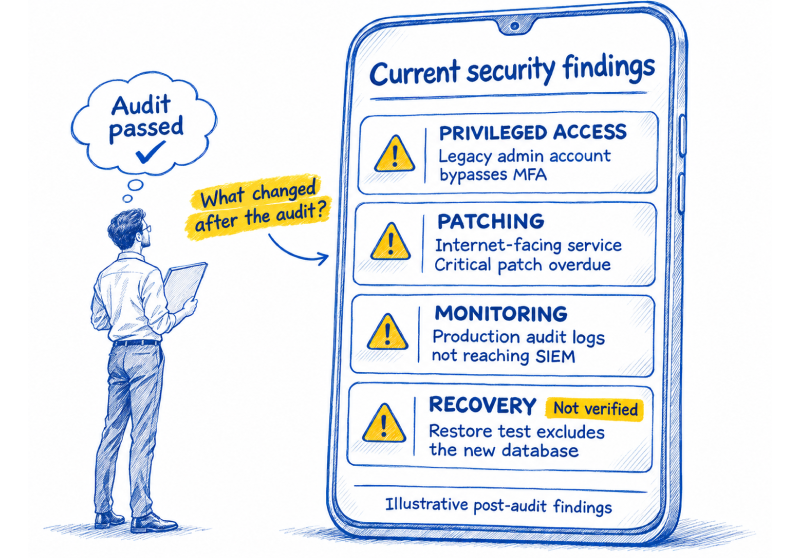
Prevent Cyberattacks by Balancing Enterprise Security and Compliance

Balancing security and compliance to prevent cyberattacks requires more than passing an audit or buying another security tool. A cybersecurity compliance program defines obligations and evidence; security testing determines whether...
Categories: Continuous Control Monitoring, Exposure Management, GRC
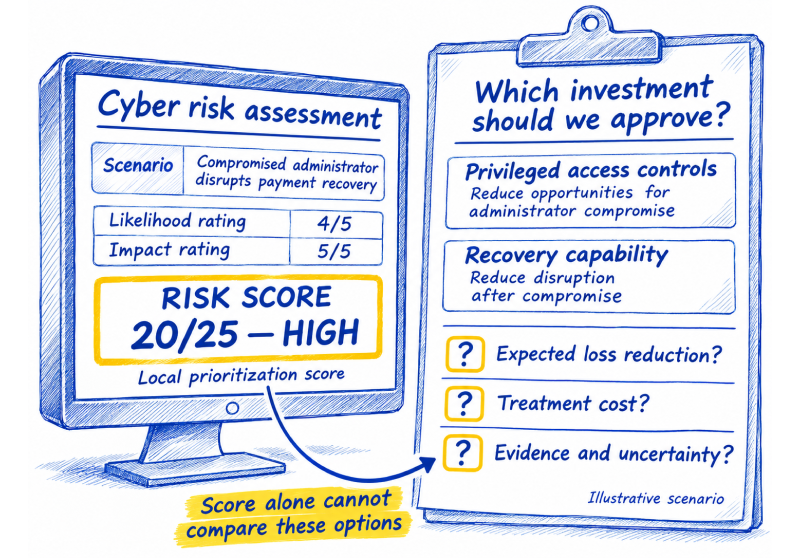
How to Select the Right Enterprise Cyber Risk Quantification Method

The right cyber risk quantification method is the one that produces evidence a decision-maker can use without implying more certainty than the inputs support. Start with the decision and required...
Categories: Exposure Management, GRC, Security Maturity
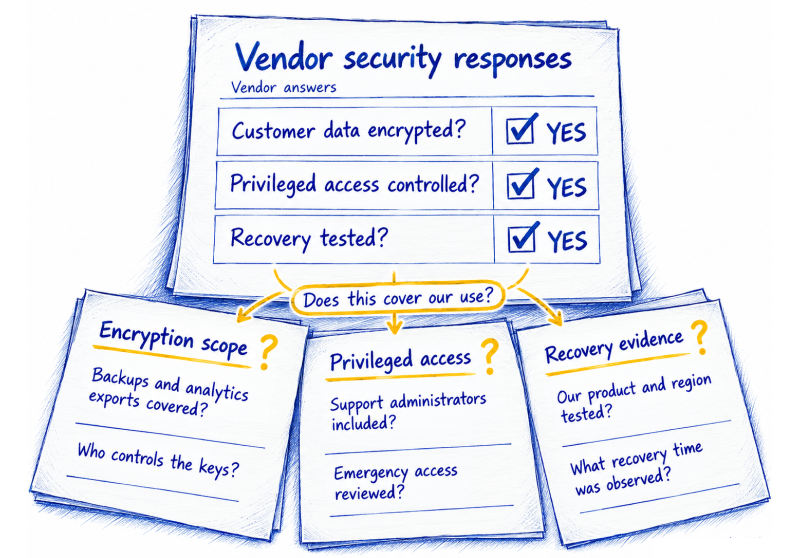
Vendor Cybersecurity Questions That Test Scope, Evidence and Exposure
A vendor cybersecurity inquiry should establish what the supplier will do, which data and systems it can access, and how the business depends on its services. Ask targeted questions, request...
Categories: Continuous Control Monitoring, Exposure Management, GRC
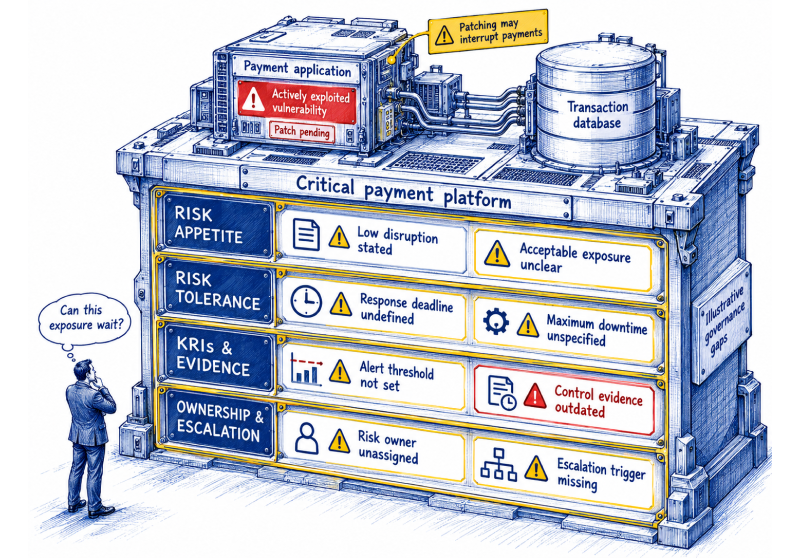
Risk Appetite vs Risk Tolerance: Set Clear Limits and Track Cyber Risk Exposure
Risk appetite, risk tolerance, and risk capacity shape how organizations assess and manage cybersecurity risks. Establishing measurable thresholds, monitoring KRIs, and evaluating control effectiveness help organizations prioritize exposure, make informed...
Categories: Exposure Management