← Back to Blog

Uncategorized

SaaS Startup Security Readiness: Prove What Enterprise Buyers Expect

SaaS Startup Security Readiness: Prove What Enterprise Buyers Expect

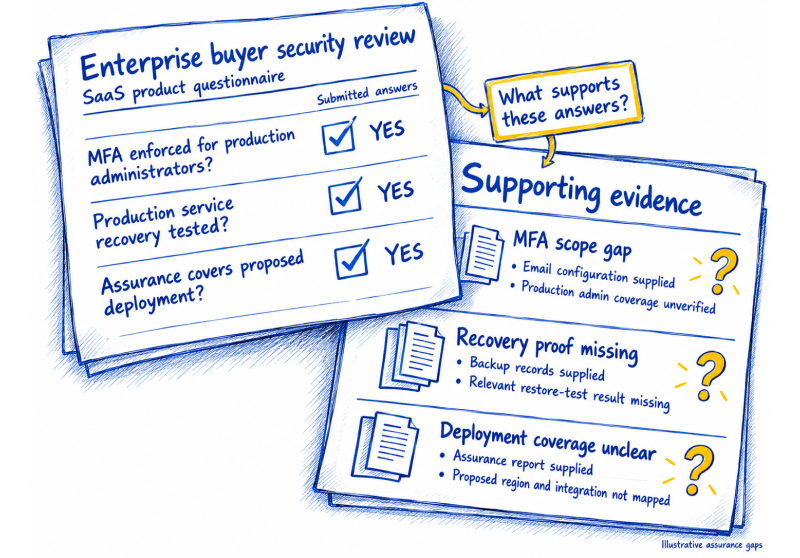
Enterprise buyers expect SaaS startups to demonstrate how they protect customer data, identities, and business operations not just present policies or certifications. This article explores how startups can build security...

Categories: Uncategorized

Designing a Company-Wide Information Security Policy for Every Team

Designing a Company-Wide Information Security Policy for Every Team

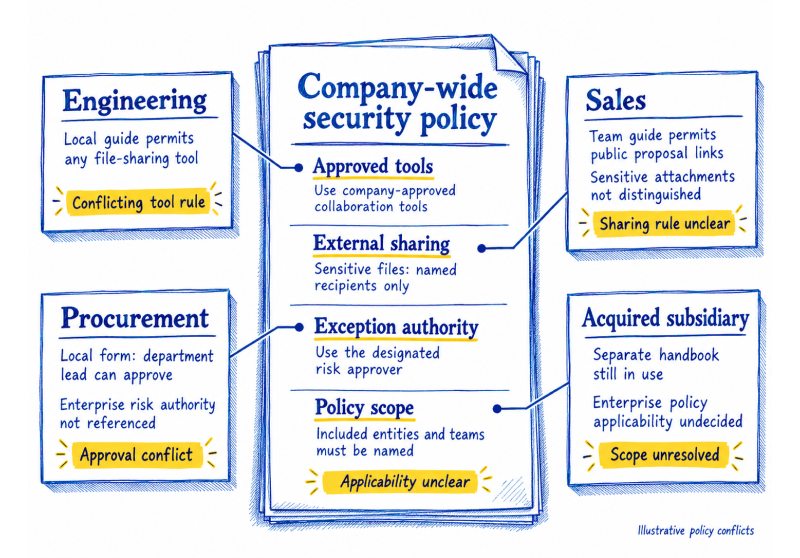
A company-wide information security policy gives people clear expectations for protecting the organization’s information, systems, and operations. Its scope should fit how the business works across teams, locations, cloud environments,...

Categories: Uncategorized

Who Owns Cyber Risk in a Small Business? Clarify Roles and Decisions

Who Owns Cyber Risk in a Small Business? Clarify Roles and Decisions

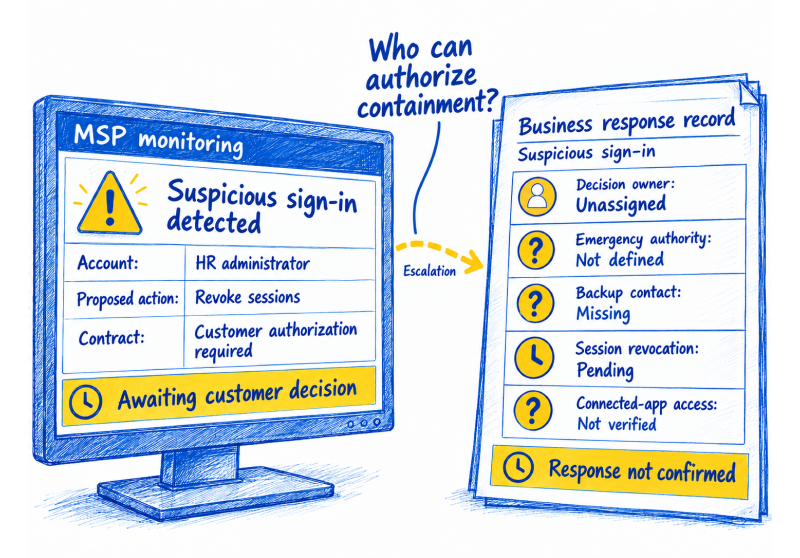
Cybersecurity responsibilities for small businesses span employees, IT staff, managed providers, and cloud vendors. Risk appears where their duties meet.Name who decides, who acts, and who verifies the outcome.Keep those...

Categories: Uncategorized

Automate Vendor Risk Assessments With Guardrails for Better Decisions

Automate Vendor Risk Assessments With Guardrails for Better Decisions

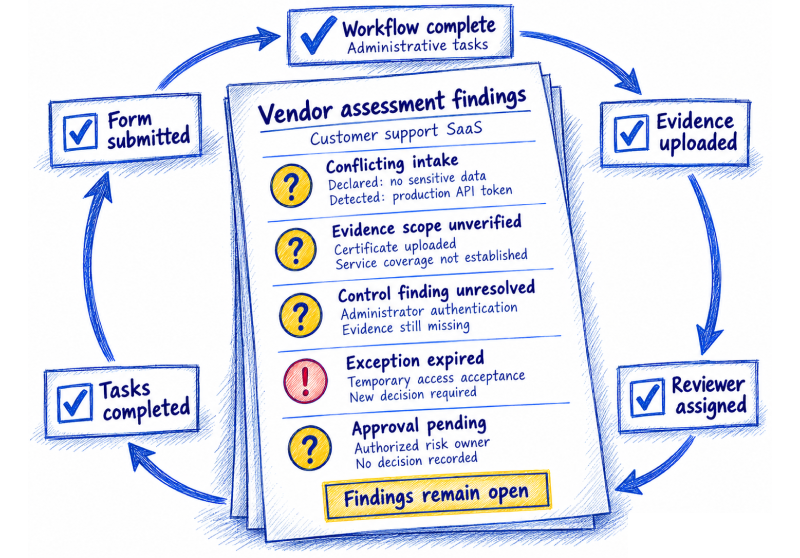
Automating vendor risk assessments should remove delay without turning a completed form into an approval. Routes each relationship appropriately, checks evidence quality and keeps risk decisions with accountable people. Keep...

Categories: Uncategorized

ICT Supplier Due Diligence Measures Risk Beyond Security Ratings Alone

ICT Supplier Due Diligence Measures Risk Beyond Security Ratings Alone

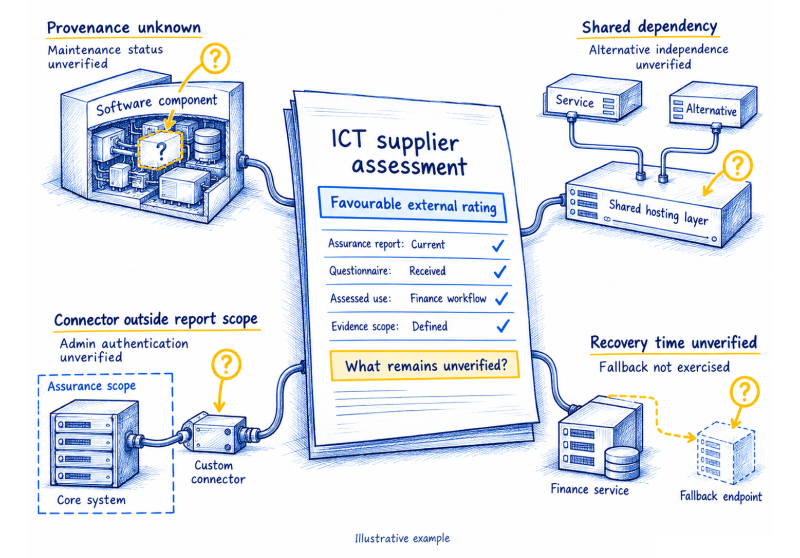
ICT supplier due diligence helps organizations assess technology dependencies, validate assurance evidence and identify uncertainty before making risk decisions. This guide applies five due-diligence lenses to the intended use, separates...

Categories: Uncategorized

Vendor Risk Management: Govern Supplier Access, Data and Dependencies

Vendor Risk Management: Govern Supplier Access, Data and Dependencies

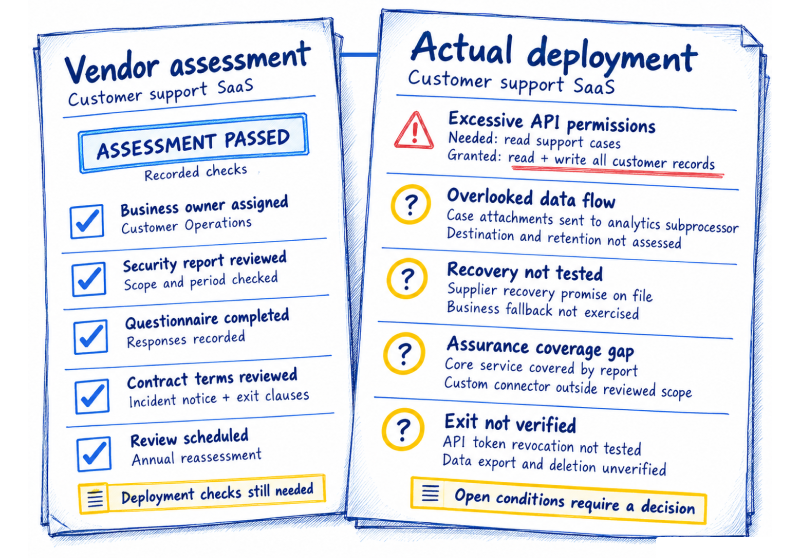
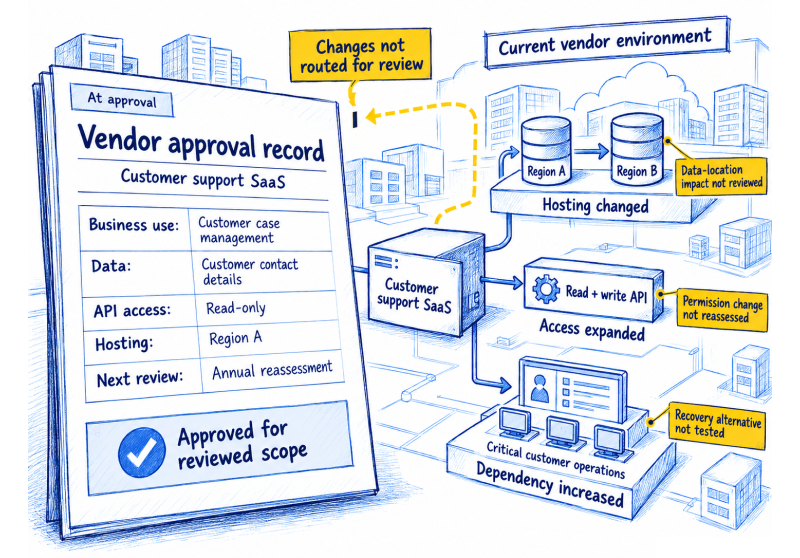
Vendor risk management helps organizations govern supplier relationships from initial assessment through verified exit. Effective oversight connects each supplier’s business role, data access and operational dependencies to proportionate checks, clear...

Categories: Uncategorized

Vendor Risk Management Maturity Model for Stronger Oversight

Vendor Risk Management Maturity Model for Stronger Oversight

Vendor risk management maturity measures how reliably an organization identifies supplier dependencies, makes proportionate risk decisions and revisits them as conditions change. This guide provides four maturity states, six capabilities...

Categories: Uncategorized

Security Compliance That Connects Regulatory Duties to Real Protection

Security Compliance That Connects Regulatory Duties to Real Protection

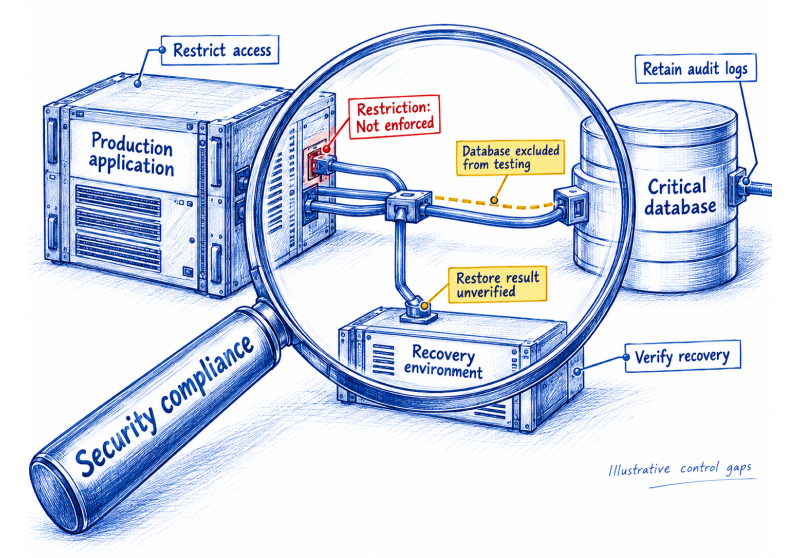
Security compliance connects applicable requirements with safeguards that protect systems, information, and business operations. A useful program establishes which duties apply, assigns control ownership, and tests whether safeguards work across...

Categories: Uncategorized

Compliance Scope Triggers for Fast-Growing Companies During Expansion

Compliance Scope Triggers for Fast-Growing Companies During Expansion

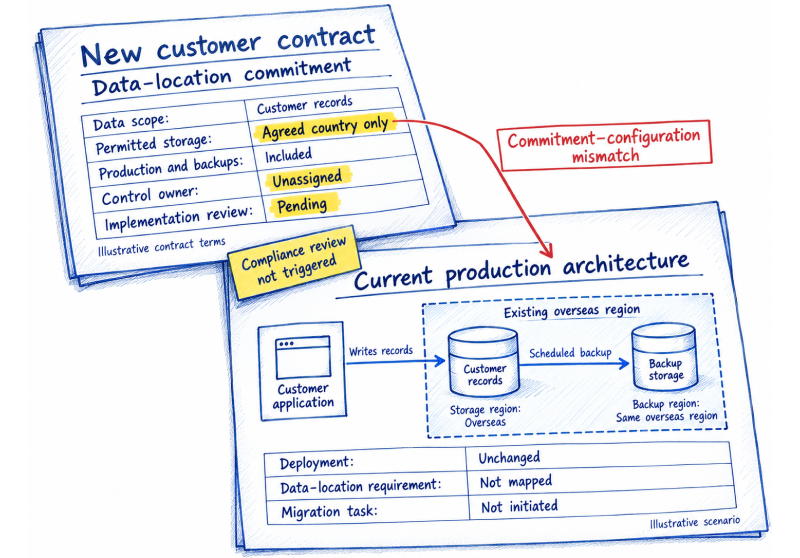
Fast-growing companies face compliance challenges when new markets, products, suppliers, and customer commitments outpace existing controls. A compliance scope review helps teams identify which obligations may change, what parts of...

Categories: Uncategorized

Access Reviews With Verified Coverage Decisions and Effective Closure

Access Reviews With Verified Coverage Decisions and Effective Closure

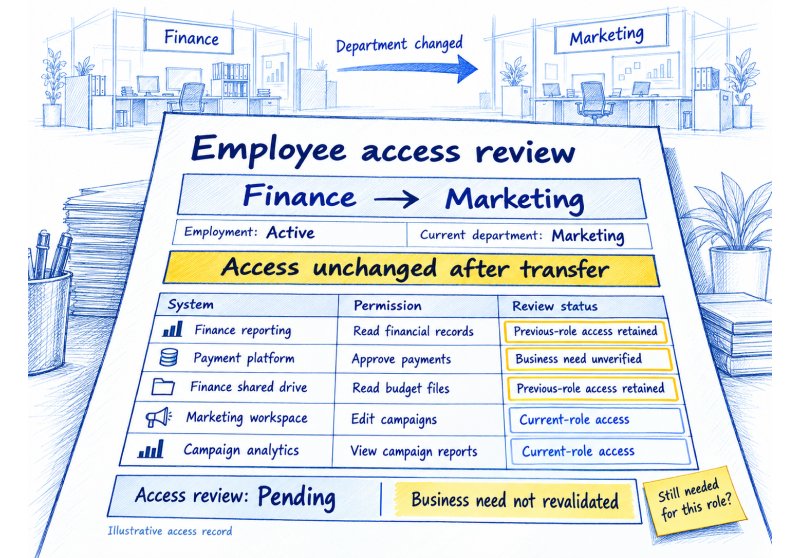
Access reviews are easy to schedule and surprisingly easy to get wrong. A clean approval report can still miss direct application accounts, privilege inherited through groups, or removals that never...

Categories: Uncategorized

Why Internal Controls Matter as Organizations Grow and Change Rapidly

Why Internal Controls Matter as Organizations Grow and Change Rapidly

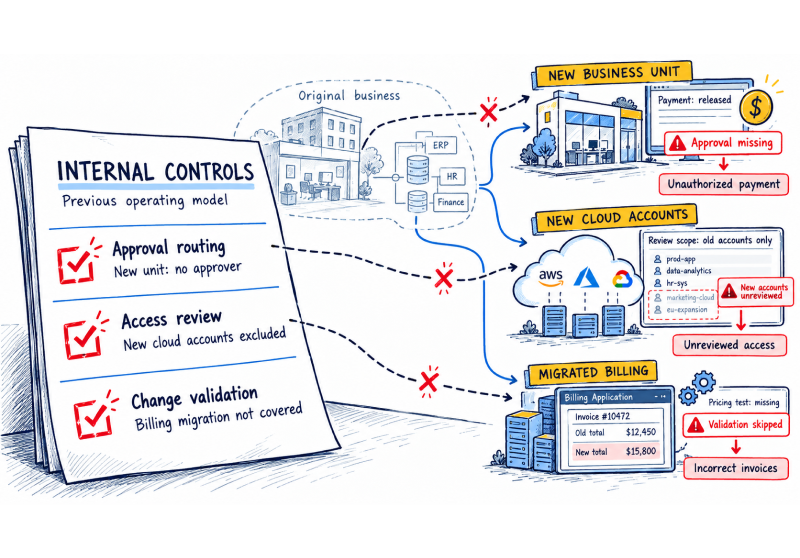
Internal controls help organizations protect assets, maintain reliable information, and keep accountability clear as they grow. Approvals, checks, and safeguards reduce preventable errors and help teams respond when processes go...

Categories: Uncategorized

Compliance Status Reporting in 2026: Turn Results Into Clear Decisions

Compliance Status Reporting in 2026: Turn Results Into Clear Decisions

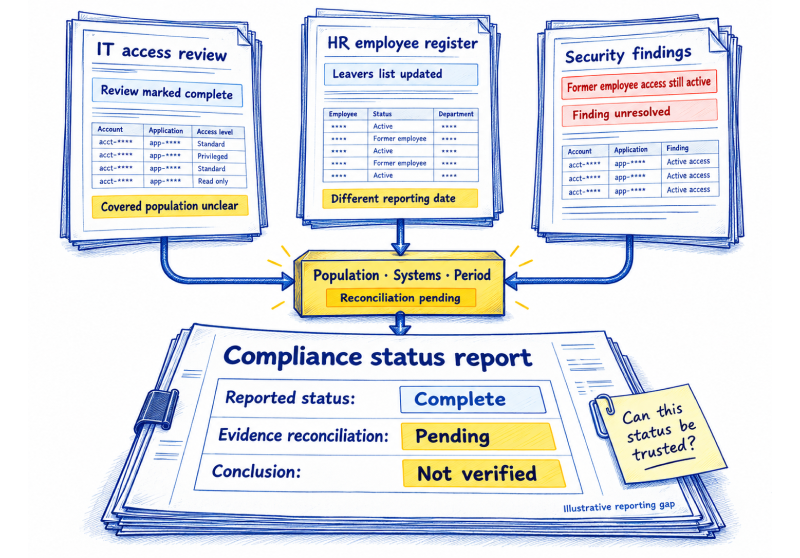
Compliance status reporting helps leaders understand what reported results cover, how reliable the supporting evidence is, and which gaps need action. Clear scope, separate test and exception states, and accountable...

Categories: Uncategorized