← Back to Blog

Uncategorized

Information Security for Businesses: Protecting Trust and Operations

Information Security for Businesses: Protecting Trust and Operations

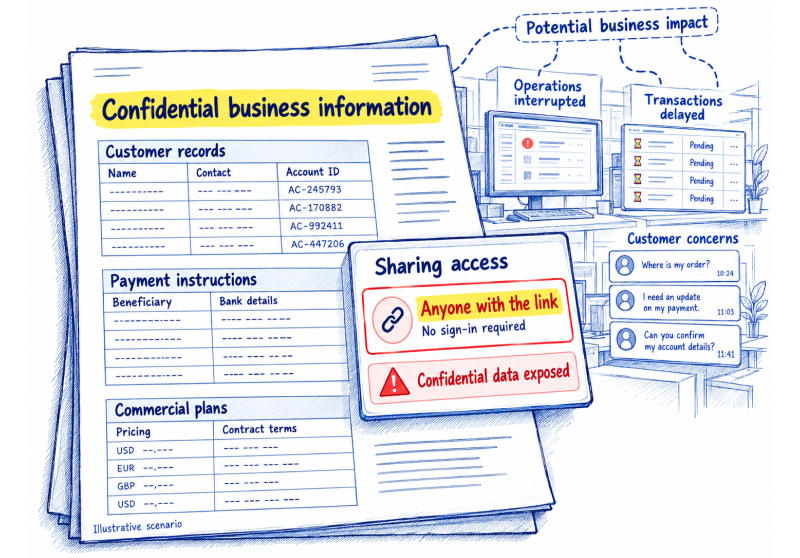
Information security for businesses protects the confidentiality, integrity and availability of information that supports everyday operations. Connecting safeguards to critical records, transactions and services helps organizations prioritize investment, limit disruption...

Categories: Uncategorized

Choosing a Security Framework for Risk, Compliance, and Business Needs

Choosing a Security Framework for Risk, Compliance, and Business Needs

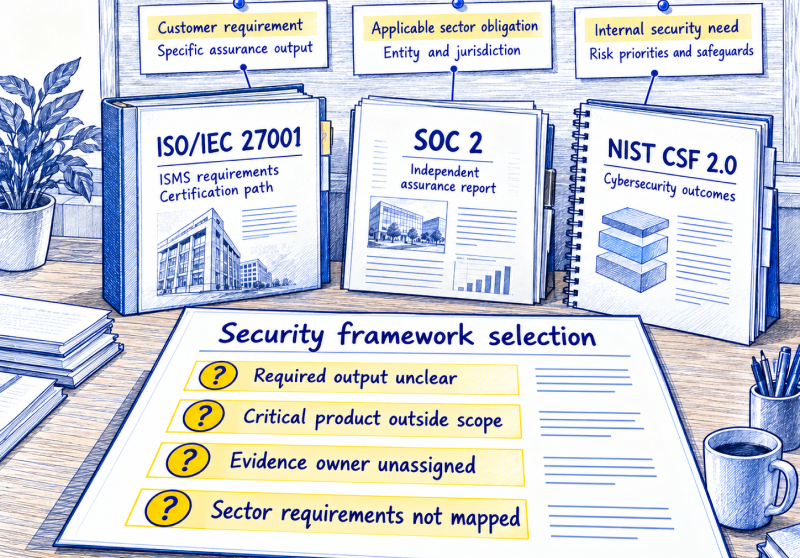
A security framework helps organizations structure cybersecurity priorities, but selecting the right approach depends on business risks, applicable obligations and stakeholder expectations. Clear scope, accountable owners and suitable evidence make...

Categories: Uncategorized

Data Privacy Compliance: Put Personal Data Controls Into Daily Practice at Scale

Data Privacy Compliance: Put Personal Data Controls Into Daily Practice at Scale

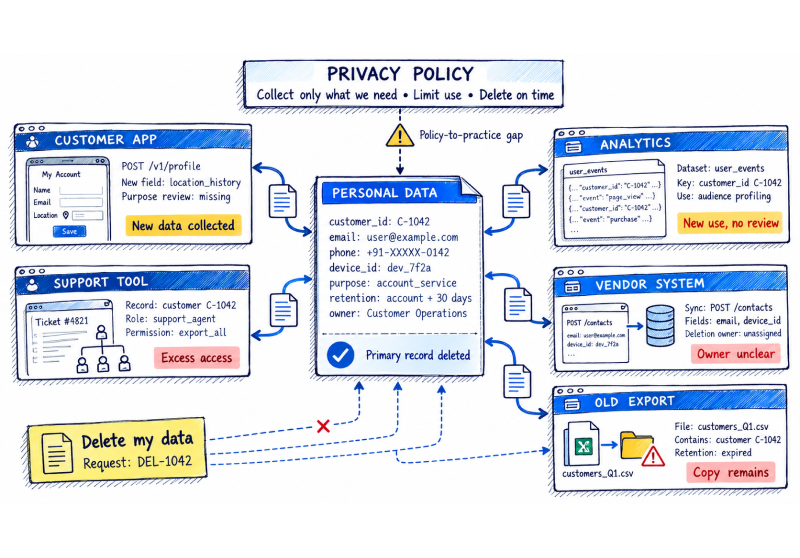
Data privacy compliance depends on whether stated purposes, actual data use and safeguards stay aligned as products and systems change. Trace each activity through access, rights requests, retention and deletion,...

Categories: Uncategorized

Fintech Compliance: A Practical Model for Regulated Digital Finance Operations

Fintech Compliance: A Practical Model for Regulated Digital Finance Operations

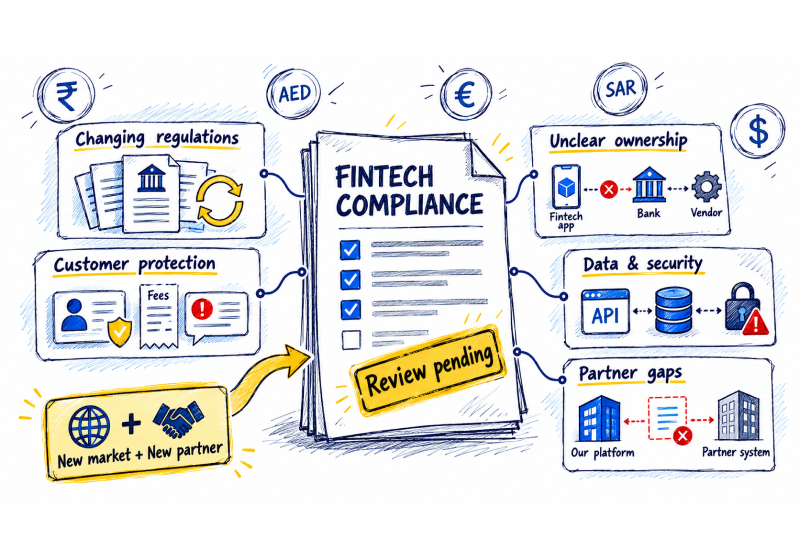
Fintech compliance depends on what a product does, which entities deliver it, and where customers, money, and data move. Mapping obligations across customer journeys clarifies control ownership and partner responsibilities....

Categories: Uncategorized

Data Governance Metrics: KPIs for Quality, Ownership, and Trusted Data Decisions

Data Governance Metrics: KPIs for Quality, Ownership, and Trusted Data Decisions

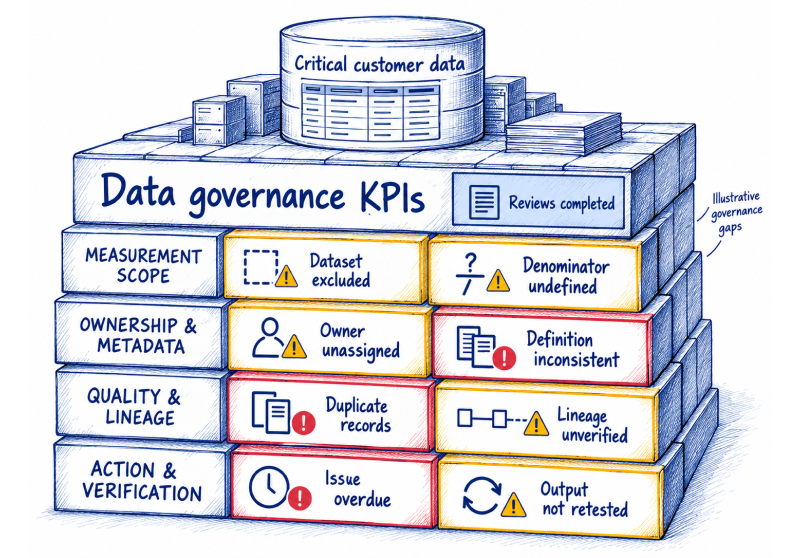
Data governance earns trust when teams can show where important data comes from, who is accountable, and whether it is fit for a defined use. A small set of well-defined...

Categories: Uncategorized

Time to Compliance: How CISOs Speed Audit Readiness and Measure Business Value

Time to Compliance: How CISOs Speed Audit Readiness and Measure Business Value

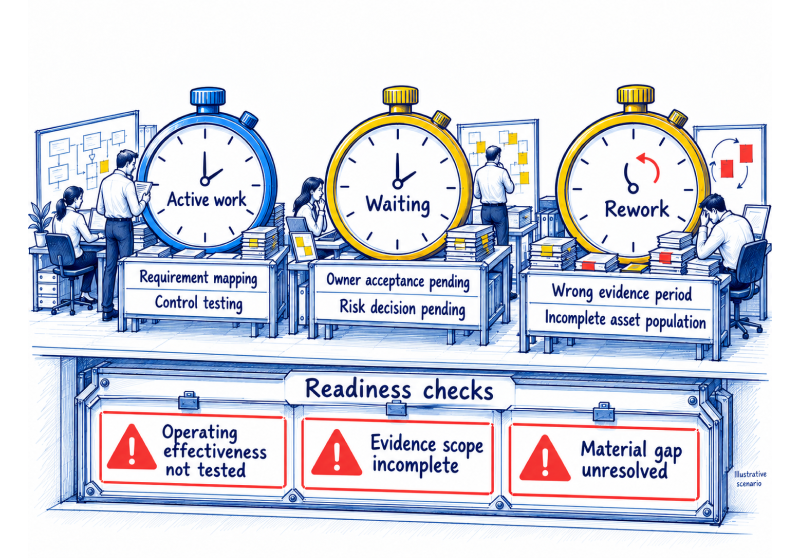
Time to compliance helps CISOs understand where audit preparation stalls and how to reduce avoidable delays. Clear milestones, accountable owners, and validated evidence reuse make readiness more predictable. Measuring preparation...

Categories: Uncategorized

Risk Management Automation: Connect Evidence to Timely and Accountable Decisions

Risk Management Automation: Connect Evidence to Timely and Accountable Decisions

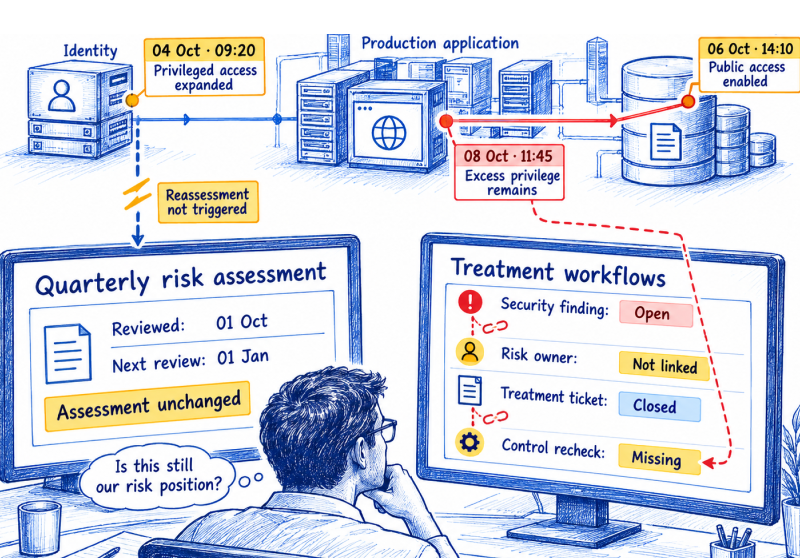
Risk management automation connects current operational evidence with structured risk assessments, monitoring, and accountable decisions. By reducing manual collection and follow-up, organizations can identify meaningful changes earlier while retaining human...

Categories: Uncategorized

SCRM vs TPRM vs VRM: Understand External Risks and Shared Supplier Dependencies

SCRM vs TPRM vs VRM: Understand External Risks and Shared Supplier Dependencies

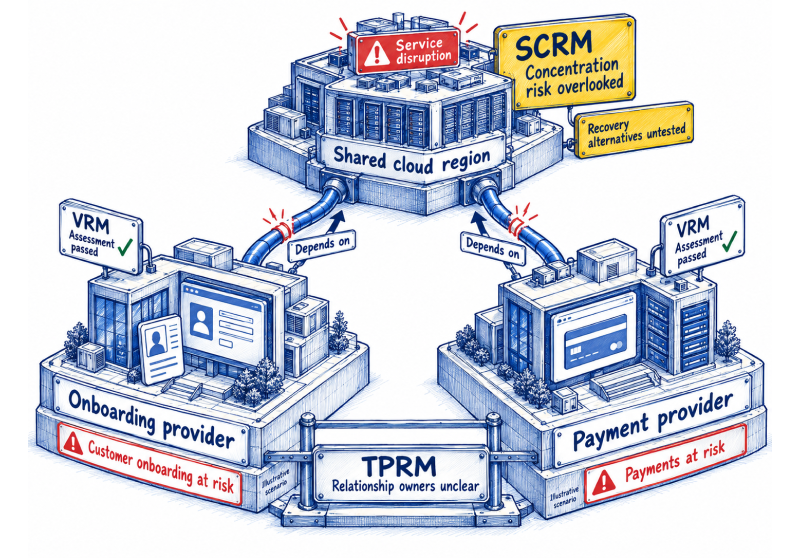
SCRM, TPRM, and VRM address different layers of external business risk, from individual suppliers to interconnected supply chains. Understanding their scope and governance responsibilities helps organizations assess exposure, manage dependencies,...

Categories: Uncategorized

How to Calculate RPN in FMEA: Formula, Scoring Criteria and Practical Examples

How to Calculate RPN in FMEA: Formula, Scoring Criteria and Practical Examples

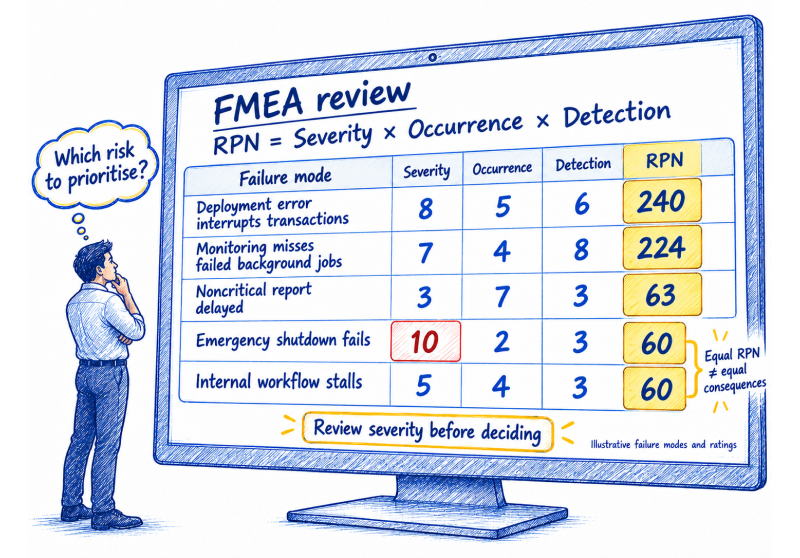
Risk Priority Number (RPN) helps teams compare potential failures through their severity, likelihood of occurrence, and difficulty of detection. Consistent scoring, practical examples, and regular reassessment make FMEA more useful...

Categories: Uncategorized

Cybersecurity Risk Scoring: Making Scores Useful for Security and Risk Decisions

Cybersecurity Risk Scoring: Making Scores Useful for Security and Risk Decisions

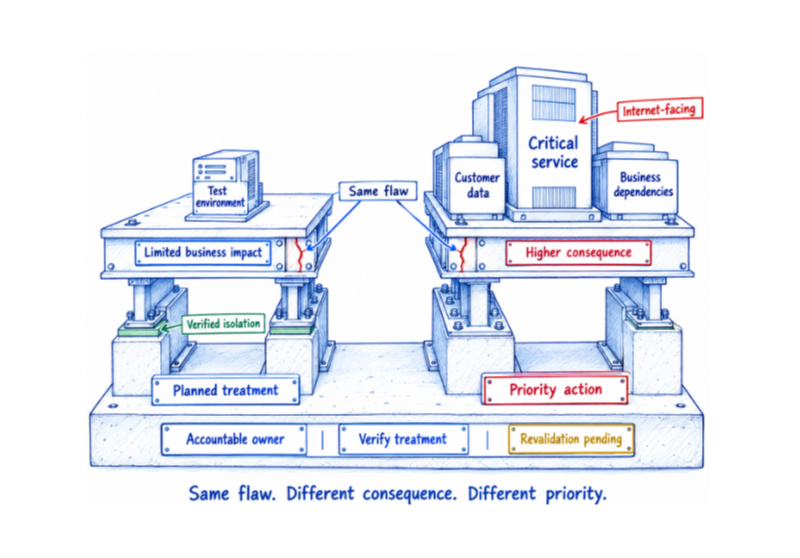
A cybersecurity risk score should explain why an exposure matters and what action it requires. Learn how to combine threat signals, reachability, business impact and control evidence into clear priorities,...

Categories: Uncategorized

Automated Compliance Evidence: Make Control Signals Traceable and Reviewable

Automated Compliance Evidence: Make Control Signals Traceable and Reviewable

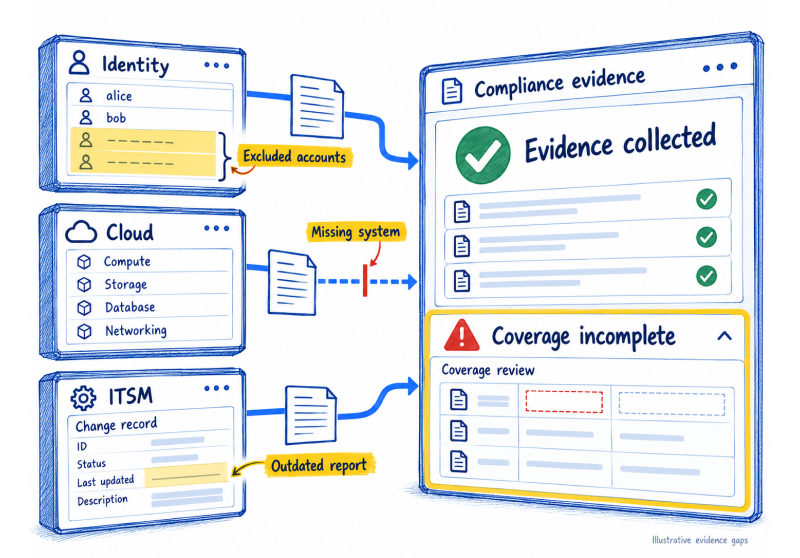
Automated evidence can save teams from repeated exports and audit-week searches. But capture is only the start: the evidence must still answer the auditor’s question. Automated compliance evidence collection can...

Categories: Uncategorized

Data Classification Policy: Align Data Handling With Risk and Control Evidence

Data Classification Policy: Align Data Handling With Risk and Control Evidence

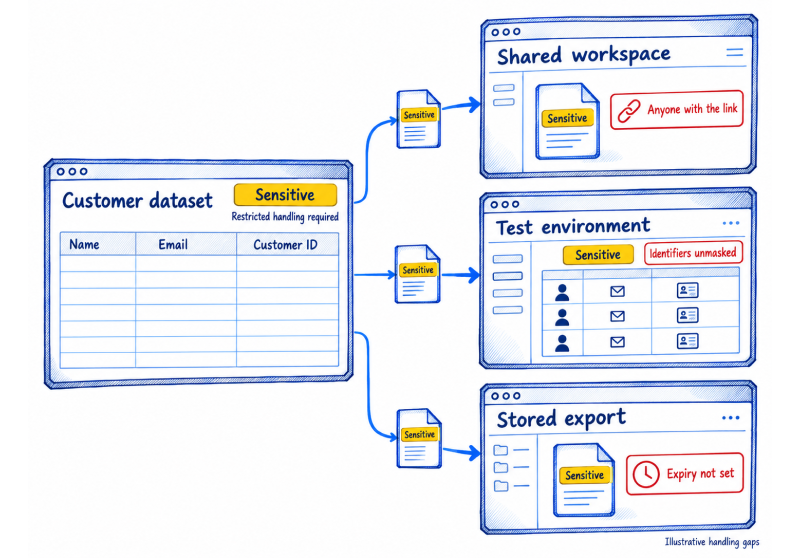
Define labels that guide access, sharing and disposal. This article explains how to apply them across data copies, assign decisions and connect handling controls to applicable framework requirements. A data...

Categories: Uncategorized