
Surbhi Bhutani
November 4, 2026
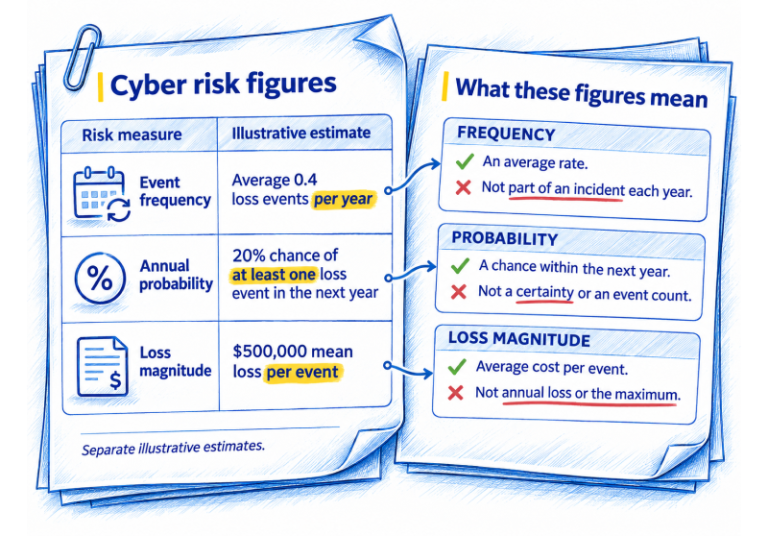
Cyber risk quantification expresses possible cyber losses in numerical terms, often money, for a defined scenario and period. Understanding its vocabulary helps...
Surbhi Bhutani
November 4, 2026
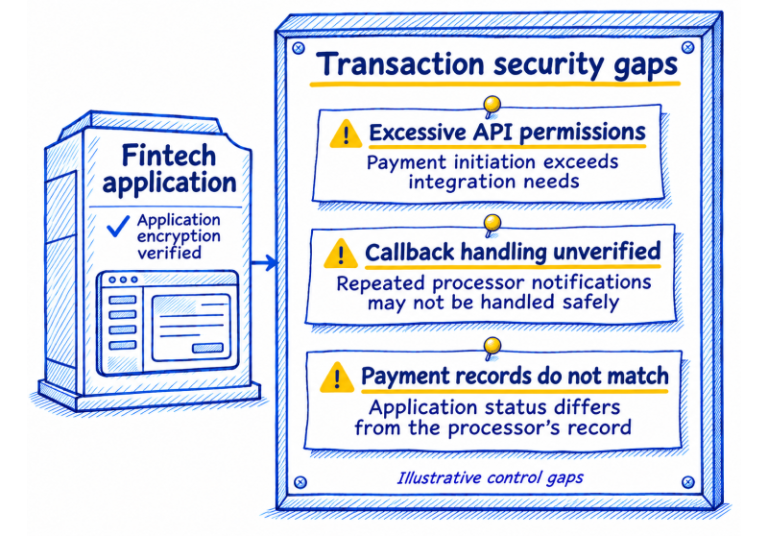
Fintech startup security must protect money, identity and financial data across live workflows enterprise buyers depend on. A credible InfoSec posture secures...
Surbhi Bhutani
November 3, 2026
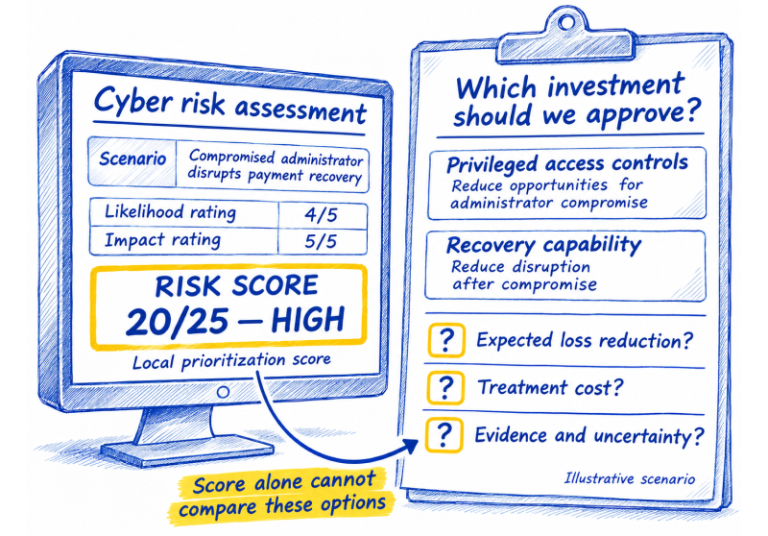
The right cyber risk quantification method is the one that produces evidence a decision-maker can use without implying more certainty than the...
Surbhi Bhutani
November 2, 2026
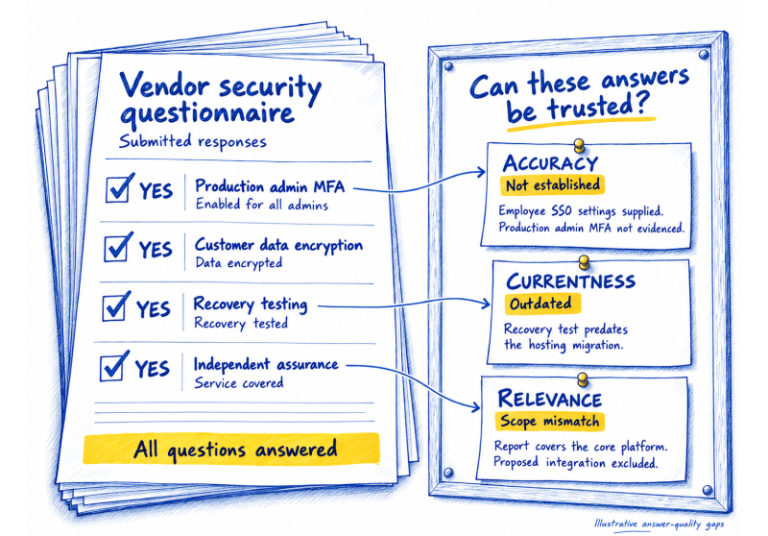
Security questionnaires help buyers understand how a supplier protects the data, systems and services involved in a proposed relationship. Reliable responses define...
Surbhi Bhutani
November 2, 2026
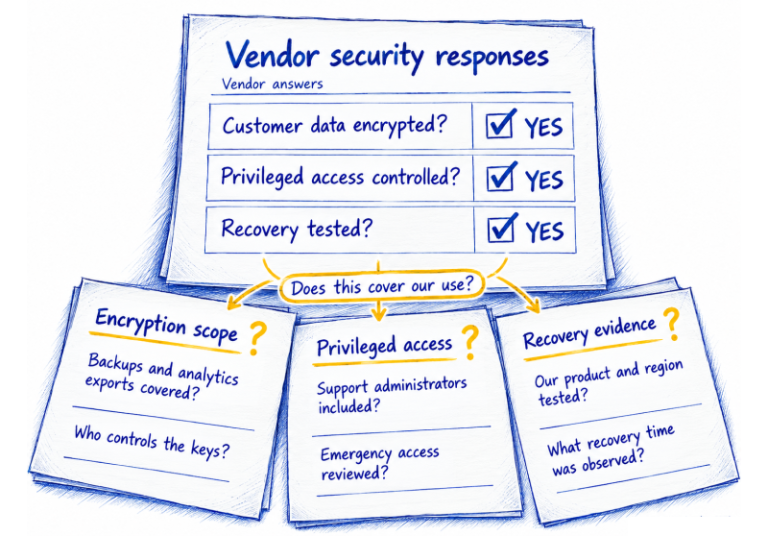
A vendor cybersecurity inquiry should establish what the supplier will do, which data and systems it can access, and how the business...
Surbhi Bhutani
November 2, 2026
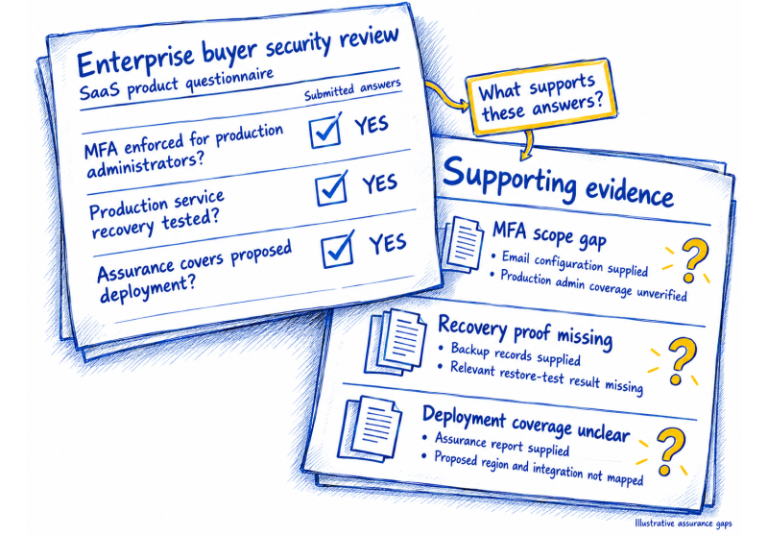
Enterprise buyers expect SaaS startups to demonstrate how they protect customer data, identities, and business operations not just present policies or certifications....
Surbhi Bhutani
October 30, 2026
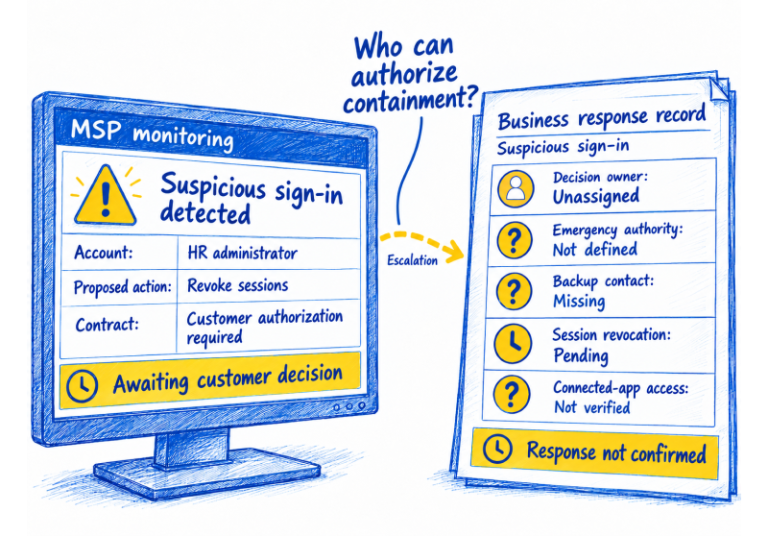
Cybersecurity responsibilities for small businesses span employees, IT staff, managed providers, and cloud vendors. Risk appears where their duties meet.Name who decides,...
Surbhi Bhutani
October 29, 2026
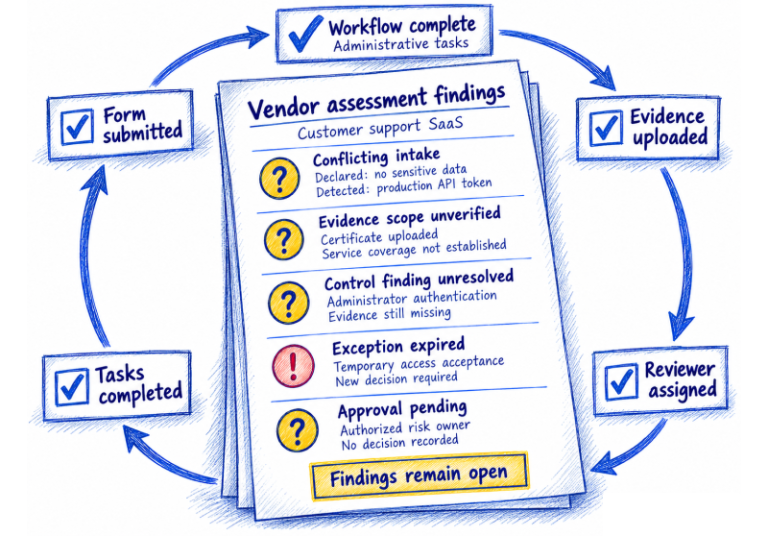
Automating vendor risk assessments should remove delay without turning a completed form into an approval. Routes each relationship appropriately, checks evidence quality...
Surbhi Bhutani
October 29, 2026
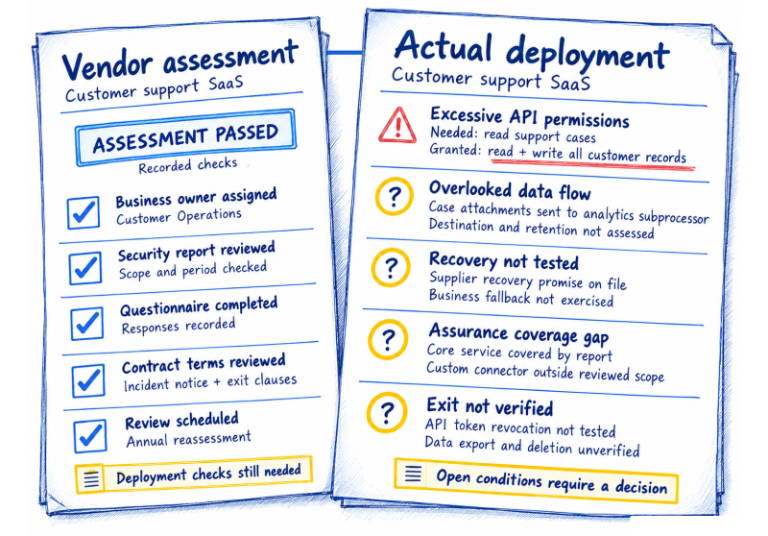
Vendor risk management helps organizations govern supplier relationships from initial assessment through verified exit. Effective oversight connects each supplier’s business role, data...
Surbhi Bhutani
October 28, 2026
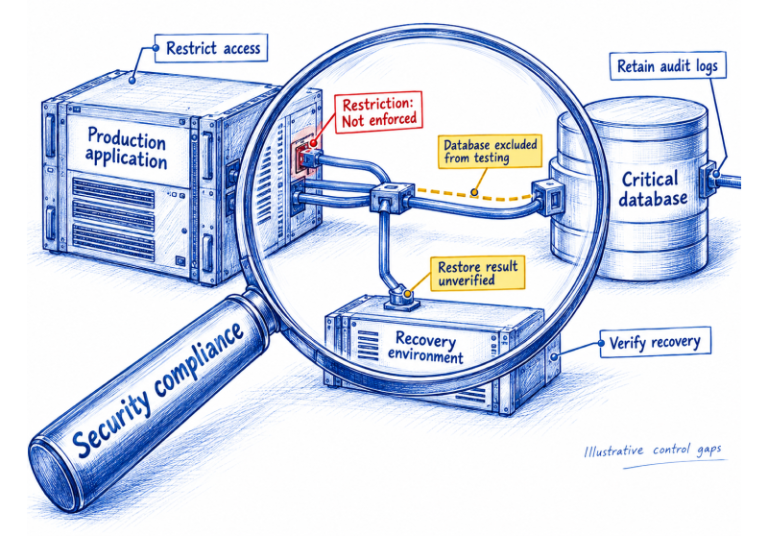
Security compliance connects applicable requirements with safeguards that protect systems, information, and business operations. A useful program establishes which duties apply, assigns...
Surbhi Bhutani
October 28, 2026
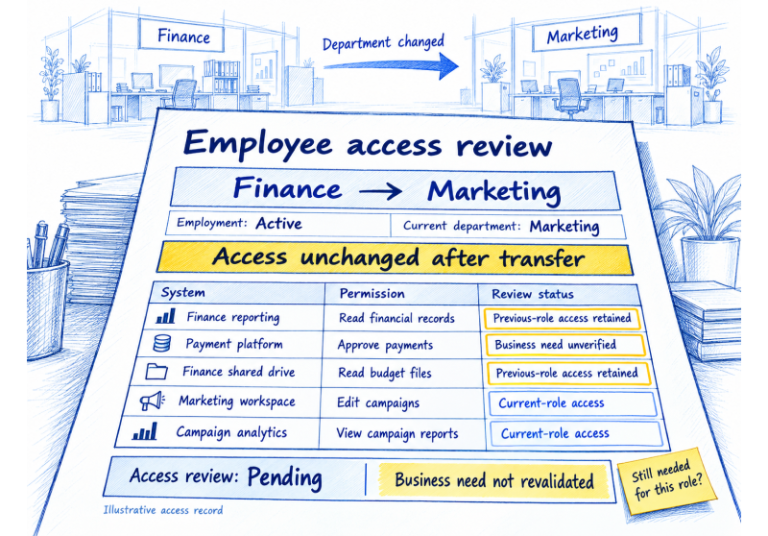
Access reviews are easy to schedule and surprisingly easy to get wrong. A clean approval report can still miss direct application accounts,...
Surbhi Bhutani
October 27, 2026
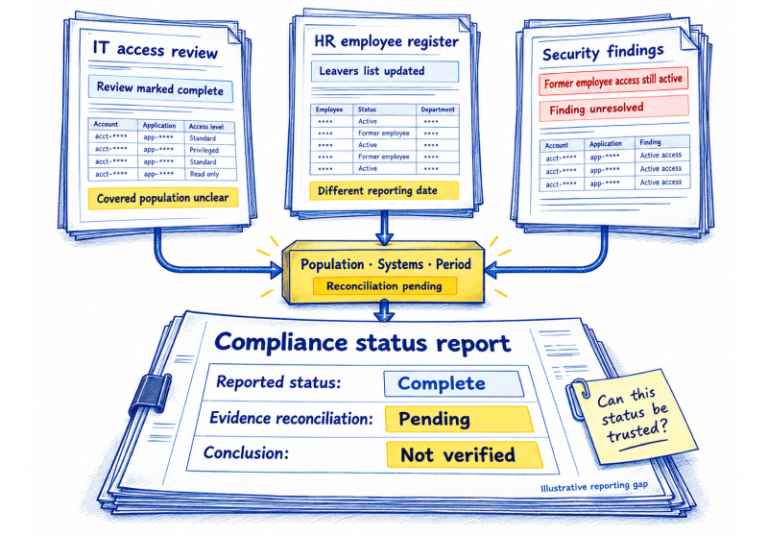
Compliance status reporting helps leaders understand what reported results cover, how reliable the supporting evidence is, and which gaps need action. Clear...