
Surbhi Bhutani
October 27, 2026
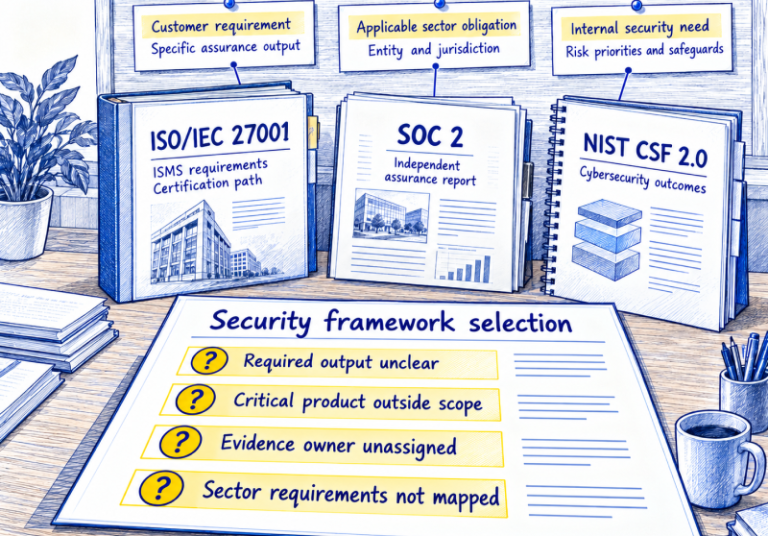
A security framework helps organizations structure cybersecurity priorities, but selecting the right approach depends on business risks, applicable obligations and stakeholder expectations....
Surbhi Bhutani
October 27, 2026
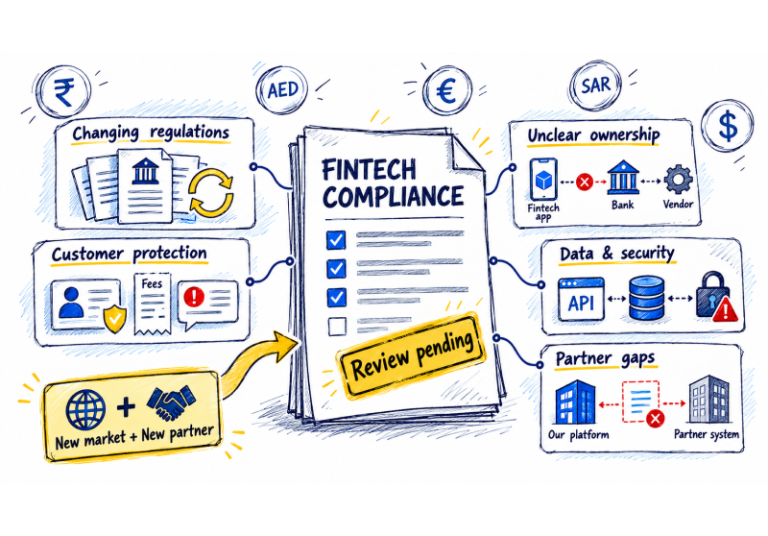
Fintech compliance depends on what a product does, which entities deliver it, and where customers, money, and data move. Mapping obligations across...
Surbhi Bhutani
October 26, 2026
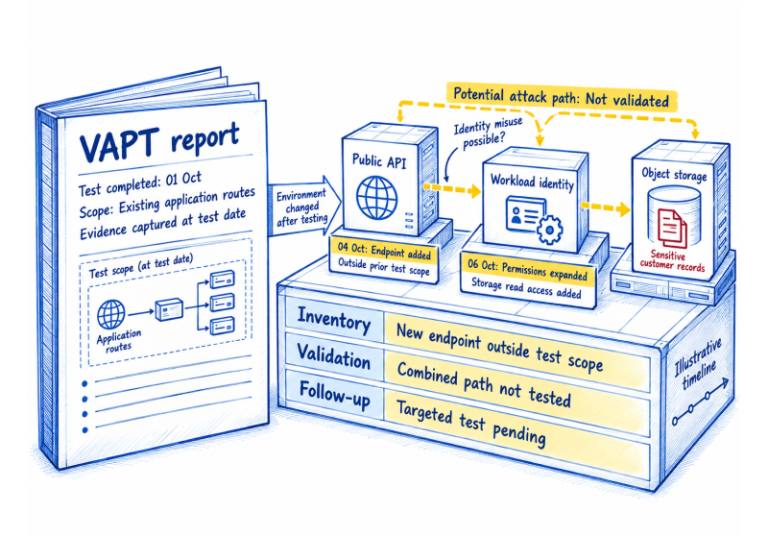
Cloud environments change with every deployment, identity update and configuration shift.Scanning can find weaknesses; scoped testing shows whether they combine into a...
Surbhi Bhutani
October 26, 2026
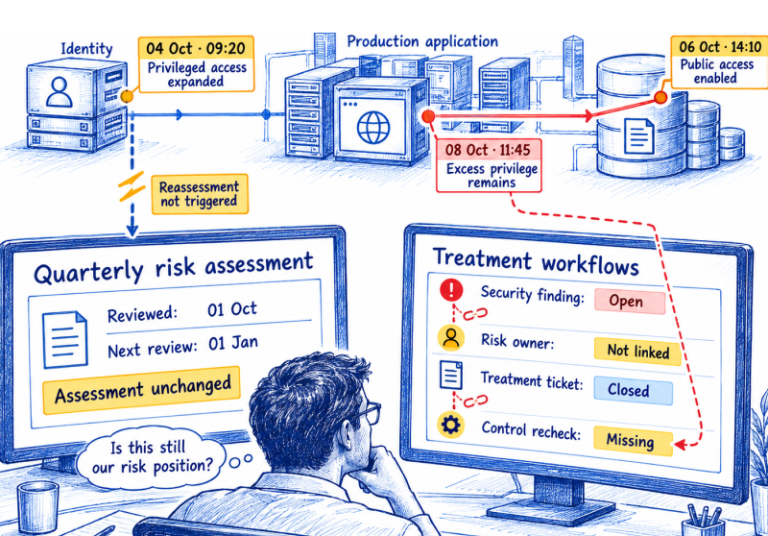
Risk management automation connects current operational evidence with structured risk assessments, monitoring, and accountable decisions. By reducing manual collection and follow-up, organizations...
Surbhi Bhutani
October 26, 2026
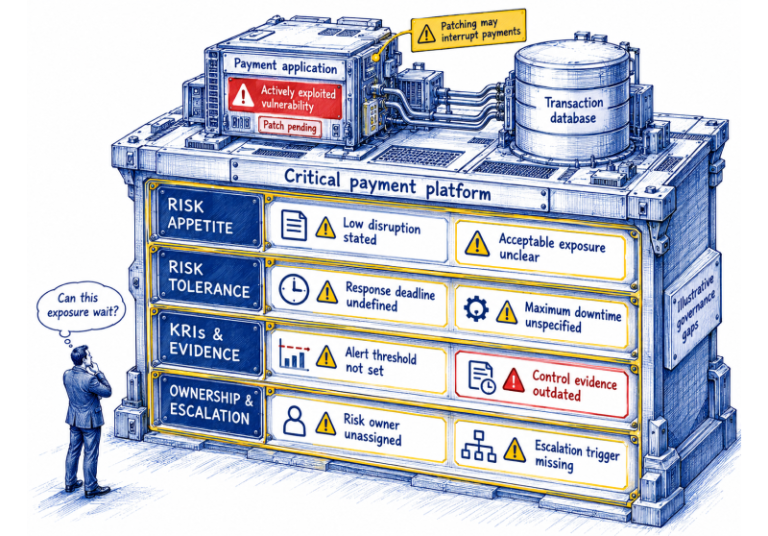
Risk appetite, risk tolerance, and risk capacity shape how organizations assess and manage cybersecurity risks. Establishing measurable thresholds, monitoring KRIs, and evaluating...
Surbhi Bhutani
October 21, 2026
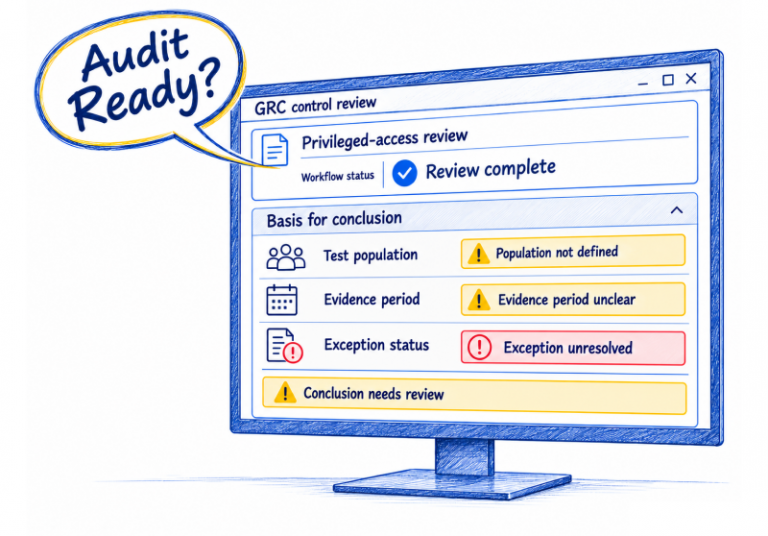
A platform can support a defensible audit trail, but it cannot guarantee a high-quality audit. Use a realistic demonstration, written acceptance criteria...
Surbhi Bhutani
October 21, 2026
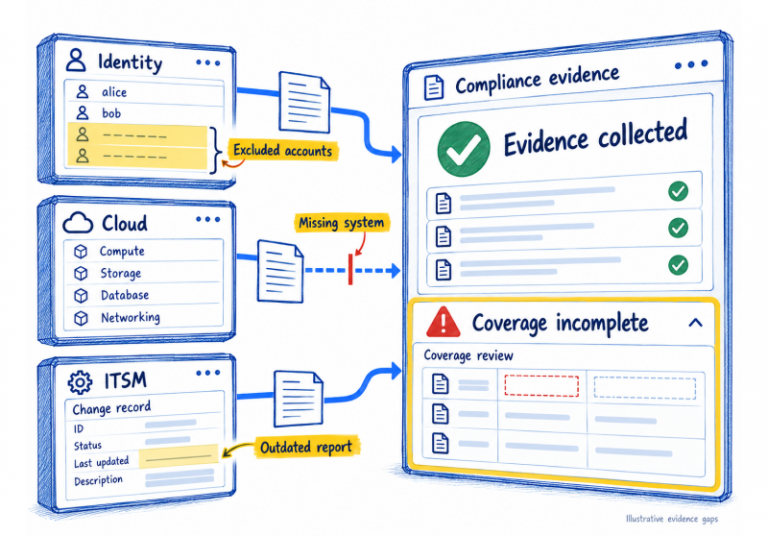
Automated evidence can save teams from repeated exports and audit-week searches. But capture is only the start: the evidence must still answer...
Surbhi Bhutani
October 21, 2026
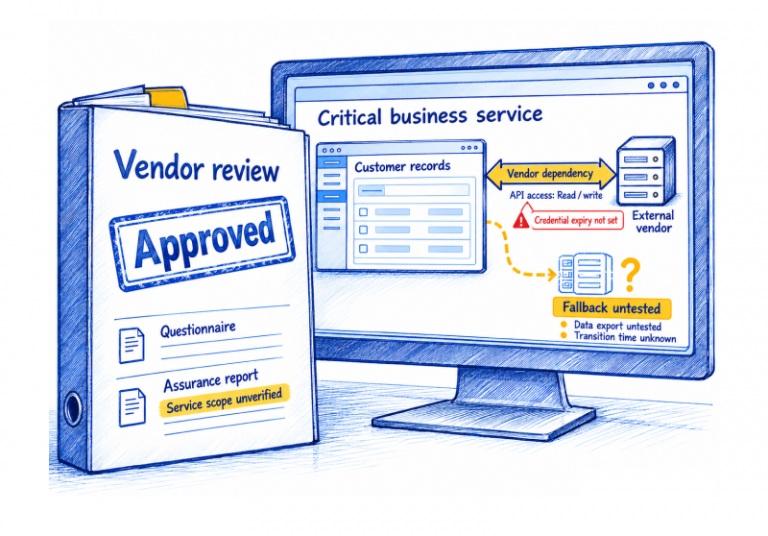
A vendor review should tell decision-makers what access and dependency they are accepting, what conditions must hold, and what would trigger a...
Surbhi Bhutani
October 20, 2026
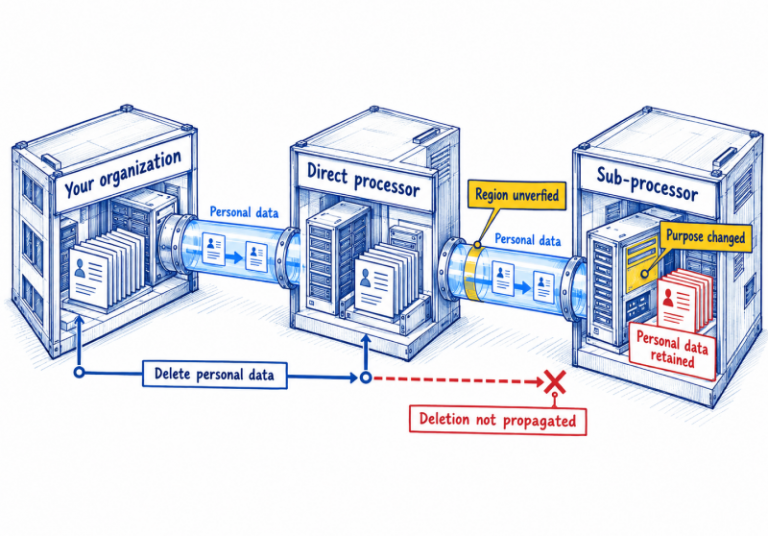
A direct vendor is only the first link in a personal-data chain. Build a program that keeps purpose, location, authorization, safeguards, and...
Surbhi Bhutani
October 19, 2026
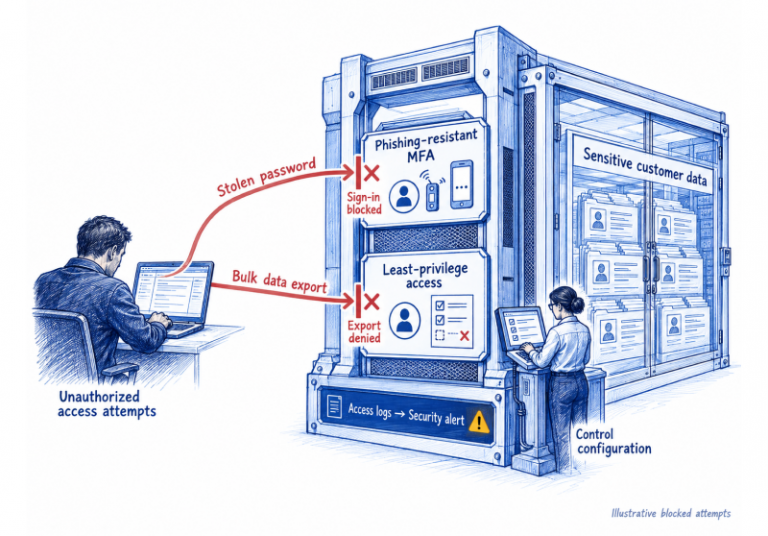
A practical guide to reducing the paths attackers can use to reach sensitive information. Build prevention around data, identity, and access decisions...
Surbhi Bhutani
October 19, 2026
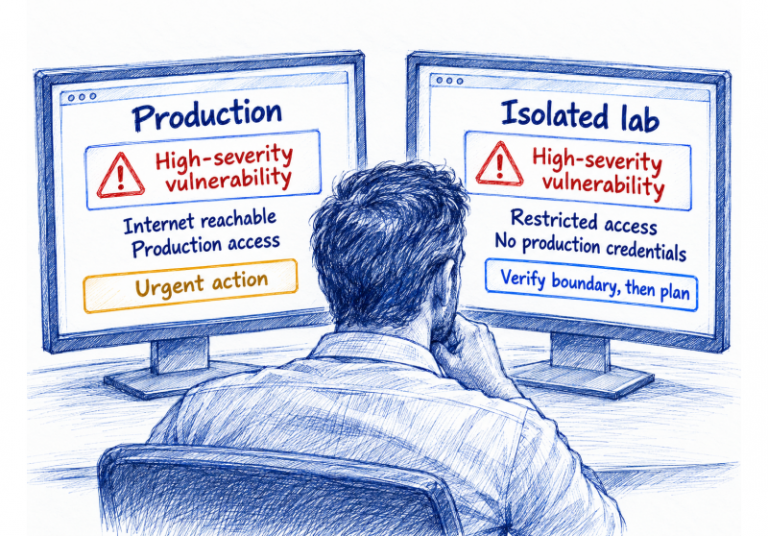
A practical guide for security and IT leaders deciding what to fix first.Use exploit evidence, real exposure, and business impact to create...
Surbhi Bhutani
October 16, 2026
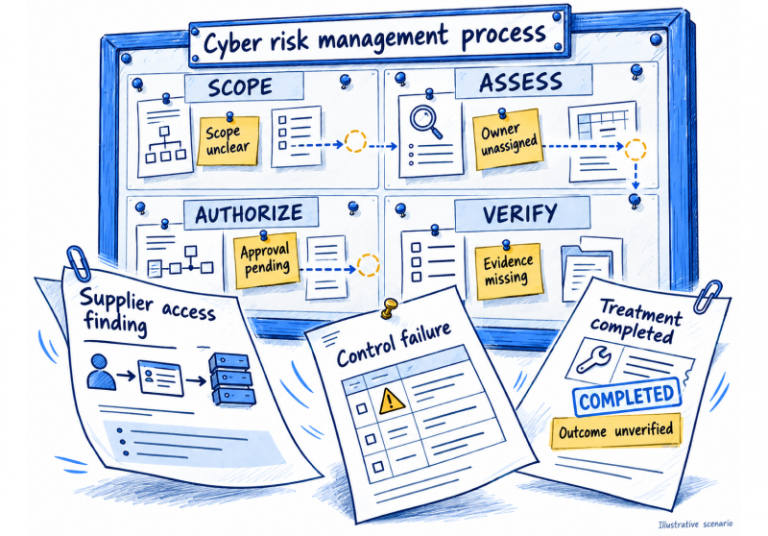
A cybersecurity risk management process should move from a defined business question to a decision, funded action, and evidence that the response...