
Surbhi Bhutani
October 16, 2026
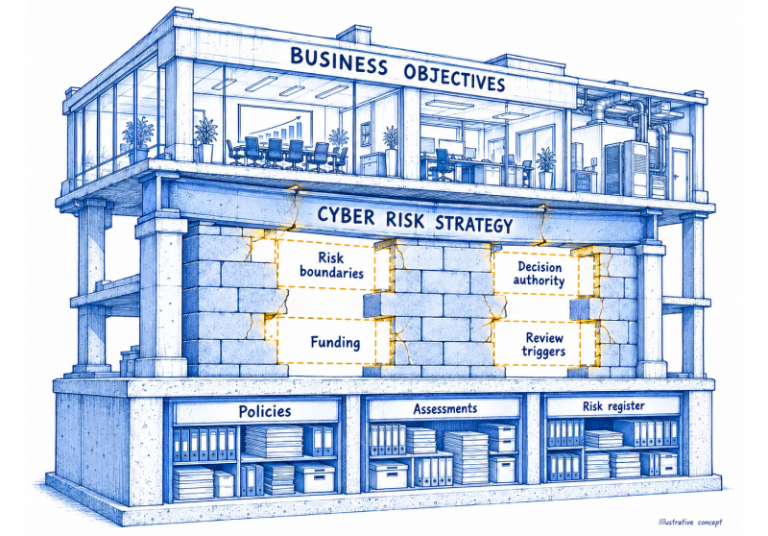
A cybersecurity risk management strategy should guide real choices about priorities, investment and acceptable exposure. This practical framework connects business objectives to...
Surbhi Bhutani
October 15, 2026
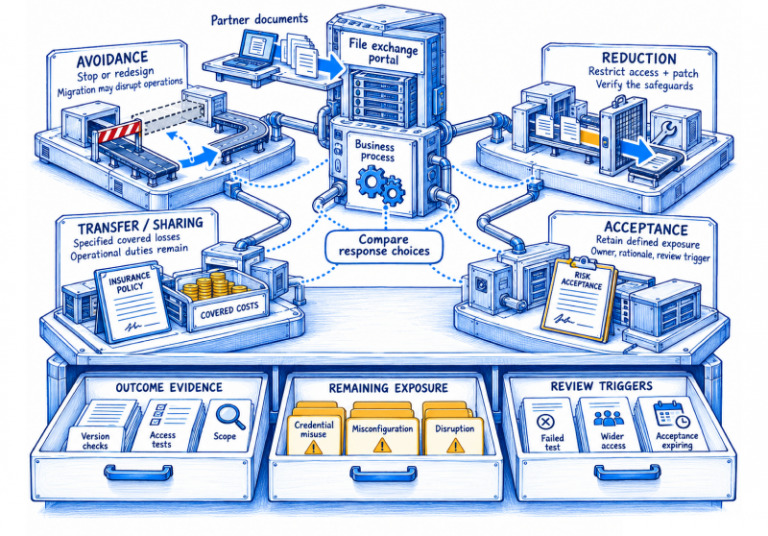
Risk mitigation is often used to mean reducing exposure, while risk treatment covers the full set of response choices. Learn how to...
Surbhi Bhutani
October 15, 2026
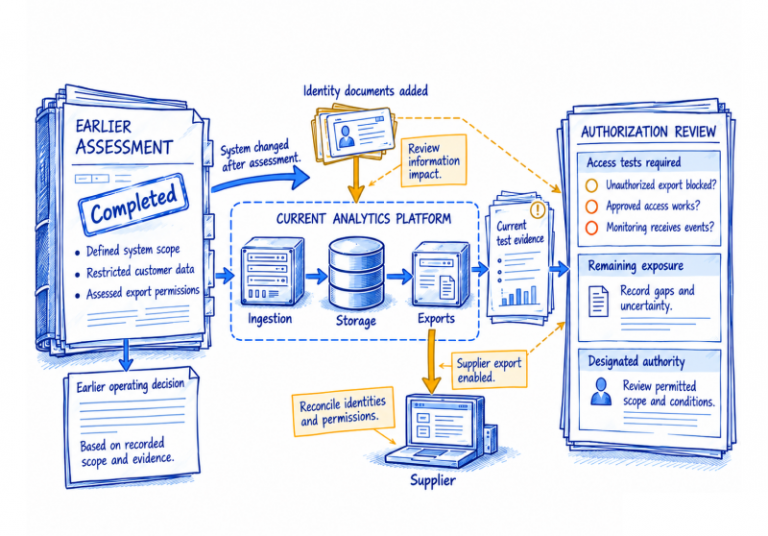
A risk management framework connects system scope, control evidence and accountable decisions. Applying NIST RMF means establishing why a system can operate,...
Surbhi Bhutani
October 15, 2026
A risk control matrix makes clear how a defined business risk is addressed, who owns the response, and what evidence shows the...
Surbhi Bhutani
October 14, 2026
Attack surface management helps security teams discover assets and access paths their existing inventories miss. Learn how external and internal discovery, contextual...
Surbhi Bhutani
October 14, 2026
Quantitative cyber risk assessment helps teams decide which security treatments justify their cost. Defined scenarios, current evidence and explicit uncertainty make the...
Surbhi Bhutani
October 13, 2026
How security leaders can design roles, handoffs and decision safeguards that help people contain incidents without creating a second failure. Human factors...
Surbhi Bhutani
October 13, 2026
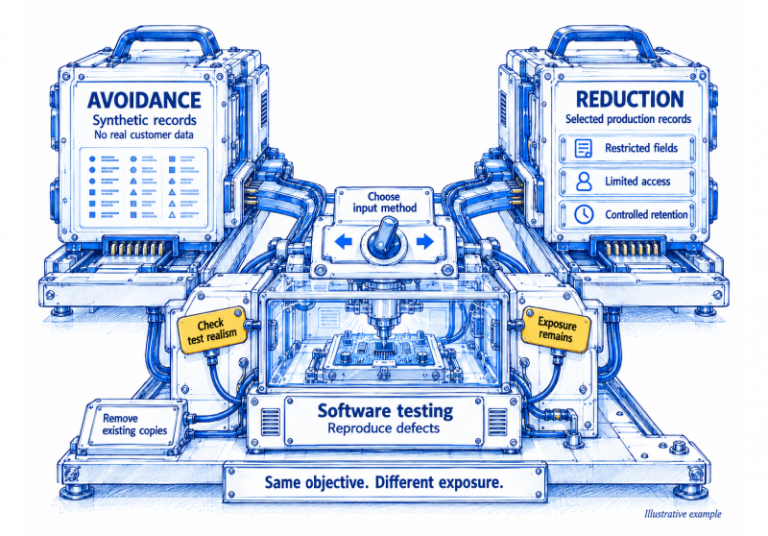
Measure whether decisions improveTrack time from an escalation trigger to acknowledgment by an authorized responder. Measure incomplete handoffs as a proportion of...
Surbhi Bhutani
October 12, 2026
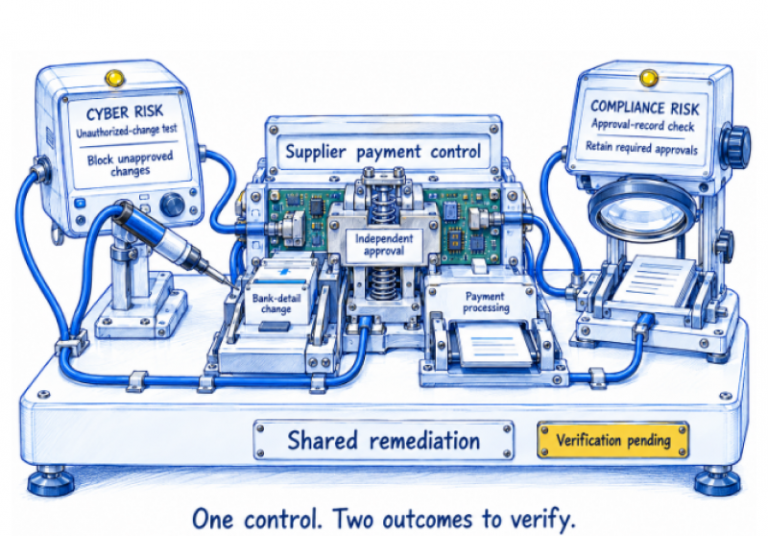
Cyber risk and compliance risk can share the same control weakness while requiring different decisions. Learn how mid-market teams can assess business...
Surbhi Bhutani
October 12, 2026
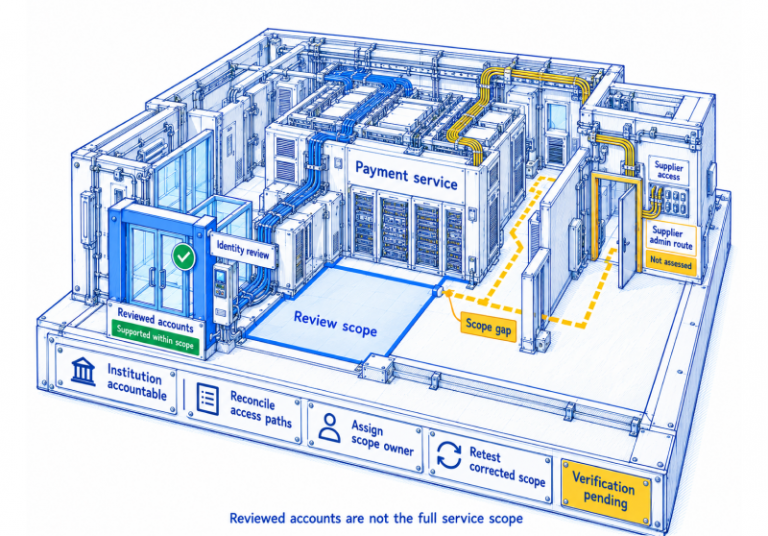
Financial services compliance needs evidence that supports decisions about critical services. Learn how to define control scope, assess supplier evidence, expose uncertainty...
Surbhi Bhutani
October 12, 2026
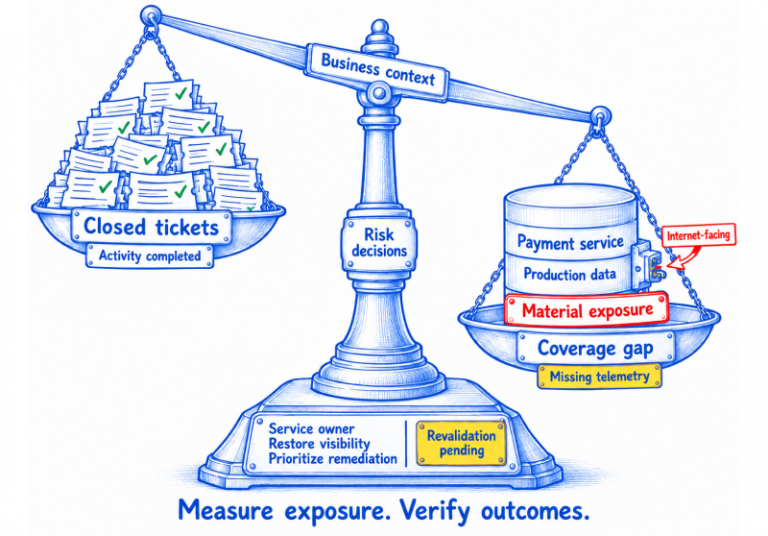
Useful cybersecurity metrics show where material exposure remains, who needs to act and whether corrective work reduced the risk. Learn how to...
Surbhi Bhutani
October 9, 2026
Integrations connect cloud, identity, endpoint and business systems to automate evidence collection and coordinate compliance workflows. They reduce repeated requests, support control...