
Surbhi Bhutani
October 9, 2026
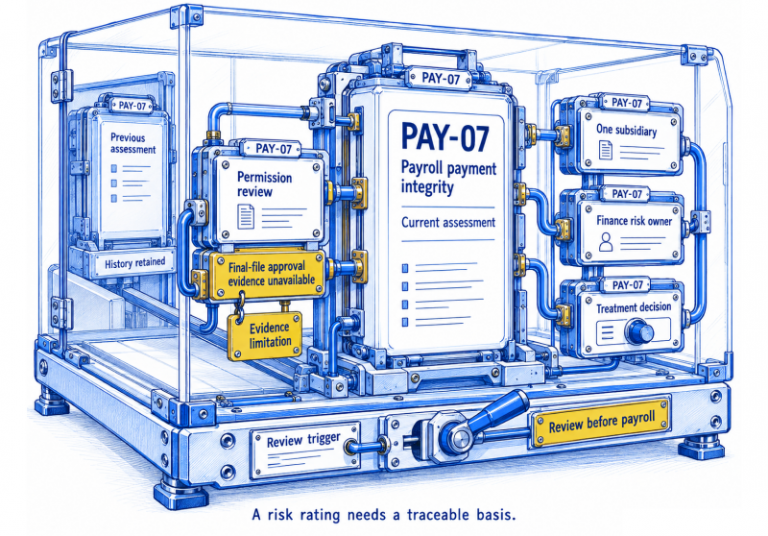
A risk rating needs a clear basis and a record of the decision behind it. Build risk entries that connect business scenarios...
Surbhi Bhutani
October 9, 2026
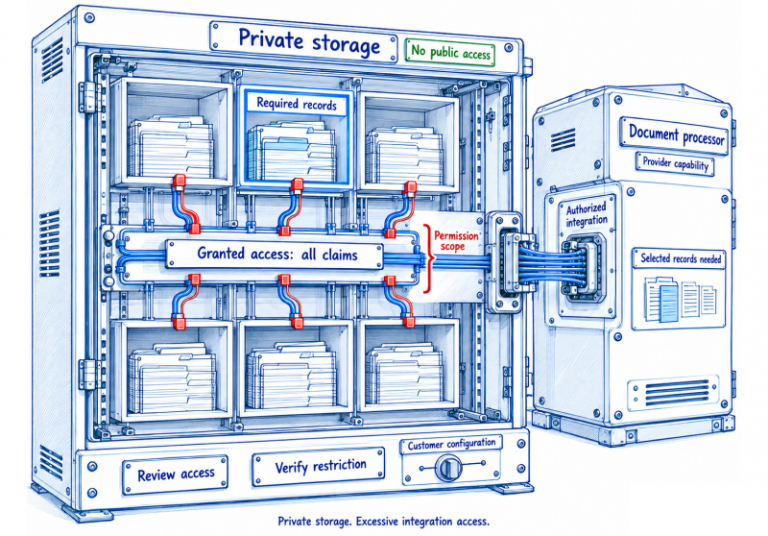
Cloud risk extends beyond configuration settings. Map identity access, data flows and provider responsibilities across connected services to identify hidden exposure, assign...
Surbhi Bhutani
October 7, 2026
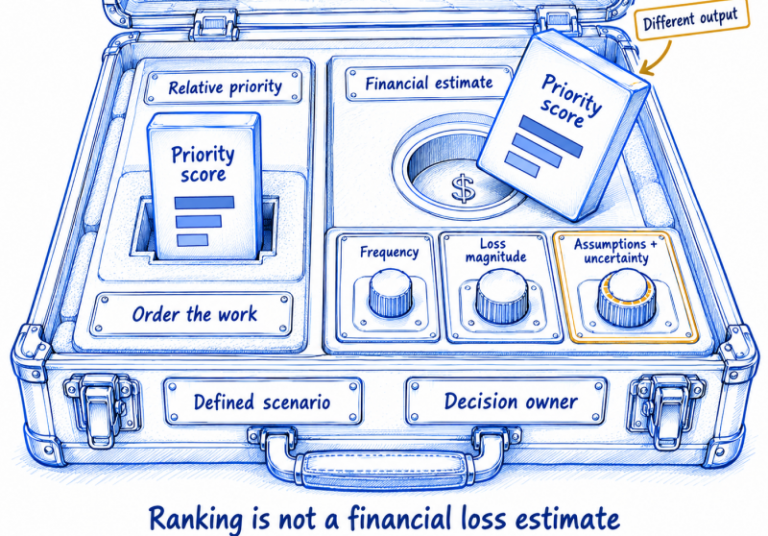
Different risk decisions need different outputs. Compare qualitative assessments, priority scores and quantitative loss estimates, and learn how to choose a method...
Surbhi Bhutani
October 4, 2026
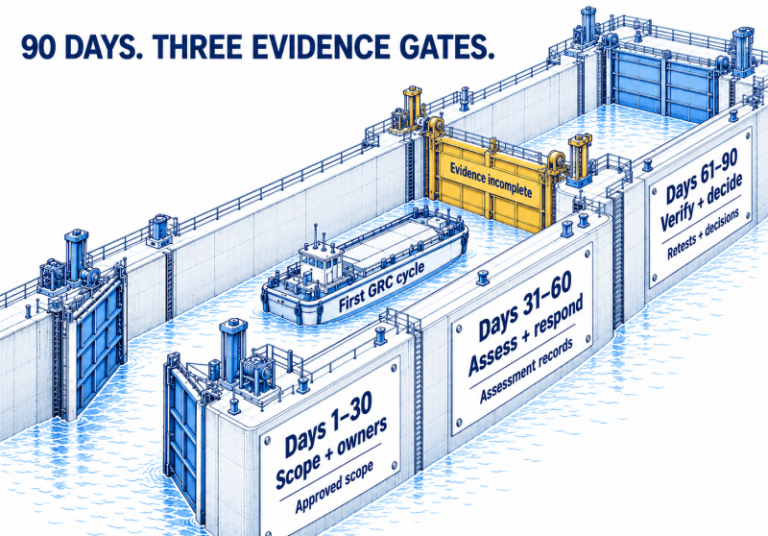
Establish a first GRC voyage in 90 days, with clear scope, accountable owners and evidence that supports control decisions. Follow three practical...
Surbhi Bhutani
October 3, 2026
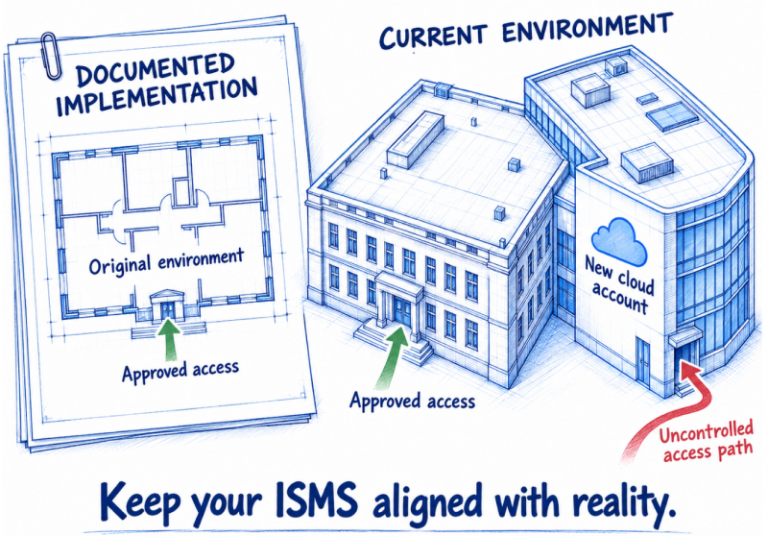
An effective ISO 27001 program keeps control scope, the Statement of Applicability and supporting evidence aligned as services, identities and suppliers change....
Surbhi Bhutani
September 25, 2026
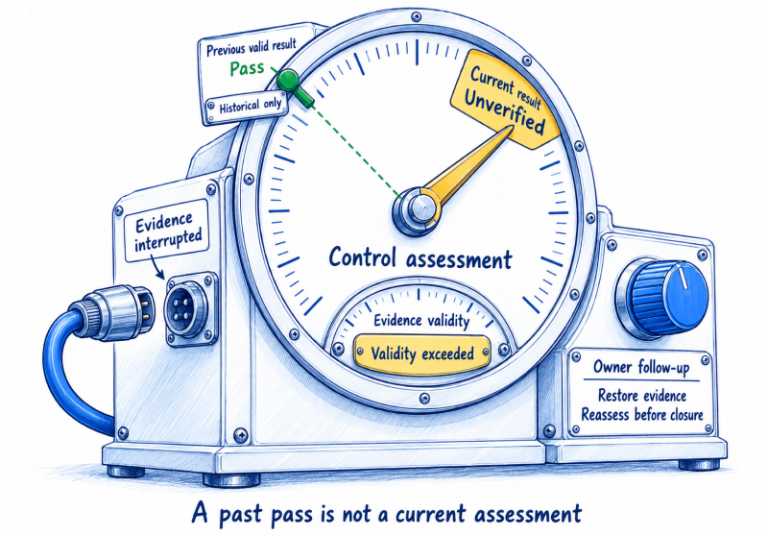
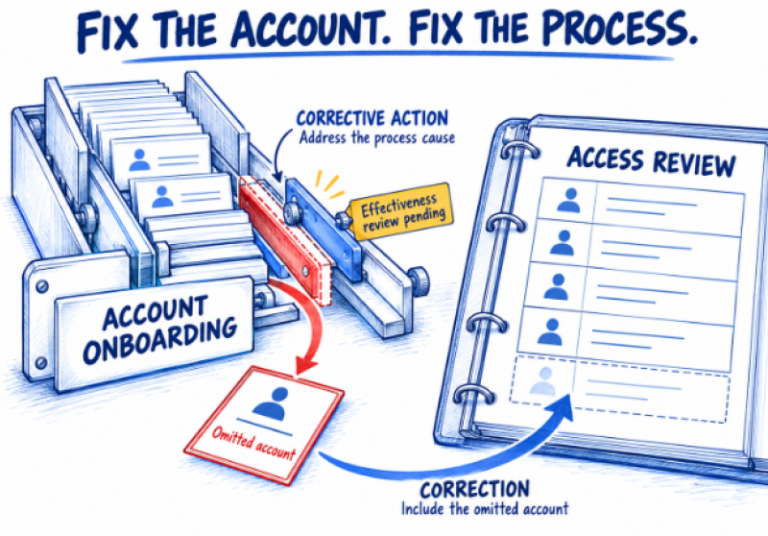
Compliance Monitoring in 2026: Detect Evidence Gaps and Verify Control ResultsA passing result is only useful when its coverage, evidence and test...
Surbhi Bhutani
September 25, 2026
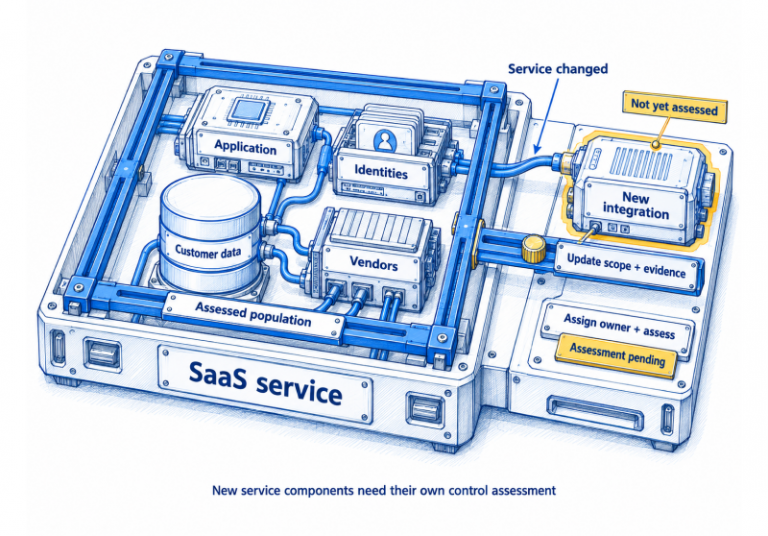
Build a SaaS compliance program around the services you deliver and the obligations that apply. Use this practical checklist to clarify cloud...
Surbhi Bhutani
September 25, 2026
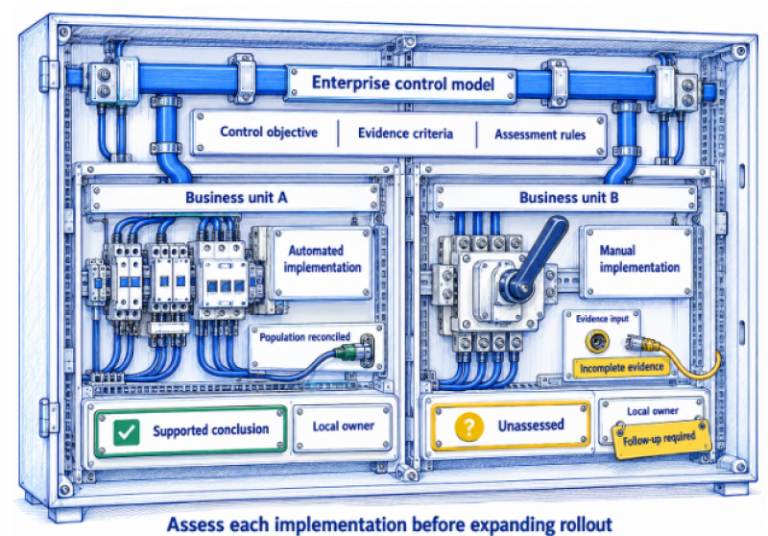
Enterprise GRC needs consistent assessments across business units while preserving local responsibilities and obligations. Establish clear ownership, reliable evidence and a complete...
Surbhi Bhutani
September 25, 2026
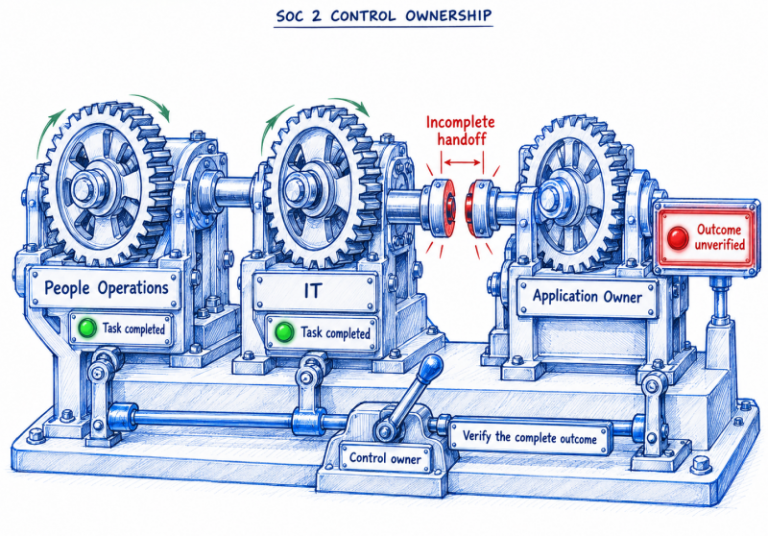
Build a practical SOC 2 control list with clear owners, reliable evidence and complete handoffs across teams. Learn how to manage responsibilities...
Surbhi Bhutani
September 25, 2026
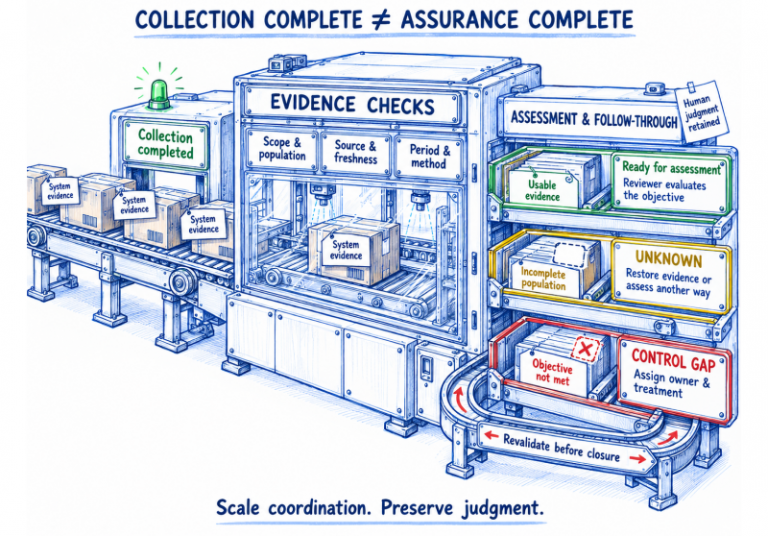
Help lean GRC teams support growing compliance demands with clear ownership, reliable evidence and selective automation. Reduce repeated follow-up, keep exceptions visible...
Surbhi Bhutani
September 24, 2026
Prepare for ISO 27001 certification with a clear scope, traceable evidence and accountable control owners. Understand the audit stages, timeline and cost...