Arjun Mehrishi
October 20, 2026
Vulnerability management confirms and treats known weaknesses; attack surface management shows where reachable assets and paths exist. Connect them to make exposure...

Arjun Mehrishi
October 20, 2026
Understand what a weakened control exposes, which operations depend on it and how to verify that corrective action has restored protection. Cybersecurity...
Arjun Mehrishi
October 19, 2026
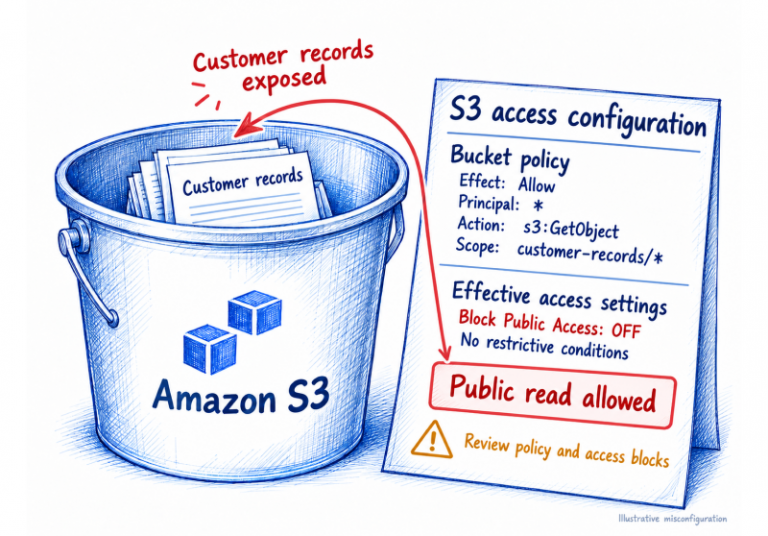
A practical guide to account boundaries, identity, guardrails, and operations in AWS.Build a secure foundation that lets workload teams move without relying...
Arjun Mehrishi
October 19, 2026
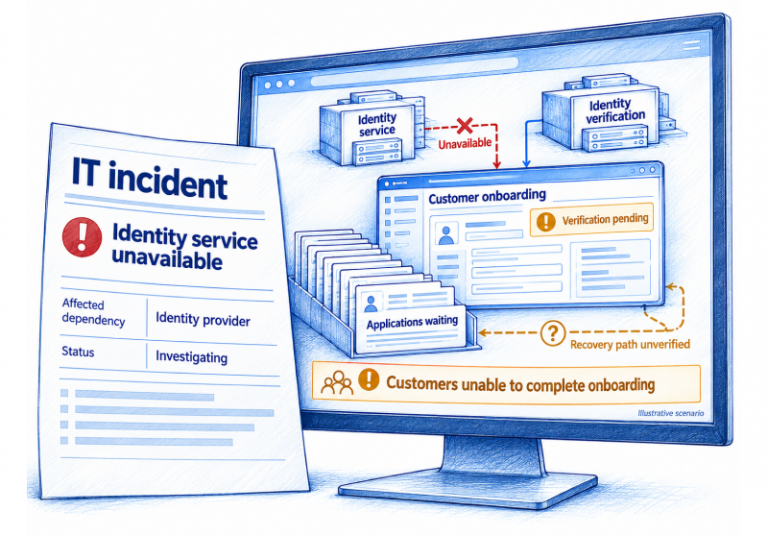
A practical guide for security, IT, and GRC leaders to identify concentration risk and improve portfolio decisions. IT risk management is harder...
Arjun Mehrishi
October 16, 2026
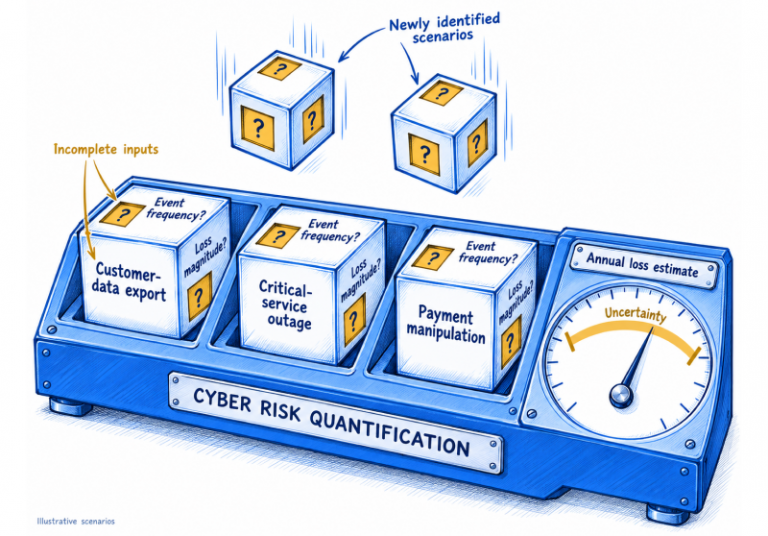
Quantitative cyber risk analysis can help leaders compare security choices, but a precise-looking number is only as sound as its scenario and...
Arjun Mehrishi
October 16, 2026
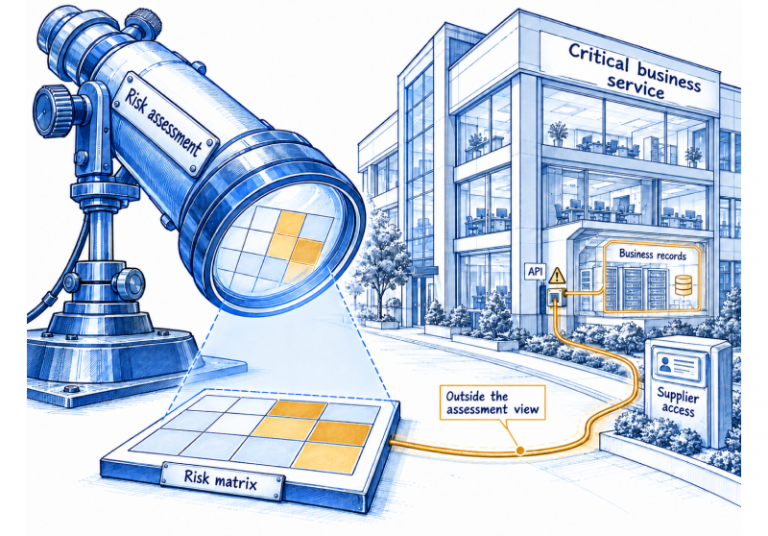
Different risk questions need different methods. Compare practical techniques, see how two methods reach different decisions on the same supplier scenario, and...
Arjun Mehrishi
October 15, 2026
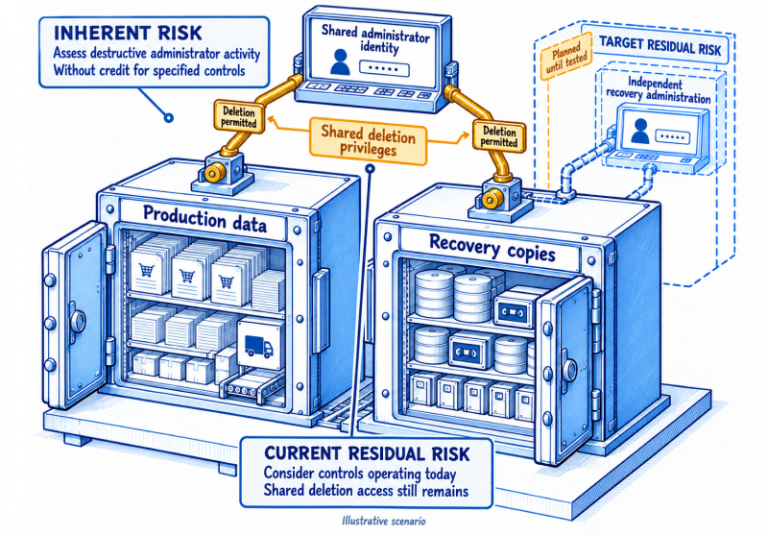
Inherent risk vs residual risk is a comparison between exposure without specified risk responses and exposure after those responses. The distinction helps...
Arjun Mehrishi
October 14, 2026
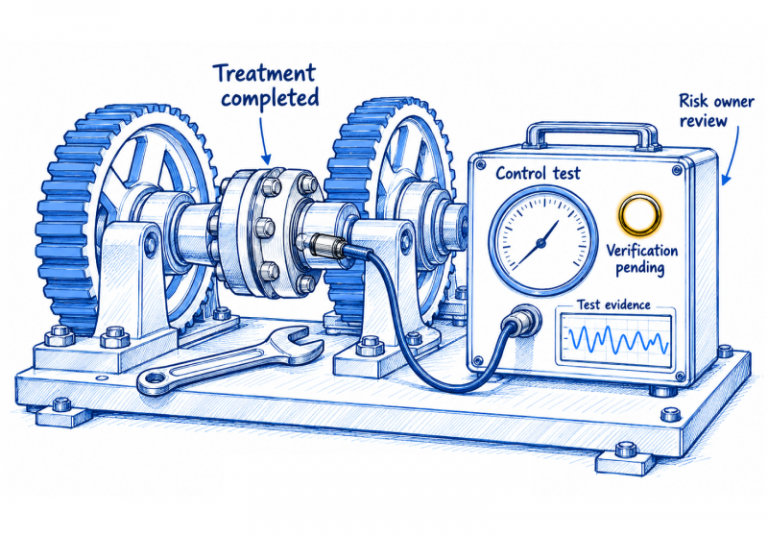
Operational risk management helps leaders understand how everyday activity can disrupt critical services, and what to do before a weakness becomes a...
Arjun Mehrishi
October 14, 2026
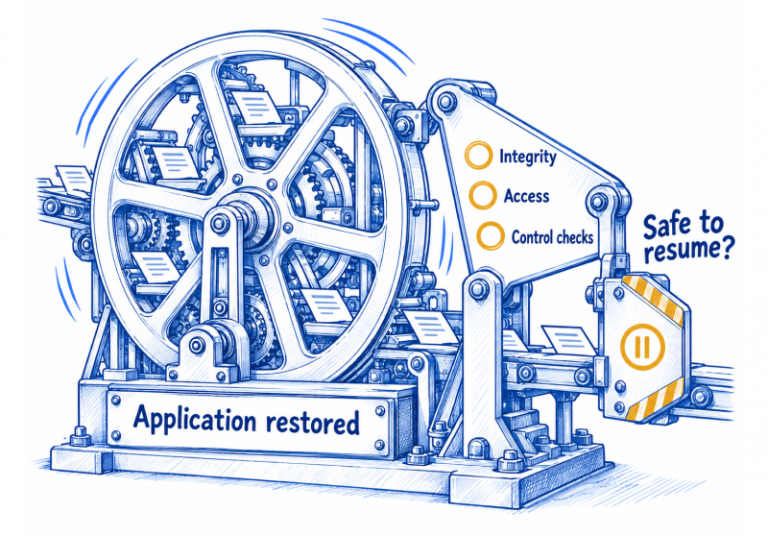
Business impact analysis helps organizations understand how disruption affects critical services and set recovery priorities. This article explains how to assess impacts...
Arjun Mehrishi
October 14, 2026
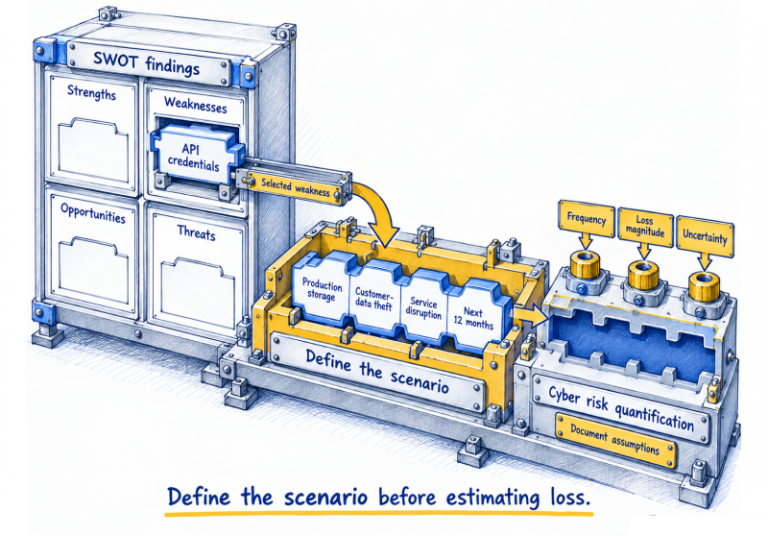
SWOT analysis can help security leaders identify strategic concerns, while cyber risk quantification can test how those concerns may affect the business....
Arjun Mehrishi
October 13, 2026
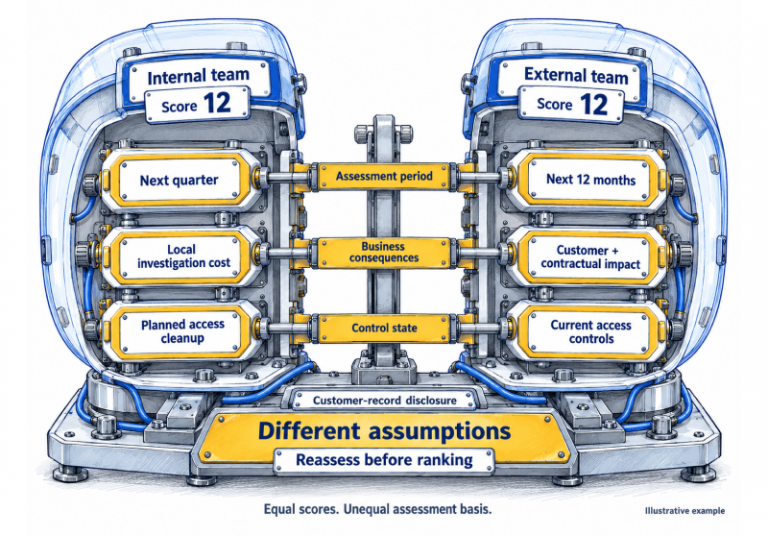
Learn how to calculate risk scores, reconcile conflicting ratings and compare internal failures with external threats without distorting management priorities. The method...
Arjun Mehrishi
October 12, 2026
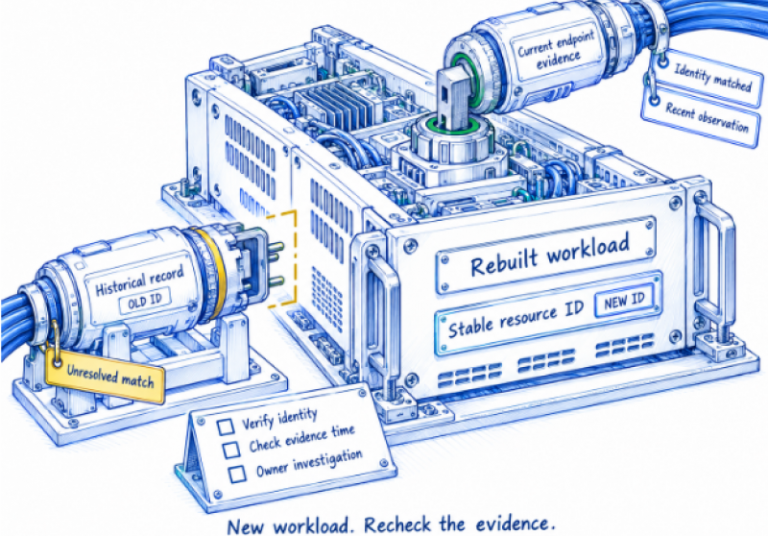
Cyber Asset Attack Surface Management connects fragmented asset records so teams can investigate exposure and security coverage. Its value depends on explainable...
Arjun Mehrishi
October 12, 2026
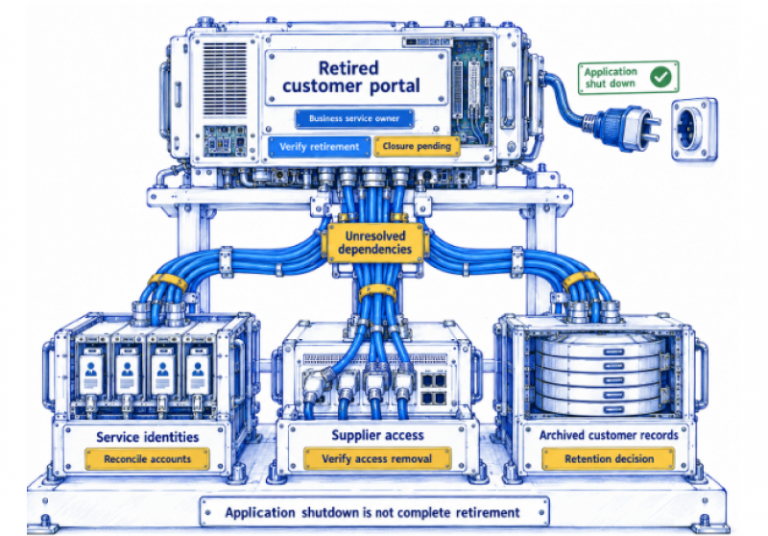
IT governance, risk management, and compliance (IT GRC) should help a CISO answer a difficult operational question: when technology changes, do the...
Arjun Mehrishi
October 12, 2026
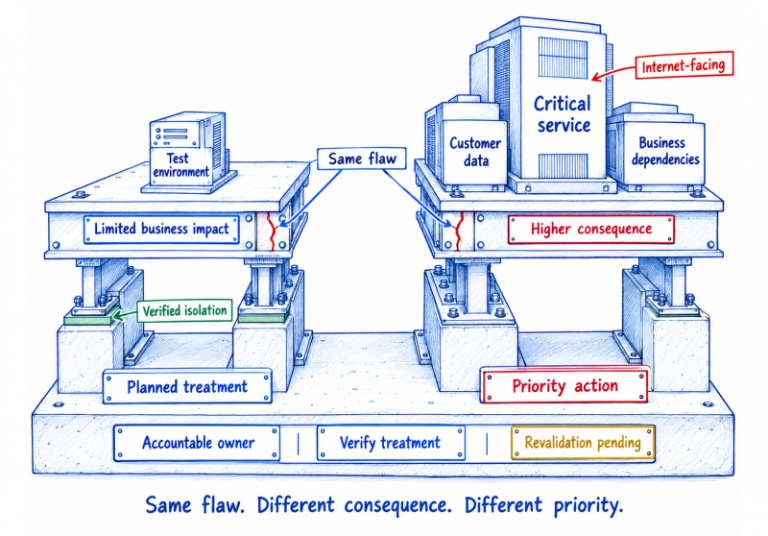
A cybersecurity risk score should explain why an exposure matters and what action it requires. Learn how to combine threat signals, reachability,...
Arjun Mehrishi
October 12, 2026
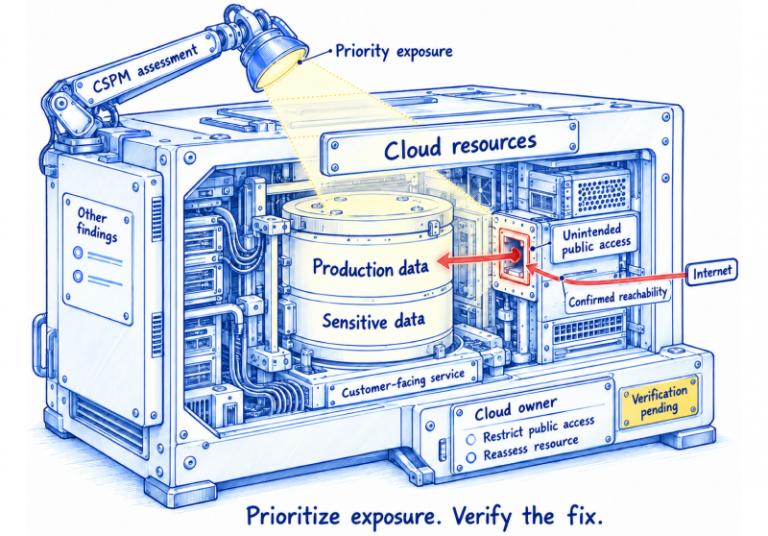
Cloud security posture management helps teams find configuration gaps and understand which exposures matter most. Learn how to establish coverage, prioritize findings,...
Arjun Mehrishi
October 12, 2026
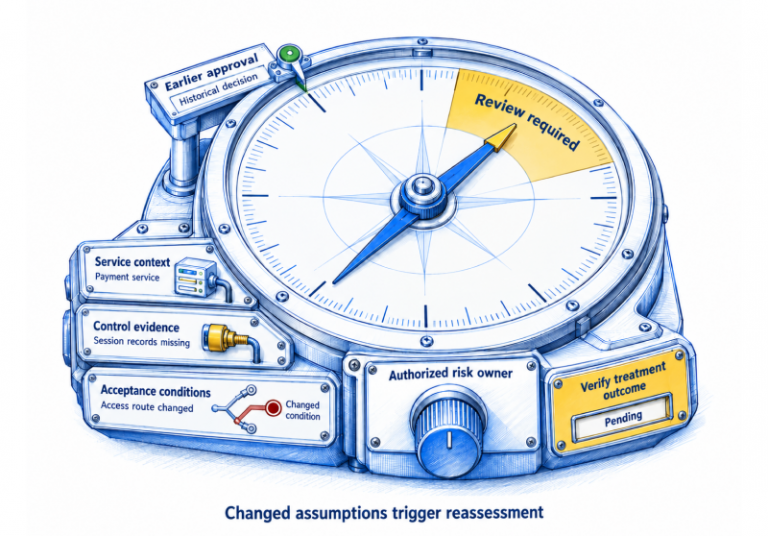
Effective enterprise GRC connects cyber risk to business services, current control evidence and accountable owners. Learn how to reassess decisions when conditions...
Arjun Mehrishi
October 8, 2026
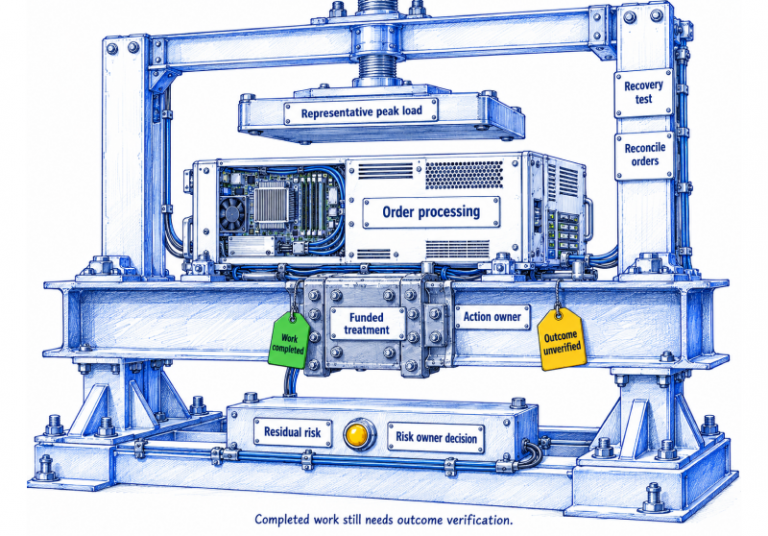
Risk decisions need funding, ownership and follow-through. Build a risk management plan that connects response choices to accountable actions, tracks delivery and...
Arjun Mehrishi
October 4, 2026
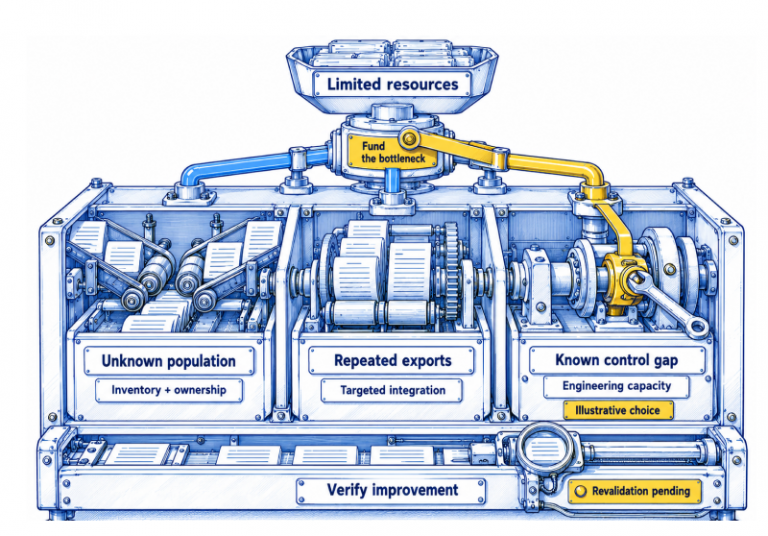
Make limited security budgets count by focusing on critical services, reliable evidence and accountable action. Learn how mid-market teams can identify control...
Arjun Mehrishi
October 4, 2026
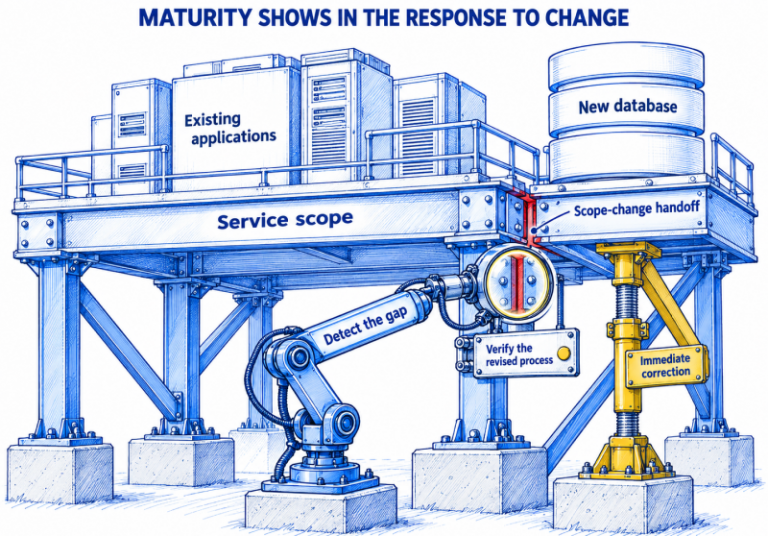
Help lean GRC teams support growing compliance demands with clear ownership, reliable evidence and selective automation. Reduce repeated follow-up, keep exceptions visible...
Arjun Mehrishi
October 3, 2026
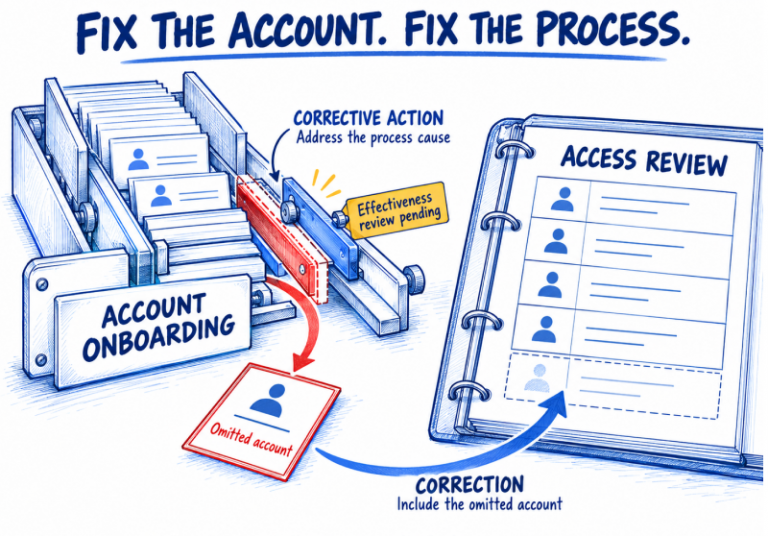
Prepare for ISO 27001 certification with a clear scope, traceable evidence and accountable control owners. Understand the audit stages, timeline and cost...
Arjun Mehrishi
October 2, 2026
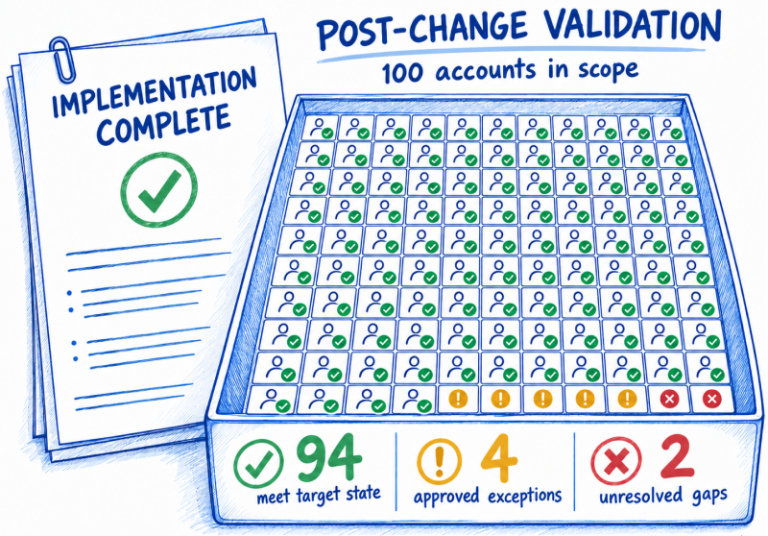
An approved change can still leave a security control in the wrong state. Connect ISO 27001 change management with post-change validation to...
Arjun Mehrishi
October 2, 2026
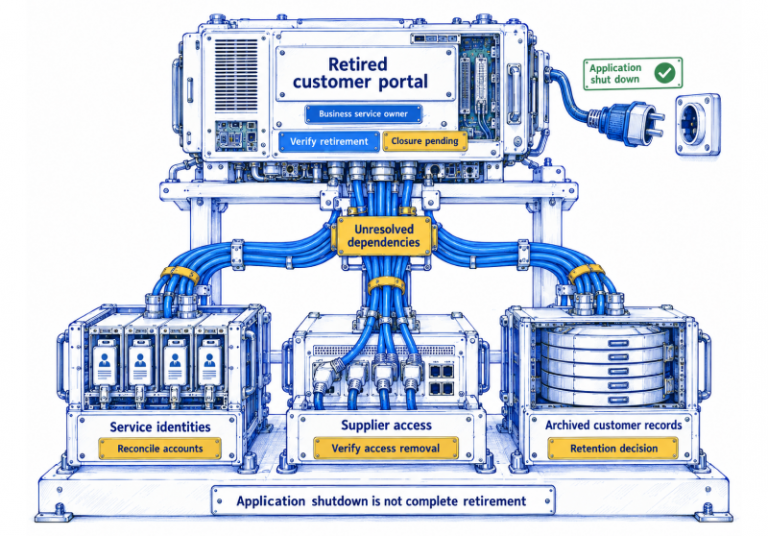
IT governance, risk management, and compliance (IT GRC) should help a CISO answer a difficult operational question: when technology changes, do the...
Arjun Mehrishi
September 25, 2026
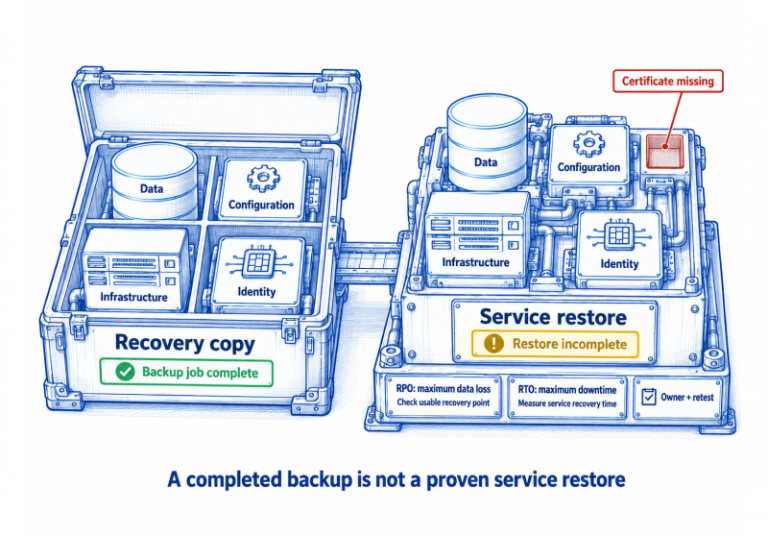
A successful backup job does not prove that a service can be restored. Use this checklist to define recovery coverage, set RPO...
Arjun Mehrishi
September 25, 2026
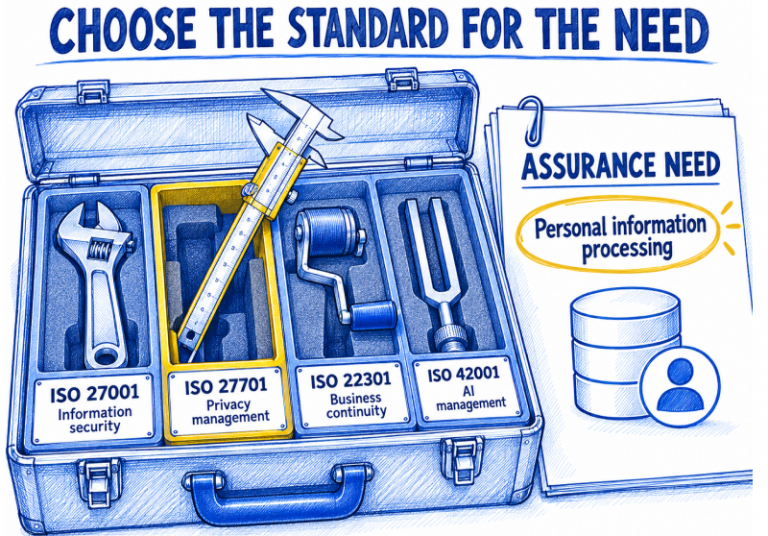
Choose ISO security standards based on your business needs, responsibilities and the assurance stakeholders expect. Compare security, privacy, cloud, continuity and AI...