
Arjun Mehrishi
October 26, 2026
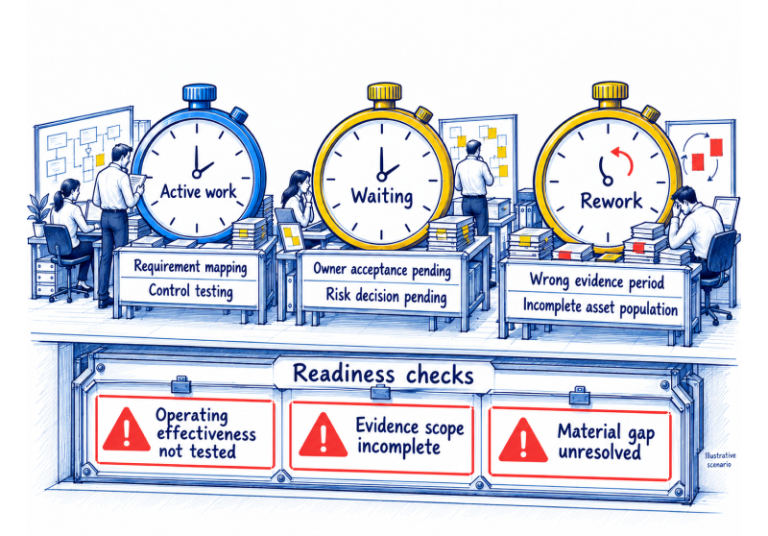
Time to compliance helps CISOs understand where audit preparation stalls and how to reduce avoidable delays. Clear milestones, accountable owners, and validated...
Arjun Mehrishi
October 26, 2026
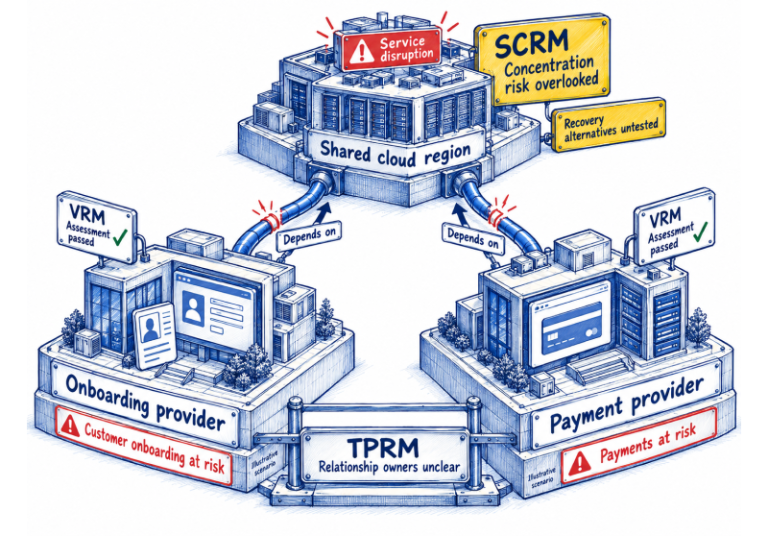
SCRM, TPRM, and VRM address different layers of external business risk, from individual suppliers to interconnected supply chains. Understanding their scope and...
Arjun Mehrishi
October 26, 2026
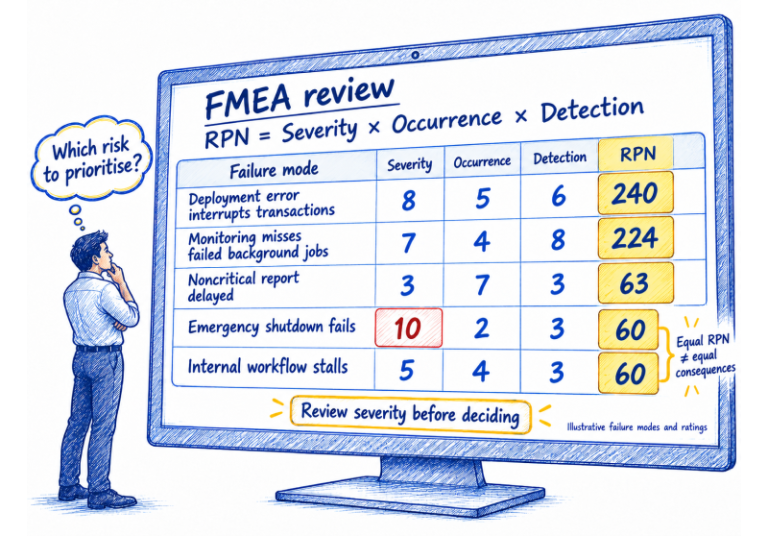
Risk Priority Number (RPN) helps teams compare potential failures through their severity, likelihood of occurrence, and difficulty of detection. Consistent scoring, practical...
Arjun Mehrishi
October 21, 2026
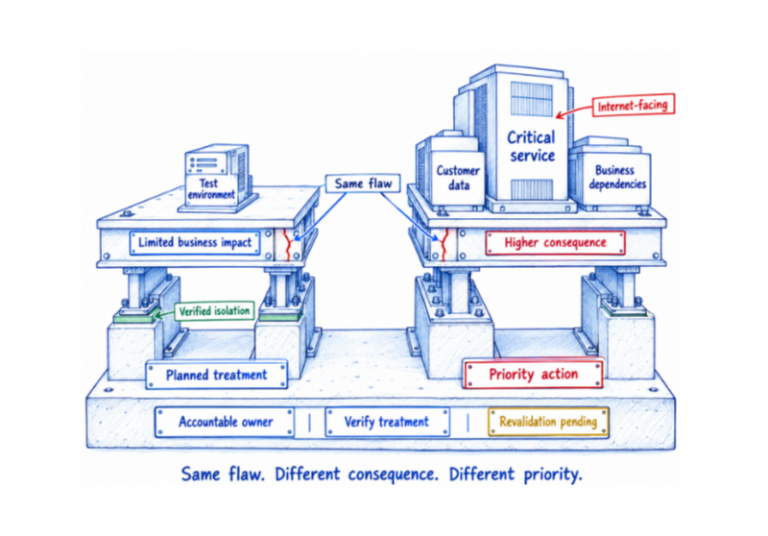
A cybersecurity risk score should explain why an exposure matters and what action it requires. Learn how to combine threat signals, reachability,...
Arjun Mehrishi
October 21, 2026
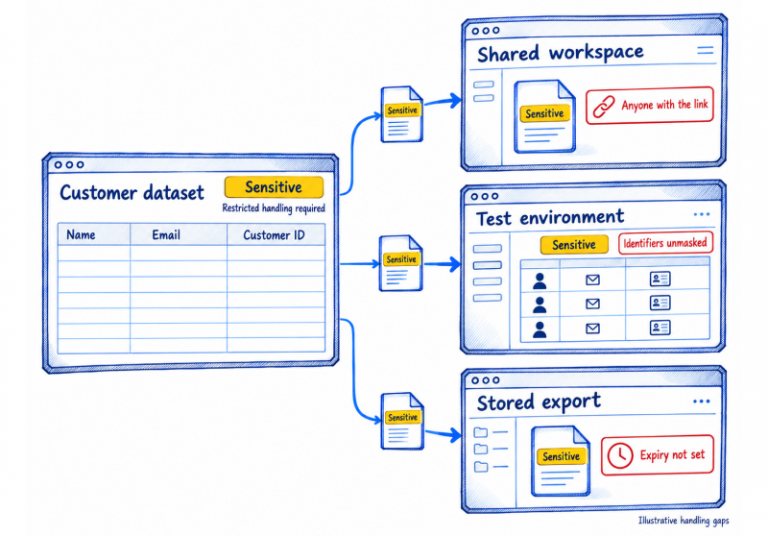
Define labels that guide access, sharing and disposal. This article explains how to apply them across data copies, assign decisions and connect...
Arjun Mehrishi
October 20, 2026
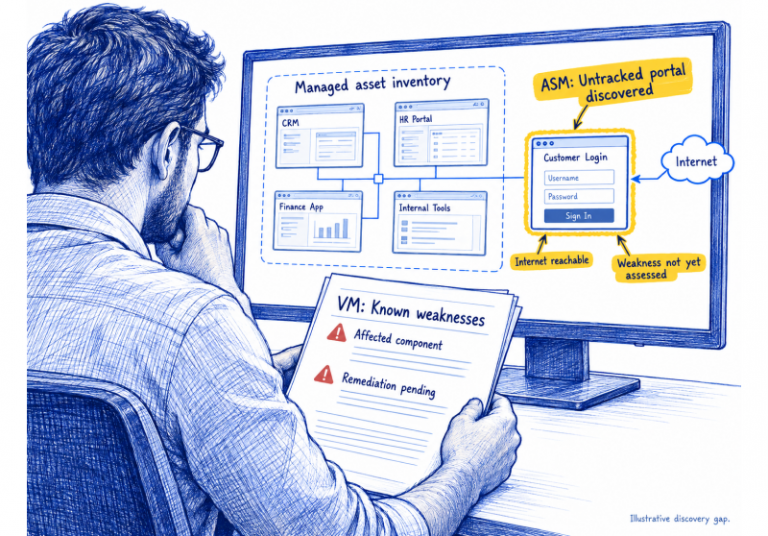
Vulnerability management confirms and treats known weaknesses; attack surface management shows where reachable assets and paths exist. Connect them to make exposure...
Arjun Mehrishi
October 20, 2026
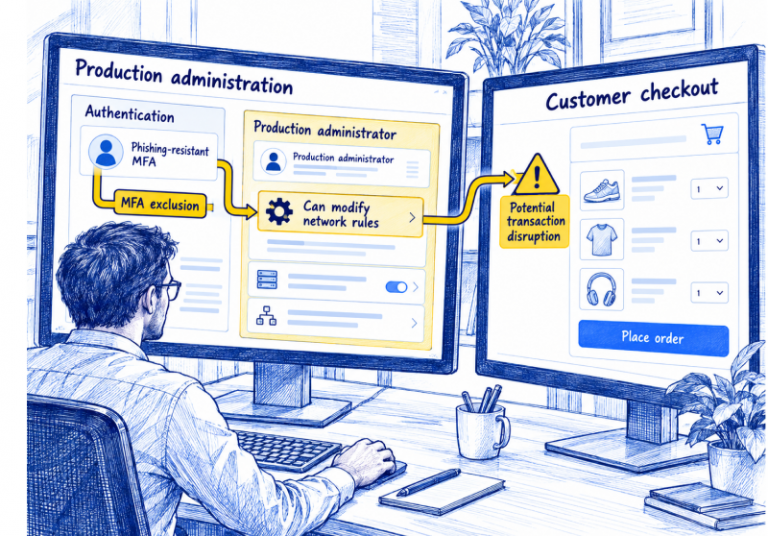
Understand what a weakened control exposes, which operations depend on it and how to verify that corrective action has restored protection.Cybersecurity control...
Arjun Mehrishi
October 19, 2026
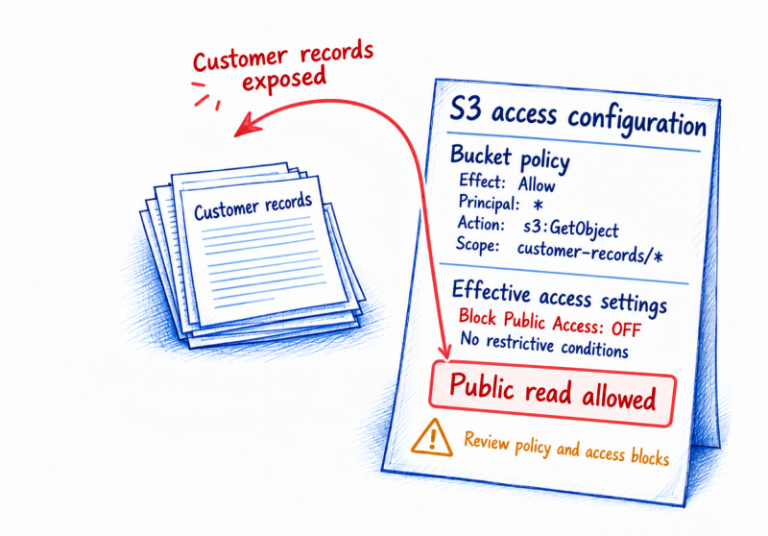
A practical guide to account boundaries, identity, guardrails, and operations in AWS.Build a secure foundation that lets workload teams move without relying...
Arjun Mehrishi
October 19, 2026
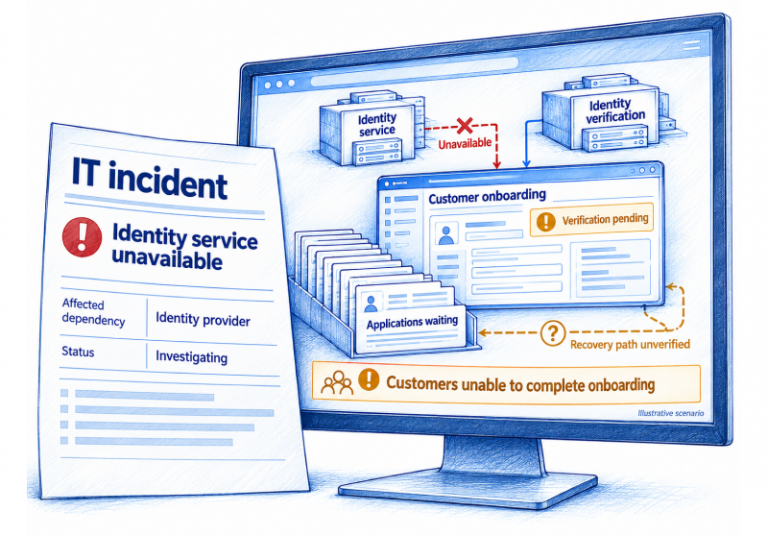
Executives need to understand material changes, business exposure, decisions required and limits to confidence. Control owners need the affected populations, supporting evidence,...
Arjun Mehrishi
October 16, 2026
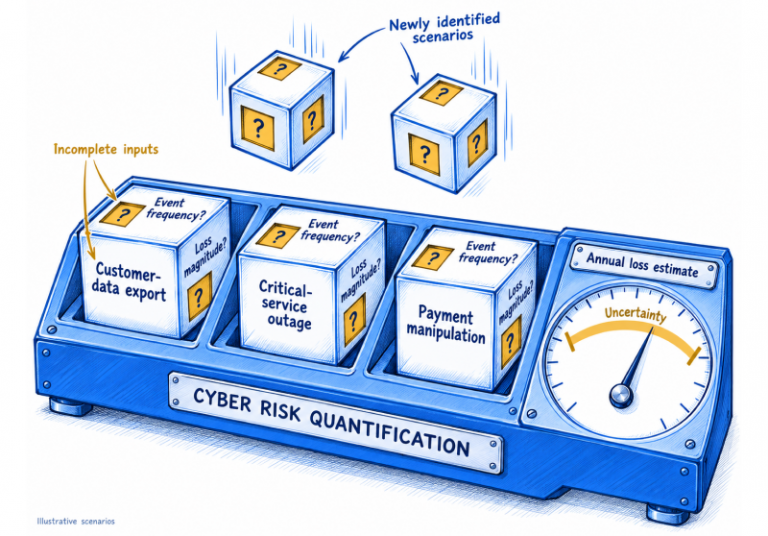
Quantitative cyber risk analysis can help leaders compare security choices, but a precise-looking number is only as sound as its scenario and...
Arjun Mehrishi
October 16, 2026
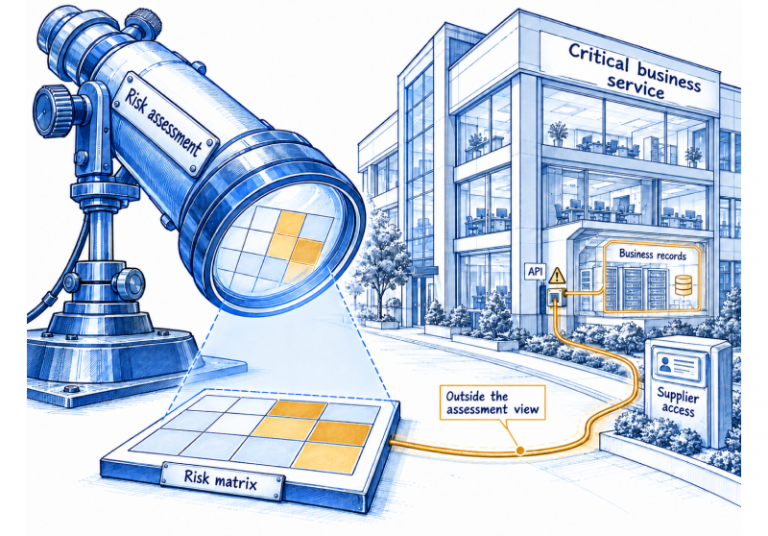
Different risk questions need different methods. Compare practical techniques, see how two methods reach different decisions on the same supplier scenario, and...
Arjun Mehrishi
October 15, 2026
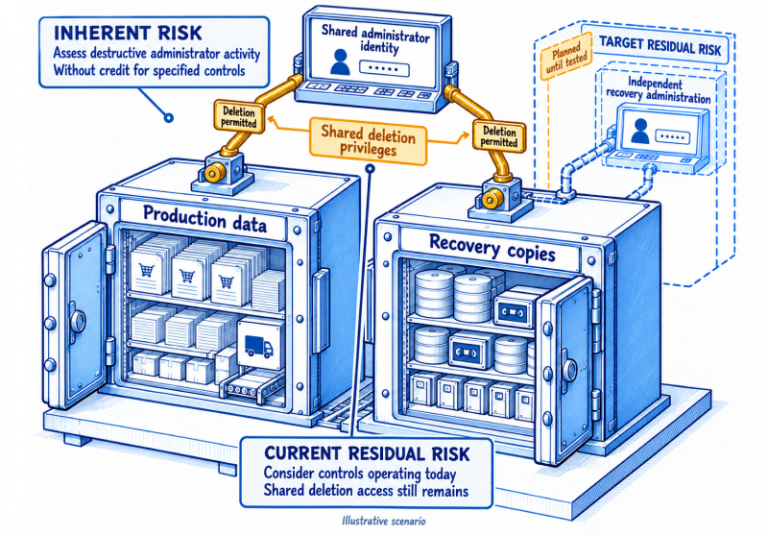
Inherent risk vs residual risk is a comparison between exposure without specified risk responses and exposure after those responses. The distinction helps...