
Arjun Mehrishi
October 14, 2026
Operational risk management helps leaders understand how everyday activity can disrupt critical services, and what to do before a weakness becomes a...
Arjun Mehrishi
October 14, 2026
Business impact analysis helps organizations understand how disruption affects critical services and set recovery priorities. This article explains how to assess impacts...
Arjun Mehrishi
October 14, 2026
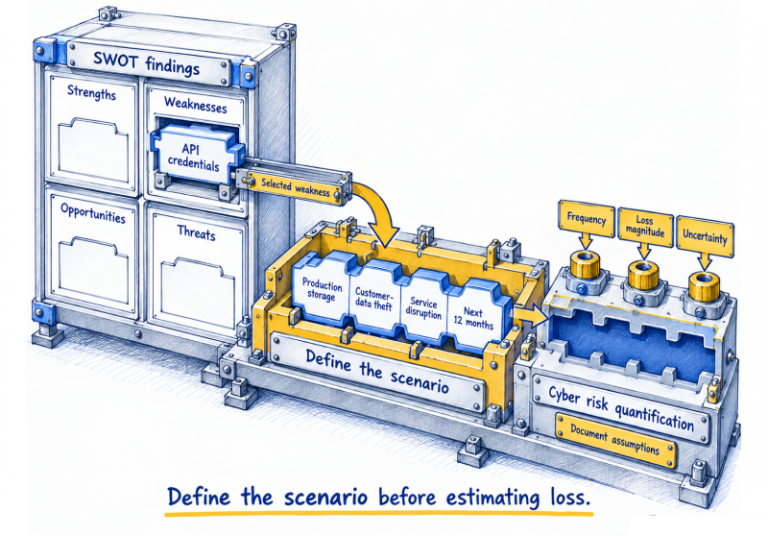
SWOT analysis can help security leaders identify strategic concerns, while cyber risk quantification can test how those concerns may affect the business....
Arjun Mehrishi
October 13, 2026
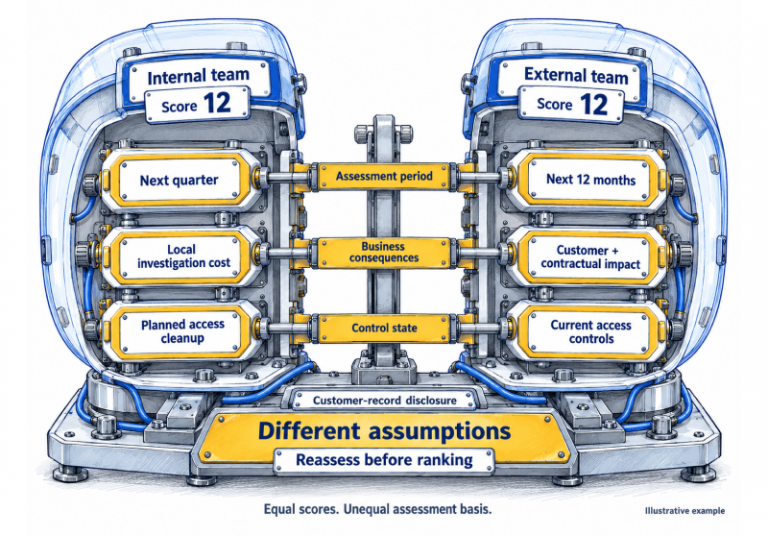
Learn how to calculate risk scores, reconcile conflicting ratings and compare internal failures with external threats without distorting management priorities. The method...
Arjun Mehrishi
October 12, 2026
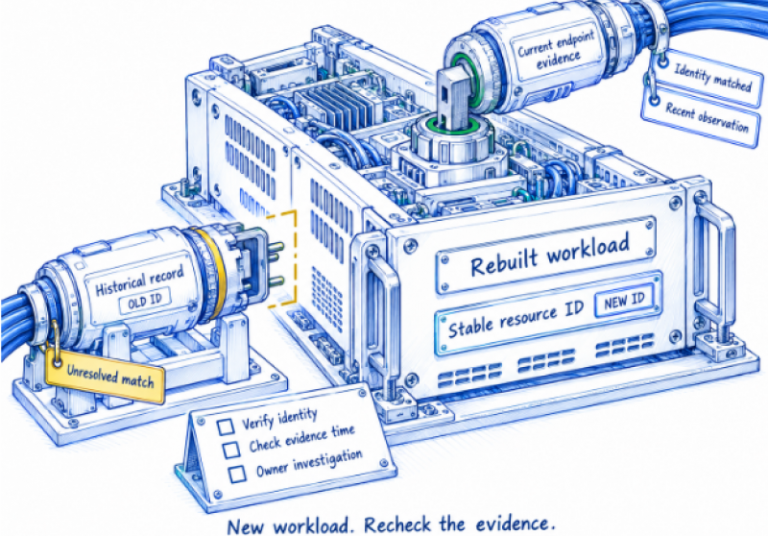
Cyber Asset Attack Surface Management connects fragmented asset records so teams can investigate exposure and security coverage. Its value depends on explainable...
Arjun Mehrishi
October 12, 2026
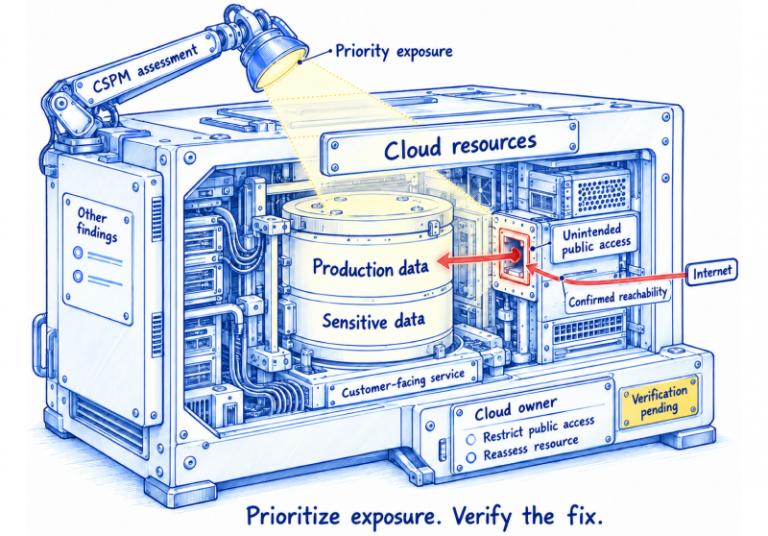
Cloud security posture management helps teams find configuration gaps and understand which exposures matter most. Learn how to establish coverage, prioritize findings,...
Arjun Mehrishi
October 12, 2026
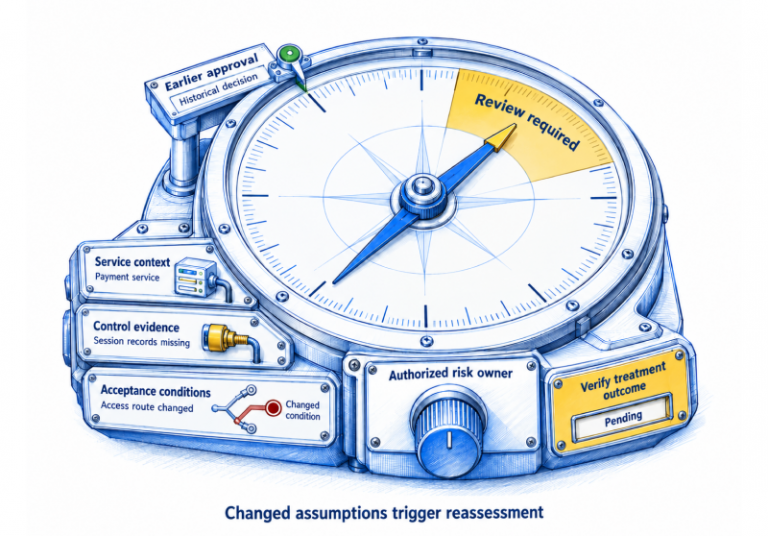
Effective enterprise GRC connects cyber risk to business services, current control evidence and accountable owners. Learn how to reassess decisions when conditions...
Arjun Mehrishi
October 8, 2026
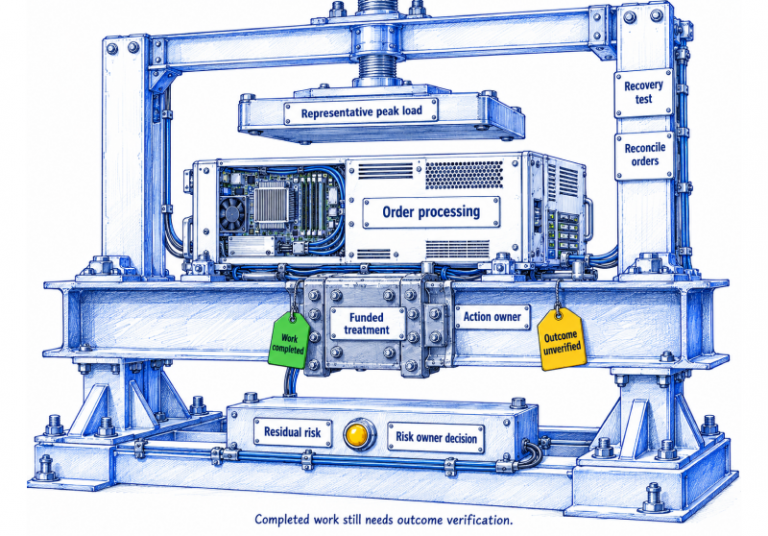
Risk decisions need funding, ownership and follow-through. Build a risk management plan that connects response choices to accountable actions, tracks delivery and...
Arjun Mehrishi
October 4, 2026
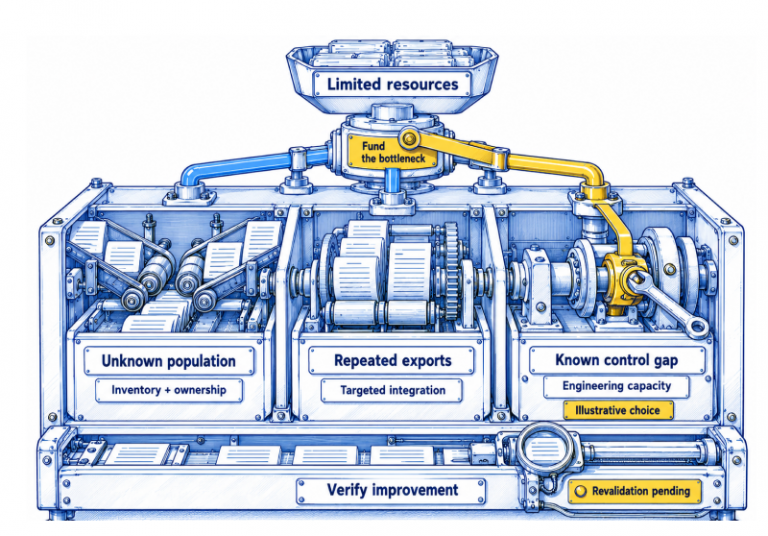
Make limited security budgets count by focusing on critical services, reliable evidence and accountable action. Learn how mid-market teams can identify control...
Arjun Mehrishi
October 4, 2026
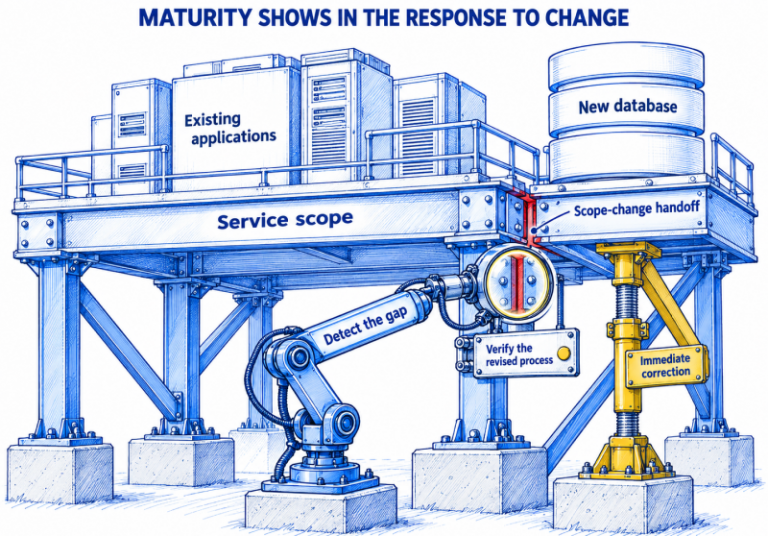
GRC maturity reflects how reliably an organization governs risk, meets obligations and improves its practices. Assess capabilities across ownership, evidence, risk decisions...
Arjun Mehrishi
October 3, 2026
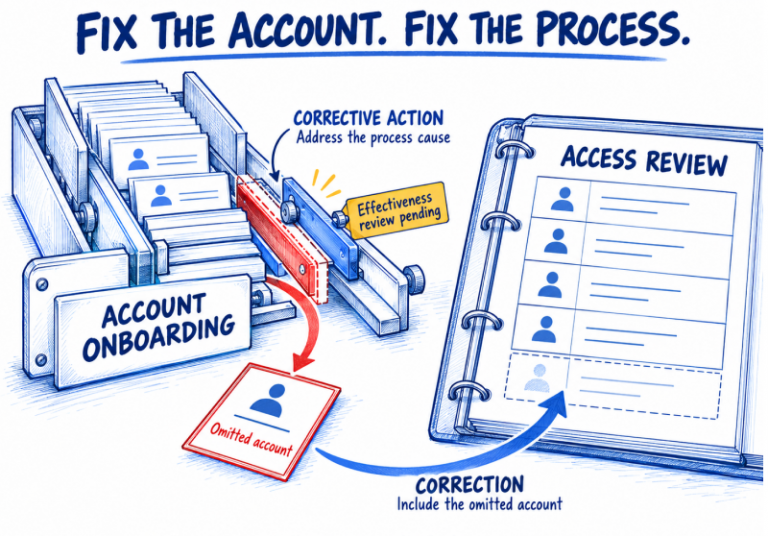
Prepare for ISO 27001 certification with a clear scope, traceable evidence and accountable control owners. Understand the audit stages, timeline and cost...
Arjun Mehrishi
October 2, 2026
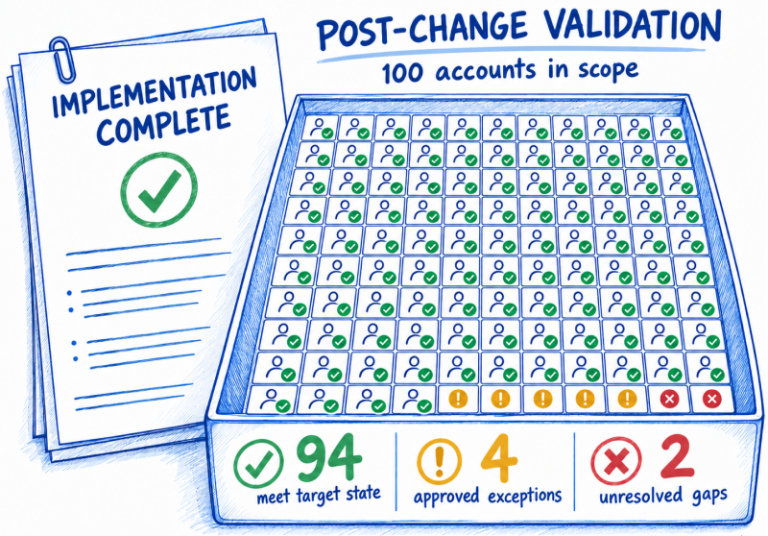
An approved change can still leave a security control in the wrong state. Connect ISO 27001 change management with post-change validation to...