← Back to Blog

Continuous Control Monitoring
Why Passing an Audit Does Not Prove Ongoing Compliance

Why Passing an Audit Does Not Prove Ongoing Compliance

An audit can confirm that security controls met assessed requirements during a defined period. But system changes can weaken those controls while earlier audit results remain valid. Ongoing compliance requires...

Categories: Continuous Control Monitoring, GRC, IT & Operations
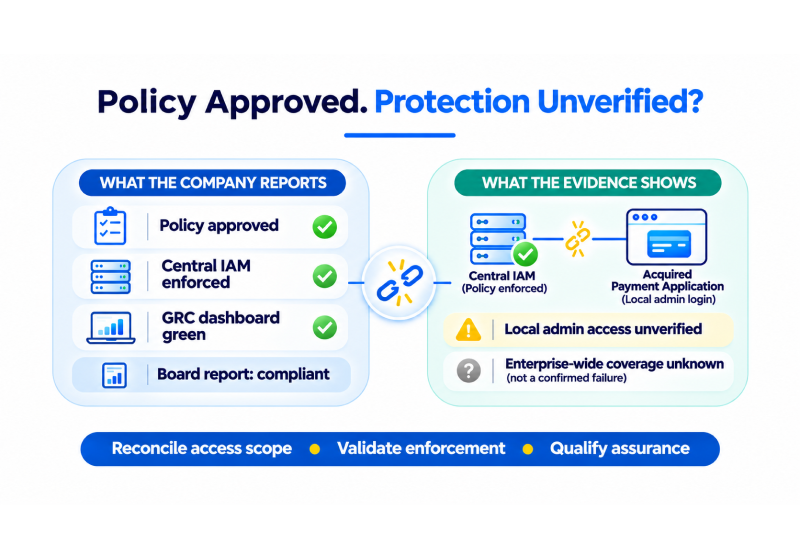
Why Cyber Governance Fails When Policies and Controls Are Disconnected

Why Cyber Governance Fails When Policies and Controls Are Disconnected

An approved policy can coexist with an unprotected business-critical system. The governance failure begins when leadership treats approval, configuration and evidence as one assurance claim, without establishing which systems and...

Categories: Continuous Control Monitoring, GRC, Security Maturity
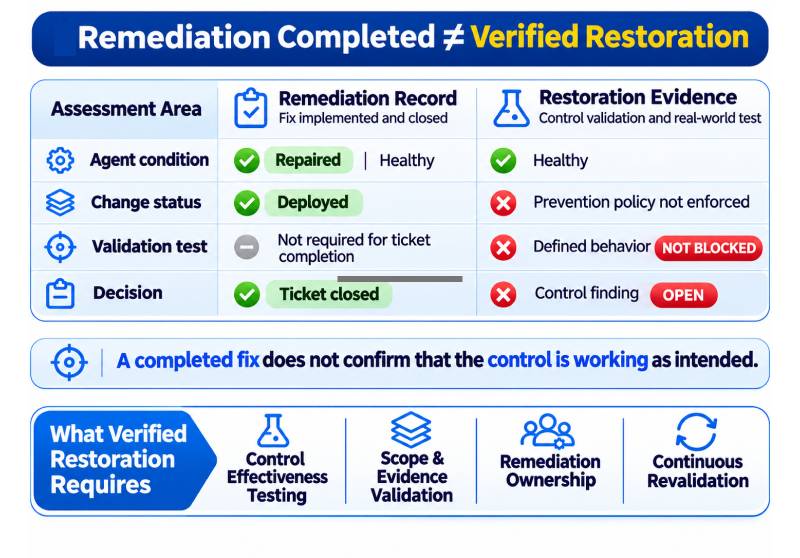
From Failed Control to Verified Restoration: Proving the Fix Works

From Failed Control to Verified Restoration: Proving the Fix Works

A completed change can conceal an unresolved security exposure. Verified control restoration requires a testable protection claim, current evidence across the affected scope, and a closure decision that does not...

Categories: Continuous Control Monitoring
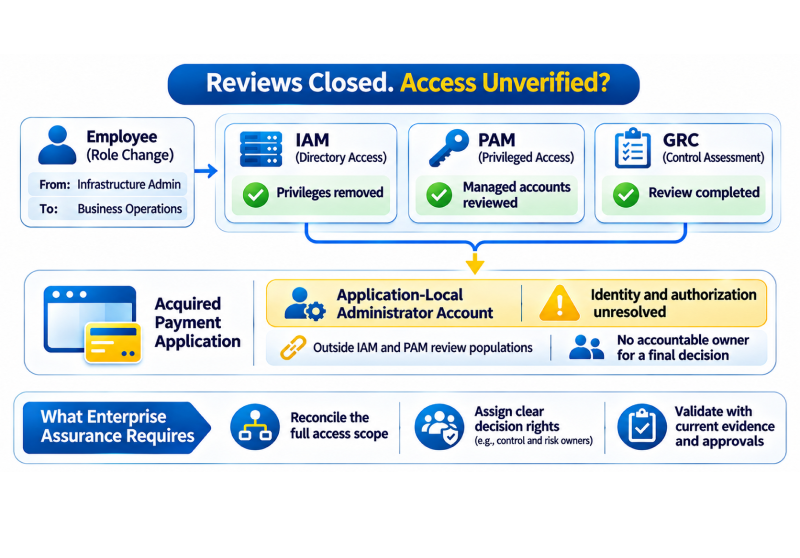
Security Control Ownership: Why Accountability Gaps Weaken Assurance

Security Control Ownership: Why Accountability Gaps Weaken Assurance

Assigning a control owner does not guarantee protection across every intended system. When teams complete their tasks without verifying that all relevant systems and accounts are covered, management may assume...

Categories: Continuous Control Monitoring, GRC, Uncategorized
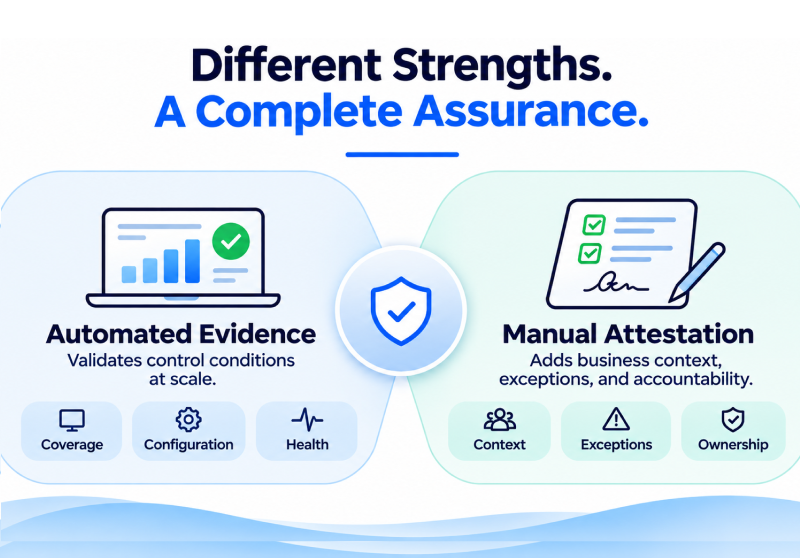
Automated Evidence Collection vs Manual Attestation: What Each Proves

Automated Evidence Collection vs Manual Attestation: What Each Proves

Your quarterly compliance review is complete. The endpoint protection control is marked compliant, supported by evidence and an attestation from the IT team. But does that declaration establish that protection...

Categories: Continuous Control Monitoring, GRC, Remediation
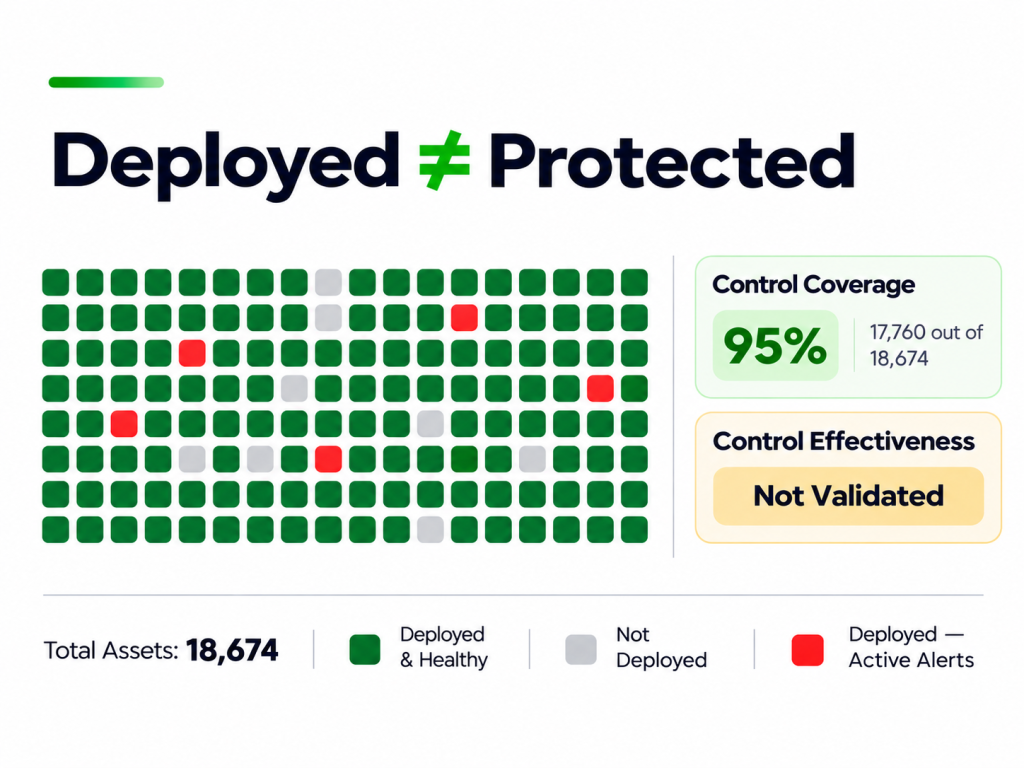
Control Coverage vs Control Effectiveness: Measure Reach and Results

Control Coverage vs Control Effectiveness: Measure Reach and Results

Security dashboards routinely report control coverage, compliance percentages and control health scores. These metrics provide valuable visibility into security operations, but they are often interpreted as evidence that security controls...

Categories: Continuous Control Monitoring, GRC, Security Maturity
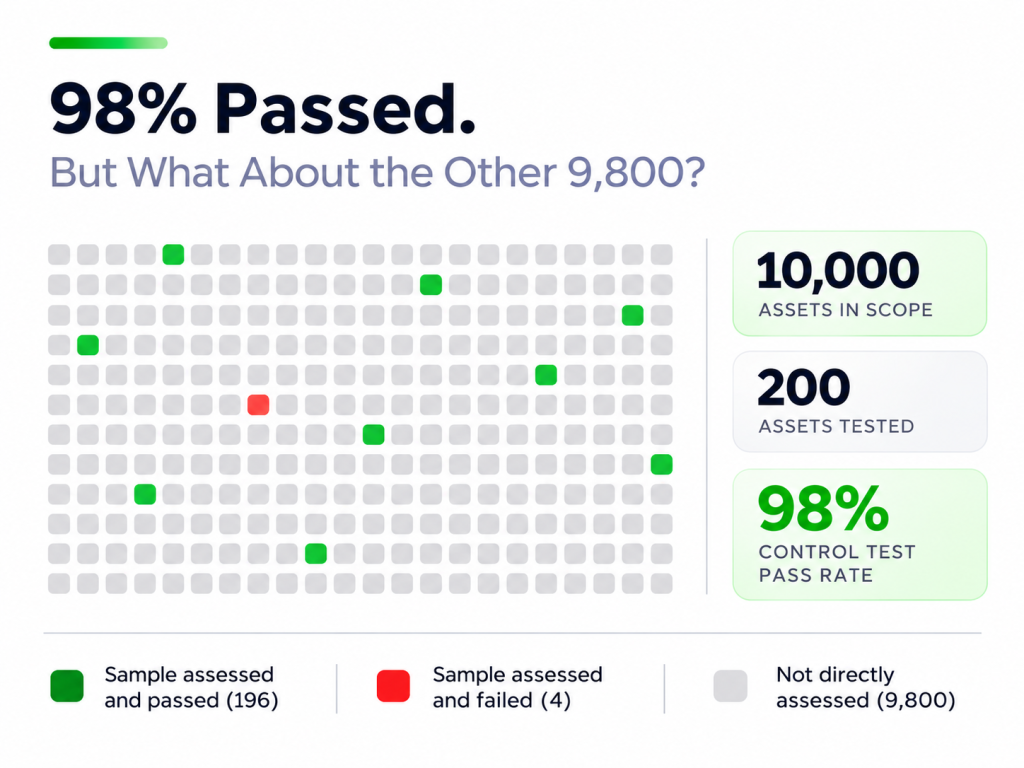
Control Testing vs Continuous Control Monitoring: What Each Can Prove

Control Testing vs Continuous Control Monitoring: What Each Can Prove

Organizations invest significant effort in testing security controls to establish whether they are operating as intended. These assessments support regulatory compliance, identify weaknesses and provide management with assurance about the...

Categories: Continuous Control Monitoring, Uncategorized
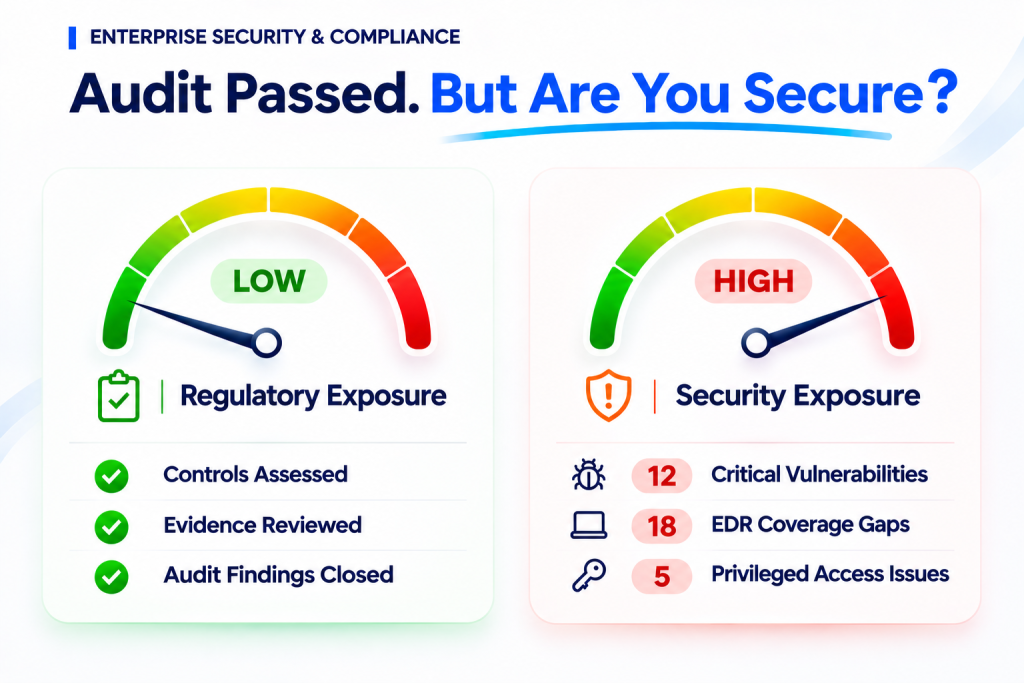
Prevent Cyberattacks by Balancing Enterprise Security and Compliance

Prevent Cyberattacks by Balancing Enterprise Security and Compliance

Your organization has completed its security audit. The required controls are documented, the evidence has been submitted, and compliance status is green. Yet a critical server remains exposed, a privileged...

Categories: Continuous Control Monitoring, Exposure Management, GRC
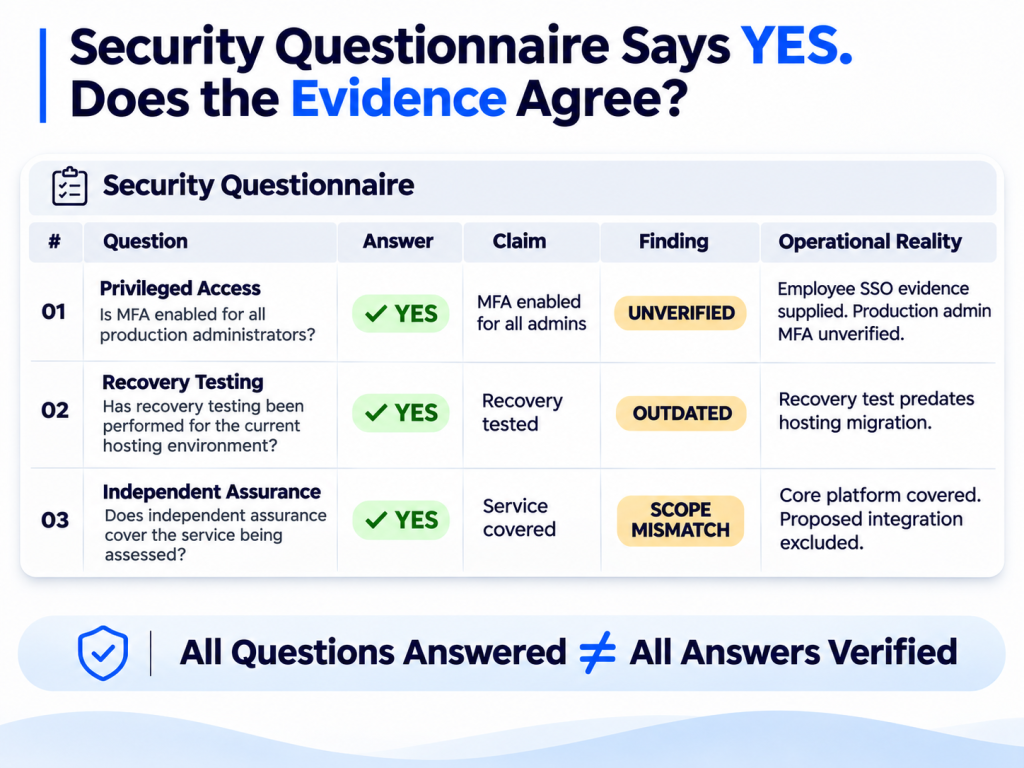
Security Questionnaires: Respond with Accurate, Verifiable Answers

Security Questionnaires: Respond with Accurate, Verifiable Answers

Security questionnaires help buyers understand how a supplier protects the data, systems and services involved in a proposed relationship. Reliable responses define where controls apply, provide current supporting evidence and...

Categories: Continuous Control Monitoring, GRC, IT & Operations
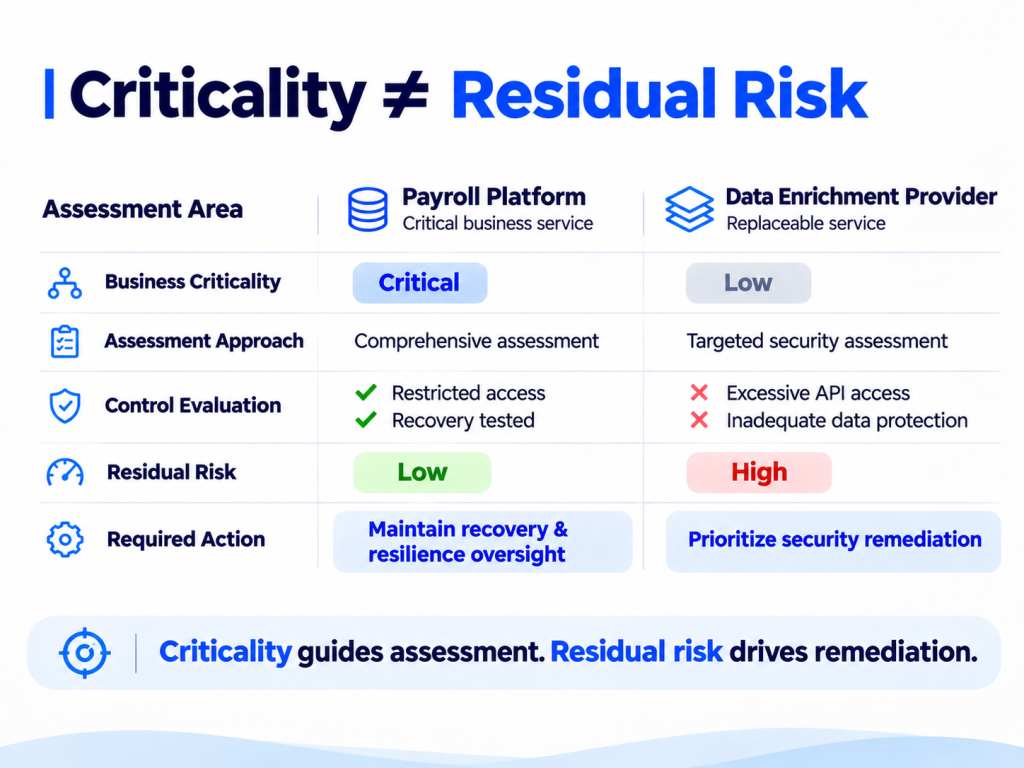
Vendor Cybersecurity Questions That Test Scope, Evidence and Exposure

Vendor Cybersecurity Questions That Test Scope, Evidence and Exposure

A vendor cybersecurity inquiry should establish what the supplier will do, which data and systems it can access, and how the business depends on its services. Ask targeted questions, request...

Categories: Continuous Control Monitoring, Exposure Management, GRC
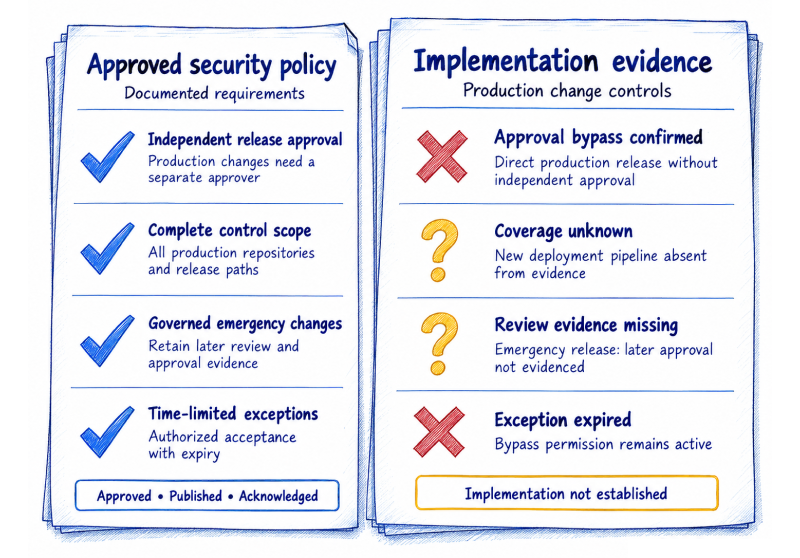
Cybersecurity Policy Management That Connects Rules to Real Controls

Cybersecurity Policy Management That Connects Rules to Real Controls

Cybersecurity policy management works when approved rules stay connected to accountable decisions, controls and current evidence. A policy library alone cannot show whether teams can apply a rule, whether systems...

Categories: Continuous Control Monitoring
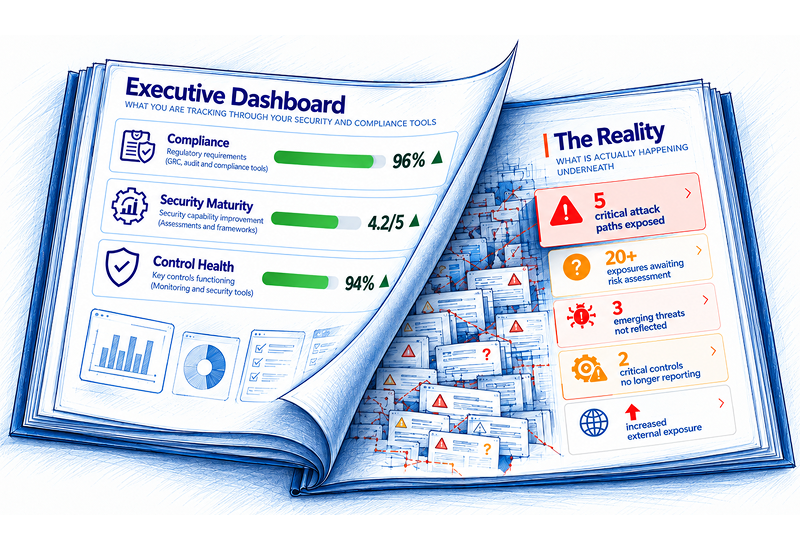
Why Green Security Dashboards Don’t Mean Lower Risk

Why Green Security Dashboards Don’t Mean Lower Risk

Learn how compliance, security maturity, and continuously assessed business risk must work together to drive better security decisions. Compliance, security maturity, and risk assessment are three essential pillars of enterprise...

Categories: Continuous Control Monitoring, Security Maturity