← Back to Blog

Risk Management

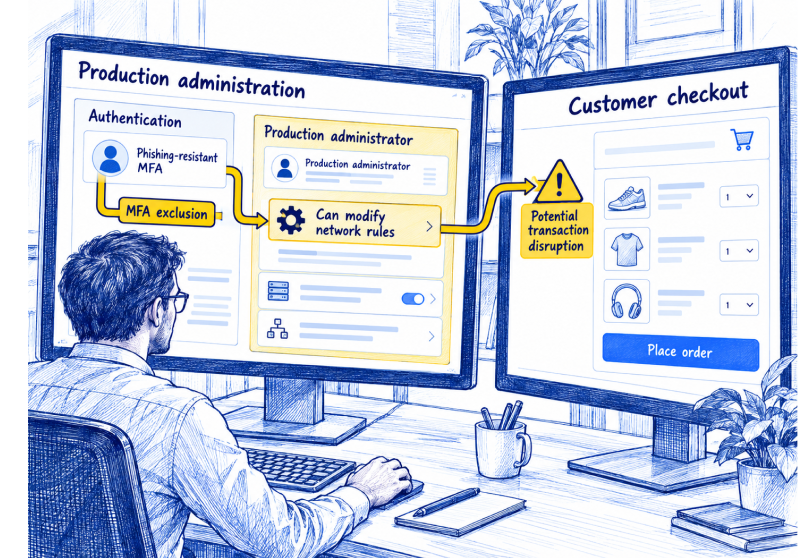
Cybersecurity Control Impact Analysis: Find Control Failures Before They Spread

Cybersecurity Control Impact Analysis: Find Control Failures Before They Spread

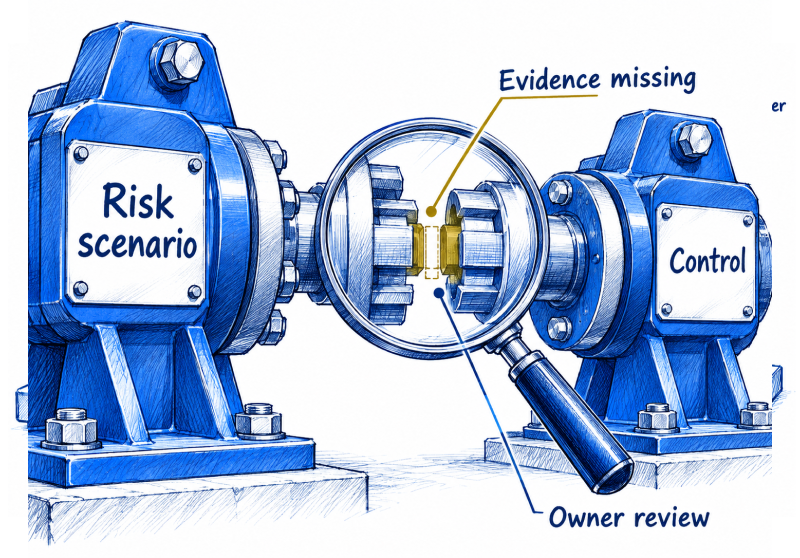
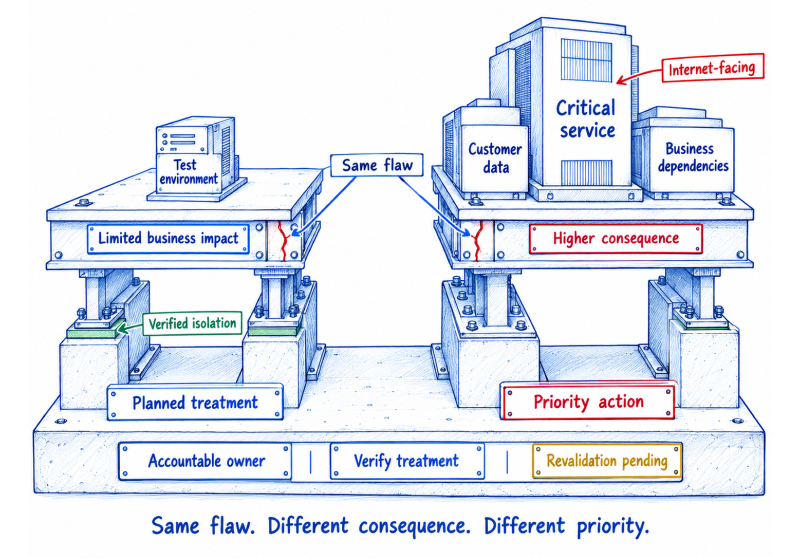
Understand what a weakened control exposes, which operations depend on it and how to verify that corrective action has restored protection. Cybersecurity control impact analysis traces a failed or weakened...

Categories: Cybersecurity, Risk Management
AWS Security Best Practices: Secure Multi-Account AWS Workloads With Guardrails

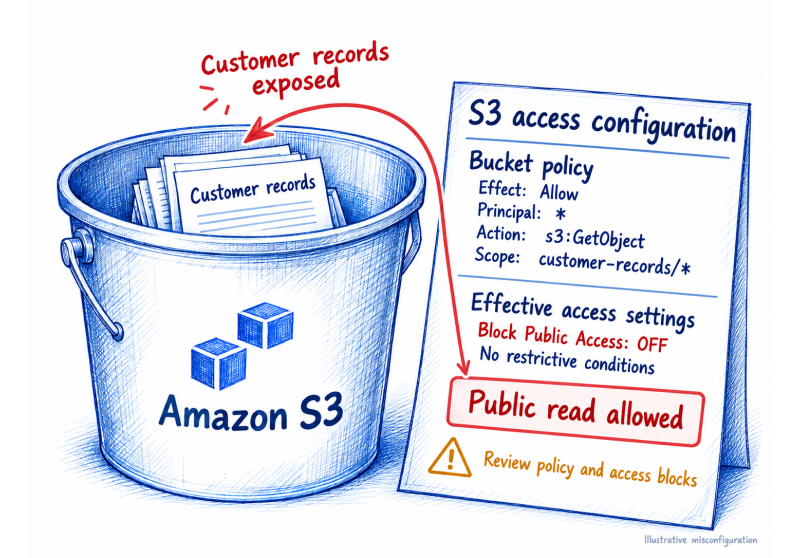
AWS Security Best Practices: Secure Multi-Account AWS Workloads With Guardrails

A practical guide to account boundaries, identity, guardrails, and operations in AWS.Build a secure foundation that lets workload teams move without relying on every account owner to remember every control....

Categories: Cloud Security, Cybersecurity, Risk Management
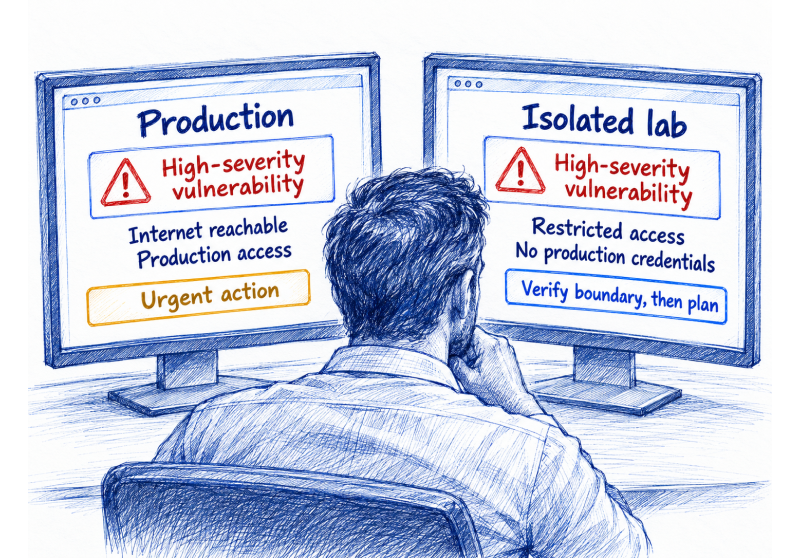
Risk-Based Vulnerability Management: Prioritize Exposure Beyond Scores

Risk-Based Vulnerability Management: Prioritize Exposure Beyond Scores

A practical guide for security and IT leaders deciding what to fix first.Use exploit evidence, real exposure, and business impact to create a defensible remediation queue. The backlog is a...

Categories: Cybersecurity, Risk Management
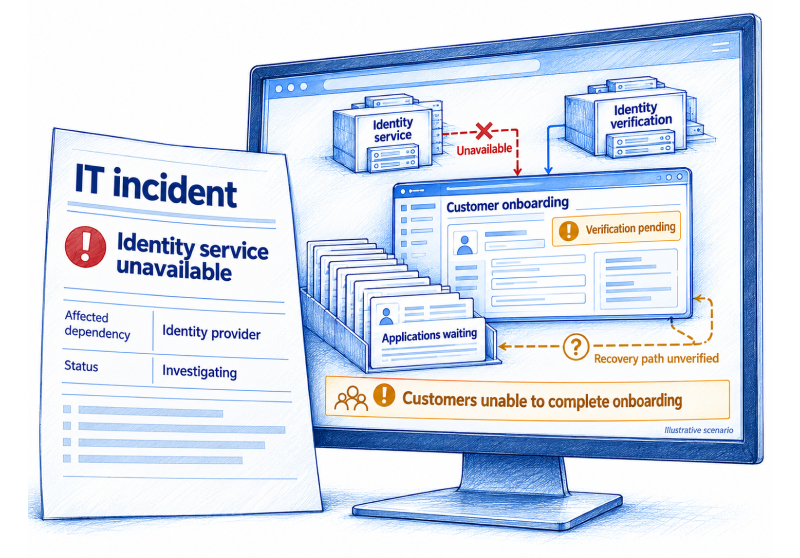
IT Risk Management in 2026: Connect Dependencies to Business Impact

IT Risk Management in 2026: Connect Dependencies to Business Impact

A practical guide for security, IT, and GRC leaders to identify concentration risk and improve portfolio decisions. IT risk management is harder to see when technology spans cloud platforms, vendors,...

Categories: Cybersecurity, Risk Management
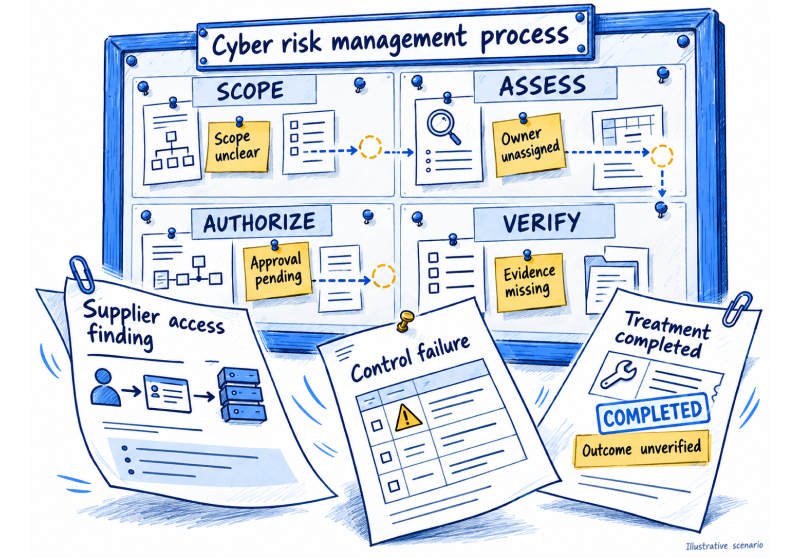
Cybersecurity Risk Management Process: A Practical Guide to Decisions

Cybersecurity Risk Management Process: A Practical Guide to Decisions

A cybersecurity risk management process should move from a defined business question to a decision, funded action, and evidence that the response worked.This guide gives security and GRC leaders a...

Categories: Cybersecurity, Risk Management
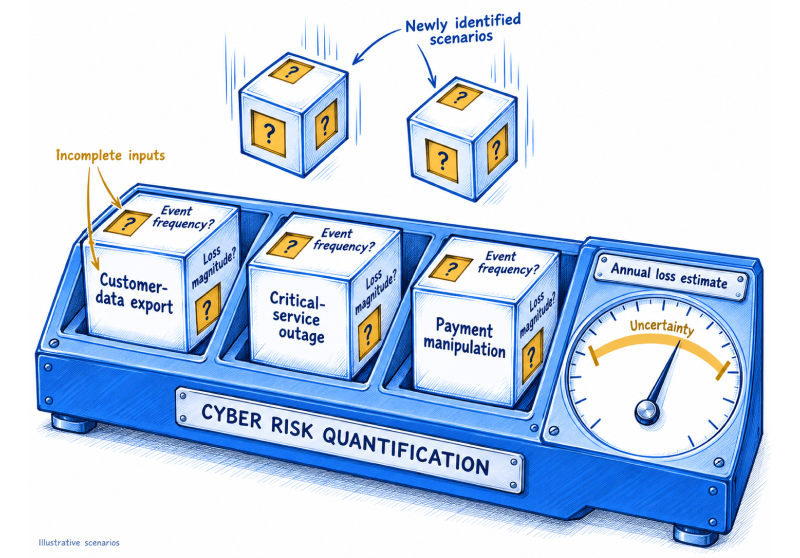
Quantitative Cyber Risk Analysis: Put Loss Ranges to Work in Security Decisions

Quantitative Cyber Risk Analysis: Put Loss Ranges to Work in Security Decisions

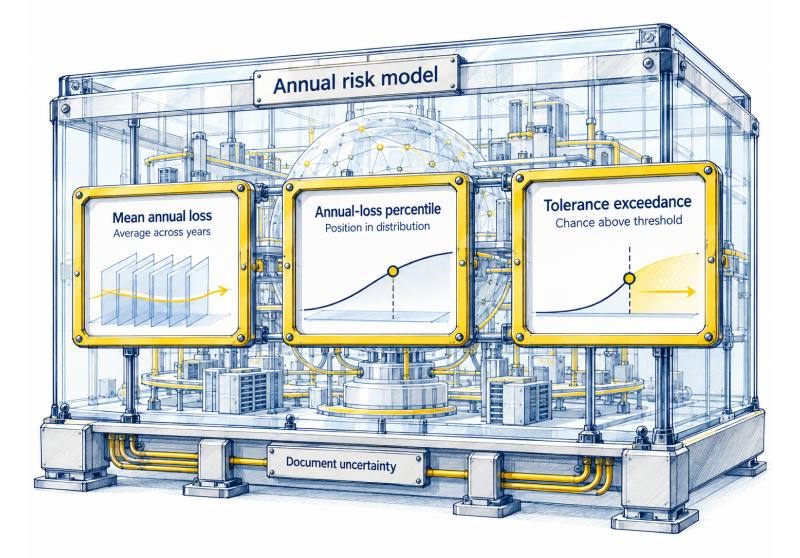
Quantitative cyber risk analysis can help leaders compare security choices, but a precise-looking number is only as sound as its scenario and inputs. This guide shows how to model loss...

Categories: Cybersecurity, Risk Management
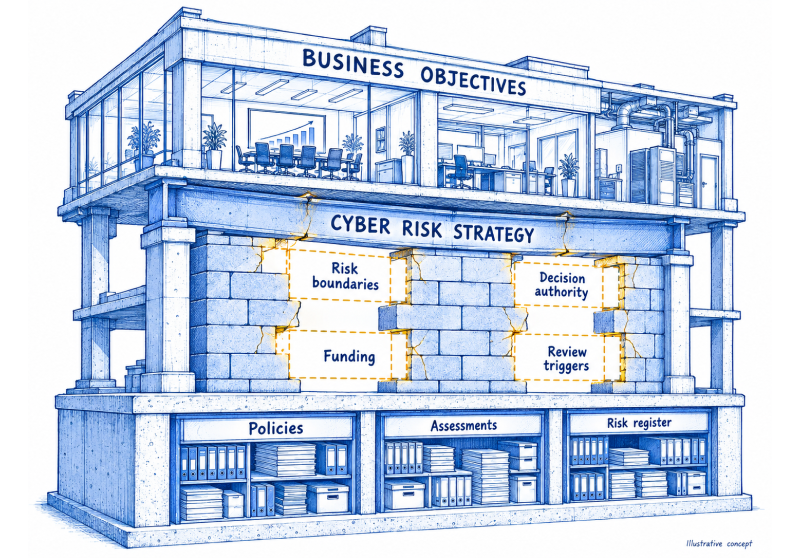
Cybersecurity Risk Management Strategy: Define Priorities, Authority and Limits

Cybersecurity Risk Management Strategy: Define Priorities, Authority and Limits

A cybersecurity risk management strategy should guide real choices about priorities, investment and acceptable exposure. This practical framework connects business objectives to decision authority, treatment and review. A cybersecurity risk...

Categories: Cybersecurity, Risk Management
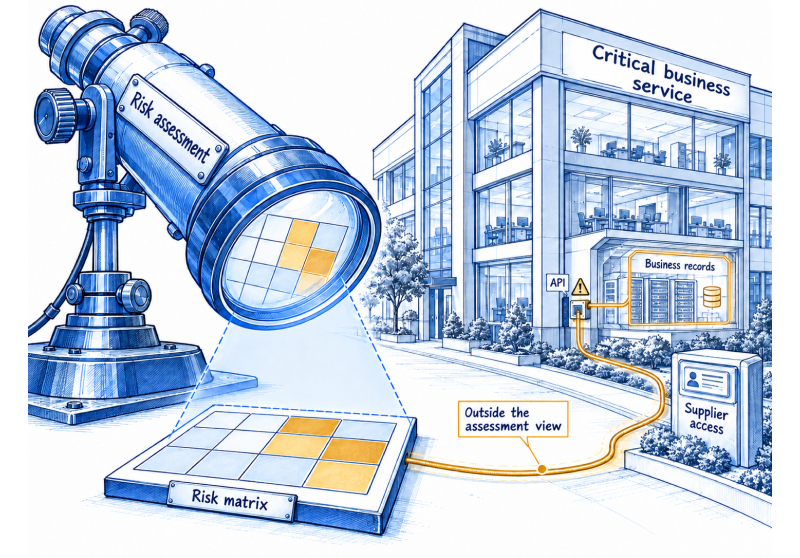
Cybersecurity Risk Management Techniques: Choose the Right Method

Cybersecurity Risk Management Techniques: Choose the Right Method

Different risk questions need different methods. Compare practical techniques, see how two methods reach different decisions on the same supplier scenario, and choose an approach that fits the evidence and...

Categories: Cybersecurity, GRC, Risk Management
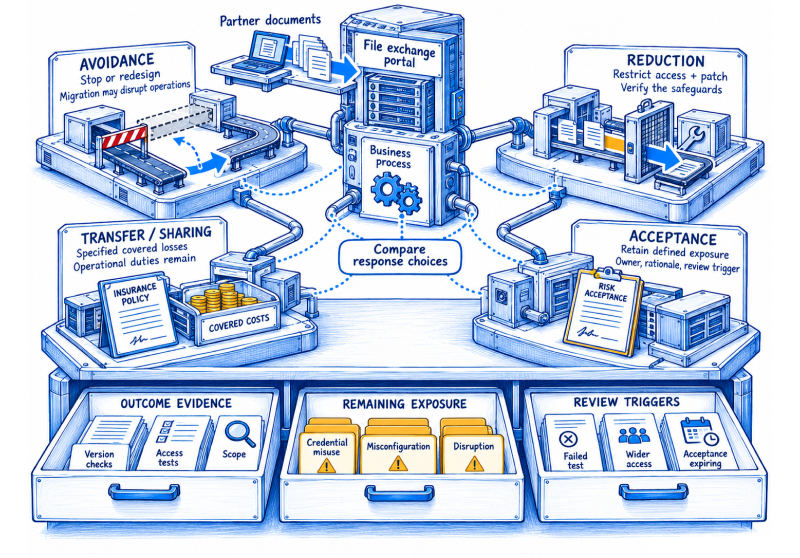
Risk Mitigation Strategies: Comparing Treatment Choices and Trade-offs in Practice

Risk Mitigation Strategies: Comparing Treatment Choices and Trade-offs in Practice

Risk mitigation is often used to mean reducing exposure, while risk treatment covers the full set of response choices. Learn how to compare avoidance, reduction, transfer and acceptance, then verify...

Categories: Cybersecurity, GRC, Risk Management
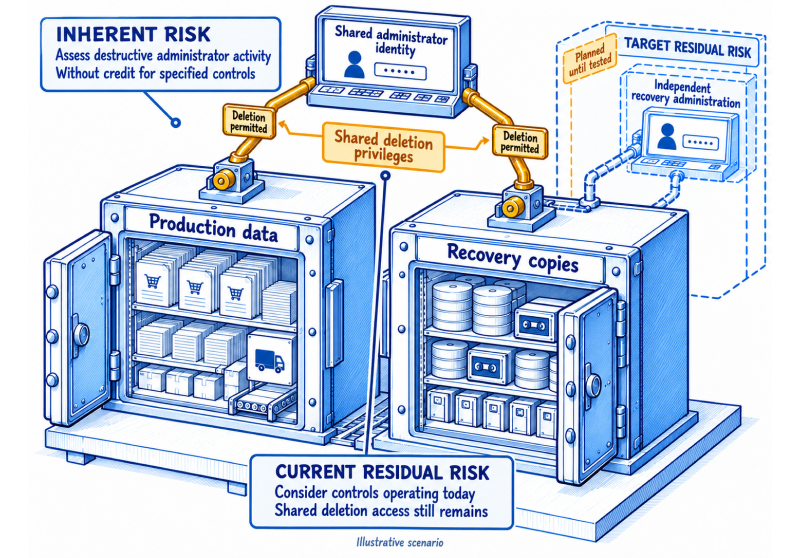
Inherent Risk vs Residual Risk: Use Control Evidence to Defend the Risk You Accept

Inherent Risk vs Residual Risk: Use Control Evidence to Defend the Risk You Accept

Inherent risk vs residual risk is a comparison between exposure without specified risk responses and exposure after those responses. The distinction helps leaders decide what protection is necessary, what risk...

Categories: Risk Management

Risk Management Framework in Practice From System Scope to Decisions You Can Defend

Risk Management Framework in Practice From System Scope to Decisions You Can Defend

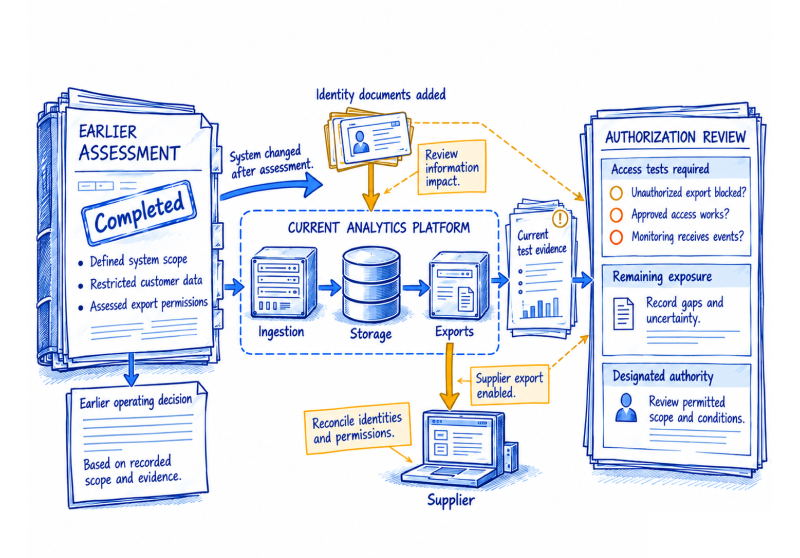
A risk management framework connects system scope, control evidence and accountable decisions. Applying NIST RMF means establishing why a system can operate, what exposure remains and which changes require that...

Categories: Risk Management

The UAE Risk Landscape Is Changing. Is Your Risk Strategy Keeping Up?

The UAE Risk Landscape Is Changing. Is Your Risk Strategy Keeping Up?

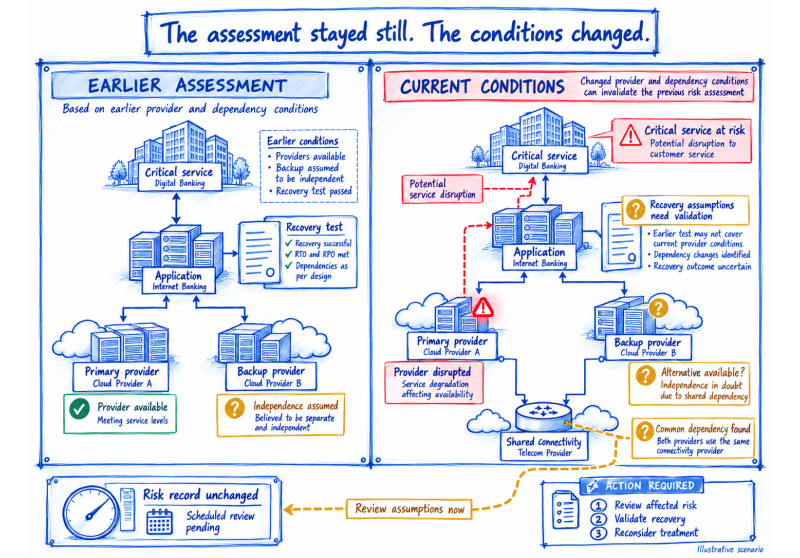
The article explains why UAE enterprises need to update risk assessments when threats, business dependencies, or control effectiveness change. It highlights how geopolitical uncertainty, cyber threats, and third-party disruptions can...

Categories: Risk Management

Risk Control Matrix: Connect Cybersecurity Risks to Controls and Useful Evidence

Risk Control Matrix: Connect Cybersecurity Risks to Controls and Useful Evidence

A risk control matrix makes clear how a defined business risk is addressed, who owns the response, and what evidence shows the control works. For cybersecurity and GRC teams, its...

Categories: Cybersecurity, GRC, Risk Management
Operational Risk Management in 2026: Keep Decisions Current as Operations Change

Operational Risk Management in 2026: Keep Decisions Current as Operations Change

Operational risk management helps leaders understand how everyday activity can disrupt critical services, and what to do before a weakness becomes a loss. A practical program connects risk scenarios to...

Categories: Cybersecurity, GRC, Risk Management
Business Impact Analysis in 2026: Connect Critical Services to Recovery Decisions

Business Impact Analysis in 2026: Connect Critical Services to Recovery Decisions

Business impact analysis helps organizations understand how disruption affects critical services and set recovery priorities. This article explains how to assess impacts over time, map dependencies, define realistic recovery targets...

Categories: Risk Management

Quantitative Cyber Risk Assessment in 2026 for Better GRC Decisions

Quantitative Cyber Risk Assessment in 2026 for Better GRC Decisions

Quantitative cyber risk assessment helps teams decide which security treatments justify their cost. Defined scenarios, current evidence and explicit uncertainty make the estimates useful to security, finance and business owners....

Categories: Cybersecurity, Risk Management
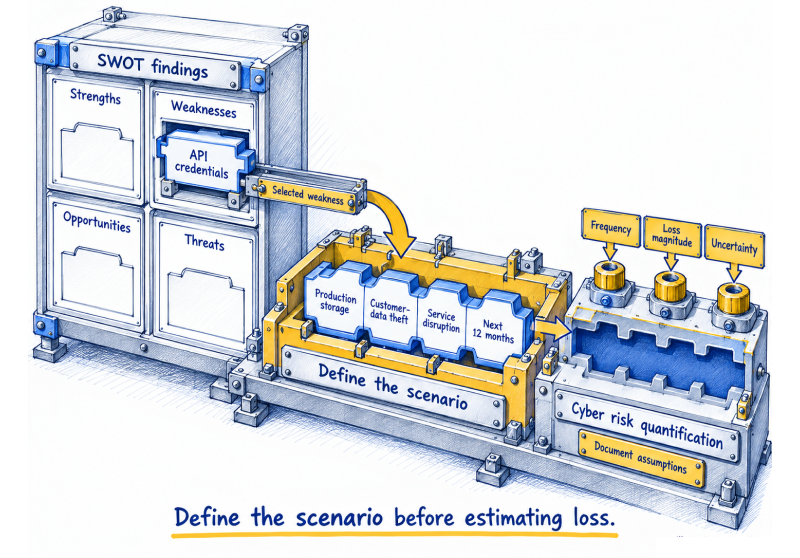
SWOT Analysis and Cyber Risk Quantification: A Practical GRC Strategy for 2026

SWOT Analysis and Cyber Risk Quantification: A Practical GRC Strategy for 2026

SWOT analysis can help security leaders identify strategic concerns, while cyber risk quantification can test how those concerns may affect the business. This article explains how to connect the two...

Categories: Cybersecurity, Risk Management
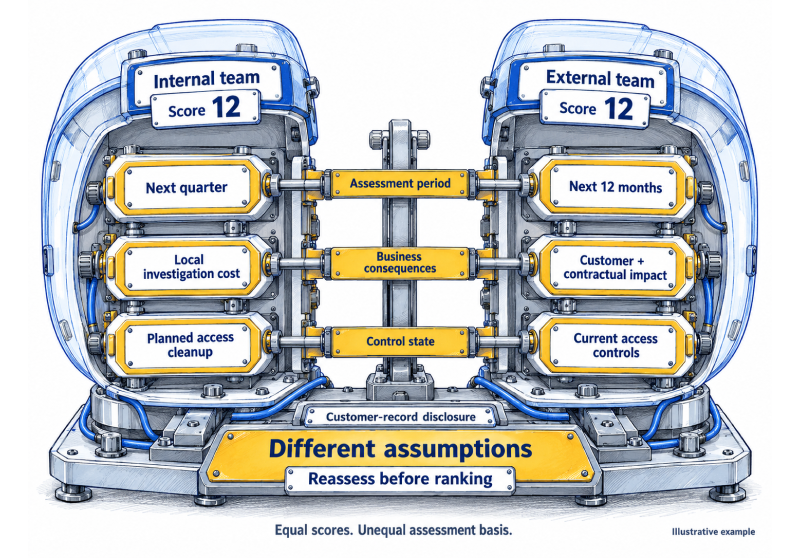
Risk Scoring in 2026: Make Internal and External Risks Comparable Across Teams

Risk Scoring in 2026: Make Internal and External Risks Comparable Across Teams

Learn how to calculate risk scores, reconcile conflicting ratings and compare internal failures with external threats without distorting management priorities. The method aligns scenarios, time horizons, impact criteria, control assumptions...

Categories: Cybersecurity, Risk Management
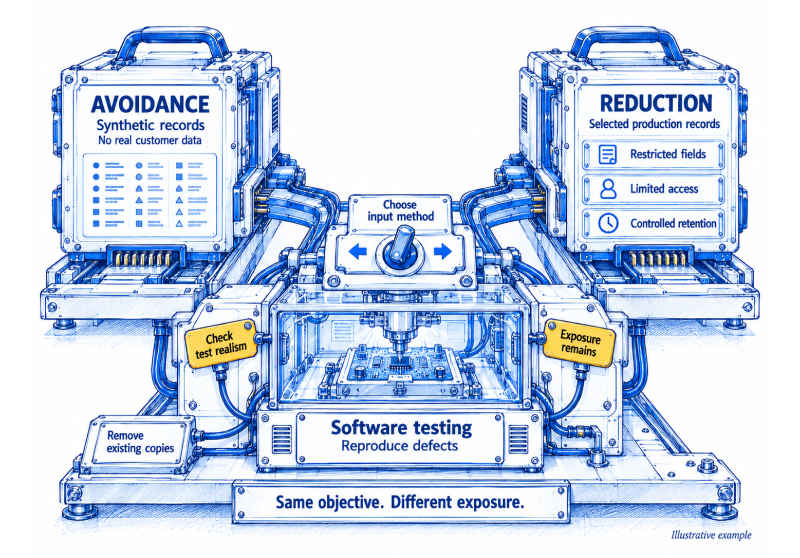
Risk Avoidance vs Risk Reduction in 2026: Choosing the Right Business Response

Risk Avoidance vs Risk Reduction in 2026: Choosing the Right Business Response

Compare the value of continuing an activity with the cost of withdrawing, and choose a response that addresses the specific exposure. Risk avoidance vs risk reduction asks a practical business...

Categories: Cybersecurity, GRC, Risk Management
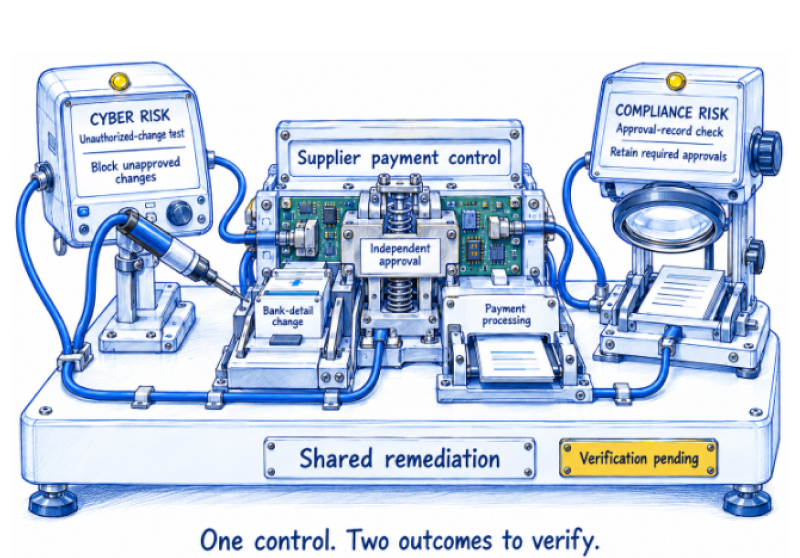
Cyber Risk and Compliance Risk: Decide What Needs Action

Cyber Risk and Compliance Risk: Decide What Needs Action

Cyber risk and compliance risk can share the same control weakness while requiring different decisions. Learn how mid-market teams can assess business harm and applicable obligations together, coordinate corrective action...

Categories: Compliance, Risk Management
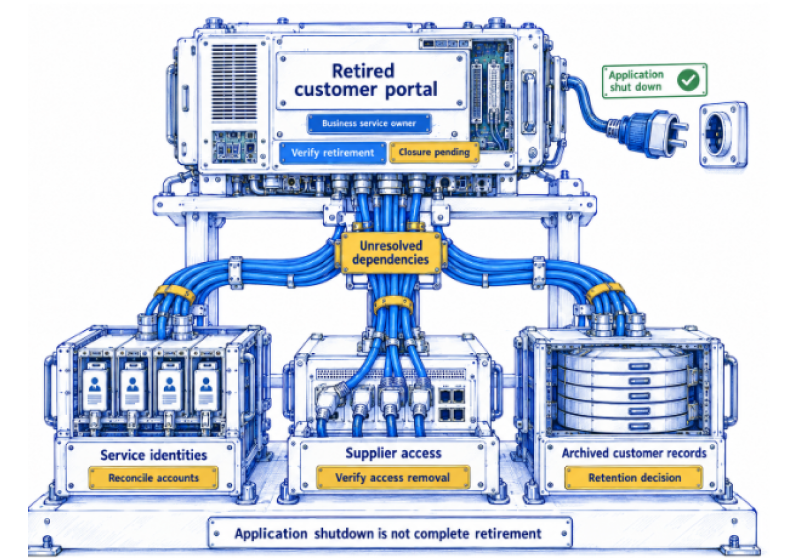
IT GRC: Keep Accountability Intact When Technology Changes

IT GRC: Keep Accountability Intact When Technology Changes

IT governance, risk management, and compliance (IT GRC) should help a CISO answer a difficult operational question: when technology changes, do the business's risk decisions and control assurances still hold?...

Categories: Risk Management

Cybersecurity Risk Scoring: Make the Score Decision-Ready

Cybersecurity Risk Scoring: Make the Score Decision-Ready

A cybersecurity risk score should explain why an exposure matters and what action it requires. Learn how to combine threat signals, reachability, business impact and control evidence into clear priorities,...

Categories: Cybersecurity, Risk Management
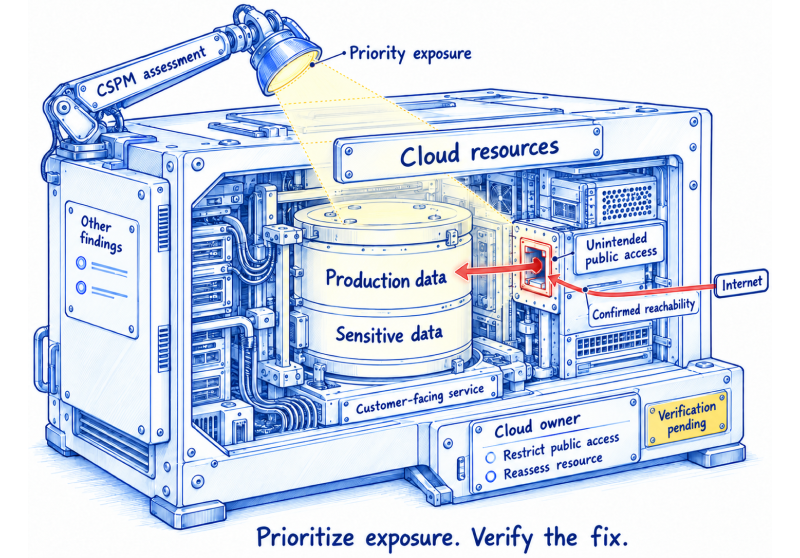
Cloud Security Posture Management: Find and Fix What Matters

Cloud Security Posture Management: Find and Fix What Matters

Cloud security posture management helps teams find configuration gaps and understand which exposures matter most. Learn how to establish coverage, prioritize findings, assign owners and verify that remediation restores the...

Categories: Cloud Security, Risk Management
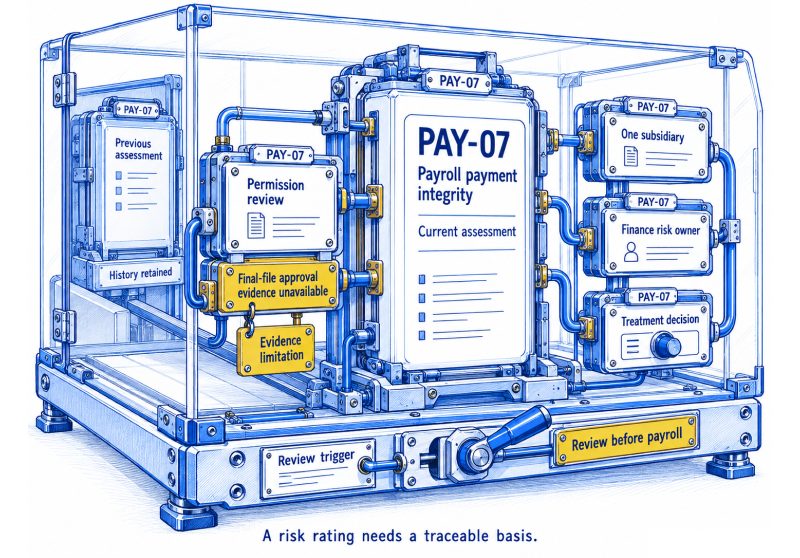
Build a Risk Register in 2026 With Clear Evidence and Traceable Business Decisions

Build a Risk Register in 2026 With Clear Evidence and Traceable Business Decisions

A risk rating needs a clear basis and a record of the decision behind it. Build risk entries that connect business scenarios with evidence, ownership and review triggers, keeping current...

Categories: Cybersecurity, GRC, Risk Management
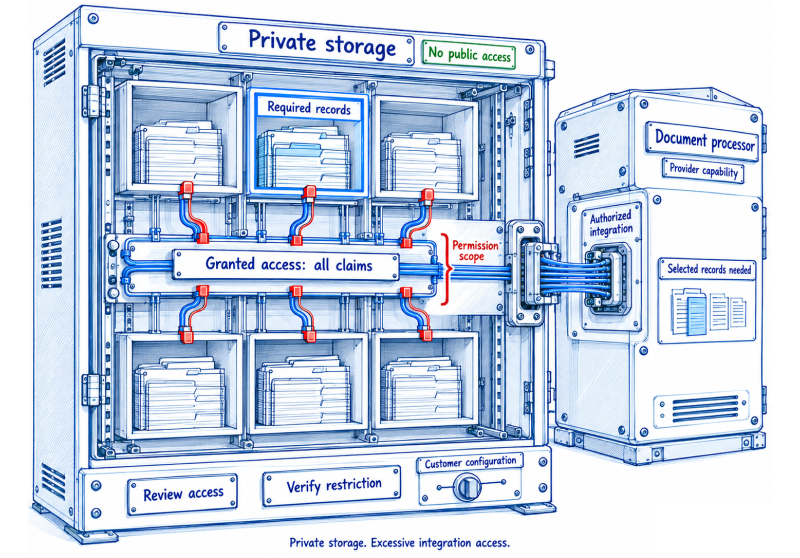
Cloud Risk Management in 2026: Map Ownership Across Services and Dependencies

Cloud Risk Management in 2026: Map Ownership Across Services and Dependencies

Cloud risk extends beyond configuration settings. Map identity access, data flows and provider responsibilities across connected services to identify hidden exposure, assign ownership and test whether recovery dependencies hold up....

Categories: Cloud Security, GRC, Risk Management
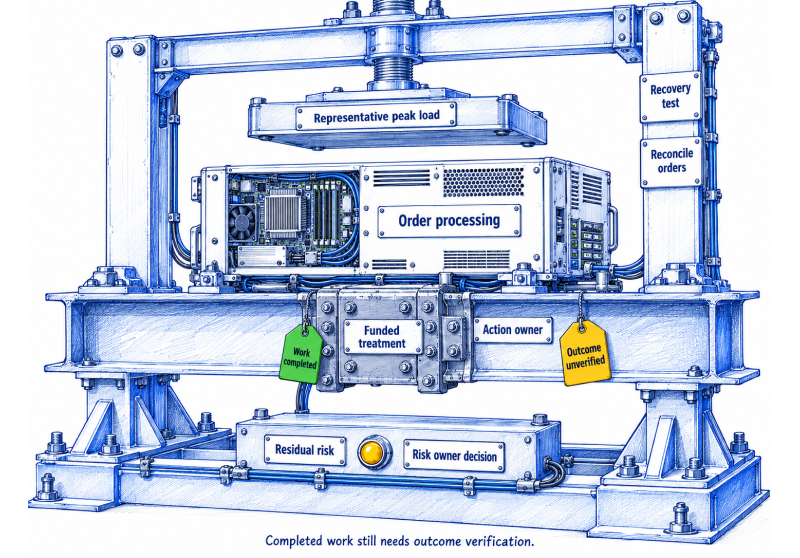
Risk Management Plan in 2026: Turn Decisions into Funded and Accountable Actions 

Risk Management Plan in 2026: Turn Decisions into Funded and Accountable Actions 

Risk decisions need funding, ownership and follow-through. Build a risk management plan that connects response choices to accountable actions, tracks delivery and keeps remaining exposure visible as conditions change. A...

Categories: Cybersecurity, GRC, Risk Management
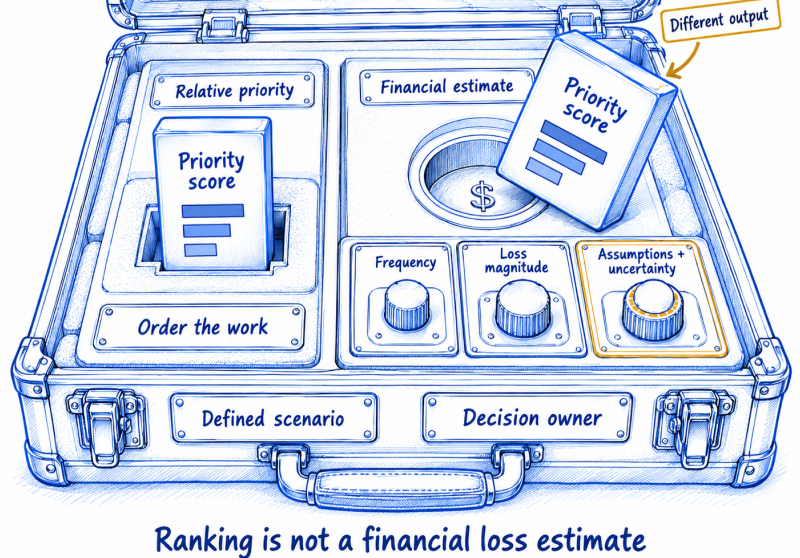
Cyber Risk Calculation Methods: Match the Output to the Decision

Cyber Risk Calculation Methods: Match the Output to the Decision

Different risk decisions need different outputs. Compare qualitative assessments, priority scores and quantitative loss estimates, and learn how to choose a method that makes assumptions, evidence and uncertainty clear to...

Categories: Cyber Risk, Risk Management
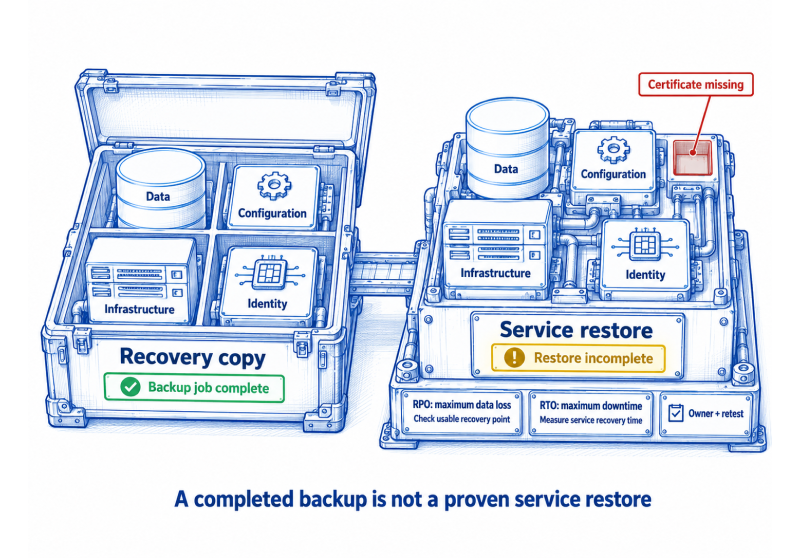
Backup Checklist in 2026: Verify Recovery for Security and Compliance Teams

Backup Checklist in 2026: Verify Recovery for Security and Compliance Teams

A successful backup job does not prove that a service can be restored. Use this checklist to define recovery coverage, set RPO and RTO targets, protect recovery copies and verify...

Categories: Compliance, Cyber Risk, Risk Management
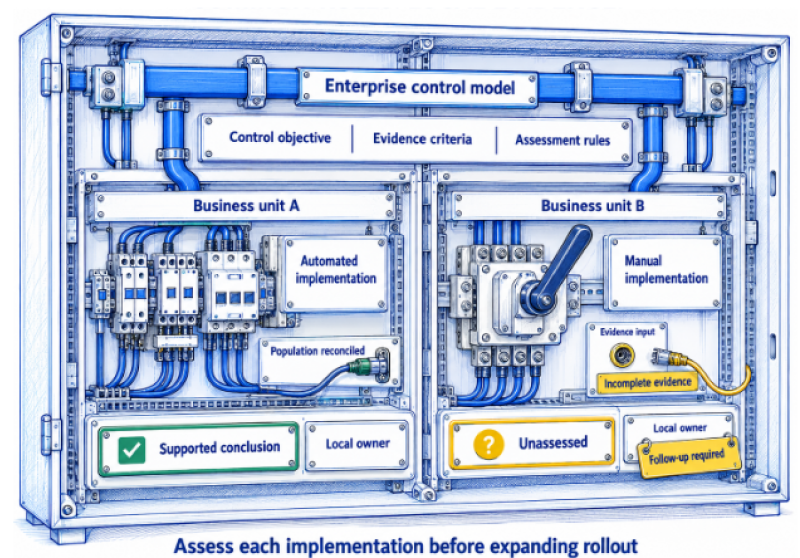
How to Roll Out Enterprise GRC: Prove the Model Before You Scale

How to Roll Out Enterprise GRC: Prove the Model Before You Scale

Enterprise GRC needs consistent assessments across business units while preserving local responsibilities and obligations. Establish clear ownership, reliable evidence and a complete pilot control cycle before expanding, so each rollout...

Categories: Compliance, GRC, Risk Management
Why Has Risk Management Become Process Theater and How Do We Fix It?

Why Has Risk Management Become Process Theater and How Do We Fix It?

Introduction — The Performance of Protection In too many organizations, risk management has become a performance rather than a practice. Every quarter, teams scramble to refresh risk registers, hold a...

Categories: Risk Management

Turning Risk Registers from Static Records into Living Intelligence

Turning Risk Registers from Static Records into Living Intelligence

For years, the risk register has been a key tool in governance, risk, and compliance (GRC) programs. But in most organizations, it still sits in spreadsheets or static forms that...

Categories: Risk Management

Third-Party Risk Metrics: How to Track and Report

Third-Party Risk Metrics: How to Track and Report

Third-party data breaches are more commonplace than ever. The majority of high-stakes data breaches in recent years have been caused by one missing link in the vendor management workflow. Take...

Categories: Risk Management

Connecting Risk and Remediation with Integrated Incident Response

Connecting Risk and Remediation with Integrated Incident Response

In 2023, attackers exploited a known vulnerability in MOVEit Transfer—a popular file transfer tool used by governments, banks, and large enterprises. Even after the vulnerability became public, many organizations failed...

Categories: Risk Management

Modernizing Third-Party Risk Management with Continuous Monitoring

Modernizing Third-Party Risk Management with Continuous Monitoring

Introduction: The Evolution of Third-Party Risk Management Businesses today rely on third-party vendors for everything from cloud services to data processing. These partners enable scale and speed—but also open the...

Categories: Risk Management

What is a Risk and Controls Matrix? A Beginner’s Guide

What is a Risk and Controls Matrix? A Beginner’s Guide

Every organization, big or small, faces uncertainty. It could be a data breach waiting to happen, a missed regulatory deadline, or risks that emerge from a third-party vendor. The hard...

Categories: Risk Management

10 Common Gaps in Enterprise Risk Assessments—and How to Close Them

10 Common Gaps in Enterprise Risk Assessments—and How to Close Them

Many organizations treat risk assessments as annual checklists, missing the dynamic threats that truly matter. This guide dives into the top 10 gaps that weaken enterprise risk assessments—from inconsistent scoring...

Categories: Risk Management

Risk Management vs Compliance Management: Which Should Be Your Priority?

Risk Management vs Compliance Management: Which Should Be Your Priority?

Stuck Between Risk and Compliance? That’s the Real Risk. Discover why treating them as rivals is holding your organization back—and how smart teams use both to fuel resilience and agility....

Categories: Risk Management

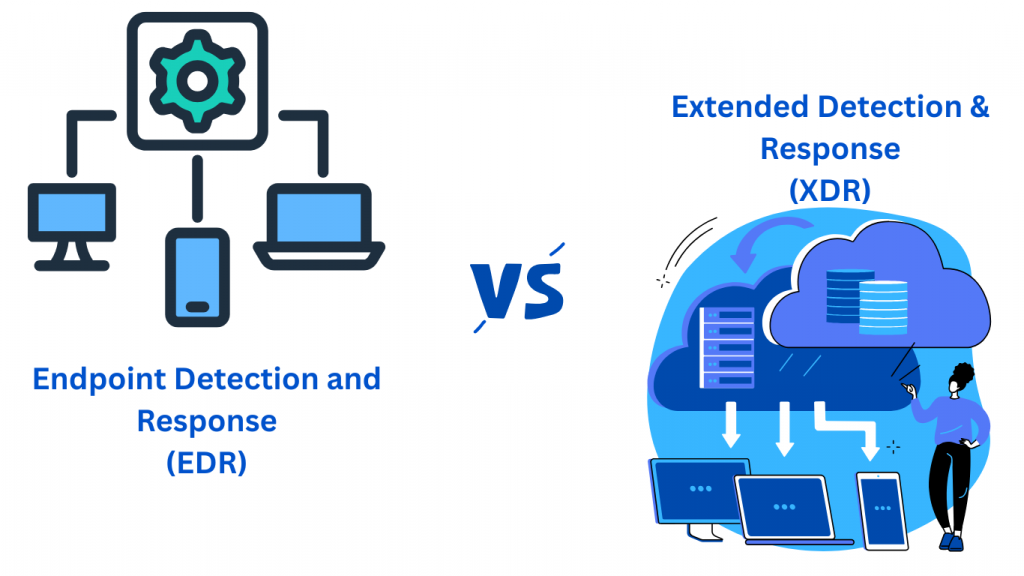
From EDR to XDR: Evaluating Tool Efficacy in Risk Assessments

From EDR to XDR: Evaluating Tool Efficacy in Risk Assessments

Cyber threats are faster, stealthier, and more coordinated than ever — and your tools need to keep up. This article dives into the real difference between EDR and XDR, how...

Categories: Risk Management

Conducting a Holistic Risk Audit: Key Steps & Best Practices

Conducting a Holistic Risk Audit: Key Steps & Best Practices

Most organizations approach risk audits the way they approach an annual health check-up—routine, compliance-driven, and often surface-level. If nothing appears broken, it’s business as usual. But just as hidden health...

Categories: Risk Management

Measuring Organizational Risk Maturity: An In-Depth Framework Overview

Measuring Organizational Risk Maturity: An In-Depth Framework Overview

Cyber threats aren’t slowing down. Every day, security teams are fighting fires, trying to keep up with evolving risks, compliance demands, and resource constraints. But here’s the question: Do you...

Categories: Risk Management