
kalpana v
October 22, 2025
Introduction — When the Cloud Shakes, Compliance Crumbles When AWS’s US-east-1 region went dark, so did thousands of companies. These weren’t reckless...
kalpana v
October 15, 2025
Introduction There are two sides to a coin and AI is no exception. AI’s versatility is what makes it useful across a...
kalpana v
October 9, 2025
As India accelerates toward becoming a digital-first economy, regulatory frameworks are increasingly shaping how enterprises manage data, AI, and security operations. At...
kalpana v
October 6, 2025
Introduction — The Performance of Protection In too many organizations, risk management has become a performance rather than a practice. Every quarter,...
kalpana v
September 29, 2025
Third-party vendors play a critical role in modern business operations, but they also expand exposure to unpredictable risks. These risks often do...
kalpana v
September 25, 2025
When it comes to responding to incidents, time is of the essence. The first few minutes often bring chaos—analysts must quickly switch...
kalpana v
September 19, 2025
It’s an undeniable fact that organizations of all sizes and industries have adopted AI at a colossal scale. While AI is revolutionizing...
kalpana v
September 15, 2025
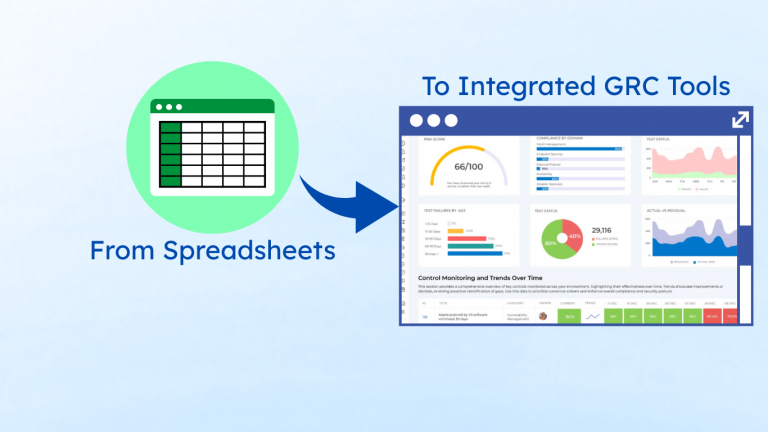
For years, spreadsheets have been the go-to tool for managing governance, risk, and compliance (GRC). They’re familiar, easy to set up, and...
kalpana v
September 9, 2025
Every 39 seconds, a cyberattack strikes somewhere in the world (University of Maryland). At the same time, regulators are tightening rules across...
kalpana v
September 3, 2025
For years, the risk register has been a key tool in governance, risk, and compliance (GRC) programs. But in most organizations, it...
kalpana v
August 28, 2025
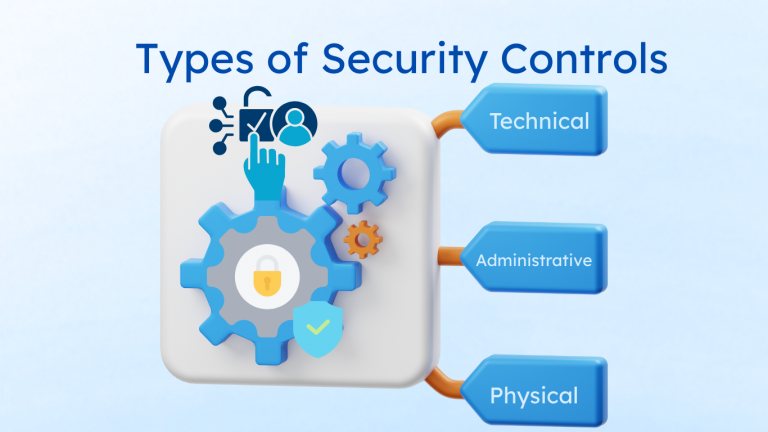
Security controls come in many forms and levels of complexity. Organizations implement them based on their own risks, needs, and processes. But...
kalpana v
August 21, 2025
The Payment Card Industry Data Security Standard (PCI DSS) has long served as the global benchmark for safeguarding cardholder data and reducing...
kalpana v
August 19, 2025
Third-party data breaches are more commonplace than ever. The majority of high-stakes data breaches in recent years have been caused by one...
kalpana v
August 11, 2025
Achieving GDPR compliance is only the beginning, maintaining it is the real challenge. The General Data Protection Regulation (GDPR) demands that organizations...
kalpana v
August 6, 2025
Too often, security tools treat all assets as equal. A critical alert on a decommissioned test server carries the same weight as...
kalpana v
July 31, 2025
Access reviews play a key role in meeting security and regulatory standards. But many companies still handle them manually, creating risk and...
kalpana v
July 28, 2025
On July 25, 2025, the Indian Computer Emergency Response Team (CERT-In) launched a major update to its cybersecurity audit guidelines. These new...
kalpana v
July 23, 2025
Introduction: The Breach That Wasn’t Loud — Until It Was The most dangerous breaches often don’t begin with a bang.They start with...
kalpana v
July 22, 2025
In May 2024, one of the most significant cloud breaches in recent memory made headlines: attackers infiltrated over 160 customer environments in...
kalpana v
July 14, 2025
Third-party data breaches are on the rise. Attackers increasingly target vendors, contractors, and SaaS providers; not just because they’re easier to breach,...
kalpana v
July 11, 2025
You’ve invested in top-tier tools—firewalls, SIEMs, XDRs, MDRs, and real-time threat intel feeds. On paper, your security stack looks solid. You’ve done...
kalpana v
July 8, 2025
Security Operations Centers (SOCs) protect modern businesses from cyber threats. But instead of battling a lack of information, SOC teams often drown...
kalpana v
July 2, 2025
In 2023, attackers exploited a known vulnerability in MOVEit Transfer—a popular file transfer tool used by governments, banks, and large enterprises. Even...
kalpana v
June 30, 2025
Introduction: Why “Boardroom-Ready” Matters More Than Ever Not long ago, cybersecurity was seen as a technical silo—an IT function buried deep in...
kalpana v
June 27, 2025
Insider threats are one of the most underestimated cybersecurity risks facing organizations today. While companies often focus on defending against external attackers,...
kalpana v
June 24, 2025
Introduction: The Evolution of Third-Party Risk Management Businesses today rely on third-party vendors for everything from cloud services to data processing. These...
kalpana v
June 23, 2025
Hybrid data centers have become the backbone of modern enterprise IT. These environments integrate on-premises infrastructure with public and private cloud platforms,...
kalpana v
June 17, 2025
Every organization, big or small, faces uncertainty. It could be a data breach waiting to happen, a missed regulatory deadline, or risks...
kalpana v
June 13, 2025
In February 2023, Karmak, a leading business software provider in the trucking industry, was hit by a ransomware attack. Thanks to a...
kalpana v
June 6, 2025
Banks today work in a fast-moving, always-connected digital world. With every new API, cloud platform, third-party service, remote employee, or customer-facing app,...
kalpana v
June 4, 2025
Most companies today aren’t operating in just one environment. They’ve got systems running in the cloud, some in private data centers, and...
kalpana v
May 29, 2025
As cyber threats grow in sophistication and scale, traditional security models that once protected corporate networks are no longer sufficient. Businesses today...
kalpana v
May 28, 2025
Governance, Risk, and Compliance (GRC) functions have evolved from reactive compliance checkpoints into proactive strategic enablers. However, this evolution brings a new...
kalpana v
May 28, 2025
83% of enterprise buyers require SOC 2 compliance before vendor onboarding—making it not just a regulatory checkbox, but a mission-critical enabler of...
kalpana v
May 28, 2025
Think of a compliance report like a routine health check-up for your organization. It might not be the most exciting appointment on...
kalpana v
May 15, 2025
Many organizations treat risk assessments as annual checklists, missing the dynamic threats that truly matter. This guide dives into the top 10...
kalpana v
May 15, 2025
The GRC (Governance, Risk, and Compliance) technology landscape is vast. It touches nearly every part of a company’s operations—from policy management and...
kalpana v
May 8, 2025
Introduction: When Compliance Blocks Market Entry Sometimes, a region’s regulatory compliance rules block businesses from entering a market. That’s exactly what happened...
kalpana v
May 8, 2025
Banks today operate in a high-stakes environment, managing sensitive financial data, digital customer interactions, and a growing portfolio of online services. These...
kalpana v
April 29, 2025
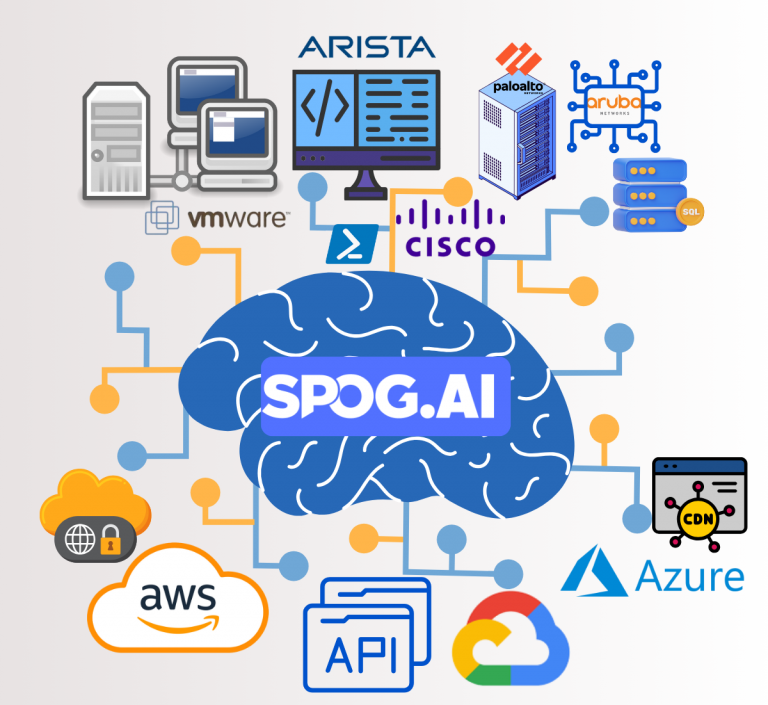
“Just connect the API.” It’s something that we commonly hear in GRC automation—and one of the least useful if you’re dealing with...
kalpana v
April 29, 2025
Stuck Between Risk and Compliance? That’s the Real Risk. Discover why treating them as rivals is holding your organization back—and how smart...
kalpana v
April 29, 2025
Compliance fatigue is real—and it’s putting your security at risk.When checklists replace critical thinking, organizations become vulnerable. Learn how to move beyond...
kalpana v
April 29, 2025
In the Banking, Financial Services, and Insurance (BFSI) sector, many organizations still rely on traditional risk management frameworks like the Three Lines...
kalpana v
April 1, 2025
Compliance isn’t just about meeting regulatory requirements; it’s about safeguarding your organization from risks that can cost millions. Yet, many companies still...
kalpana v
March 28, 2025
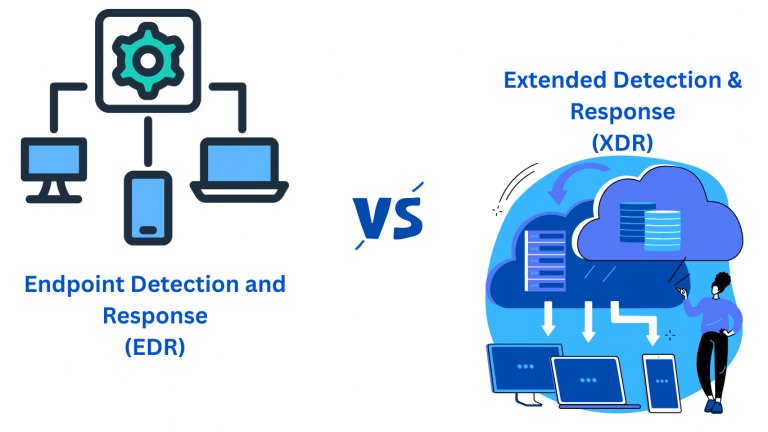
Cyber threats are faster, stealthier, and more coordinated than ever — and your tools need to keep up. This article dives into...
kalpana v
March 25, 2025
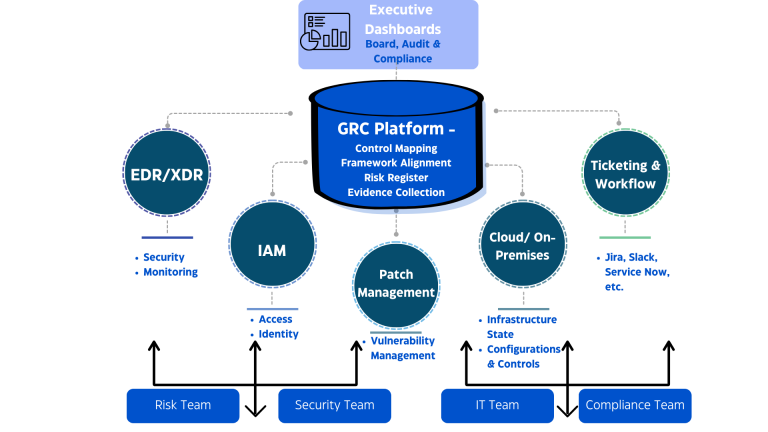
Your team ships code every day. But your audit still runs once a year. In between, things break. Evidence gets lost. Risk...
kalpana v
March 20, 2025
Protection starts with people. And, if you have not recognized this yet, you are overlooking the human element in security. In fact,...
kalpana v
March 18, 2025
Imagine trying to find your way through a maze where many paths look the same, but each has different rules. Organizations face...
kalpana v
March 17, 2025
This article explores the best ways to identify and manage cyber risks. By using techniques like scenario modeling, machine learning analytics, and...
kalpana v
March 12, 2025
Ignoring compliance is not just a legal risk. It is a financial mistake. But there is a better way. Let’s dive into...
kalpana v
March 10, 2025
Most organizations approach risk audits the way they approach an annual health check-up—routine, compliance-driven, and often surface-level. If nothing appears broken, it’s...
kalpana v
March 7, 2025
Did you know that nearly 67% of businesses reported an increase in data privacy violations in 2024 compared to the previous year?....
kalpana v
March 5, 2025
Cyber threats aren’t slowing down. Every day, security teams are fighting fires, trying to keep up with evolving risks, compliance demands, and...
kalpana v
March 3, 2025
Every CISO and cybersecurity leader faces the same challenge. You invest in advanced vulnerability management (VM) tools, run regular scans, and patch...
kalpana v
February 27, 2025
Cyber threats are rising, and SEBI’s Cybersecurity and Cyber Resilience Framework (CSCRF) sets strict mandates to protect financial entities. With a March...
kalpana v
February 25, 2025
Governance, Risk, and Compliance (GRC) functions often operate in silos, leading to inefficiencies, higher costs, and increased regulatory risks. Disjointed processes create...
kalpana v
February 24, 2025
With AI transforming industries at an unprecedented pace, the risks of bias, privacy violations, and regulatory non-compliance are skyrocketing. Global regulations like...
