Data Breach Prevention: Build Controls That Protect Data Before Attackers Arrive

Data Breach Prevention: Build Controls That Protect Data Before Attackers Arrive

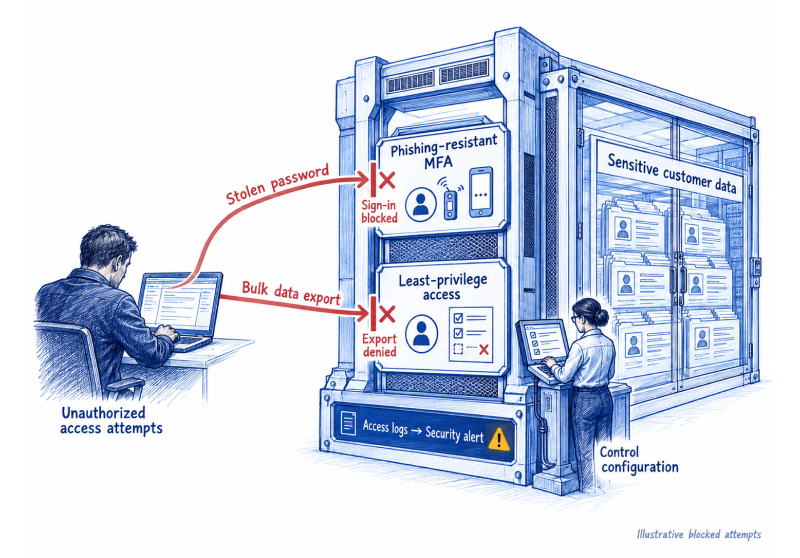
A practical guide to reducing the paths attackers can use to reach sensitive information.Build prevention around data, identity, and access decisions your teams can verify, not a checklist that looks...

Categories: Compliance, Cyber Risk, Cybersecurity
CERT-In’s 12-Hour Remediation Window: Why Faster Patching Is Not Enough

CERT-In’s 12-Hour Remediation Window: Why Faster Patching Is Not Enough

CERT-In’s 2026 vulnerability remediation guidance challenges how enterprises manage cyber exposure. Meeting shorter remediation windows requires continuous exposure intelligence, faster decisions, and verified risk reduction, not simply faster patch deployment....

Categories: Compliance

Cyber Risk and Compliance Risk: Decide What Needs Action

Cyber Risk and Compliance Risk: Decide What Needs Action

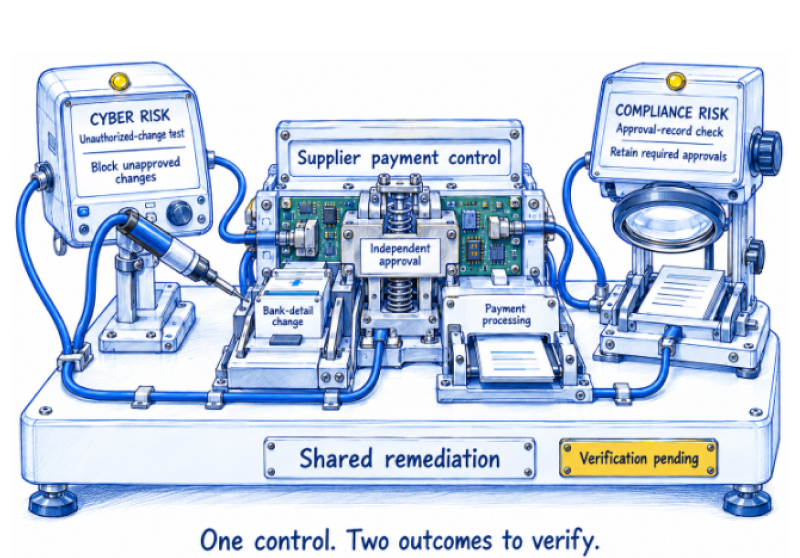
Cyber risk and compliance risk can share the same control weakness while requiring different decisions. Learn how mid-market teams can assess business harm and applicable obligations together, coordinate corrective action...

Categories: Compliance, Risk Management
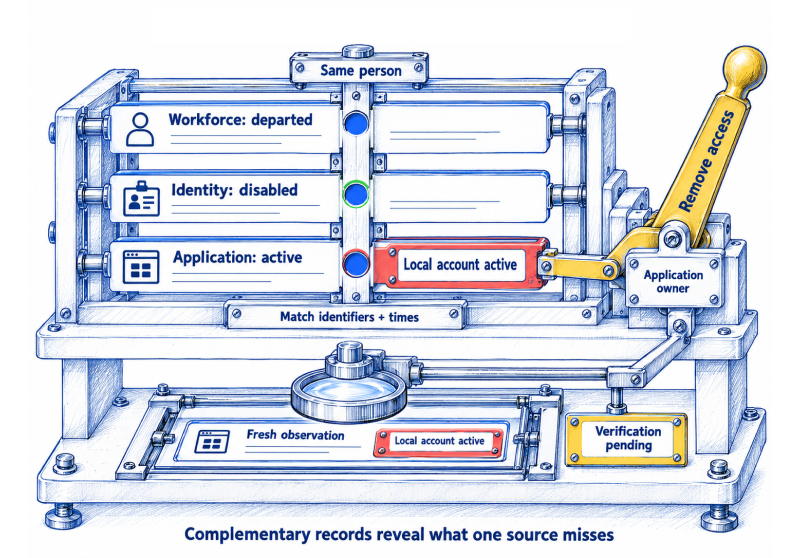
Compliance Automation: Make Your Integrations Count for Trusted Control Evidence

Compliance Automation: Make Your Integrations Count for Trusted Control Evidence

Integrations connect cloud, identity, endpoint and business systems to automate evidence collection and coordinate compliance workflows. They reduce repeated requests, support control assessments and route exceptions to accountable owners. The...

Categories: Compliance

Compliance Monitoring in 2026: Detect Evidence Gaps and Verify Control Results

Compliance Monitoring in 2026: Detect Evidence Gaps and Verify Control Results

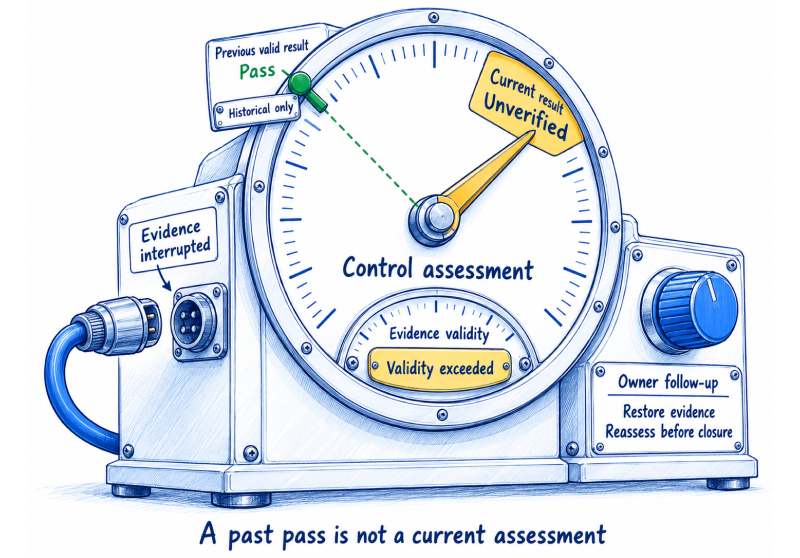
Compliance Monitoring in 2026: Detect Evidence Gaps and Verify Control Results A passing result is only useful when its coverage, evidence and test remain valid. Learn how to distinguish control...

Categories: Compliance

SaaS Compliance in 2026: A Checklist for Control Ownership and Clear Evidence

SaaS Compliance in 2026: A Checklist for Control Ownership and Clear Evidence

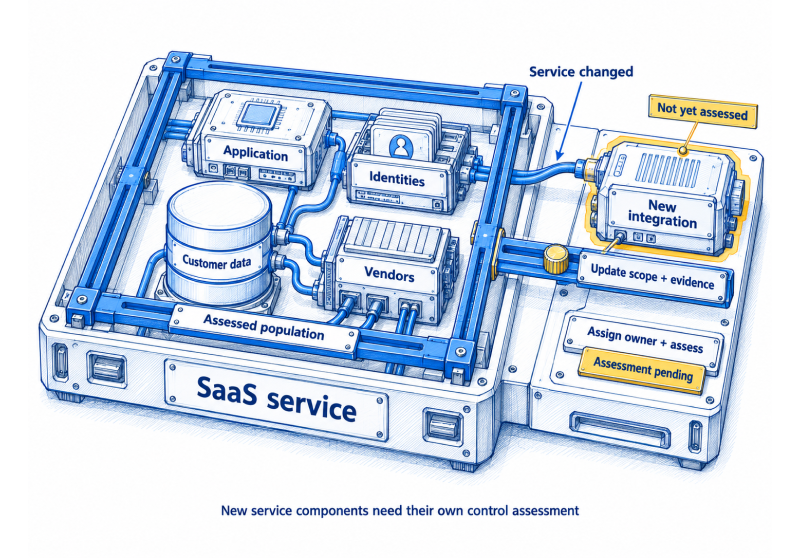
Build a SaaS compliance program around the services you deliver and the obligations that apply. Use this practical checklist to clarify cloud responsibilities, assign control owners and verify evidence as...

Categories: Compliance, GRC

Backup Checklist in 2026: Verify Recovery for Security and Compliance Teams

Backup Checklist in 2026: Verify Recovery for Security and Compliance Teams

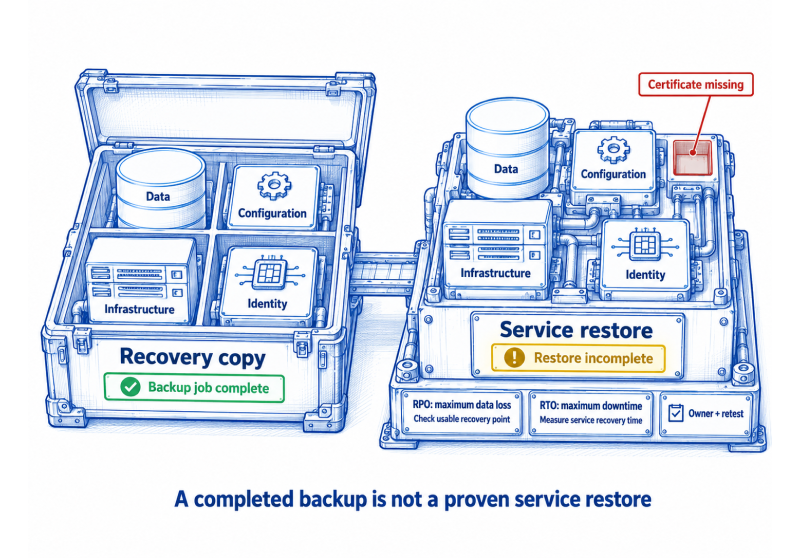
A successful backup job does not prove that a service can be restored. Use this checklist to define recovery coverage, set RPO and RTO targets, protect recovery copies and verify...

Categories: Compliance, Cyber Risk, Risk Management
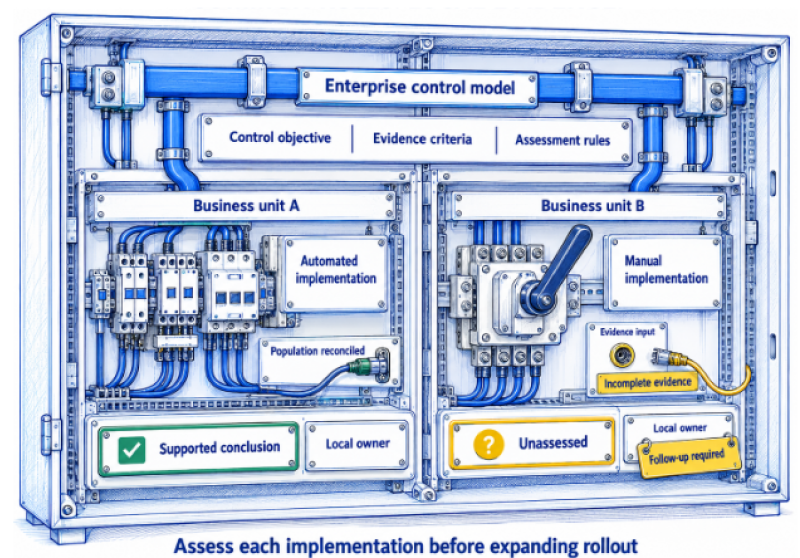
How to Roll Out Enterprise GRC: Prove the Model Before You Scale

How to Roll Out Enterprise GRC: Prove the Model Before You Scale

Enterprise GRC needs consistent assessments across business units while preserving local responsibilities and obligations. Establish clear ownership, reliable evidence and a complete pilot control cycle before expanding, so each rollout...

Categories: Compliance, GRC, Risk Management
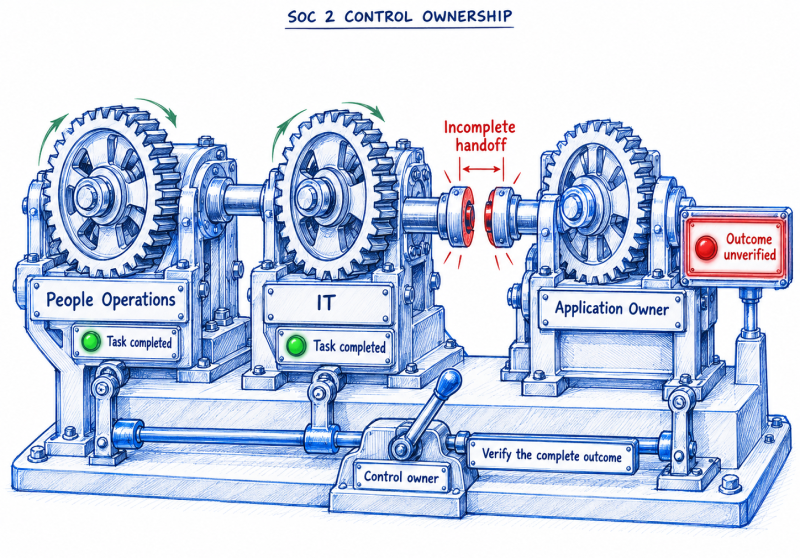
SOC 2 Control Ownership: Define Clear Roles and Validate Evidence Without a CISO

SOC 2 Control Ownership: Define Clear Roles and Validate Evidence Without a CISO

Build a practical SOC 2 control list with clear owners, reliable evidence and complete handoffs across teams. Learn how to manage responsibilities without a CISO, address missed controls and verify...

Categories: Compliance, GRC

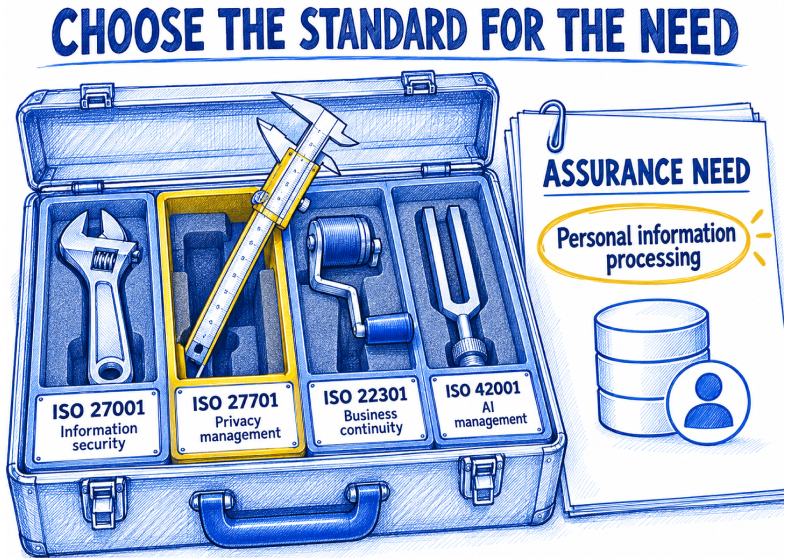
ISO Security Standards in 2026: Which Ones Matter for Your Organization?

ISO Security Standards in 2026: Which Ones Matter for Your Organization?

Choose ISO security standards based on your business needs, responsibilities and the assurance stakeholders expect. Compare security, privacy, cloud, continuity and AI standards, and understand where certification, guidance and shared...

Categories: Compliance, GRC, ISO 27001
Why Compliance Doesn’t Equal Resilience

Why Compliance Doesn’t Equal Resilience

Introduction — When the Cloud Shakes, Compliance Crumbles When AWS’s US-east-1 region went dark, so did thousands of companies. These weren’t reckless startups or poorly managed systems; they were organizations...

Categories: Compliance

DPDP Act & Rules 2025: The Compliance Readiness Checklist 

DPDP Act & Rules 2025: The Compliance Readiness Checklist 

As India accelerates toward becoming a digital-first economy, regulatory frameworks are increasingly shaping how enterprises manage data, AI, and security operations. At the heart of this transformation lies the Digital...

Categories: Compliance

Unifying Remediation and Compliance with Integrated Incident Response

Unifying Remediation and Compliance with Integrated Incident Response

When it comes to responding to incidents, time is of the essence. The first few minutes often bring chaos—analysts must quickly switch between tools, evaluate the scope of impact, and...

Categories: Compliance

Setting Up a GDPR Compliance Monitoring and Audit Program: Steps and Checklist

Setting Up a GDPR Compliance Monitoring and Audit Program: Steps and Checklist

Achieving GDPR compliance is only the beginning, maintaining it is the real challenge. The General Data Protection Regulation (GDPR) demands that organizations not only put privacy controls in place but...

Categories: Compliance

Automated Access Reviews: Strengthening Security, Simplifying Compliance

Automated Access Reviews: Strengthening Security, Simplifying Compliance

Access reviews play a key role in meeting security and regulatory standards. But many companies still handle them manually, creating risk and complexity. According to The State of Access Review...

Categories: Compliance

The Complete Guide to Data Center Security and Compliance (with an actionable checklist)

The Complete Guide to Data Center Security and Compliance (with an actionable checklist)

Hybrid data centers have become the backbone of modern enterprise IT. These environments integrate on-premises infrastructure with public and private cloud platforms, offering agility, control, and performance. But as architecture...

Categories: Compliance

How to Prepare for a SOC 2 Type II Audit in Half the Time

How to Prepare for a SOC 2 Type II Audit in Half the Time

83% of enterprise buyers require SOC 2 compliance before vendor onboarding—making it not just a regulatory checkbox, but a mission-critical enabler of business growth and a gatekeeper for market access....

Categories: Compliance

What to Include in a High-Impact Compliance Report (With Examples)

What to Include in a High-Impact Compliance Report (With Examples)

Think of a compliance report like a routine health check-up for your organization. It might not be the most exciting appointment on the calendar, but it’s essential. Just as a...

Categories: Compliance

How Compliance Fatigue Undermines Security

How Compliance Fatigue Undermines Security

Compliance fatigue is real—and it’s putting your security at risk.When checklists replace critical thinking, organizations become vulnerable. Learn how to move beyond box-ticking and build a security culture that stays...

Categories: Compliance

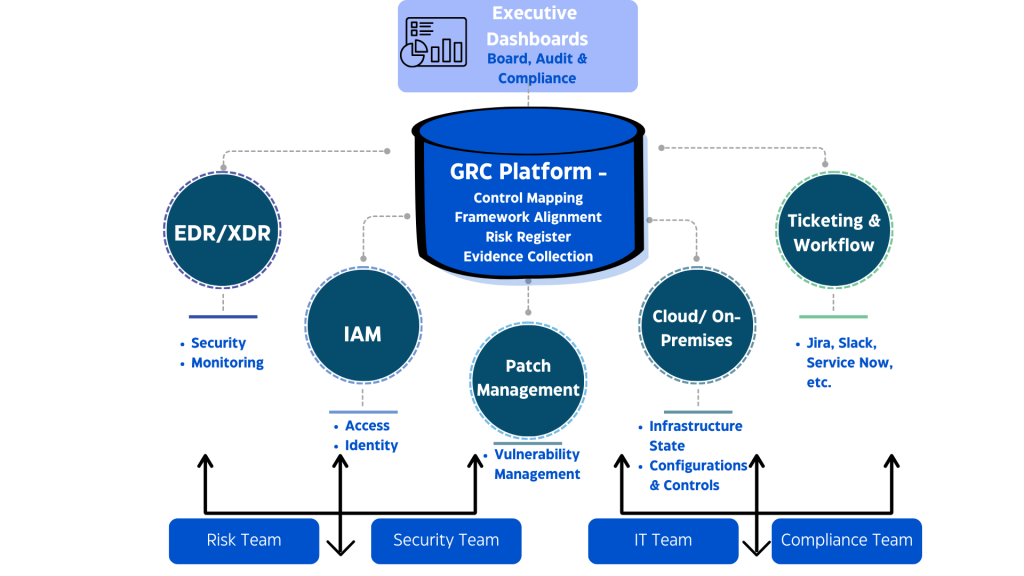
The Tech Stack for Ongoing Compliance: Integrations that Matter

The Tech Stack for Ongoing Compliance: Integrations that Matter

Your team ships code every day. But your audit still runs once a year. In between, things break. Evidence gets lost. Risk data lives in ten different places. Most companies...

Categories: Compliance

Navigating Multiple Frameworks: ISO 27001, SOC 2, GDPR, and Beyond

Navigating Multiple Frameworks: ISO 27001, SOC 2, GDPR, and Beyond

Imagine trying to find your way through a maze where many paths look the same, but each has different rules. Organizations face this challenge when complying with multiple security and...

Categories: Compliance

The ROI of Real-Time Compliance: Cost Savings and Risk Reduction

The ROI of Real-Time Compliance: Cost Savings and Risk Reduction

Ignoring compliance is not just a legal risk. It is a financial mistake. But there is a better way. Let’s dive into it! Many companies see compliance as a burden....

Categories: Compliance

Continuous Compliance Demystified: From Checklists to Real-Time Insights

Continuous Compliance Demystified: From Checklists to Real-Time Insights

Did you know that nearly 67% of businesses reported an increase in data privacy violations in 2024 compared to the previous year?. That's a clear sign that traditional compliance methods...

Categories: Compliance

SEBI CSCRF: The Ultimate Guide for SEBI-Regulated Entities

SEBI CSCRF: The Ultimate Guide for SEBI-Regulated Entities

Cyber threats are rising, and SEBI’s Cybersecurity and Cyber Resilience Framework (CSCRF) sets strict mandates to protect financial entities. With a March 31, 2025 deadline, firms must act now to...

Categories: Compliance

AI Compliance Frameworks: Why They Matter and What You Need to Know

AI Compliance Frameworks: Why They Matter and What You Need to Know

With AI transforming industries at an unprecedented pace, the risks of bias, privacy violations, and regulatory non-compliance are skyrocketing. Global regulations like the EU AI Act, NIST AI RMF, ISO/IEC...

Categories: Compliance