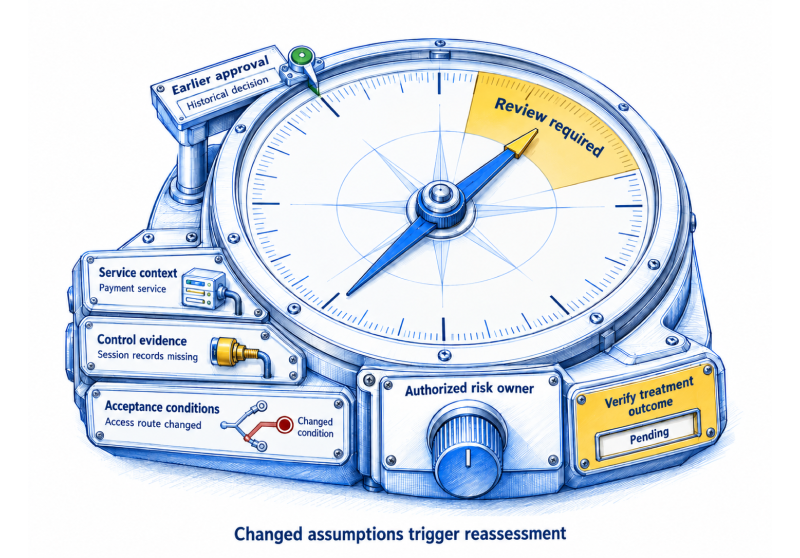
Enterprise GRC in 2026: Connect Cyber Risk, Evidence and Accountable Decisions

Enterprise GRC in 2026: Connect Cyber Risk, Evidence and Accountable Decisions

Effective enterprise GRC connects cyber risk to business services, current control evidence and accountable owners. Learn how to reassess decisions when conditions change, manage exceptions and verify treatment outcomes. A...

Categories: Cyber Risk, ISO 27001

ISO 27001 Certification in 2026: Readiness, Audit Evidence and What Happens Next

ISO 27001 Certification in 2026: Readiness, Audit Evidence and What Happens Next

Prepare for ISO 27001 certification with a clear scope, traceable evidence and accountable control owners. Understand the audit stages, timeline and cost factors, and what it takes to maintain your...

Categories: ISO 27001

ISO 27001 in 2026: Keep Controls Aligned as Business Changes

ISO 27001 in 2026: Keep Controls Aligned as Business Changes

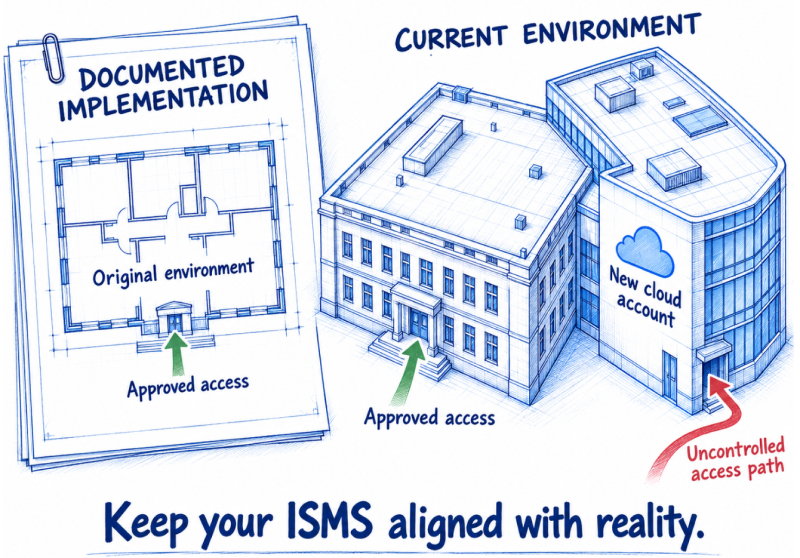
An effective ISO 27001 program keeps control scope, the Statement of Applicability and supporting evidence aligned as services, identities and suppliers change. Clear ownership, checks on coverage and effectiveness, and...

Categories: ISO 27001

ISO 27001 Change Management: From Approval to Verified Outcome

ISO 27001 Change Management: From Approval to Verified Outcome

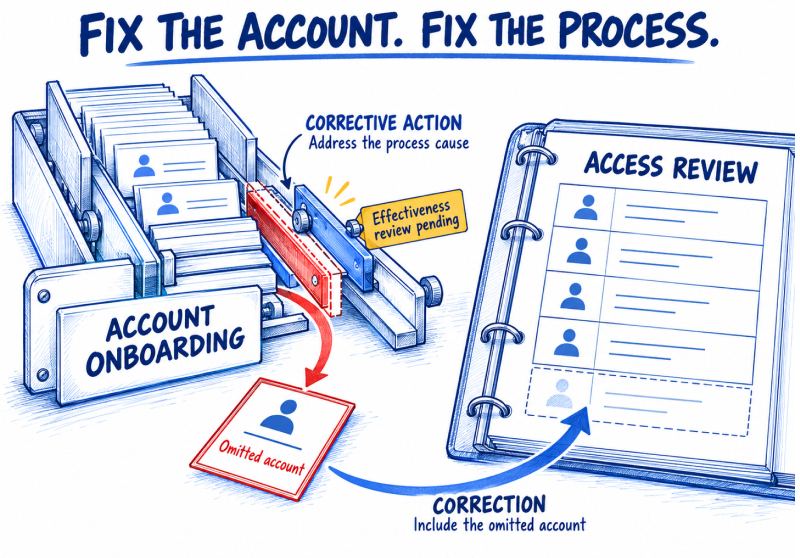
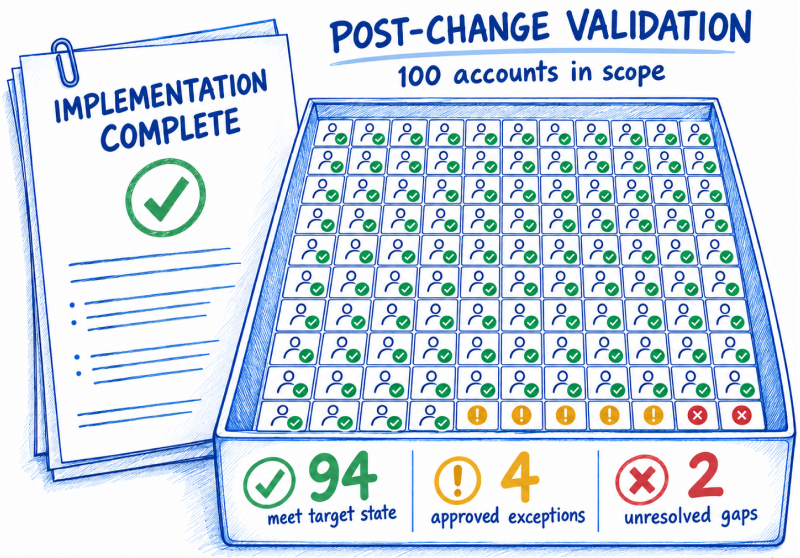
An approved change can still leave a security control in the wrong state. Connect ISO 27001 change management with post-change validation to verify control outcomes, resolve gaps and retain evidence...

Categories: ISO 27001

ISO Security Standards in 2026: Which Ones Matter for Your Organization?

ISO Security Standards in 2026: Which Ones Matter for Your Organization?

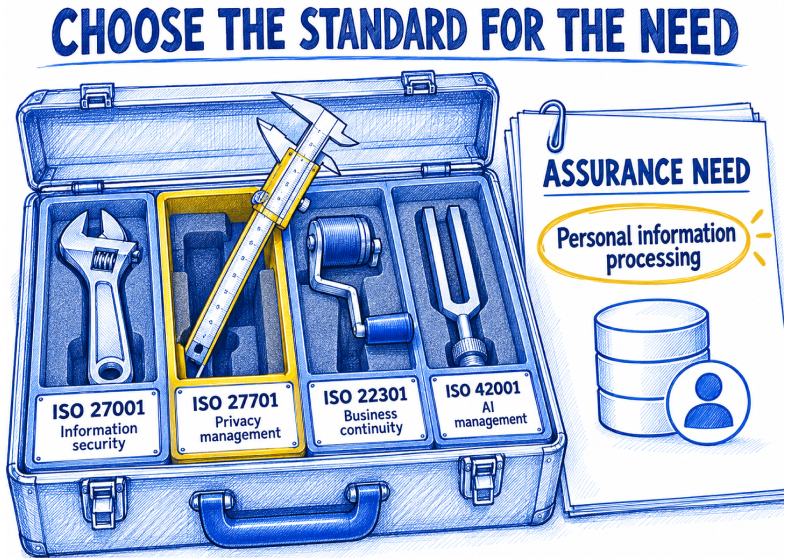
Choose ISO security standards based on your business needs, responsibilities and the assurance stakeholders expect. Compare security, privacy, cloud, continuity and AI standards, and understand where certification, guidance and shared...

Categories: Compliance, GRC, ISO 27001
ISO 27001:2022 Update – Are You Ready for the New Compliance Requirements?

ISO 27001:2022 Update – Are You Ready for the New Compliance Requirements?

The latest ISO 27001:2022 update brings critical changes to information security, risk management, and compliance requirements. With a stronger focus on cyber resilience, supply chain security, and evolving threats, organizations...

Categories: ISO 27001