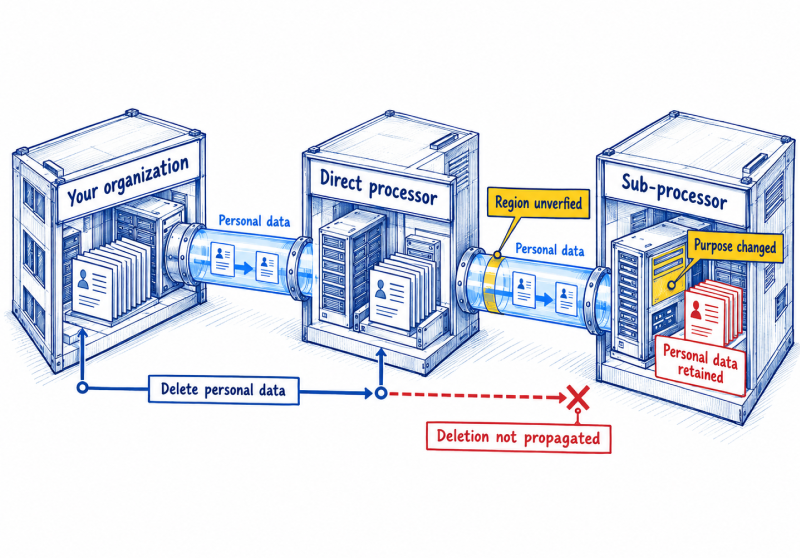
Sub-Processor Risk Management: Keep Privacy Controls Across Data Chains

Sub-Processor Risk Management: Keep Privacy Controls Across Data Chains

A direct vendor is only the first link in a personal-data chain. Build a program that keeps purpose, location, authorization, safeguards, and evidence connected as downstream processors change. Sub-processor risk...

Categories: GRC

Cybersecurity Risk Management Techniques: Choose the Right Method

Cybersecurity Risk Management Techniques: Choose the Right Method

Different risk questions need different methods. Compare practical techniques, see how two methods reach different decisions on the same supplier scenario, and choose an approach that fits the evidence and...

Categories: Cybersecurity, GRC, Risk Management
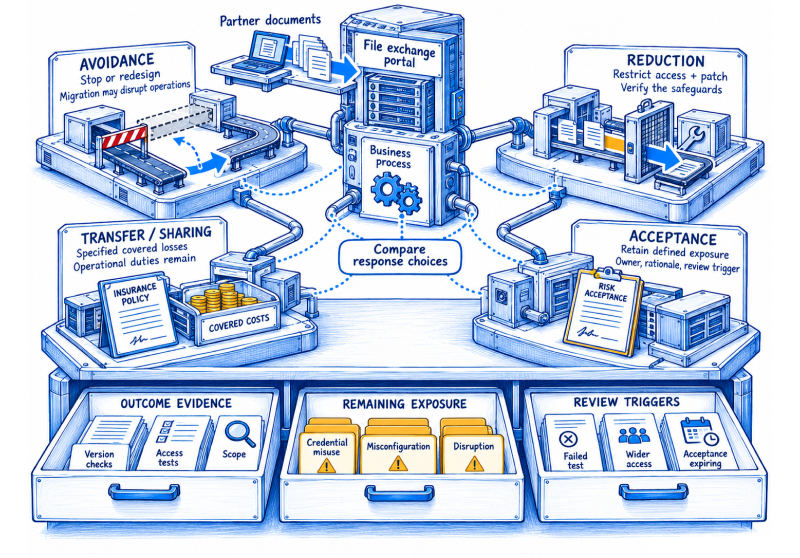
Risk Mitigation Strategies: Comparing Treatment Choices and Trade-offs in Practice

Risk Mitigation Strategies: Comparing Treatment Choices and Trade-offs in Practice

Risk mitigation is often used to mean reducing exposure, while risk treatment covers the full set of response choices. Learn how to compare avoidance, reduction, transfer and acceptance, then verify...

Categories: Cybersecurity, GRC, Risk Management
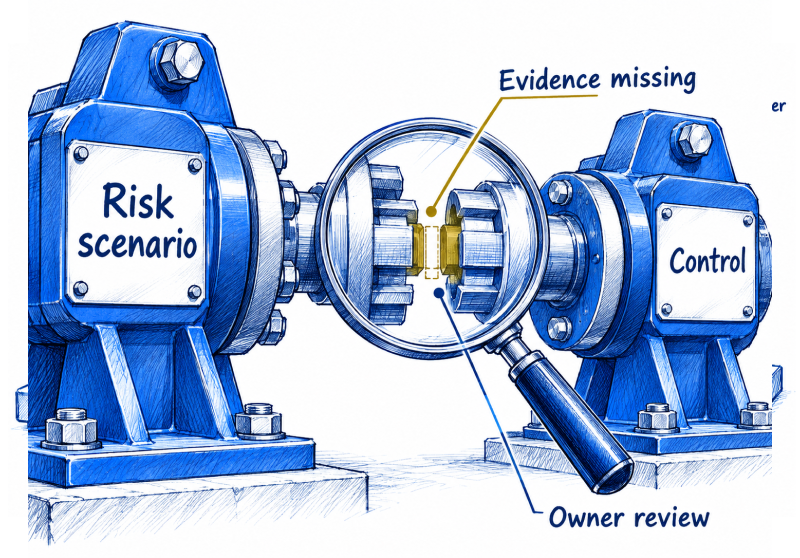
Risk Control Matrix: Connect Cybersecurity Risks to Controls and Useful Evidence

Risk Control Matrix: Connect Cybersecurity Risks to Controls and Useful Evidence

A risk control matrix makes clear how a defined business risk is addressed, who owns the response, and what evidence shows the control works. For cybersecurity and GRC teams, its...

Categories: Cybersecurity, GRC, Risk Management
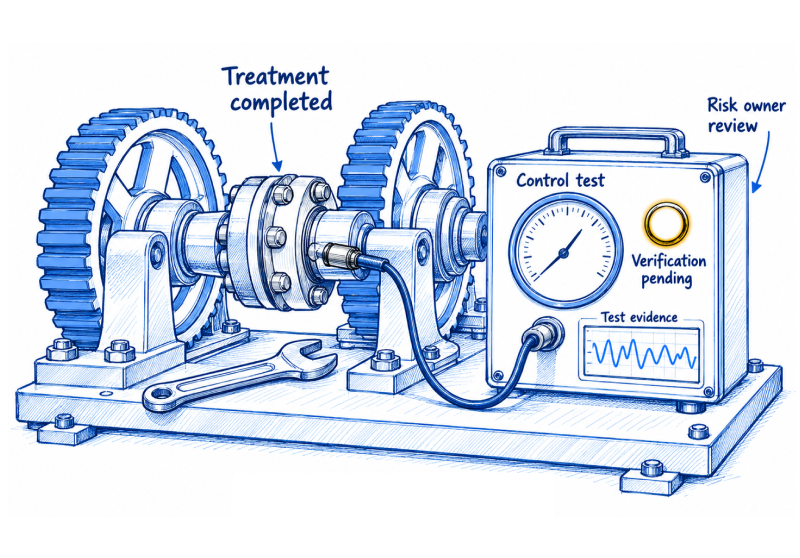
Operational Risk Management in 2026: Keep Decisions Current as Operations Change

Operational Risk Management in 2026: Keep Decisions Current as Operations Change

Operational risk management helps leaders understand how everyday activity can disrupt critical services, and what to do before a weakness becomes a loss. A practical program connects risk scenarios to...

Categories: Cybersecurity, GRC, Risk Management
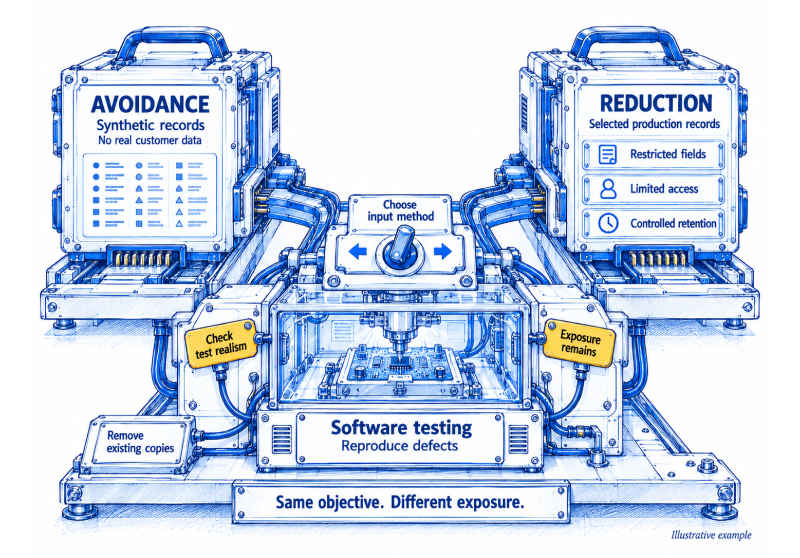
Risk Avoidance vs Risk Reduction in 2026: Choosing the Right Business Response

Risk Avoidance vs Risk Reduction in 2026: Choosing the Right Business Response

Compare the value of continuing an activity with the cost of withdrawing, and choose a response that addresses the specific exposure. Risk avoidance vs risk reduction asks a practical business...

Categories: Cybersecurity, GRC, Risk Management
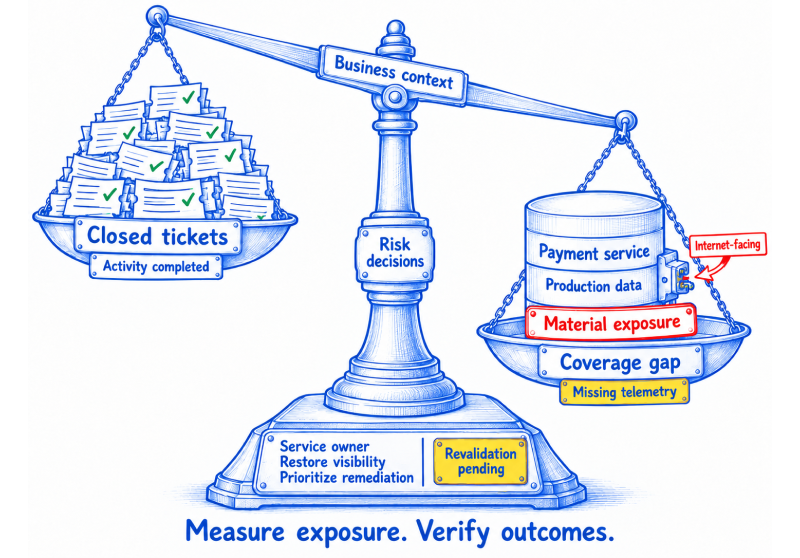
Cybersecurity Metrics in 2026: Link Control Evidence to Better Risk Decisions

Cybersecurity Metrics in 2026: Link Control Evidence to Better Risk Decisions

Useful cybersecurity metrics show where material exposure remains, who needs to act and whether corrective work reduced the risk. Learn how to define populations, keep exceptions visible and connect control...

Categories: Cybersecurity, GRC

Build a Risk Register in 2026 With Clear Evidence and Traceable Business Decisions

Build a Risk Register in 2026 With Clear Evidence and Traceable Business Decisions

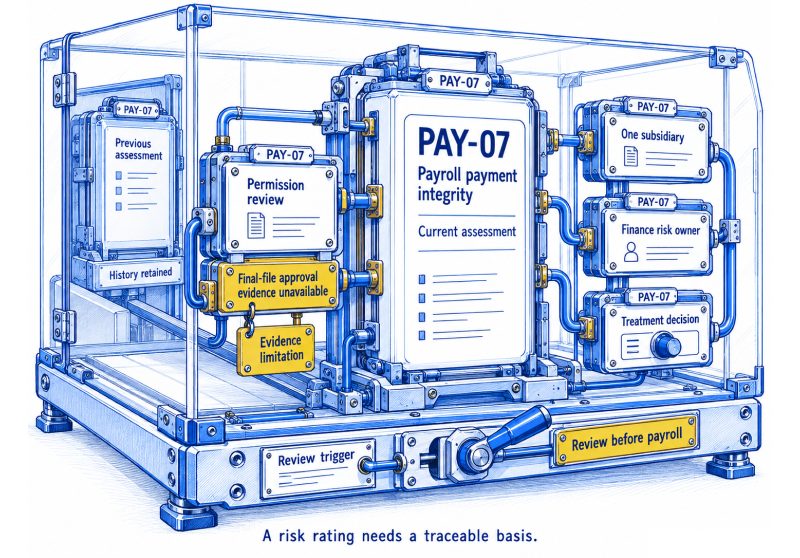
A risk rating needs a clear basis and a record of the decision behind it. Build risk entries that connect business scenarios with evidence, ownership and review triggers, keeping current...

Categories: Cybersecurity, GRC, Risk Management
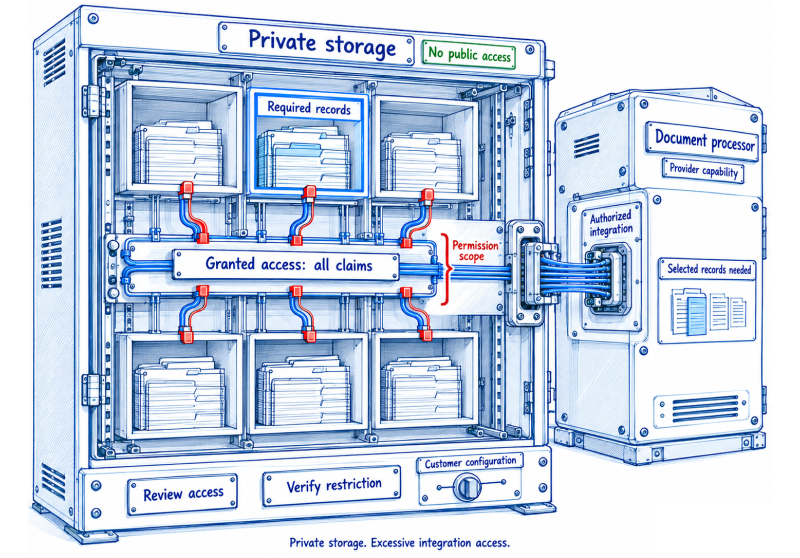
Cloud Risk Management in 2026: Map Ownership Across Services and Dependencies

Cloud Risk Management in 2026: Map Ownership Across Services and Dependencies

Cloud risk extends beyond configuration settings. Map identity access, data flows and provider responsibilities across connected services to identify hidden exposure, assign ownership and test whether recovery dependencies hold up....

Categories: Cloud Security, GRC, Risk Management
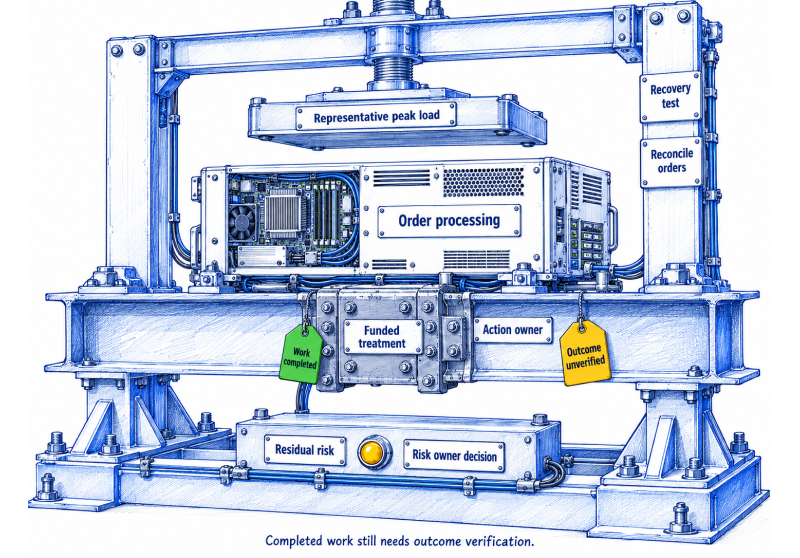
Risk Management Plan in 2026: Turn Decisions into Funded and Accountable Actions 

Risk Management Plan in 2026: Turn Decisions into Funded and Accountable Actions 

Risk decisions need funding, ownership and follow-through. Build a risk management plan that connects response choices to accountable actions, tracks delivery and keeps remaining exposure visible as conditions change. A...

Categories: Cybersecurity, GRC, Risk Management
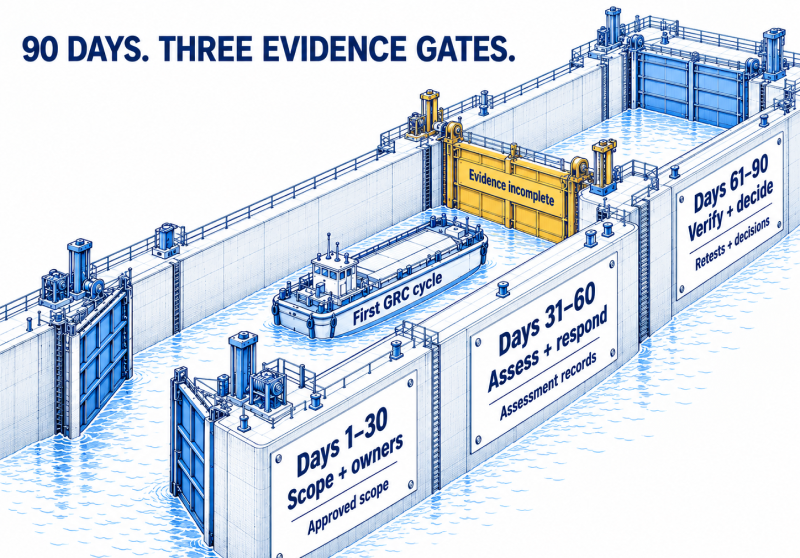
A 90-Day GRC Roadmap: From Scope and Ownership to Verified Controls Across Teams

A 90-Day GRC Roadmap: From Scope and Ownership to Verified Controls Across Teams

Establish a first GRC voyage in 90 days, with clear scope, accountable owners and evidence that supports control decisions. Follow three practical phases to assess priority controls, verify remediation and...

Categories: GRC

GRC Maturity That Holds Up Under Change: Align Evidence, Ownership and Decisions

GRC Maturity That Holds Up Under Change: Align Evidence, Ownership and Decisions

Help lean GRC teams support growing compliance demands with clear ownership, reliable evidence and selective automation. Reduce repeated follow-up, keep exceptions visible and verify remediation while measuring whether the team...

Categories: GRC

IT GRC: Keep Accountability Intact When Technology Changes

IT GRC: Keep Accountability Intact When Technology Changes

IT governance, risk management, and compliance (IT GRC) should help a CISO answer a difficult operational question: when technology changes, do the business's risk decisions and control assurances still hold?...

Categories: GRC

SaaS Compliance in 2026: A Checklist for Control Ownership and Clear Evidence

SaaS Compliance in 2026: A Checklist for Control Ownership and Clear Evidence

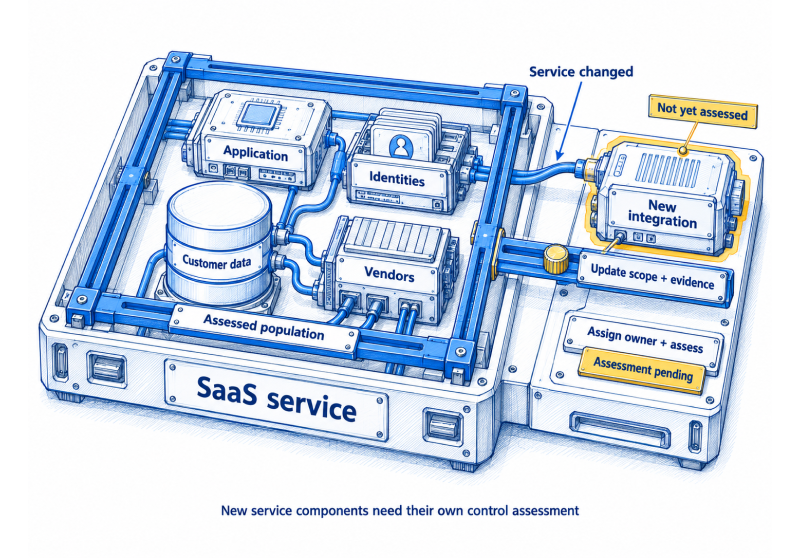
Build a SaaS compliance program around the services you deliver and the obligations that apply. Use this practical checklist to clarify cloud responsibilities, assign control owners and verify evidence as...

Categories: Compliance, GRC

How to Roll Out Enterprise GRC: Prove the Model Before You Scale

How to Roll Out Enterprise GRC: Prove the Model Before You Scale

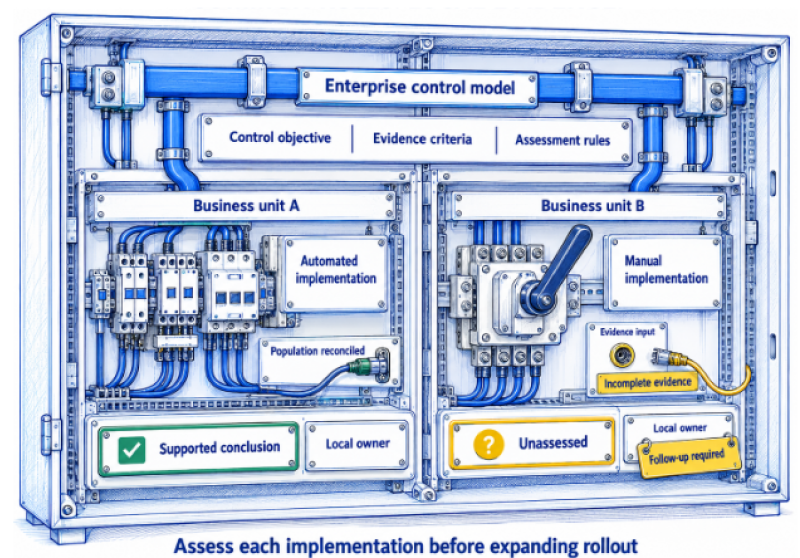
Enterprise GRC needs consistent assessments across business units while preserving local responsibilities and obligations. Establish clear ownership, reliable evidence and a complete pilot control cycle before expanding, so each rollout...

Categories: Compliance, GRC, Risk Management
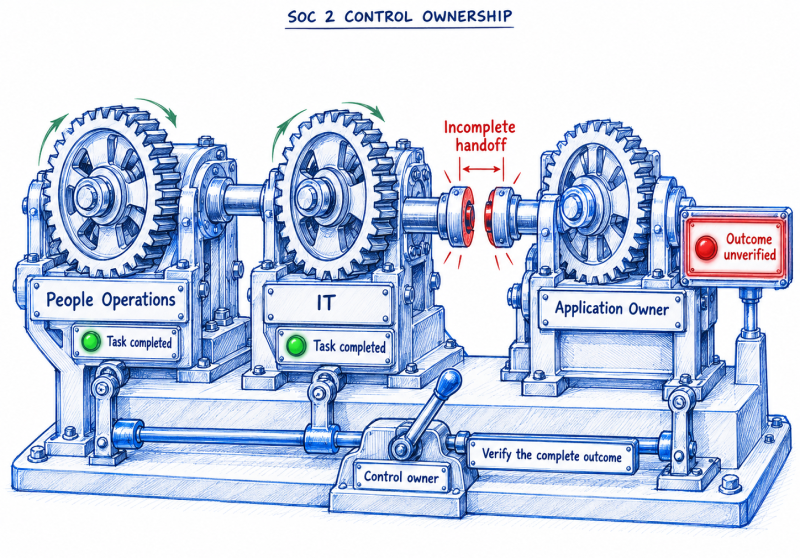
SOC 2 Control Ownership: Define Clear Roles and Validate Evidence Without a CISO

SOC 2 Control Ownership: Define Clear Roles and Validate Evidence Without a CISO

Build a practical SOC 2 control list with clear owners, reliable evidence and complete handoffs across teams. Learn how to manage responsibilities without a CISO, address missed controls and verify...

Categories: Compliance, GRC

ISO Security Standards in 2026: Which Ones Matter for Your Organization?

ISO Security Standards in 2026: Which Ones Matter for Your Organization?

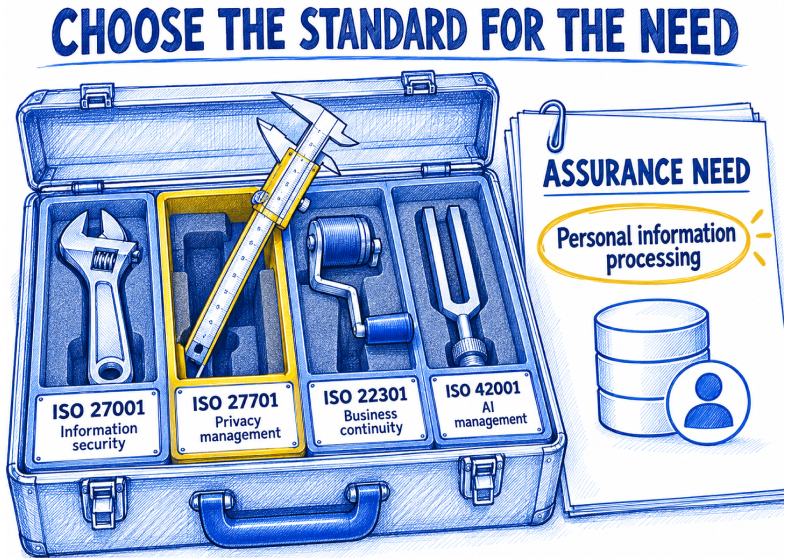
Choose ISO security standards based on your business needs, responsibilities and the assurance stakeholders expect. Compare security, privacy, cloud, continuity and AI standards, and understand where certification, guidance and shared...

Categories: Compliance, GRC, ISO 27001
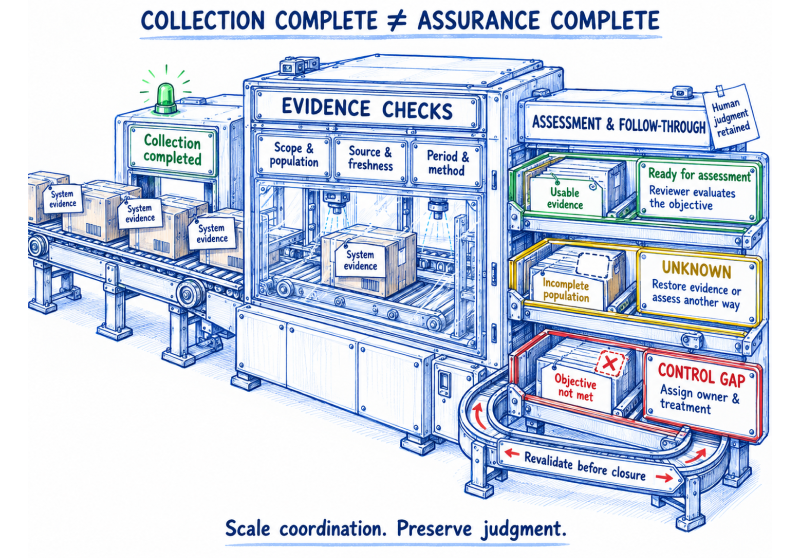
How Lean GRC Teams Can Scale Compliance Without Adding Headcount

How Lean GRC Teams Can Scale Compliance Without Adding Headcount

Help lean GRC teams support growing compliance demands with clear ownership, reliable evidence and selective automation. Reduce repeated follow-up, keep exceptions visible and verify remediation while measuring whether the team...

Categories: GRC

5 Reasons You Need to Move from Spreadsheets to GRC Tools for Compliance Management

5 Reasons You Need to Move from Spreadsheets to GRC Tools for Compliance Management

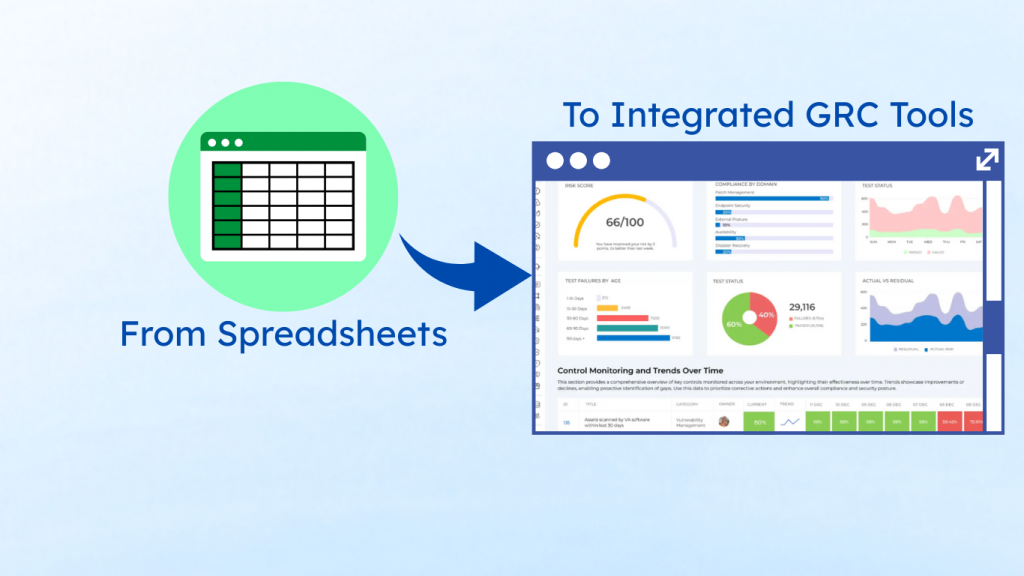
For years, spreadsheets have been the go-to tool for managing governance, risk, and compliance (GRC). They’re familiar, easy to set up, and cost nothing more than a license most businesses...

Categories: GRC

GRC Automation for Hybrid Infrastructure

GRC Automation for Hybrid Infrastructure

Most companies today aren’t operating in just one environment. They’ve got systems running in the cloud, some in private data centers, and often a good chunk still sitting on on-premises...

Categories: GRC

The GRC Metrics That Actually Matter

The GRC Metrics That Actually Matter

Governance, Risk, and Compliance (GRC) functions have evolved from reactive compliance checkpoints into proactive strategic enablers. However, this evolution brings a new challenge—how do you prove the value of GRC...

Categories: GRC

GRC Platform Selection Guide: What to Look for Based on Your Maturity Level

GRC Platform Selection Guide: What to Look for Based on Your Maturity Level

The GRC (Governance, Risk, and Compliance) technology landscape is vast. It touches nearly every part of a company’s operations—from policy management and control alignment to risk tracking and data classification....

Categories: GRC

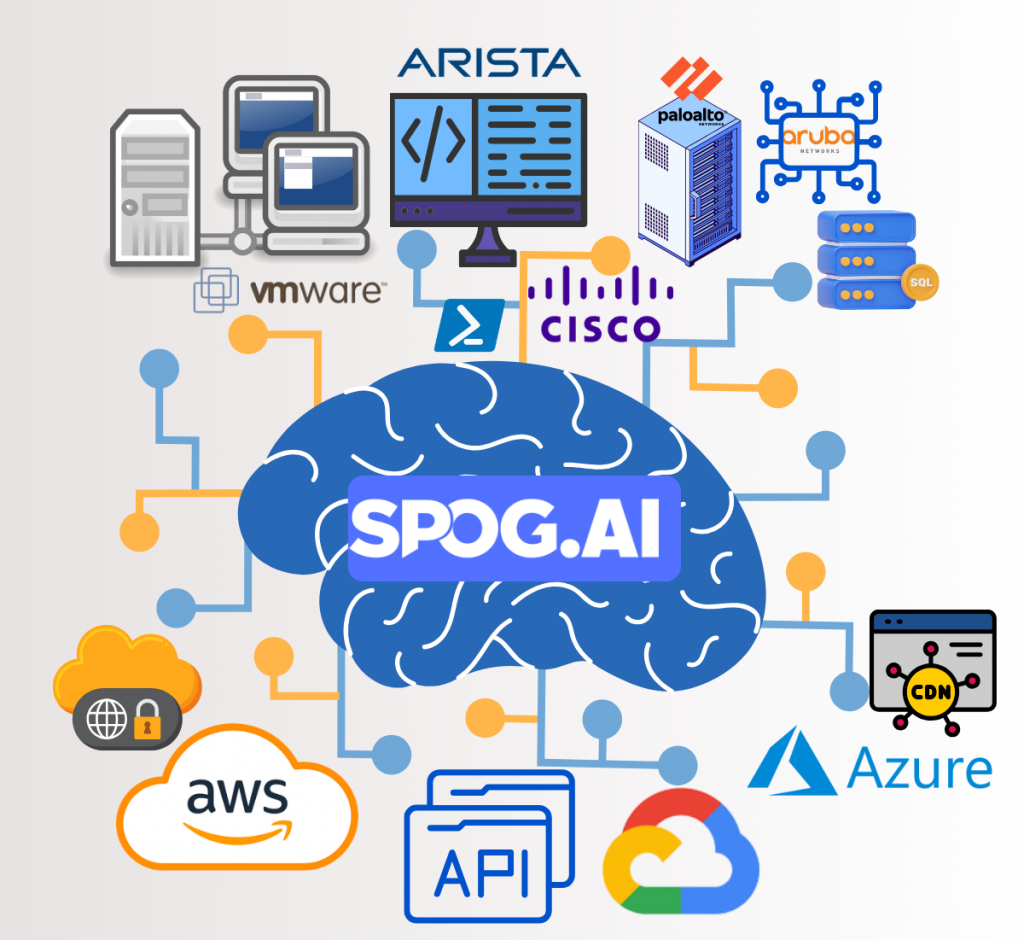
The Need for Hybrid GRC Integrations

The Need for Hybrid GRC Integrations

“Just connect the API.” It’s something that we commonly hear in GRC automation—and one of the least useful if you're dealing with legacy systems. Many Governance, Risk, and Compliance (GRC)...

Categories: GRC

GRC Silos Cost More Than You Think – Here’s Why

GRC Silos Cost More Than You Think – Here’s Why

Governance, Risk, and Compliance (GRC) functions often operate in silos, leading to inefficiencies, higher costs, and increased regulatory risks. Disjointed processes create blind spots, delay incident response, and make compliance...

Categories: GRC