← Back to Blog
Governance
Security Governance on a Budget: Where Mid-Market Teams Should Invest First

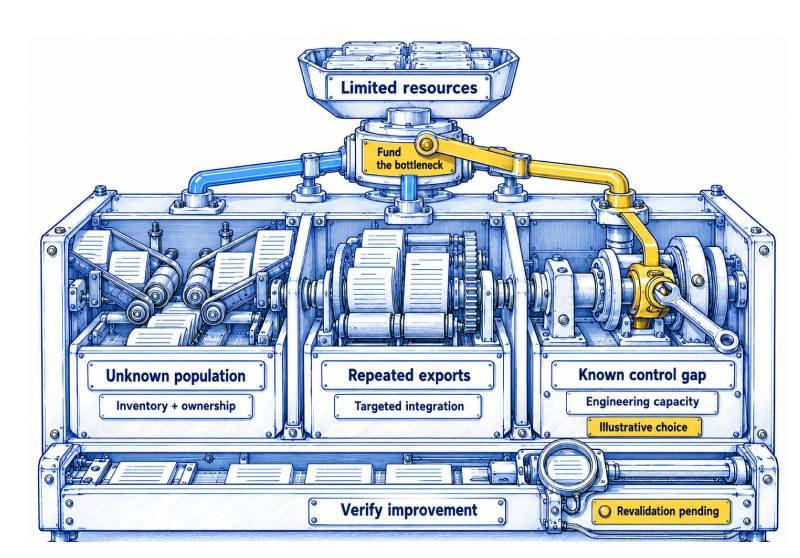
Make limited security budgets count by focusing on critical services, reliable evidence and accountable action. Learn how mid-market teams can identify control gaps and decide where better data, expertise, automation...
Categories: Governance
The Evolution of PCI DSS: From v3.2.1 to v4.0

The Payment Card Industry Data Security Standard (PCI DSS) has long served as the global benchmark for safeguarding cardholder data and reducing the risk of breaches. First introduced in 2004,...
Categories: Governance
CERT-In’s 2025 Cyber Audit Policy: What It Means for India’s Security Ecosystem
On July 25, 2025, the Indian Computer Emergency Response Team (CERT-In) launched a major update to its cybersecurity audit guidelines. These new rules aim to move India’s security posture from...
Categories: Governance
Cyber Security Regulatory Compliance in India: What You Need to Know
Introduction: When Compliance Blocks Market Entry Sometimes, a region’s regulatory compliance rules block businesses from entering a market. That’s exactly what happened with WhatsApp Pay in India. Despite having hundreds...
Categories: Cybersecurity, Governance
Compliance as a Continuous Cycle: Maintaining PCI-DSS, HIPAA, & More
Compliance isn't just about meeting regulatory requirements; it's about safeguarding your organization from risks that can cost millions. Yet, many companies still approach compliance as a one-time project, leaving them...
Categories: Governance