Organizations invest heavily in security tools, compliance programs, and risk management processes. Yet many security leaders still struggle to answer a simple question:
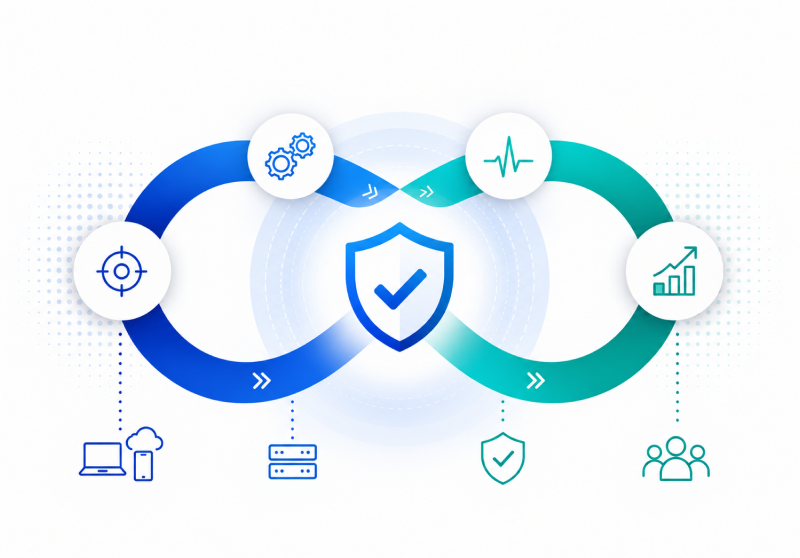
Continuous Assurance is the practice of continuously validating that security controls are deployed, configured correctly, operating as intended, and effectively reducing risk. Unlike audits or periodic assessments, it uses live operational data to continuously measure control effectiveness.
As environments change, assets are added, vulnerabilities emerge, users change roles, and controls drift from their intended configurations. Continuous Assurance helps organizations continuously verify that controls remain effective and aligned with organizational objectives.
As cybersecurity environments become more dynamic and regulatory expectations continue to rise, Continuous Assurance is emerging as a critical capability for modern security programs.
Why Is Continuous Assurance Important?
Most organizations evaluate security through periodic activities such as annual audits, quarterly risk reviews, vulnerability assessments, penetration tests and sompliance assessments.
While valuable, these activities provide only a snapshot of security at a particular point in time. The reality is that environments change constantly. Assets are added and removed, users change roles, vulnerabilities emerge daily, and security controls drift from their intended configurations.
A control that was effective during an audit may no longer be effective a month later. Continuous Assurance helps organizations identify these gaps before they become security incidents.
Continuous Assurance
Continuous Assurance is the practice of continuously validating that security controls are deployed, configured correctly, operational, and effective at reducing risk using live telemetry and automated evidence.
What Is the difference between Continuous Assurance and Continuous Compliance?
These terms are often used interchangeably, but they solve different problems.
Continuous Compliance focuses on demonstrating adherence to regulations, standards, and policies. Examples include ISO 27001, NIST Cybersecurity Framework, CIS Controls, PCI DSS, DORA, SEBI CSCRF. The objective is to prove that required controls exist and supporting evidence can be produced.
Continuous Assurance focuses on validating whether controls are functioning effectively and reducing risk. The objective is not simply to prove that a control exists, but to demonstrate that it is operating correctly and delivering the intended outcome.
Organizations increasingly need both security assurance and compliance assurance.
Effective Continuous Assurance programs validate controls across four dimensions.
Area
What one must answer
Examples
Coverage
Are required controls deployed across all applicable assets?
Endpoints protected by EDR
Systems covered by vulnerability scanning
Configuration
Are controls configured according to organizational policies and security standards?
Disk encryption policies
Endpoint security baselines
Operational Health
Are controls healthy, functioning correctly, and actively managed?
Endpoint agents reporting to management consoles
Security alerts investigated within SLA
Endpoint agents reporting to management consoles
Effectiveness
Are controls reducing exposure and improving security outcomes?
Reduction in high-risk vulnerabilities
Improved phishing resilience
These dimensions can be mapped to security and compliance controls, helping organizations demonstrate both control effectiveness and framework adherence.
What Are the Benefits of Continuous Assurance?
Organizations that adopt Continuous Assurance gain several advantages.
Better Risk Visibility
Know whether controls are deployed, healthy, and functioning as intended.
Risk-Based Prioritization
Focus remediation efforts on the issues that present the greatest business risk.
Compliance Readiness
Generate continuous evidence for audits and regulatory requirements.
Security Improvement
Measure risk reduction, control effectiveness and security maturity over time.
Security Is What You Can Prove
The next generation of security programs will not be defined by the number of tools they deploy. They will be defined by their ability to continuously validate control effectiveness, prioritize risk, demonstrate improvement, and provide evidence-based assurance.
Visibility remains important. Compliance remains necessary. But neither is sufficient on its own.
Continuous Assurance bridges the gap between security operations, compliance readiness, risk management, and executive confidence.
Because security is not what you deploy. Security is what you can continuously prove.
See Continuous Assurance in Action
Understand how modern organizations continuously validate controls, measure risk reduction, and maintain audit-ready evidence across security, compliance, and IT operations.
Founder & CEO at SPOG.AI | Cyber Risk Intelligence | Continuous Security Assurance | AI & Cybersecurity Leadership
Sumit Malhotra is the founder of SPOG.AI, a cybersecurity mesh platform purpose-built to unify risk visibility, automate compliance, and drive continuous security maturity across complex enterprise environments. With over 24 years of experience across cybersecurity, GRC, IT operations, and infrastructure strategy, Sumit has partnered with organizations to solve some of the most persistent challenges in security operations: fragmented tooling, audit fatigue, delayed risk decisions, and lack of ownership alignment.