Featured
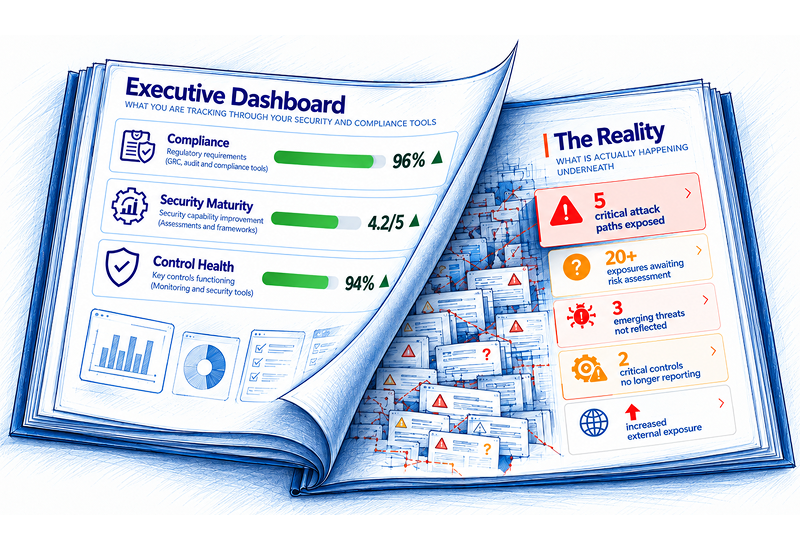
Why Green Security Dashboards Don’t Mean Lower Risk

Learn how compliance, security maturity, and continuously assessed business risk must work together to drive better security decisions. Compliance, security maturity, and risk assessment are three essential pillars of enterprise cybersecurity. Compliance measures adherence to defined requirements. Security maturity assesses organizational capabilities and opportunities for improvement. Risk assessment evaluates business exposure and the potential consequences of threats, considering existing safeguards. Yet an enterprise can achieve 96%...
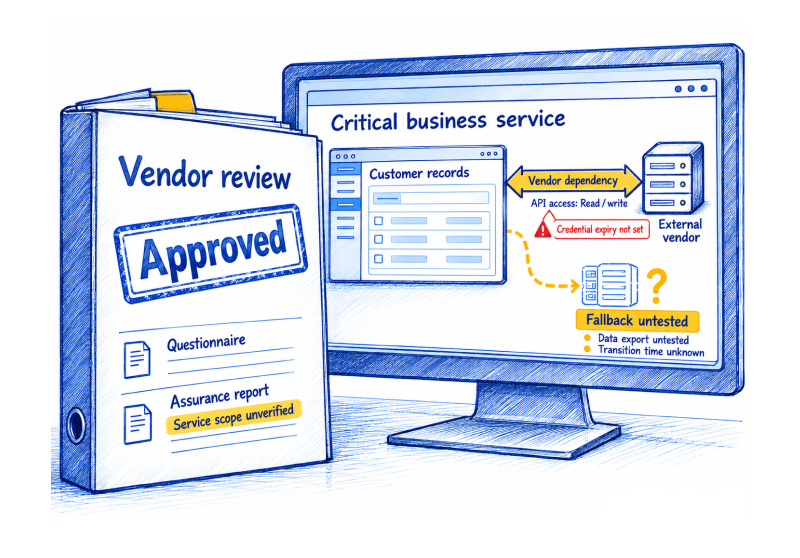
Vendor Risk Management Best Practices for Business Impact, Access and Resilience

A vendor review should tell decision-makers what access and dependency they are accepting, what conditions must hold, and what would trigger a change in that decision. This guide turns vendor...
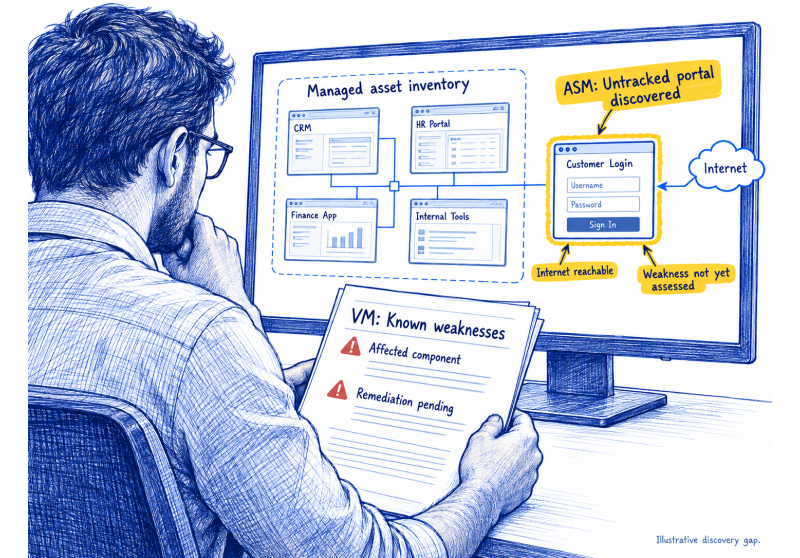
Vulnerability Management and Attack Surface Management: Two Views, One Program

Vulnerability management confirms and treats known weaknesses; attack surface management shows where reachable assets and paths exist. Connect them to make exposure priorities actionable and verify that treatment worked. The...
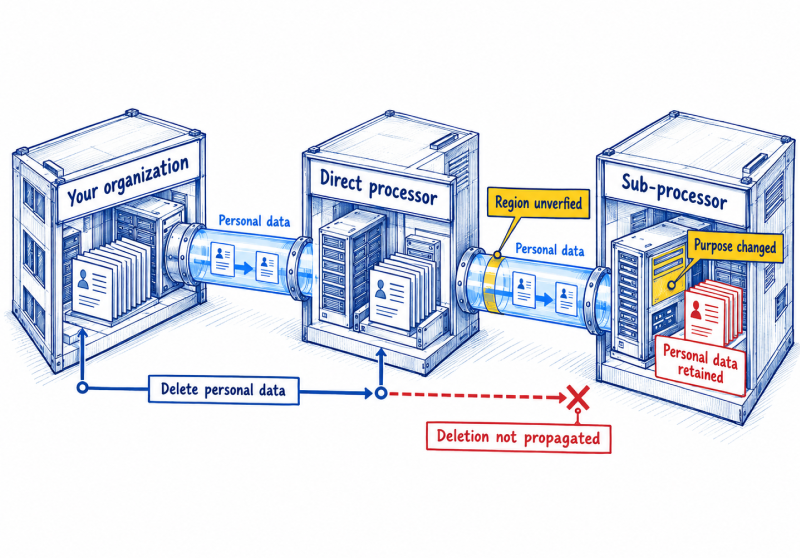
Sub-Processor Risk Management: Keep Privacy Controls Across Data Chains
A direct vendor is only the first link in a personal-data chain. Build a program that keeps purpose, location, authorization, safeguards, and evidence connected as downstream processors change. Sub-processor risk...
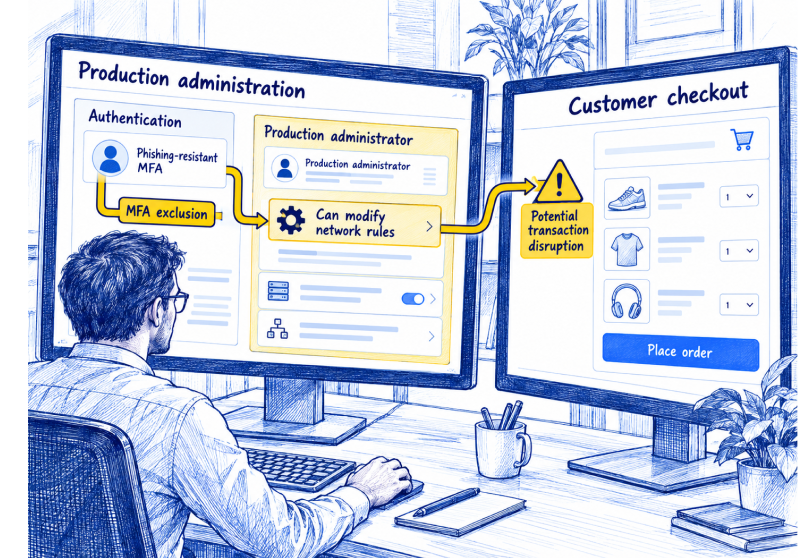
Cybersecurity Control Impact Analysis: Find Control Failures Before They Spread
Understand what a weakened control exposes, which operations depend on it and how to verify that corrective action has restored protection. Cybersecurity control impact analysis traces a failed or weakened...
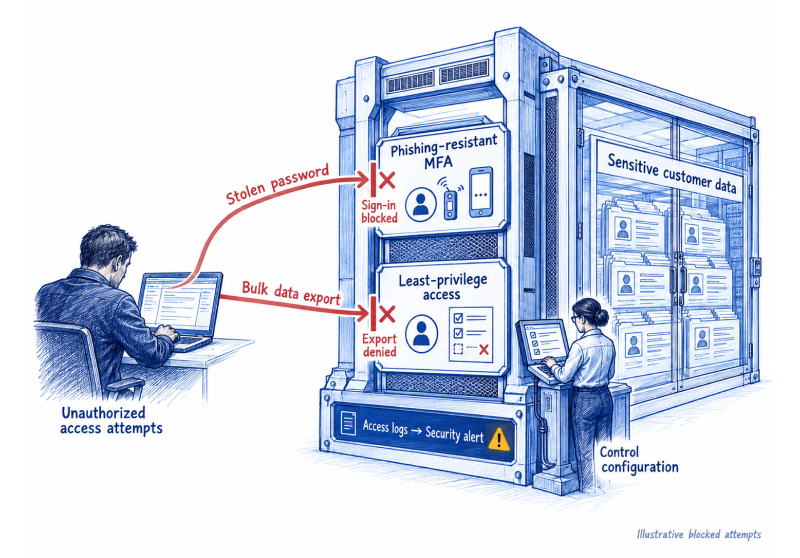
Data Breach Prevention: Build Controls That Protect Data Before Attackers Arrive
A practical guide to reducing the paths attackers can use to reach sensitive information. Build prevention around data, identity, and access decisions your teams can verify, not a checklist that...
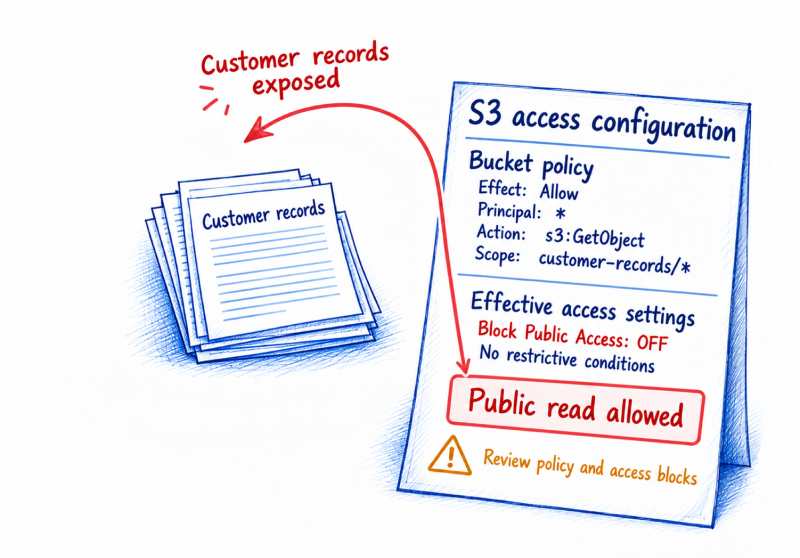
AWS Security Best Practices: Secure Multi-Account AWS Workloads With Guardrails
A practical guide to account boundaries, identity, guardrails, and operations in AWS.Build a secure foundation that lets workload teams move without relying on every account owner to remember every control....
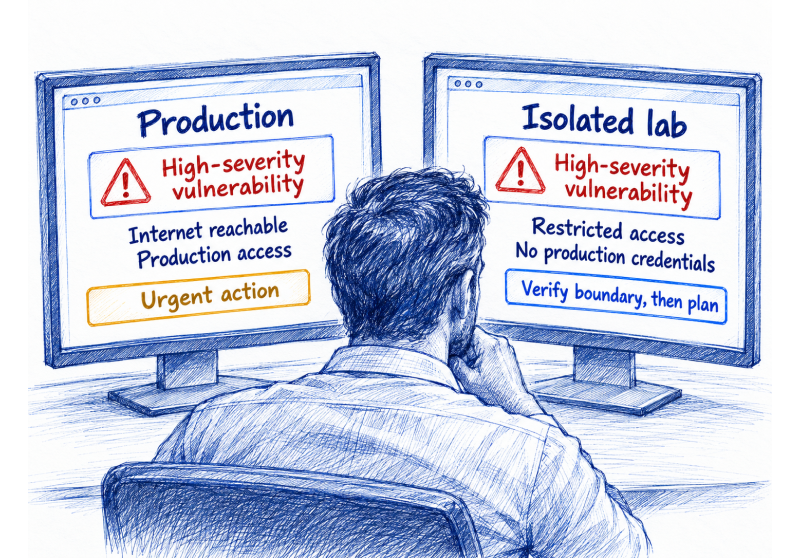
Risk-Based Vulnerability Management: Prioritize Exposure Beyond Scores
A practical guide for security and IT leaders deciding what to fix first.Use exploit evidence, real exposure, and business impact to create a defensible remediation queue. Risk-based vulnerability management is...
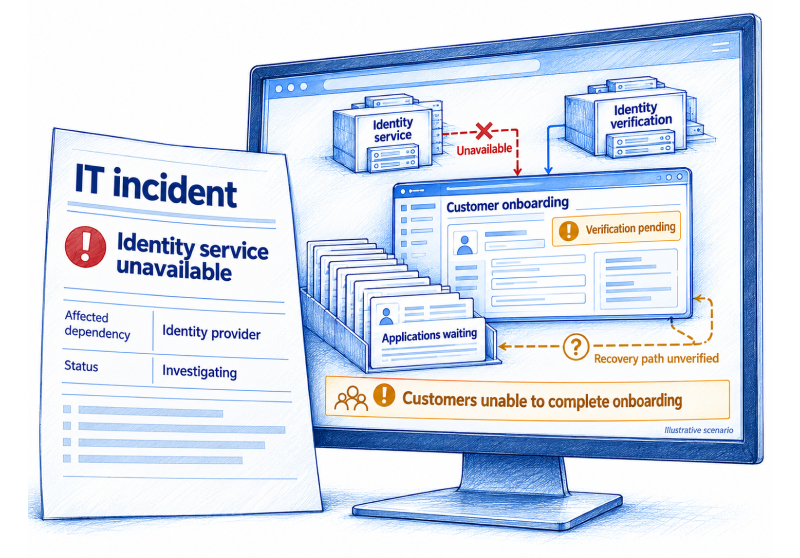
IT Risk Management in 2026: Connect Dependencies to Business Impact
Executives need to understand material changes, business exposure, decisions required and limits to confidence. Control owners need the affected populations, supporting evidence, unresolved gaps and deadlines. External readers need information...
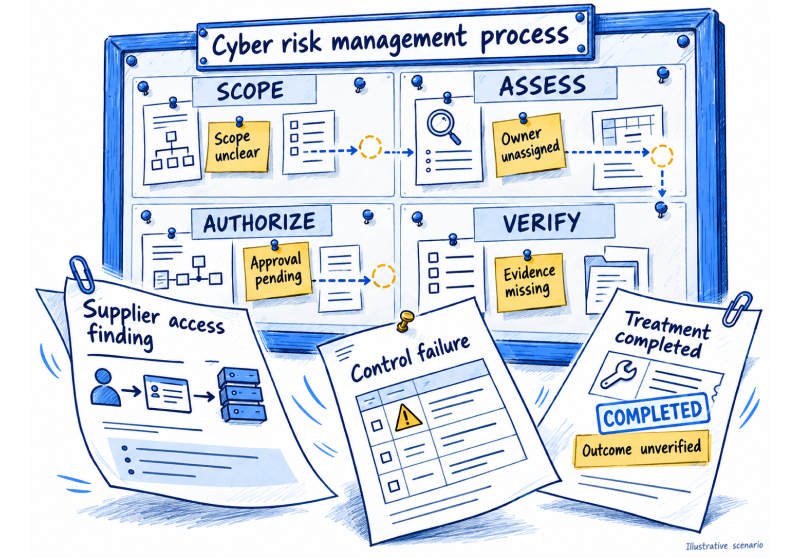
Cybersecurity Risk Management Process: A Practical Guide to Decisions
A cybersecurity risk management process should move from a defined business question to a decision, funded action, and evidence that the response worked.This guide gives security and GRC leaders a...
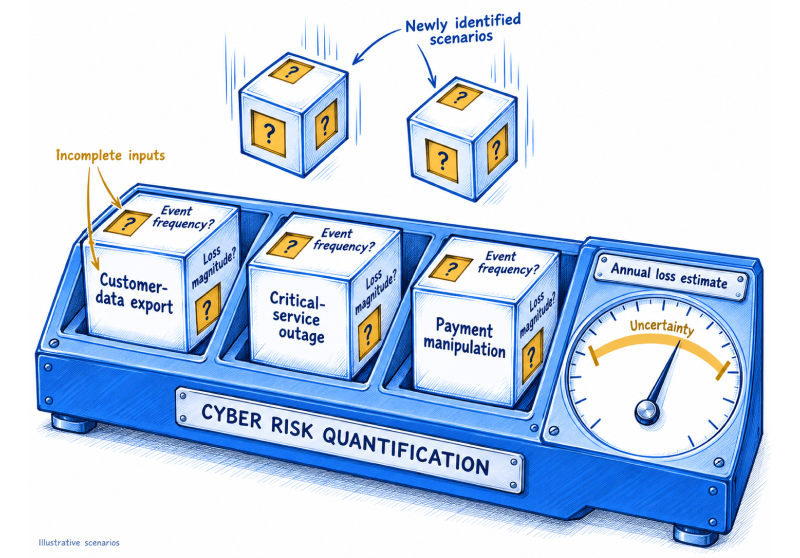
Quantitative Cyber Risk Analysis: Put Loss Ranges to Work in Security Decisions
Quantitative cyber risk analysis can help leaders compare security choices, but a precise-looking number is only as sound as its scenario and inputs. This guide shows how to model loss...
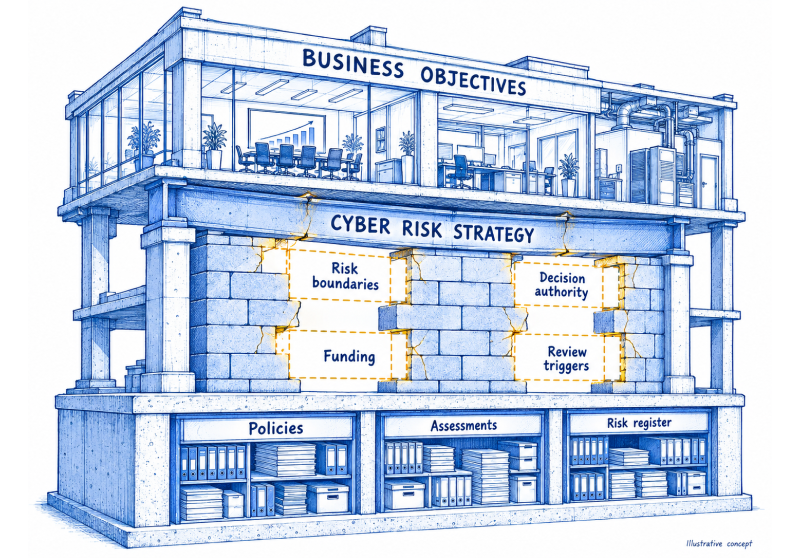
Cybersecurity Risk Management Strategy: Define Priorities, Authority and Limits
A cybersecurity risk management strategy should guide real choices about priorities, investment and acceptable exposure. This practical framework connects business objectives to decision authority, treatment and review. A cybersecurity risk...
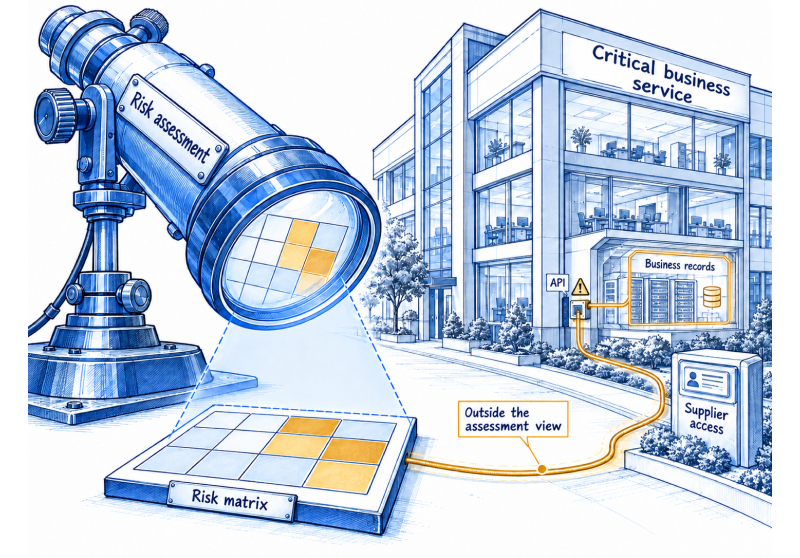
Cybersecurity Risk Management Techniques: Choose the Right Method
Different risk questions need different methods. Compare practical techniques, see how two methods reach different decisions on the same supplier scenario, and choose an approach that fits the evidence and...