Featured
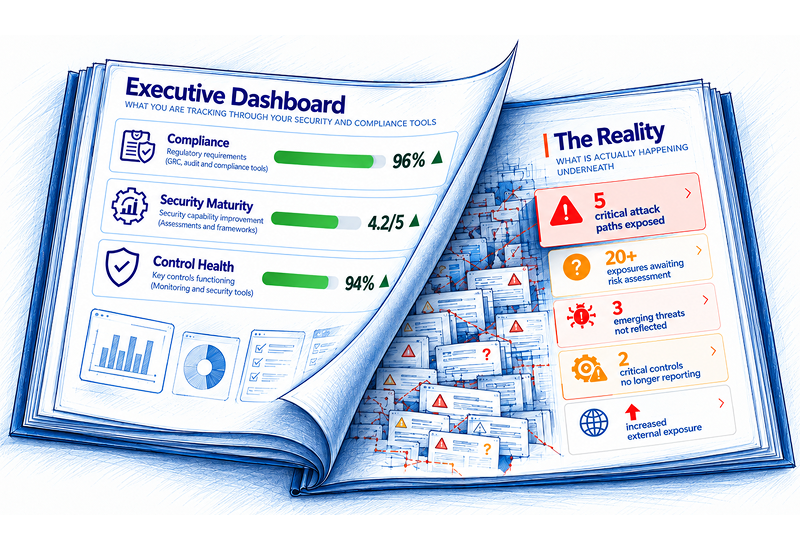
Why Green Security Dashboards Don’t Mean Lower Risk

Learn how compliance, security maturity, and continuously assessed business risk must work together to drive better security decisions. Compliance, security maturity, and risk assessment are three essential pillars of enterprise cybersecurity. Compliance measures adherence to defined requirements. Security maturity assesses organizational capabilities and opportunities for improvement. Risk assessment evaluates business exposure and the potential consequences of threats, considering existing safeguards. Yet an enterprise can achieve 96%...

Top 10 Vulnerability Management Metrics you need to be tracking

Every CISO and cybersecurity leader faces the same challenge. You invest in advanced vulnerability management (VM) tools, run regular scans, and patch the critical vulnerabilities your system detects. On paper,...
SEBI CSCRF: The Ultimate Guide for SEBI-Regulated Entities
Cyber threats are rising, and SEBI’s Cybersecurity and Cyber Resilience Framework (CSCRF) sets strict mandates to protect financial entities. With a March 31, 2025 deadline, firms must act now to...
GRC Silos Cost More Than You Think – Here’s Why
Governance, Risk, and Compliance (GRC) functions often operate in silos, leading to inefficiencies, higher costs, and increased regulatory risks. Disjointed processes create blind spots, delay incident response, and make compliance...
AI Compliance Frameworks: Why They Matter and What You Need to Know
With AI transforming industries at an unprecedented pace, the risks of bias, privacy violations, and regulatory non-compliance are skyrocketing. Global regulations like the EU AI Act, NIST AI RMF, ISO/IEC...
ISO 27001:2022 Update – Are You Ready for the New Compliance Requirements?

The latest ISO 27001:2022 update brings critical changes to information security, risk management, and compliance requirements. With a stronger focus on cyber resilience, supply chain security, and evolving threats, organizations...