Featured
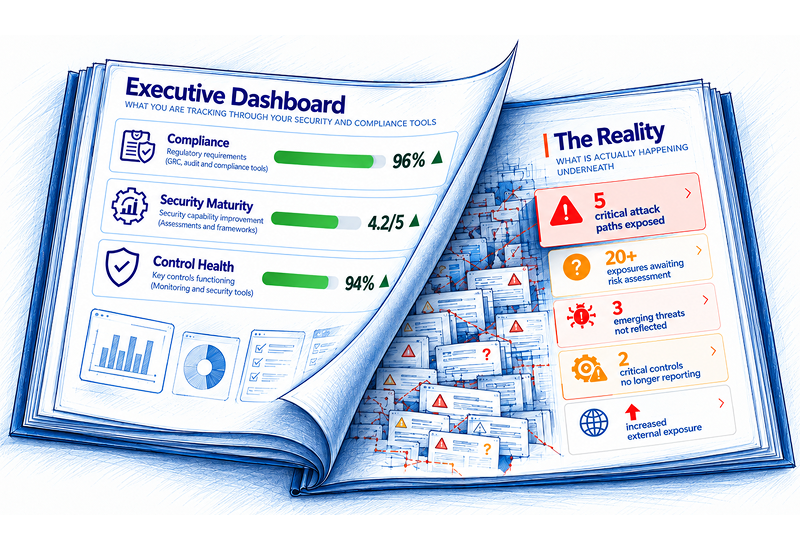
Why Green Security Dashboards Don’t Mean Lower Risk

Learn how compliance, security maturity, and continuously assessed business risk must work together to drive better security decisions. Compliance, security maturity, and risk assessment are three essential pillars of enterprise cybersecurity. Compliance measures adherence to defined requirements. Security maturity assesses organizational capabilities and opportunities for improvement. Risk assessment evaluates business exposure and the potential consequences of threats, considering existing safeguards. Yet an enterprise can achieve 96%...
Turning Risk Registers from Static Records into Living Intelligence

For years, the risk register has been a key tool in governance, risk, and compliance (GRC) programs. But in most organizations, it still sits in spreadsheets or static forms that...

Understanding the Different Types of Security Controls (and Why They Matter)
Security controls come in many forms and levels of complexity. Organizations implement them based on their own risks, needs, and processes. But is it enough to set them up once...
The Evolution of PCI DSS: From v3.2.1 to v4.0
The Payment Card Industry Data Security Standard (PCI DSS) has long served as the global benchmark for safeguarding cardholder data and reducing the risk of breaches. First introduced in 2004,...
Third-Party Risk Metrics: How to Track and Report
Third-party data breaches are more commonplace than ever. The majority of high-stakes data breaches in recent years have been caused by one missing link in the vendor management workflow. Take...

Setting Up a GDPR Compliance Monitoring and Audit Program: Steps and Checklist
Achieving GDPR compliance is only the beginning, maintaining it is the real challenge. The General Data Protection Regulation (GDPR) demands that organizations not only put privacy controls in place but...

How Cybersecurity Asset Management Improves Risk-Based Alerting and Threat Response
Too often, security tools treat all assets as equal. A critical alert on a decommissioned test server carries the same weight as one on a core financial system. A suspicious...

Automated Access Reviews: Strengthening Security, Simplifying Compliance
Access reviews play a key role in meeting security and regulatory standards. But many companies still handle them manually, creating risk and complexity. According to The State of Access Review...
CERT-In’s 2025 Cyber Audit Policy: What It Means for India’s Security Ecosystem
On July 25, 2025, the Indian Computer Emergency Response Team (CERT-In) launched a major update to its cybersecurity audit guidelines. These new rules aim to move India’s security posture from...
Silent Threats, Loud Consequences: Why Most Breaches Start with a Missed Signal
Introduction: The Breach That Wasn’t Loud — Until It Was The most dangerous breaches often don’t begin with a bang.They start with a blink—missed, ignored, or filed away for “later.”...

From CMDB to Risk Engine: Turning Asset Data into Security Decision
In May 2024, one of the most significant cloud breaches in recent memory made headlines: attackers infiltrated over 160 customer environments in the Snowflake ecosystem, affecting companies like AT&T and...

A Complete Guide to Third-Party Security Assessment
Third-party data breaches are on the rise. Attackers increasingly target vendors, contractors, and SaaS providers; not just because they’re easier to breach, but because they often have direct access to...

Is Your Security Stack Missing True Visibility?
You’ve invested in top-tier tools—firewalls, SIEMs, XDRs, MDRs, and real-time threat intel feeds. On paper, your security stack looks solid. You’ve done everything right. But tools only work if they...