Featured
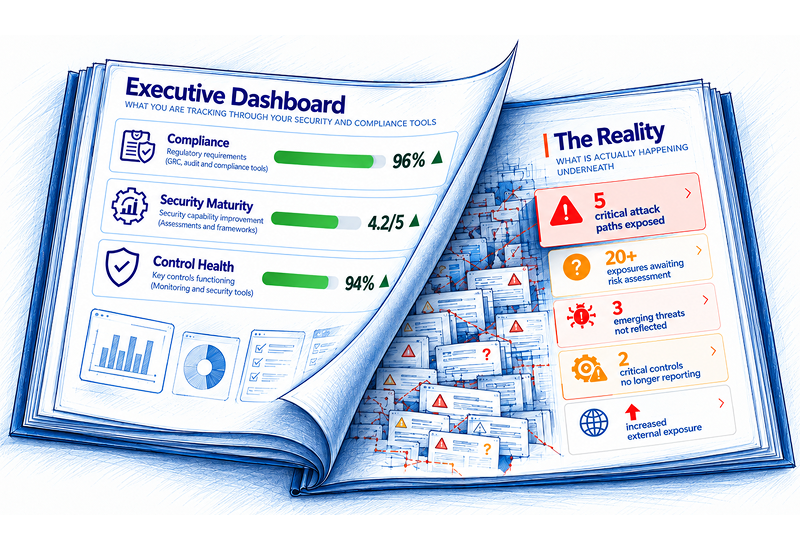
Why Green Security Dashboards Don’t Mean Lower Risk

Learn how compliance, security maturity, and continuously assessed business risk must work together to drive better security decisions. Compliance, security maturity, and risk assessment are three essential pillars of enterprise cybersecurity. Compliance measures adherence to defined requirements. Security maturity assesses organizational capabilities and opportunities for improvement. Risk assessment evaluates business exposure and the potential consequences of threats, considering existing safeguards. Yet an enterprise can achieve 96%...
How to Prepare for a SOC 2 Type II Audit in Half the Time

83% of enterprise buyers require SOC 2 compliance before vendor onboarding—making it not just a regulatory checkbox, but a mission-critical enabler of business growth and a gatekeeper for market access....
What to Include in a High-Impact Compliance Report (With Examples)
Think of a compliance report like a routine health check-up for your organization. It might not be the most exciting appointment on the calendar, but it’s essential. Just as a...
10 Common Gaps in Enterprise Risk Assessments—and How to Close Them
Many organizations treat risk assessments as annual checklists, missing the dynamic threats that truly matter. This guide dives into the top 10 gaps that weaken enterprise risk assessments—from inconsistent scoring...

GRC Platform Selection Guide: What to Look for Based on Your Maturity Level
The GRC (Governance, Risk, and Compliance) technology landscape is vast. It touches nearly every part of a company’s operations—from policy management and control alignment to risk tracking and data classification....
Cyber Security Regulatory Compliance in India: What You Need to Know
Introduction: When Compliance Blocks Market Entry Sometimes, a region’s regulatory compliance rules block businesses from entering a market. That’s exactly what happened with WhatsApp Pay in India. Despite having hundreds...
Cybersecurity Risk Assessment in Banking: A Strategic Guide with Risk Matrix Templates
Banks today operate in a high-stakes environment, managing sensitive financial data, digital customer interactions, and a growing portfolio of online services. These innovations, while necessary, have dramatically increased their exposure...
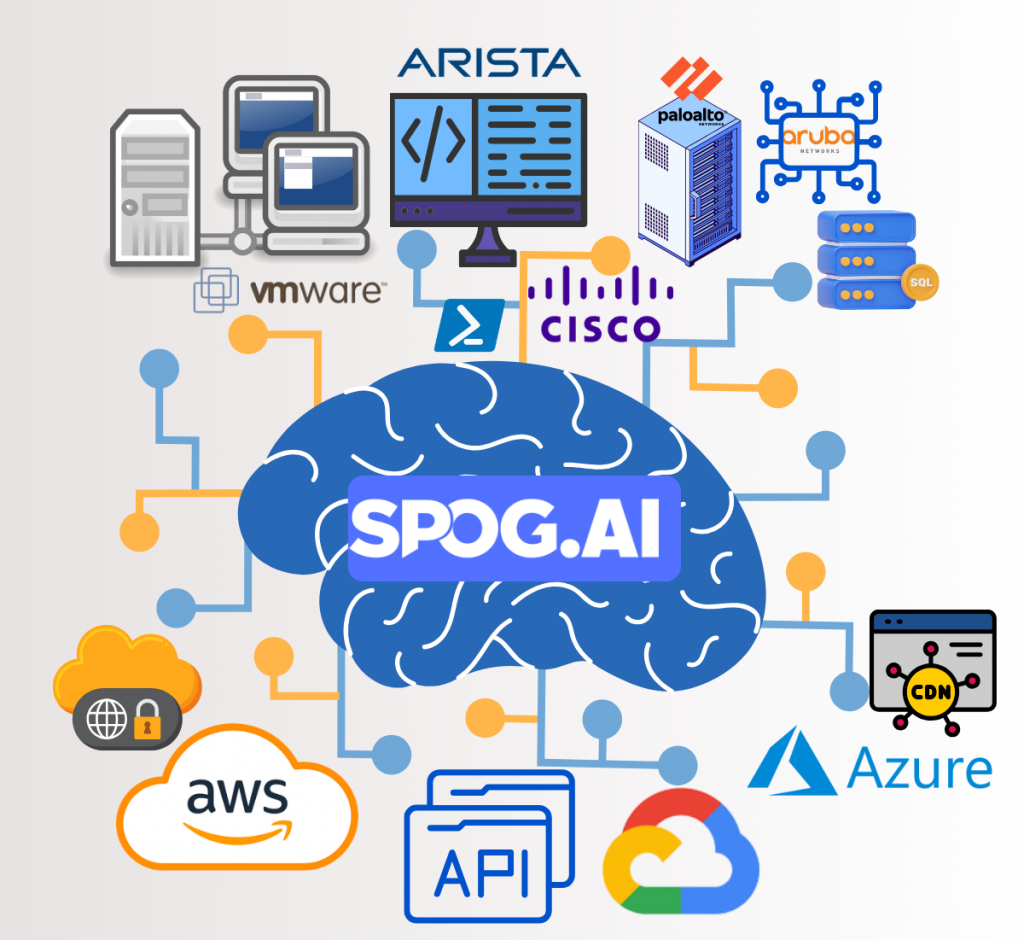
The Need for Hybrid GRC Integrations
“Just connect the API.” It’s something that we commonly hear in GRC automation—and one of the least useful if you're dealing with legacy systems. Many Governance, Risk, and Compliance (GRC)...

Risk Management vs Compliance Management: Which Should Be Your Priority?
Stuck Between Risk and Compliance? That’s the Real Risk. Discover why treating them as rivals is holding your organization back—and how smart teams use both to fuel resilience and agility....
How Compliance Fatigue Undermines Security
Compliance fatigue is real—and it’s putting your security at risk.When checklists replace critical thinking, organizations become vulnerable. Learn how to move beyond box-ticking and build a security culture that stays...

Moving Beyond Static Risk Management Frameworks to Continuous Control Monitoring
In the Banking, Financial Services, and Insurance (BFSI) sector, many organizations still rely on traditional risk management frameworks like the Three Lines of Defense (3LOD). These models worked well in...
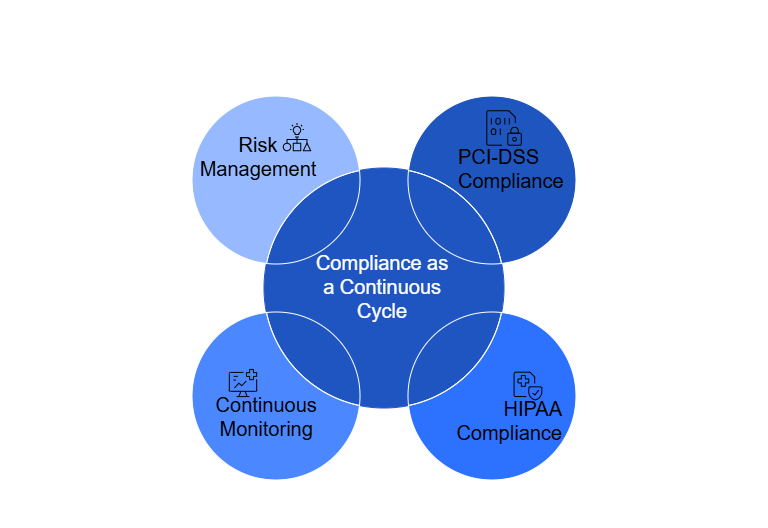
Compliance as a Continuous Cycle: Maintaining PCI-DSS, HIPAA, & More
Compliance isn't just about meeting regulatory requirements; it's about safeguarding your organization from risks that can cost millions. Yet, many companies still approach compliance as a one-time project, leaving them...
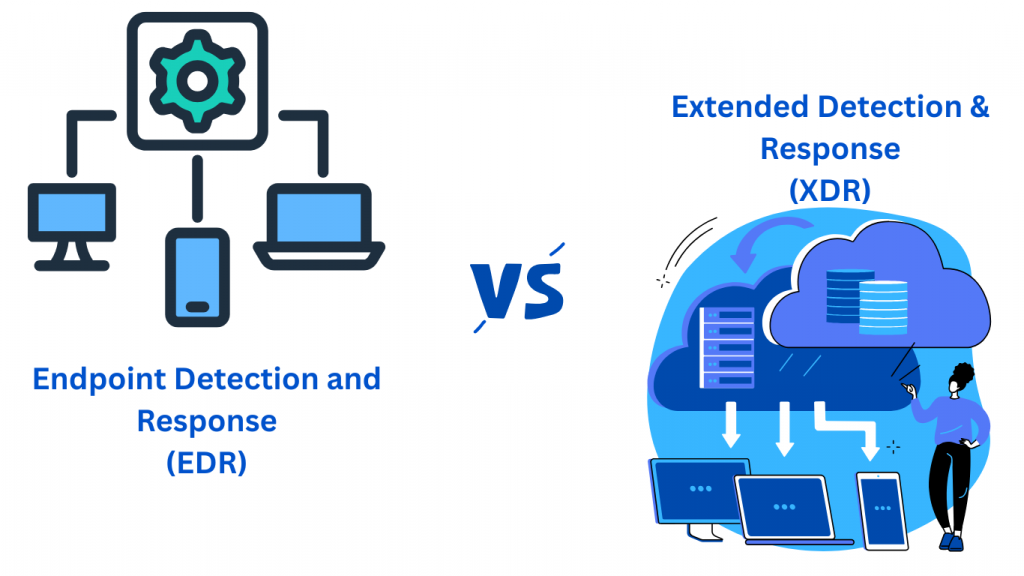
From EDR to XDR: Evaluating Tool Efficacy in Risk Assessments
Cyber threats are faster, stealthier, and more coordinated than ever — and your tools need to keep up. This article dives into the real difference between EDR and XDR, how...