Featured
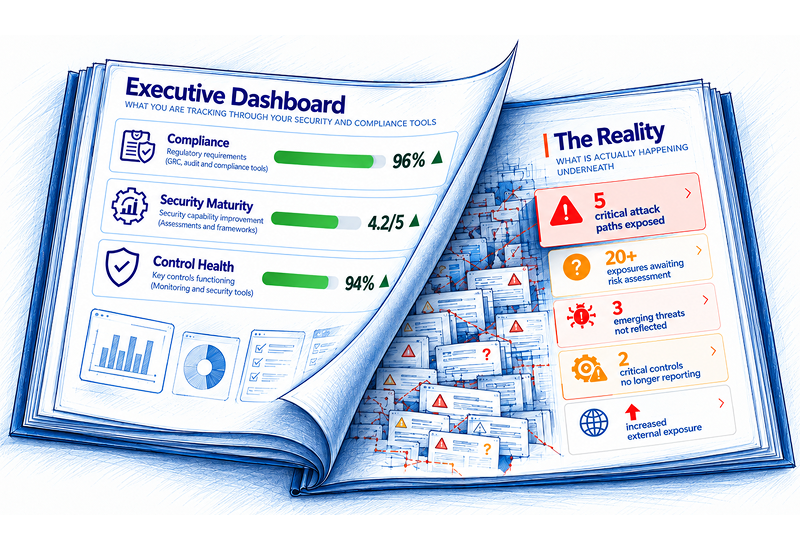
Why Green Security Dashboards Don’t Mean Lower Risk

Learn how compliance, security maturity, and continuously assessed business risk must work together to drive better security decisions. Compliance, security maturity, and risk assessment are three essential pillars of enterprise cybersecurity. Compliance measures adherence to defined requirements. Security maturity assesses organizational capabilities and opportunities for improvement. Risk assessment evaluates business exposure and the potential consequences of threats, considering existing safeguards. Yet an enterprise can achieve 96%...
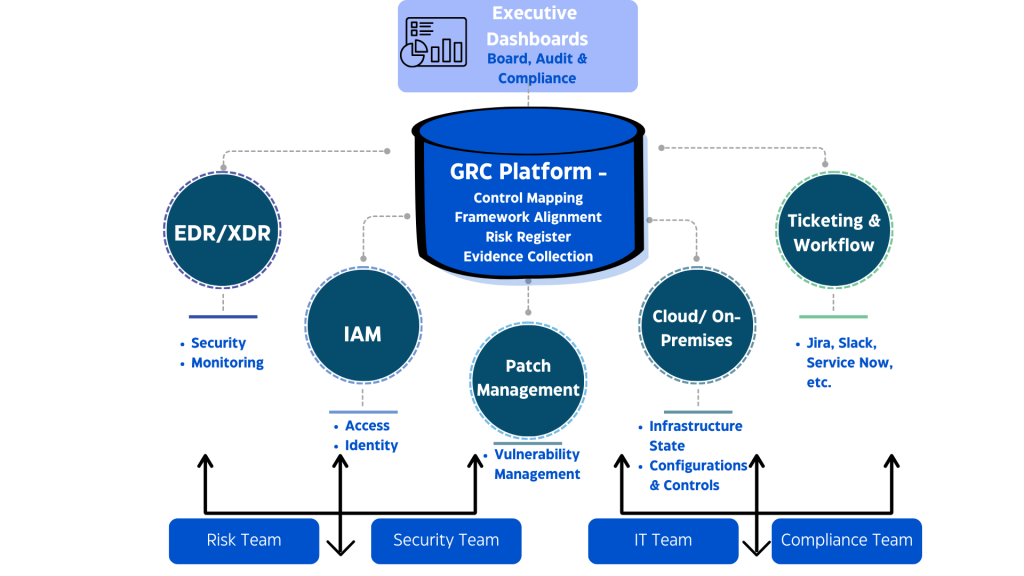
The Tech Stack for Ongoing Compliance: Integrations that Matter

Your team ships code every day. But your audit still runs once a year. In between, things break. Evidence gets lost. Risk data lives in ten different places. Most companies...
Building a Risk-Aware Culture: The Human Element in Security
Protection starts with people. And, if you have not recognized this yet, you are overlooking the human element in security. In fact, humans are the weakest link in security, not...
Navigating Multiple Frameworks: ISO 27001, SOC 2, GDPR, and Beyond
Imagine trying to find your way through a maze where many paths look the same, but each has different rules. Organizations face this challenge when complying with multiple security and...
Quantifying Cyber Threats: Advanced Techniques for Risk Identification
This article explores the best ways to identify and manage cyber risks. By using techniques like scenario modeling, machine learning analytics, and threat correlation, companies can turn cybersecurity into a...
The ROI of Real-Time Compliance: Cost Savings and Risk Reduction
Ignoring compliance is not just a legal risk. It is a financial mistake. But there is a better way. Let’s dive into it! Many companies see compliance as a burden....

Conducting a Holistic Risk Audit: Key Steps & Best Practices
Most organizations approach risk audits the way they approach an annual health check-up—routine, compliance-driven, and often surface-level. If nothing appears broken, it’s business as usual. But just as hidden health...

Continuous Compliance Demystified: From Checklists to Real-Time Insights
Did you know that nearly 67% of businesses reported an increase in data privacy violations in 2024 compared to the previous year?. That's a clear sign that traditional compliance methods...
Measuring Organizational Risk Maturity: An In-Depth Framework Overview
Cyber threats aren’t slowing down. Every day, security teams are fighting fires, trying to keep up with evolving risks, compliance demands, and resource constraints. But here’s the question: Do you...

Top 10 Vulnerability Management Metrics you need to be tracking
Every CISO and cybersecurity leader faces the same challenge. You invest in advanced vulnerability management (VM) tools, run regular scans, and patch the critical vulnerabilities your system detects. On paper,...
SEBI CSCRF: The Ultimate Guide for SEBI-Regulated Entities
Cyber threats are rising, and SEBI’s Cybersecurity and Cyber Resilience Framework (CSCRF) sets strict mandates to protect financial entities. With a March 31, 2025 deadline, firms must act now to...

GRC Silos Cost More Than You Think – Here’s Why
Governance, Risk, and Compliance (GRC) functions often operate in silos, leading to inefficiencies, higher costs, and increased regulatory risks. Disjointed processes create blind spots, delay incident response, and make compliance...
AI Compliance Frameworks: Why They Matter and What You Need to Know
With AI transforming industries at an unprecedented pace, the risks of bias, privacy violations, and regulatory non-compliance are skyrocketing. Global regulations like the EU AI Act, NIST AI RMF, ISO/IEC...