Featured
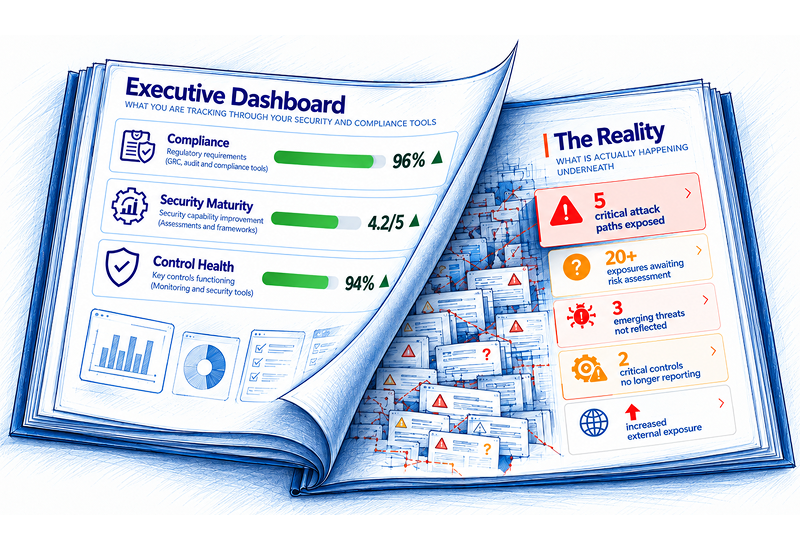
Why Green Security Dashboards Don’t Mean Lower Risk

Learn how compliance, security maturity, and continuously assessed business risk must work together to drive better security decisions. Compliance, security maturity, and risk assessment are three essential pillars of enterprise cybersecurity. Compliance measures adherence to defined requirements. Security maturity assesses organizational capabilities and opportunities for improvement. Risk assessment evaluates business exposure and the potential consequences of threats, considering existing safeguards. Yet an enterprise can achieve 96%...
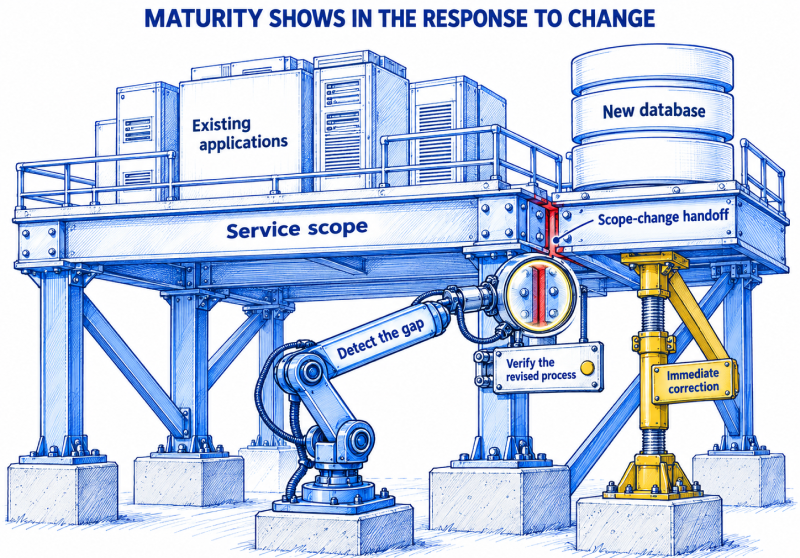
GRC Maturity That Holds Up Under Change: Align Evidence, Ownership and Decisions

GRC maturity reflects how reliably an organization governs risk, meets obligations and improves its practices. Assess capabilities across ownership, evidence, risk decisions and change management, then use the findings to...
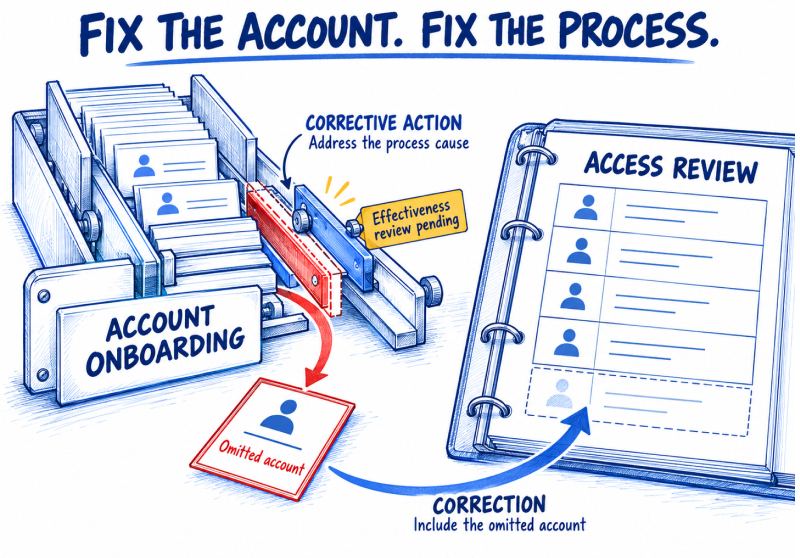
ISO 27001 Certification in 2026: Readiness, Audit Evidence and What Happens Next
Prepare for ISO 27001 certification with a clear scope, traceable evidence and accountable control owners. Understand the audit stages, timeline and cost factors, and what it takes to maintain your...
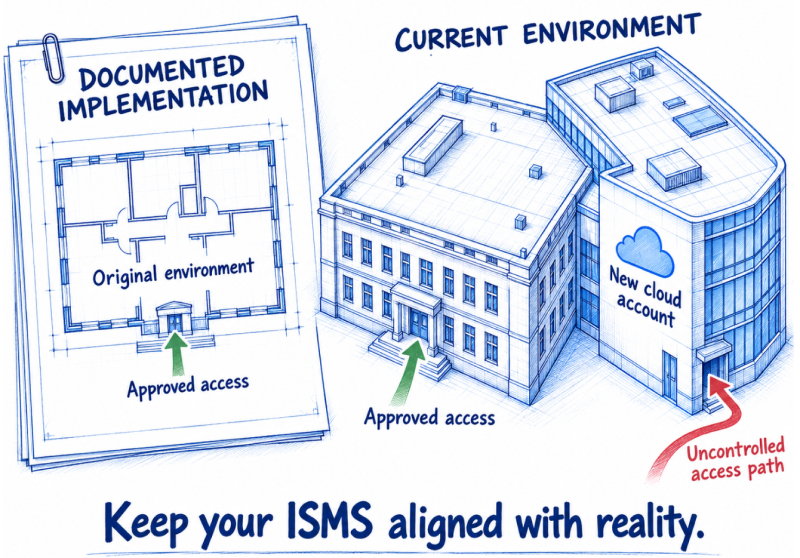
ISO 27001 in 2026: Keep Controls Aligned as Business Changes

An effective ISO 27001 program keeps control scope, the Statement of Applicability and supporting evidence aligned as services, identities and suppliers change. Clear ownership, checks on coverage and effectiveness, and...
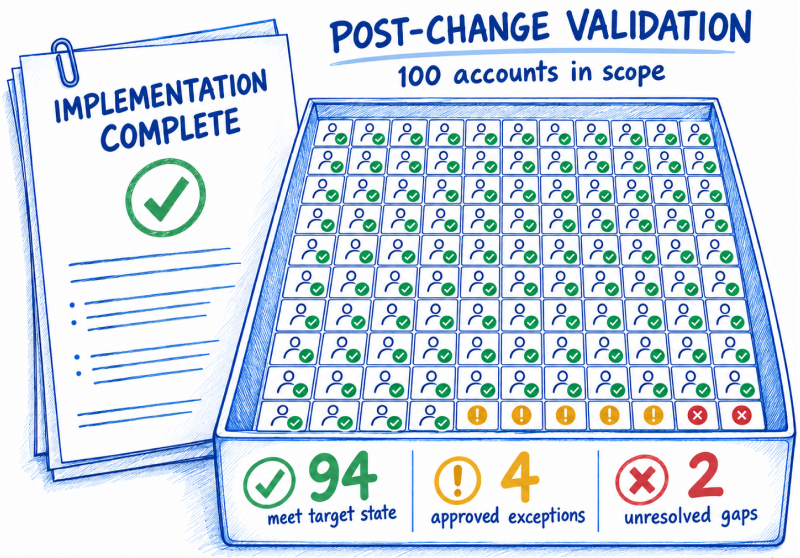
ISO 27001 Change Management: From Approval to Verified Outcome
An approved change can still leave a security control in the wrong state. Connect ISO 27001 change management with post-change validation to verify control outcomes, resolve gaps and retain evidence...
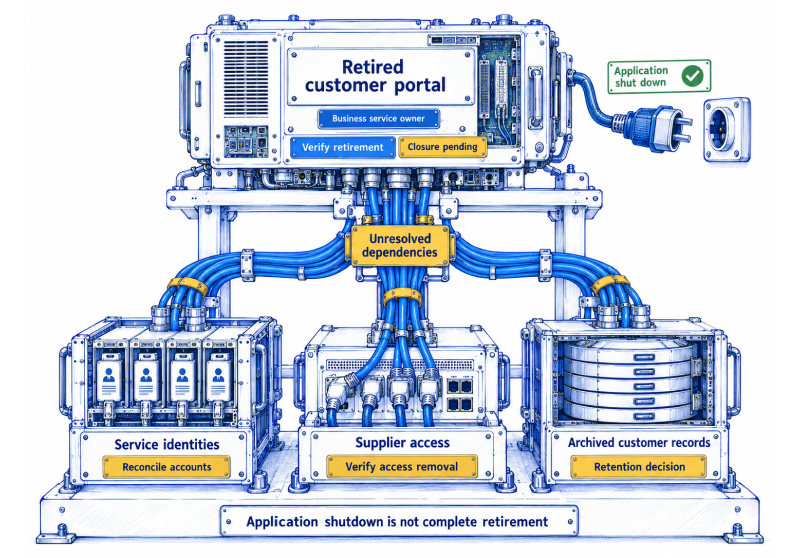
IT GRC: Keep Accountability Intact When Technology Changes
IT governance, risk management, and compliance (IT GRC) should help a CISO answer a difficult operational question: when technology changes, do the business's risk decisions and control assurances still hold?...
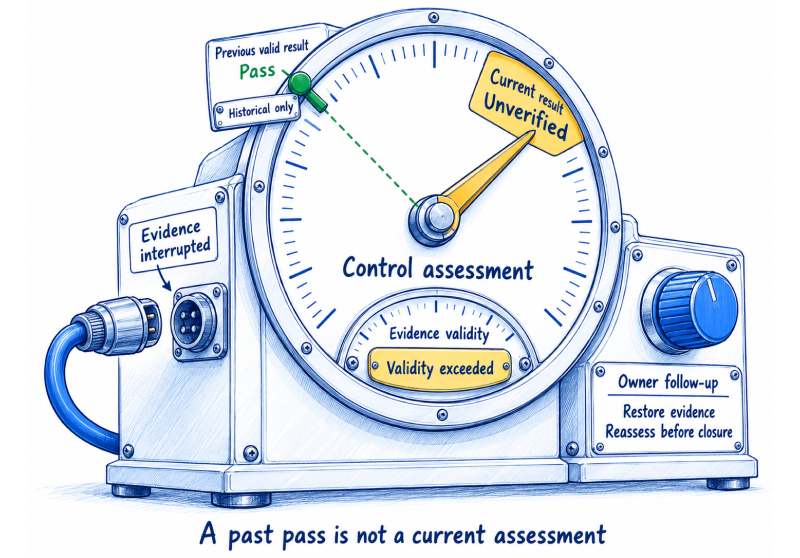
Compliance Monitoring in 2026: Detect Evidence Gaps and Verify Control Results
Compliance Monitoring in 2026: Detect Evidence Gaps and Verify Control Results A passing result is only useful when its coverage, evidence and test remain valid. Learn how to distinguish control...
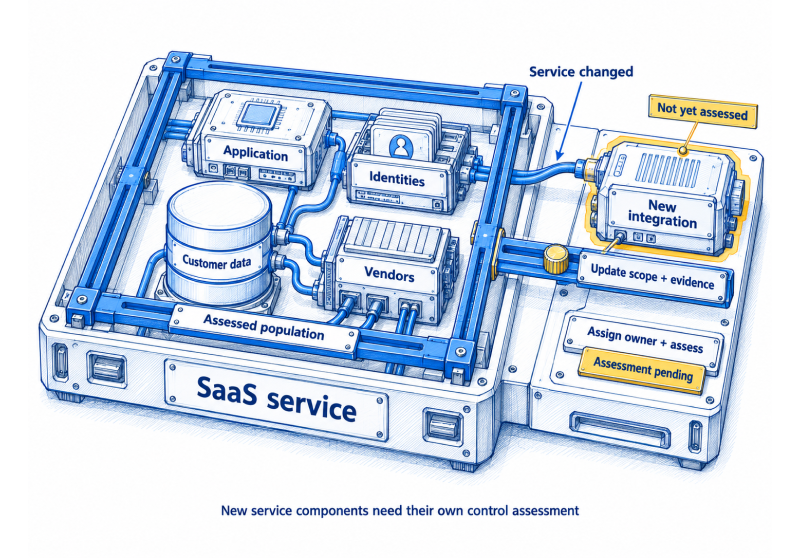
SaaS Compliance in 2026: A Checklist for Control Ownership and Clear Evidence
Build a SaaS compliance program around the services you deliver and the obligations that apply. Use this practical checklist to clarify cloud responsibilities, assign control owners and verify evidence as...
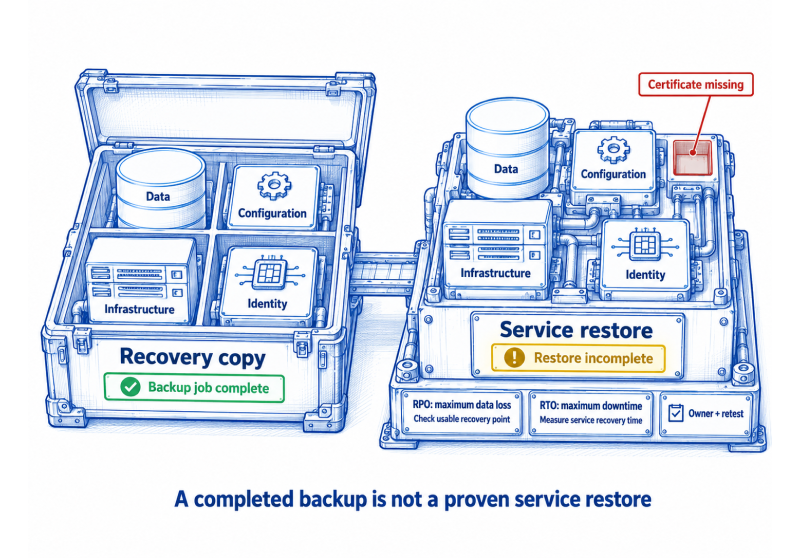
Backup Checklist in 2026: Verify Recovery for Security and Compliance Teams
A successful backup job does not prove that a service can be restored. Use this checklist to define recovery coverage, set RPO and RTO targets, protect recovery copies and verify...
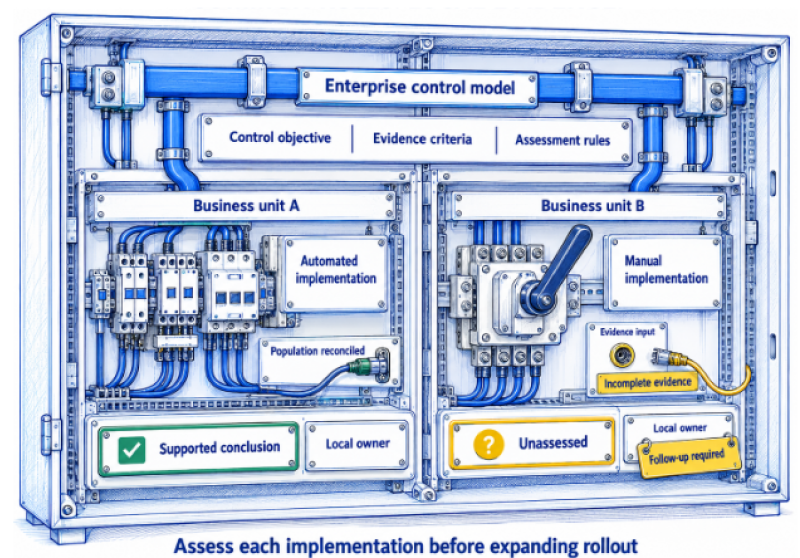
How to Roll Out Enterprise GRC: Prove the Model Before You Scale
Enterprise GRC needs consistent assessments across business units while preserving local responsibilities and obligations. Establish clear ownership, reliable evidence and a complete pilot control cycle before expanding, so each rollout...
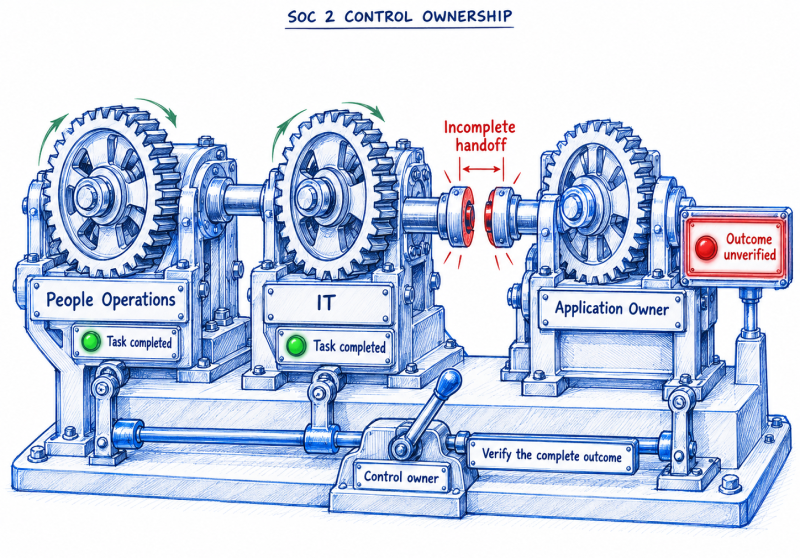
SOC 2 Control Ownership: Define Clear Roles and Validate Evidence Without a CISO
Build a practical SOC 2 control list with clear owners, reliable evidence and complete handoffs across teams. Learn how to manage responsibilities without a CISO, address missed controls and verify...
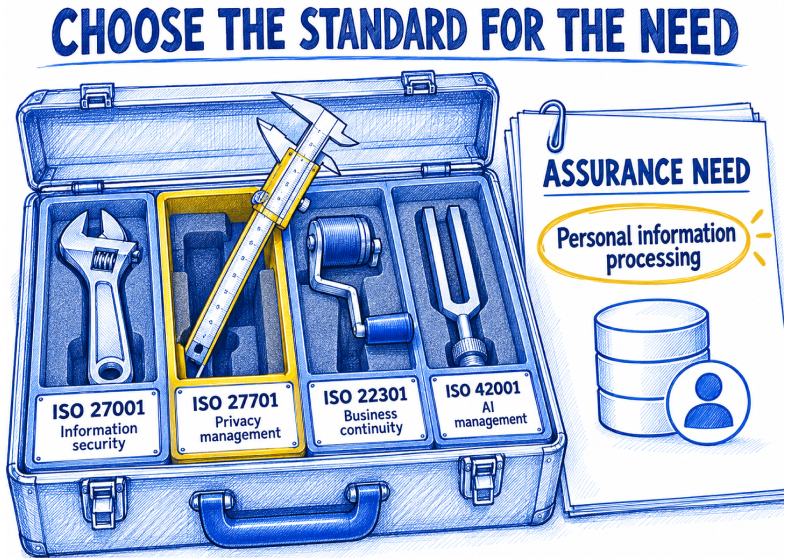
ISO Security Standards in 2026: Which Ones Matter for Your Organization?
Choose ISO security standards based on your business needs, responsibilities and the assurance stakeholders expect. Compare security, privacy, cloud, continuity and AI standards, and understand where certification, guidance and shared...
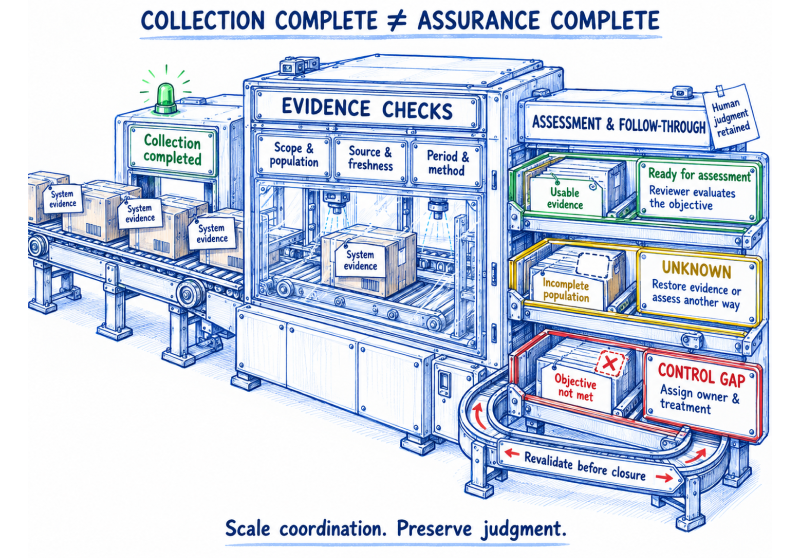
How Lean GRC Teams Can Scale Compliance Without Adding Headcount
Help lean GRC teams support growing compliance demands with clear ownership, reliable evidence and selective automation. Reduce repeated follow-up, keep exceptions visible and verify remediation while measuring whether the team...