Featured
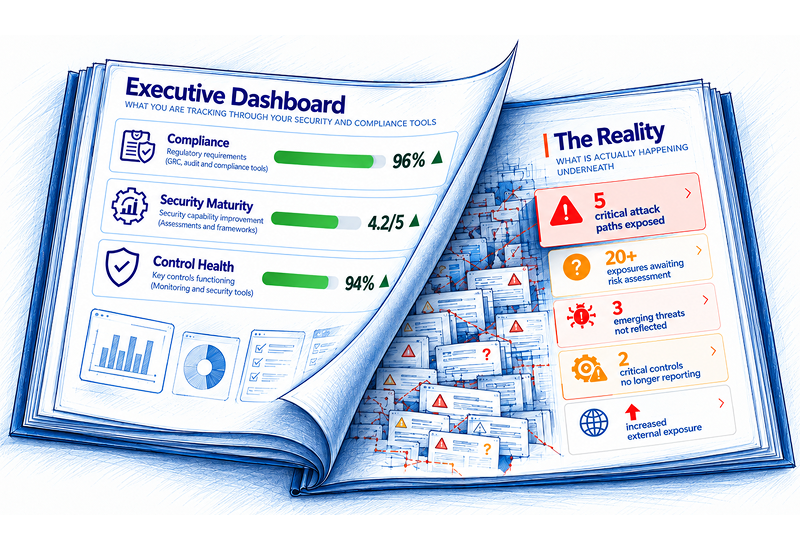
Why Green Security Dashboards Don’t Mean Lower Risk

Learn how compliance, security maturity, and continuously assessed business risk must work together to drive better security decisions. Compliance, security maturity, and risk assessment are three essential pillars of enterprise cybersecurity. Compliance measures adherence to defined requirements. Security maturity assesses organizational capabilities and opportunities for improvement. Risk assessment evaluates business exposure and the potential consequences of threats, considering existing safeguards. Yet an enterprise can achieve 96%...
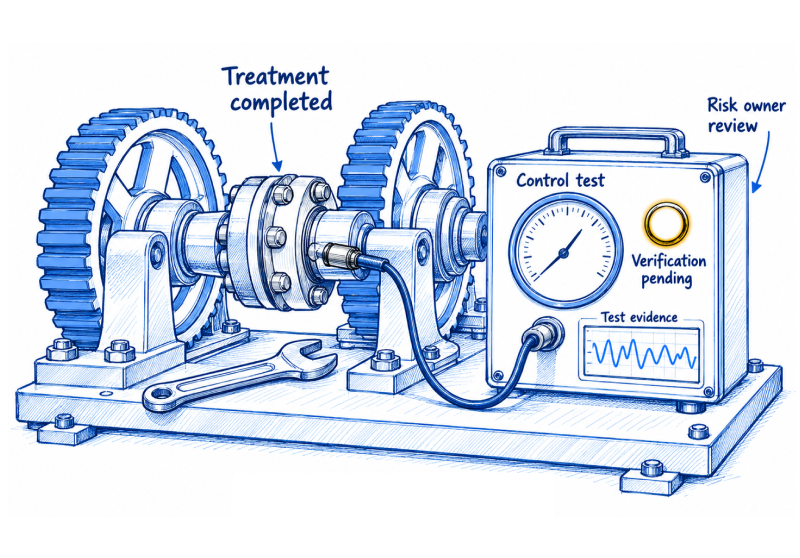
Operational Risk Management in 2026: Keep Decisions Current as Operations Change

Operational risk management helps leaders understand how everyday activity can disrupt critical services, and what to do before a weakness becomes a loss. A practical program connects risk scenarios to...
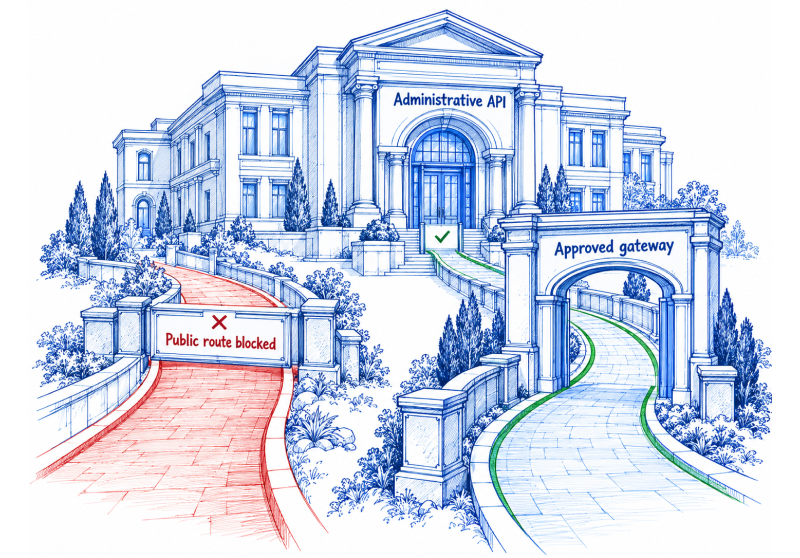
Attack Surface Management in 2026: Find Unknown Assets and Reduce Their Exposure

Attack surface management helps security teams discover assets and access paths their existing inventories miss. Learn how external and internal discovery, contextual prioritization and targeted remediation reduce exposure across changing...
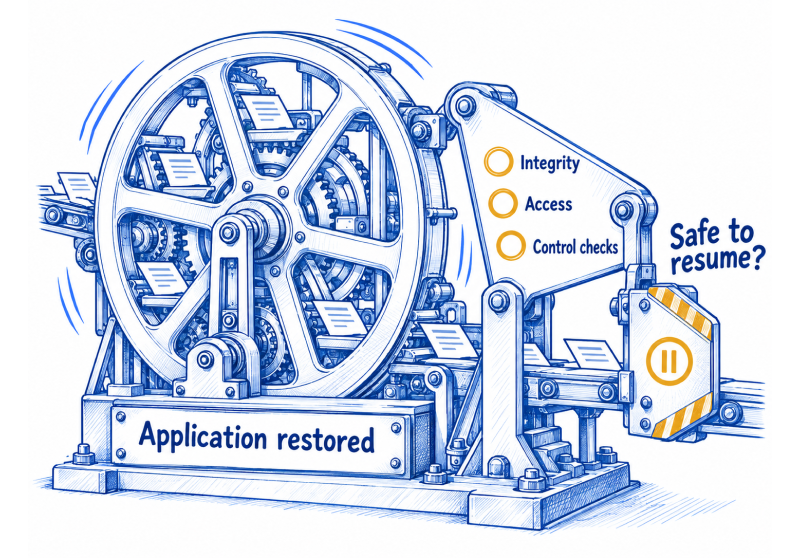
Business Impact Analysis in 2026: Connect Critical Services to Recovery Decisions
Business impact analysis helps organizations understand how disruption affects critical services and set recovery priorities. This article explains how to assess impacts over time, map dependencies, define realistic recovery targets...
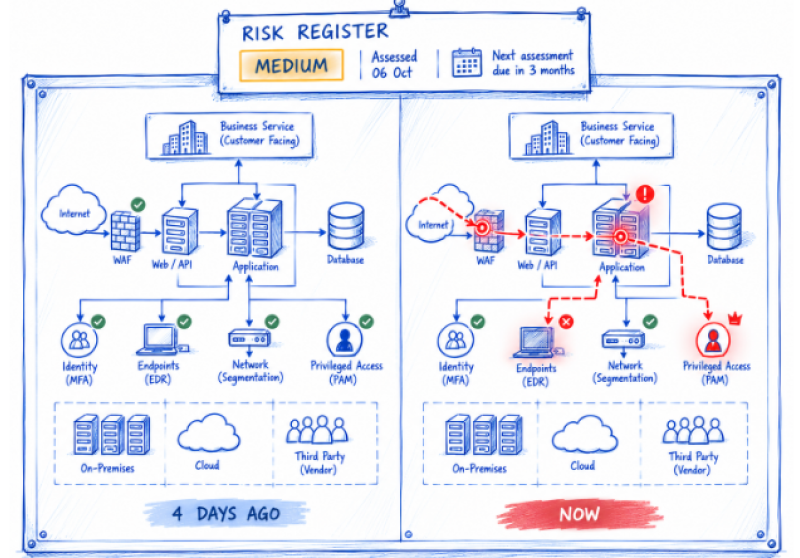
Dynamic Risk Assessment: Keep Cyber Risk Decisions Current as Conditions Change

Cyber risk changes when the conditions behind an assessment change. Dynamic Risk Assessment connects material changes in assets, threats and controls to existing risks, helping teams revisit treatment and acceptance...
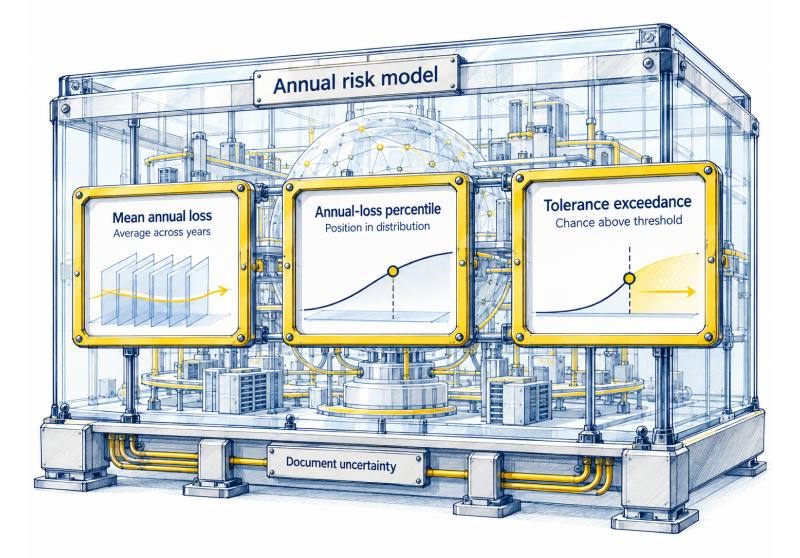
Quantitative Cyber Risk Assessment in 2026 for Better GRC Decisions
Quantitative cyber risk assessment helps teams decide which security treatments justify their cost. Defined scenarios, current evidence and explicit uncertainty make the estimates useful to security, finance and business owners....
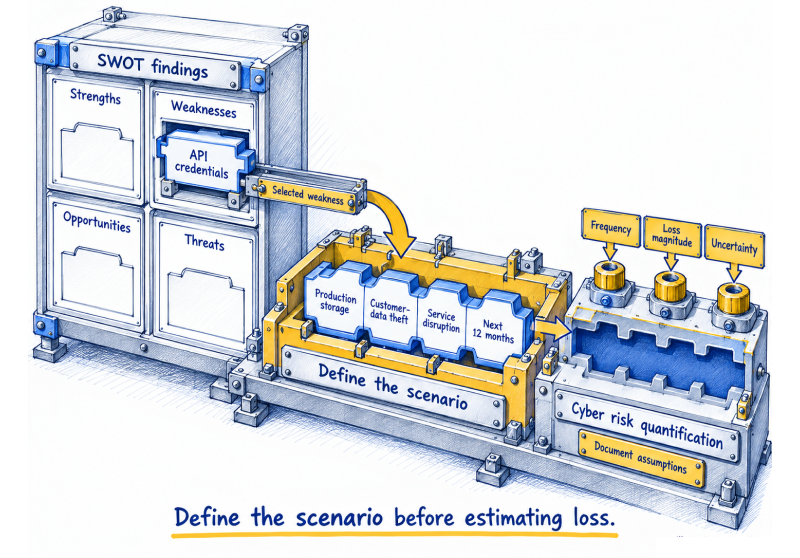
SWOT Analysis and Cyber Risk Quantification: A Practical GRC Strategy for 2026
SWOT analysis can help security leaders identify strategic concerns, while cyber risk quantification can test how those concerns may affect the business. This article explains how to connect the two...
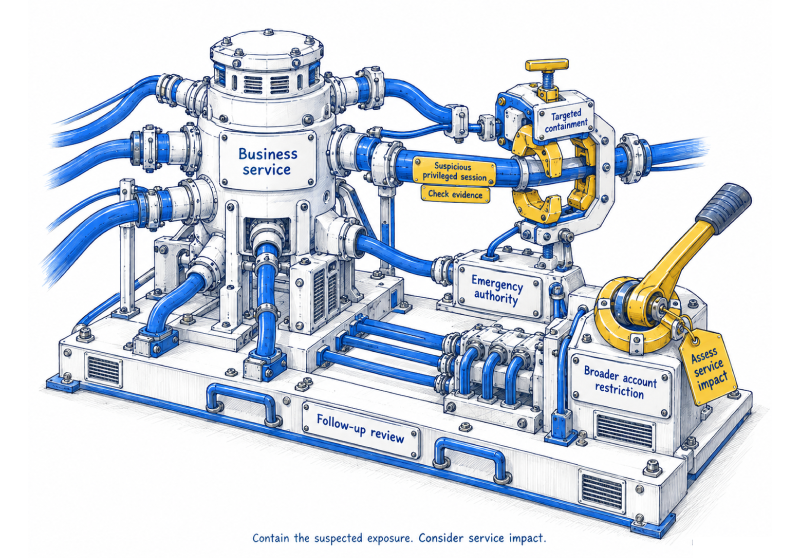
Human Factors in Incident Response in 2026: Make Safer Decisions Under Pressure
How security leaders can design roles, handoffs and decision safeguards that help people contain incidents without creating a second failure. Human factors in incident response are not a training topic...
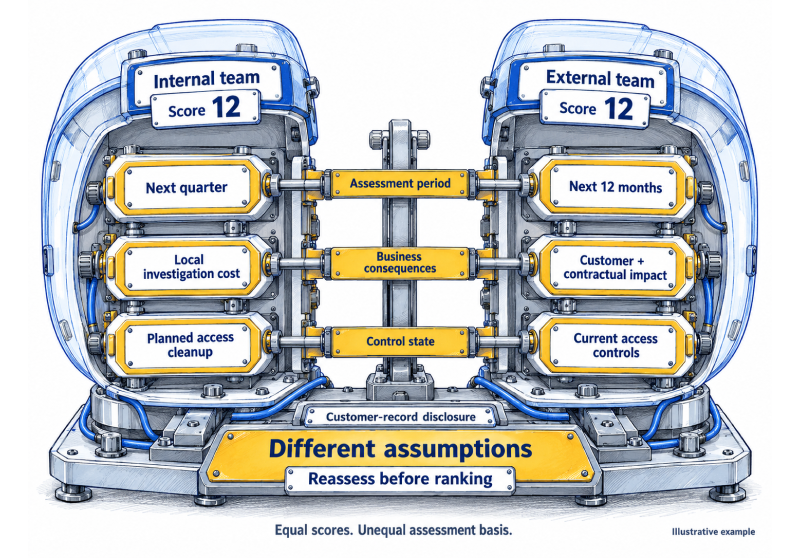
Risk Scoring in 2026: Make Internal and External Risks Comparable Across Teams
Learn how to calculate risk scores, reconcile conflicting ratings and compare internal failures with external threats without distorting management priorities. The method aligns scenarios, time horizons, impact criteria, control assumptions...
CERT-In’s 12-Hour Remediation Window: Why Faster Patching Is Not Enough

CERT-In’s 2026 vulnerability remediation guidance challenges how enterprises manage cyber exposure. Meeting shorter remediation windows requires continuous exposure intelligence, faster decisions, and verified risk reduction, not simply faster patch deployment....
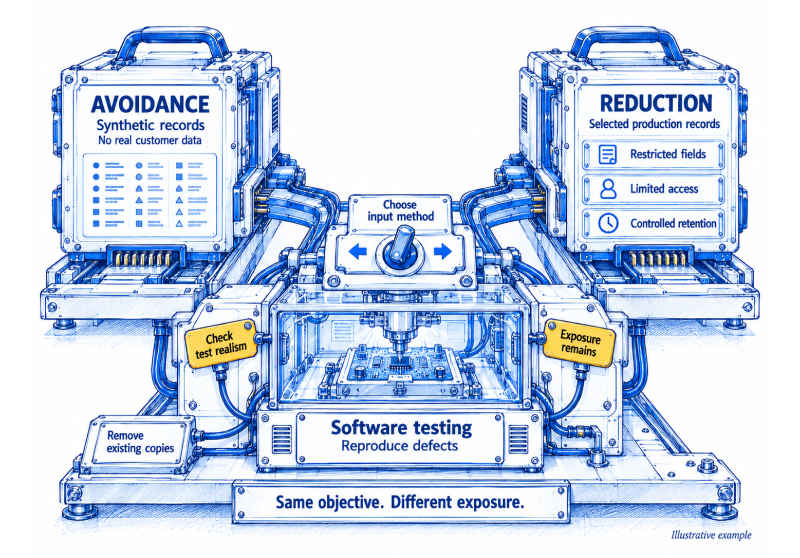
Risk Avoidance vs Risk Reduction in 2026: Choosing the Right Business Response
Measure whether decisions improve Track time from an escalation trigger to acknowledgment by an authorized responder. Measure incomplete handoffs as a proportion of all reviewed handoffs. Separately track containment actions...
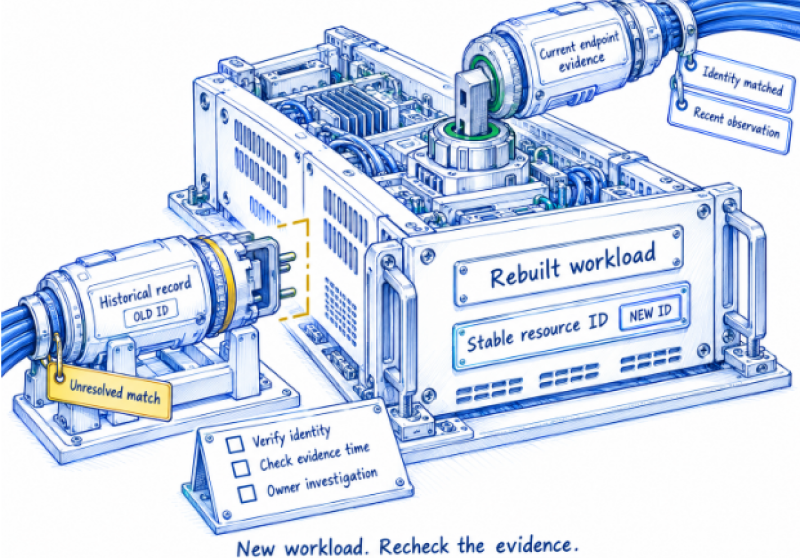
CAASM: Make Asset Visibility Useful for Security Decisions and Responses
Cyber Asset Attack Surface Management connects fragmented asset records so teams can investigate exposure and security coverage. Its value depends on explainable matching, current evidence and decisions that reach an...
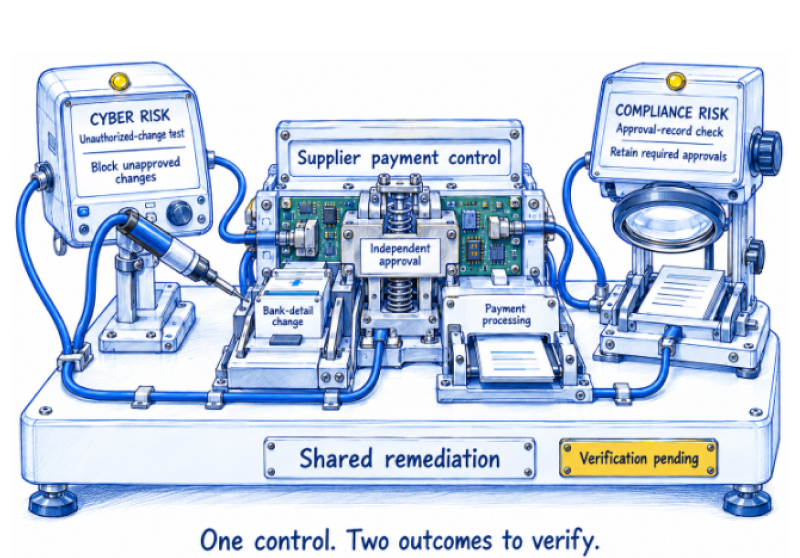
Cyber Risk and Compliance Risk: Decide What Needs Action
Cyber risk and compliance risk can share the same control weakness while requiring different decisions. Learn how mid-market teams can assess business harm and applicable obligations together, coordinate corrective action...