Featured
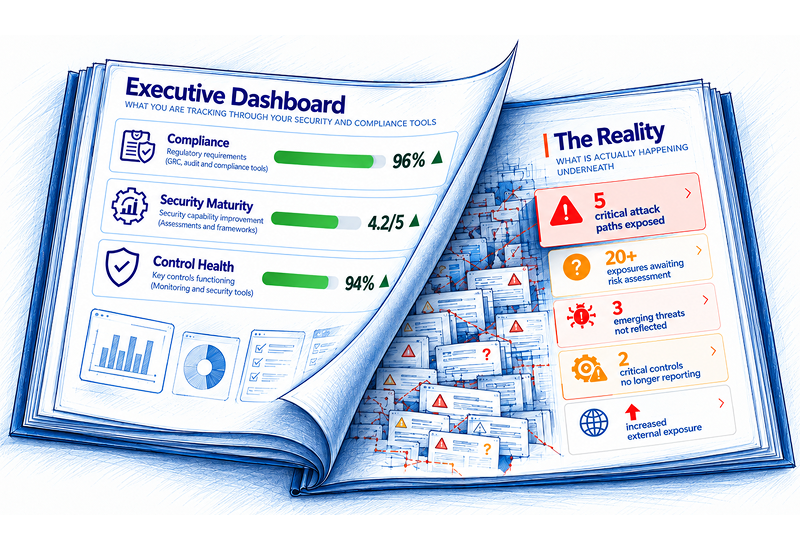
Why Green Security Dashboards Don’t Mean Lower Risk

Learn how compliance, security maturity, and continuously assessed business risk must work together to drive better security decisions. Compliance, security maturity, and risk assessment are three essential pillars of enterprise cybersecurity. Compliance measures adherence to defined requirements. Security maturity assesses organizational capabilities and opportunities for improvement. Risk assessment evaluates business exposure and the potential consequences of threats, considering existing safeguards. Yet an enterprise can achieve 96%...
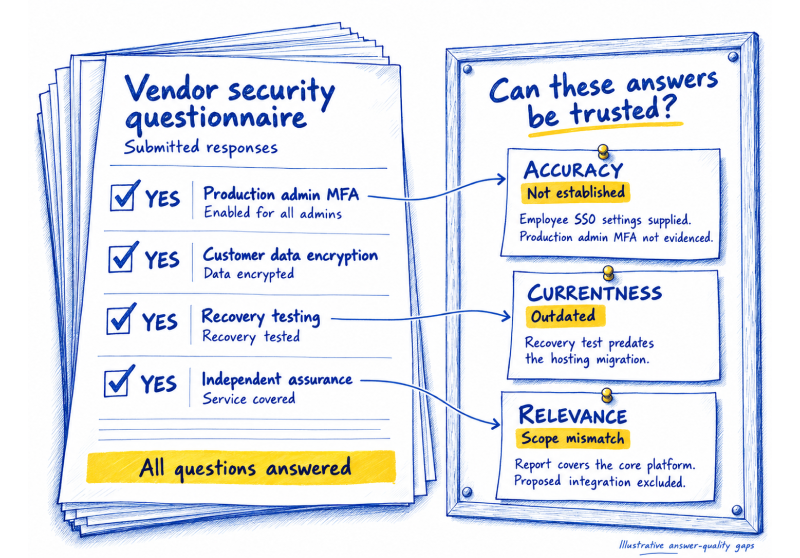
Security Questionnaires: Respond with Accurate, Verifiable Answers

Security questionnaires help buyers understand how a supplier protects the data, systems and services involved in a proposed relationship. Reliable responses define where controls apply, provide current supporting evidence and...
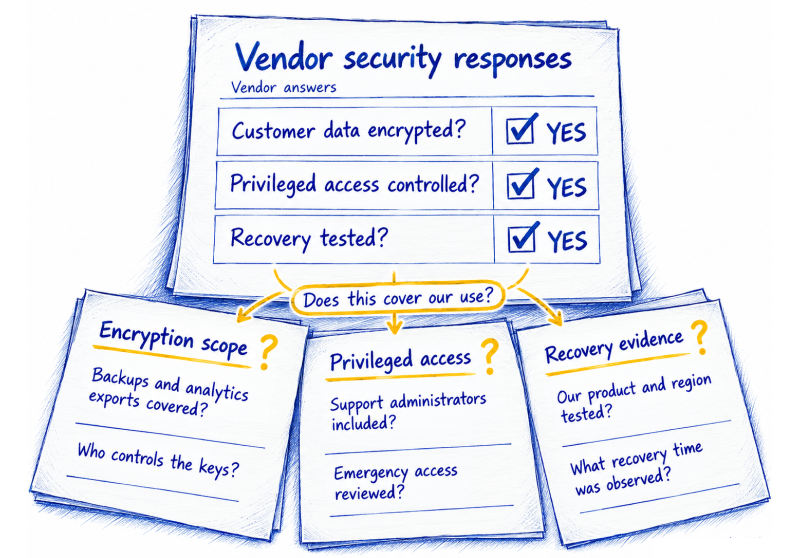
Vendor Cybersecurity Questions That Test Scope, Evidence and Exposure
A vendor cybersecurity inquiry should establish what the supplier will do, which data and systems it can access, and how the business depends on its services. Ask targeted questions, request...
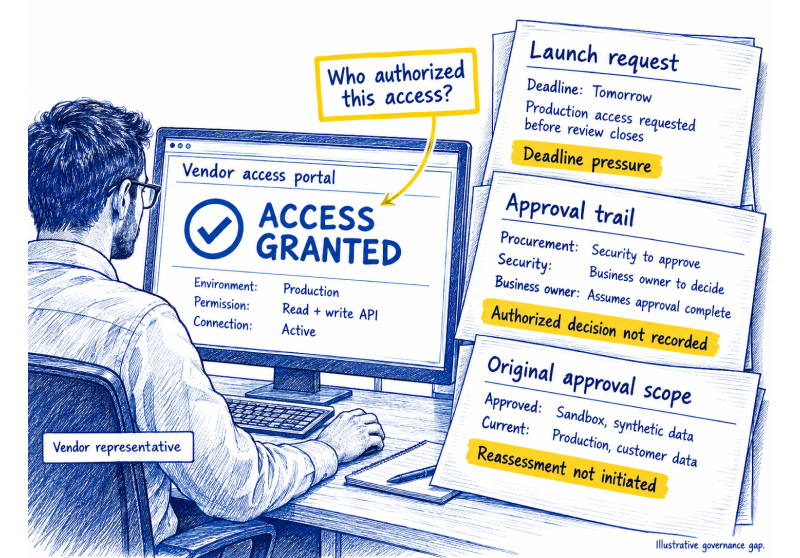
Why Your Vendor Management Policy Must Guide Decisions Through Change

A vendor management policy sets the rules for approving suppliers, accepting exceptions and responding when relationships change. This guide explains how to define decision authority, approval conditions, reassessment triggers and...
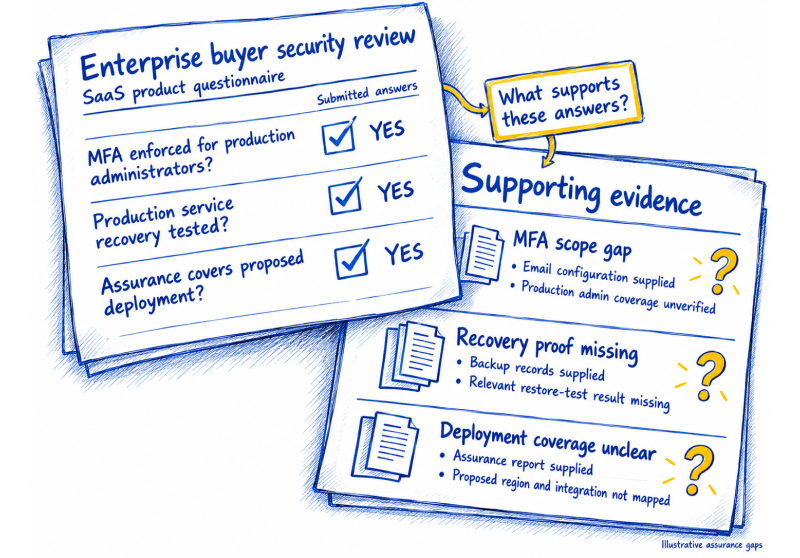
SaaS Startup Security Readiness: Prove What Enterprise Buyers Expect
Enterprise buyers expect SaaS startups to demonstrate how they protect customer data, identities, and business operations not just present policies or certifications. This article explores how startups can build security...
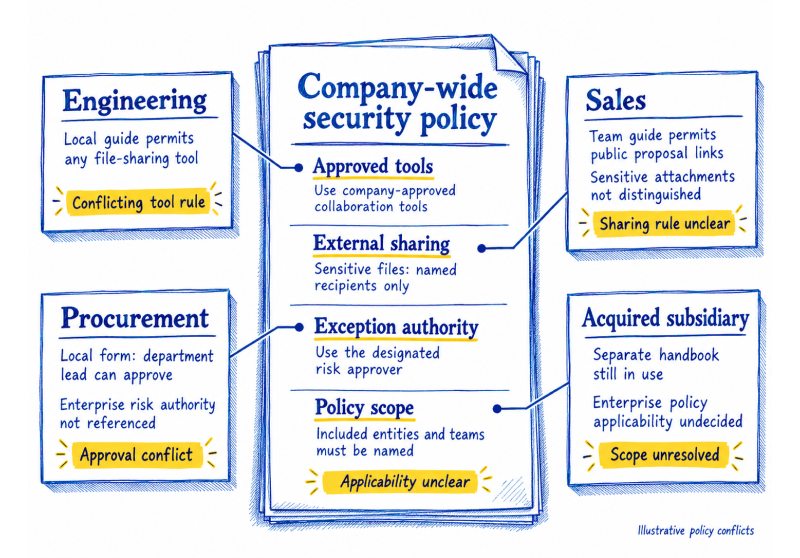
Designing a Company-Wide Information Security Policy for Every Team
A company-wide information security policy gives people clear expectations for protecting the organization’s information, systems, and operations. Its scope should fit how the business works across teams, locations, cloud environments,...
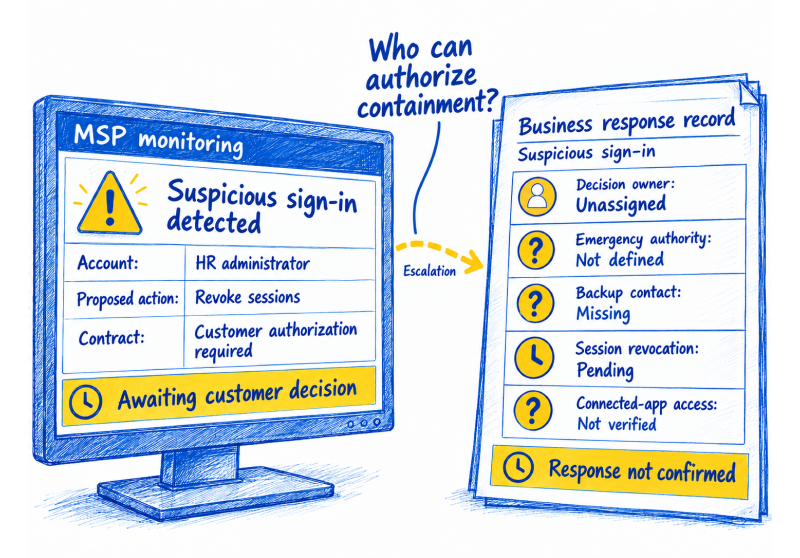
Who Owns Cyber Risk in a Small Business? Clarify Roles and Decisions
Cybersecurity responsibilities for small businesses span employees, IT staff, managed providers, and cloud vendors. Risk appears where their duties meet.Name who decides, who acts, and who verifies the outcome.Keep those...
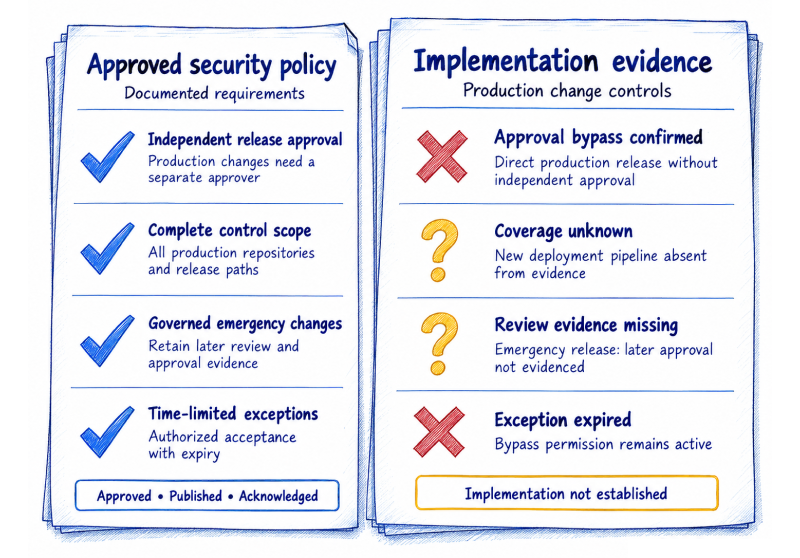
Cybersecurity Policy Management That Connects Rules to Real Controls
Cybersecurity policy management works when approved rules stay connected to accountable decisions, controls and current evidence. A policy library alone cannot show whether teams can apply a rule, whether systems...
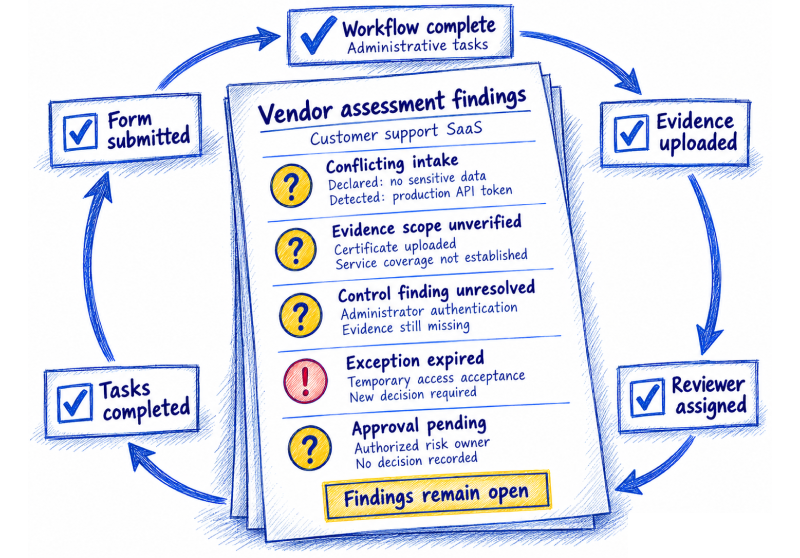
Automate Vendor Risk Assessments With Guardrails for Better Decisions
Automating vendor risk assessments should remove delay without turning a completed form into an approval. Routes each relationship appropriately, checks evidence quality and keeps risk decisions with accountable people. Keep...
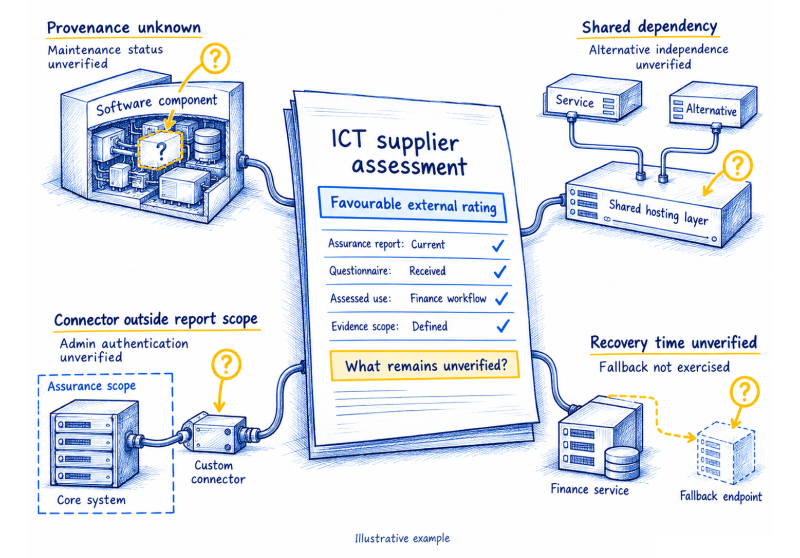
ICT Supplier Due Diligence Measures Risk Beyond Security Ratings Alone
ICT supplier due diligence helps organizations assess technology dependencies, validate assurance evidence and identify uncertainty before making risk decisions. This guide applies five due-diligence lenses to the intended use, separates...
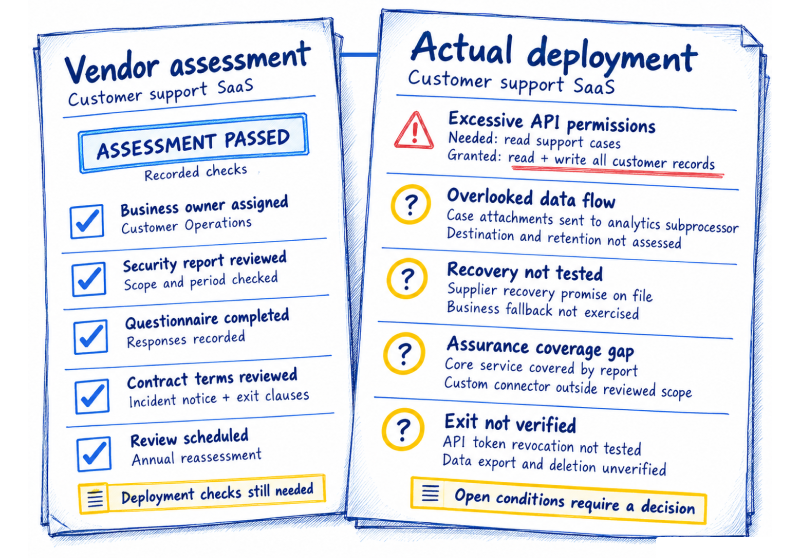
Vendor Risk Management: Govern Supplier Access, Data and Dependencies
Vendor risk management helps organizations govern supplier relationships from initial assessment through verified exit. Effective oversight connects each supplier’s business role, data access and operational dependencies to proportionate checks, clear...
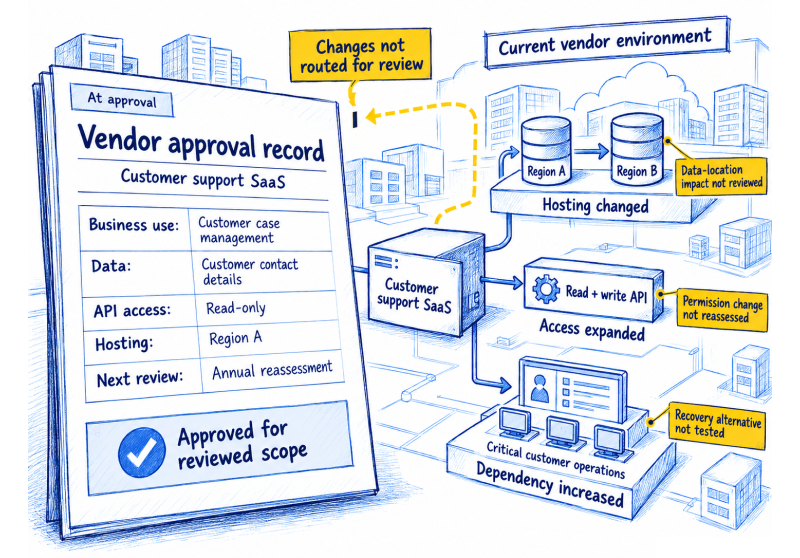
Vendor Risk Management Maturity Model for Stronger Oversight
Vendor risk management maturity measures how reliably an organization identifies supplier dependencies, makes proportionate risk decisions and revisits them as conditions change. This guide provides four maturity states, six capabilities...
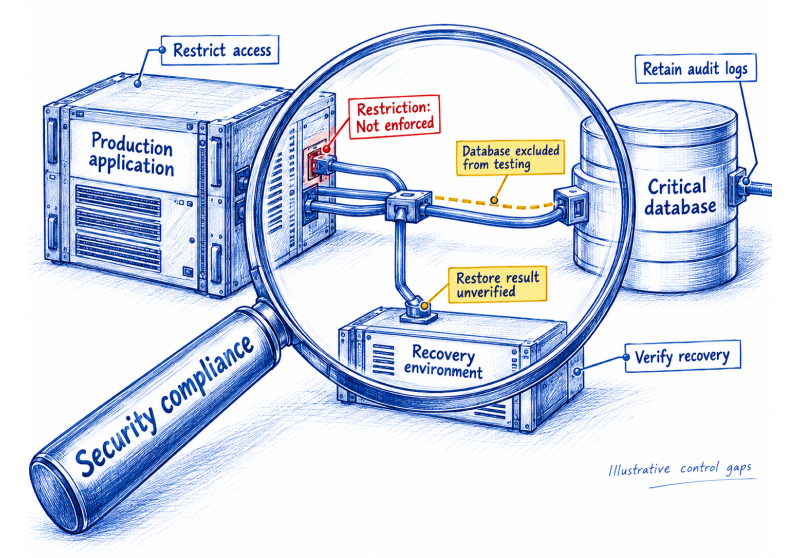
Security Compliance That Connects Regulatory Duties to Real Protection
Security compliance connects applicable requirements with safeguards that protect systems, information, and business operations. A useful program establishes which duties apply, assigns control ownership, and tests whether safeguards work across...