Featured
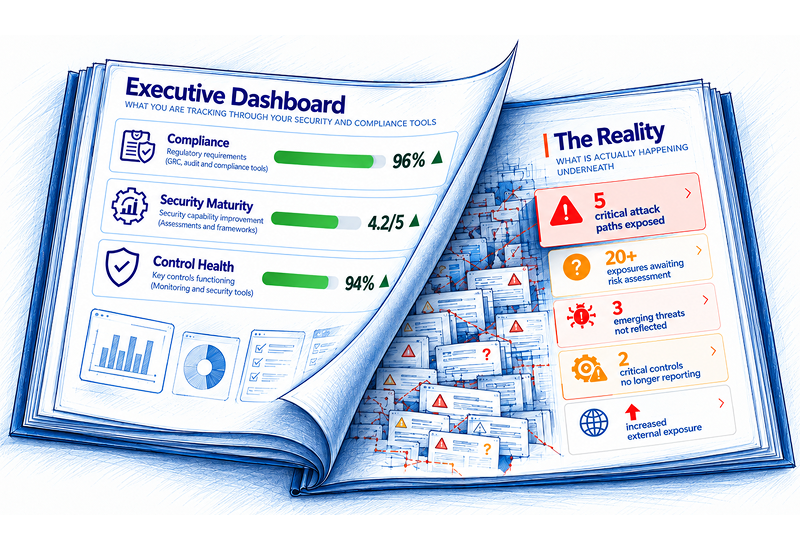
Why Green Security Dashboards Don’t Mean Lower Risk

Learn how compliance, security maturity, and continuously assessed business risk must work together to drive better security decisions. Compliance, security maturity, and risk assessment are three essential pillars of enterprise cybersecurity. Compliance measures adherence to defined requirements. Security maturity assesses organizational capabilities and opportunities for improvement. Risk assessment evaluates business exposure and the potential consequences of threats, considering existing safeguards. Yet an enterprise can achieve 96%...
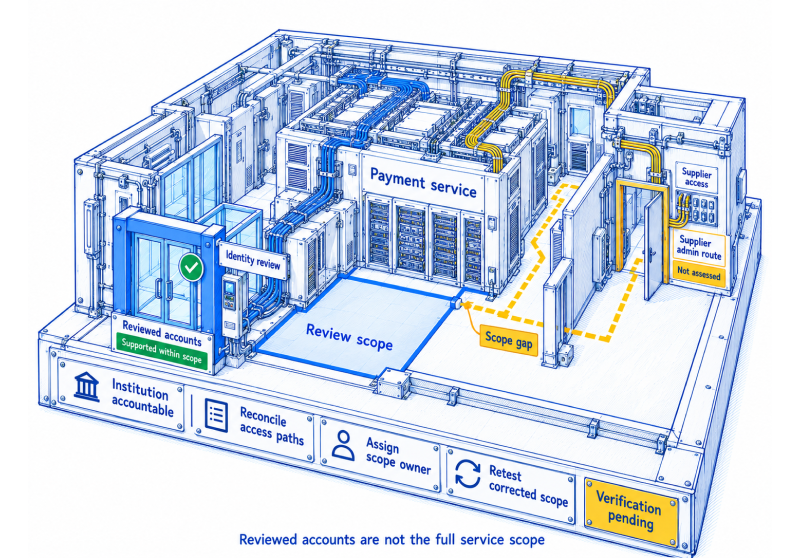
Financial Services Compliance: Can Your Evidence Support the Decision?

Financial services compliance needs evidence that supports decisions about critical services. Learn how to define control scope, assess supplier evidence, expose uncertainty and verify remediation while keeping institutional accountability clear....
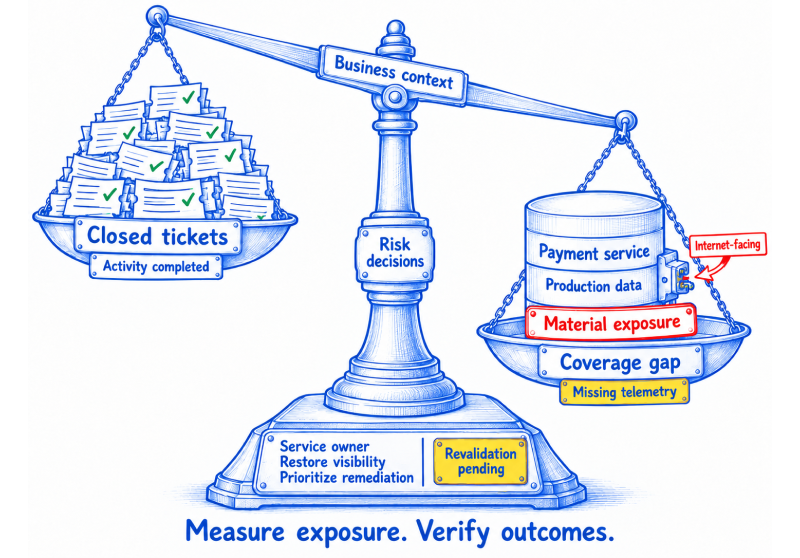
Cybersecurity Metrics in 2026: Link Control Evidence to Better Risk Decisions
Useful cybersecurity metrics show where material exposure remains, who needs to act and whether corrective work reduced the risk. Learn how to define populations, keep exceptions visible and connect control...
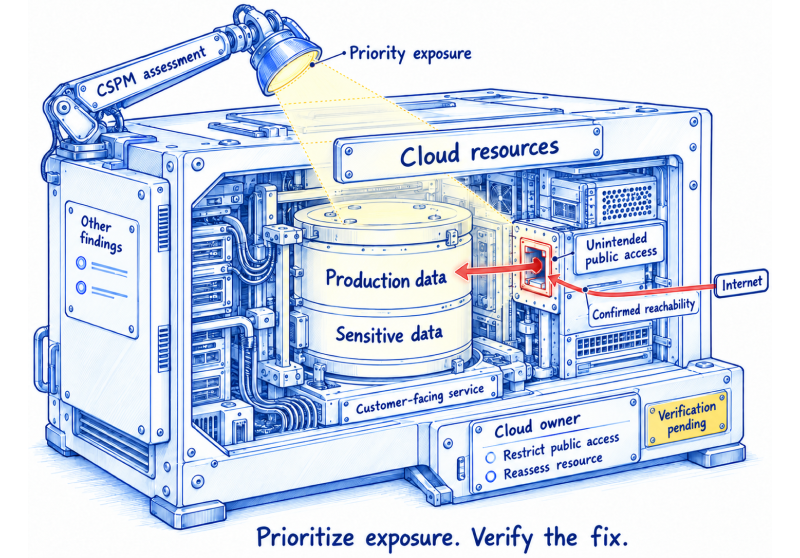
Cloud Security Posture Management: Find and Fix What Matters

Cloud security posture management helps teams find configuration gaps and understand which exposures matter most. Learn how to establish coverage, prioritize findings, assign owners and verify that remediation restores the...
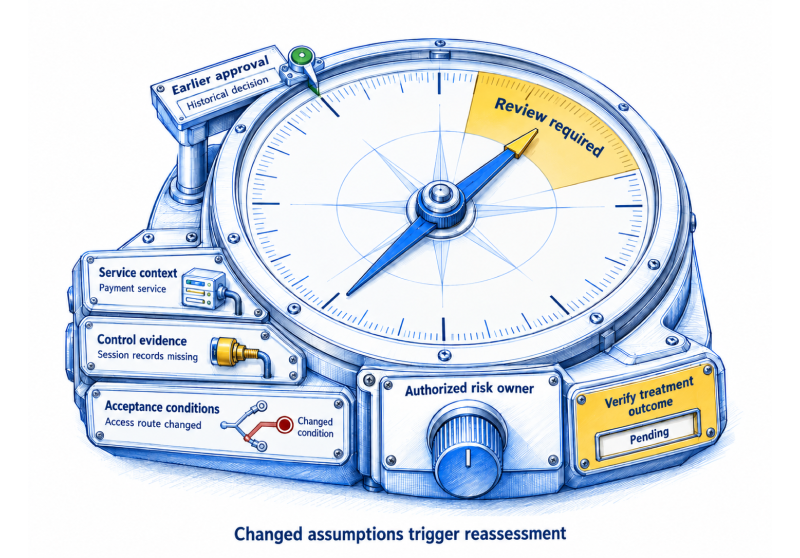
Enterprise GRC in 2026: Connect Cyber Risk, Evidence and Accountable Decisions
Effective enterprise GRC connects cyber risk to business services, current control evidence and accountable owners. Learn how to reassess decisions when conditions change, manage exceptions and verify treatment outcomes. A...
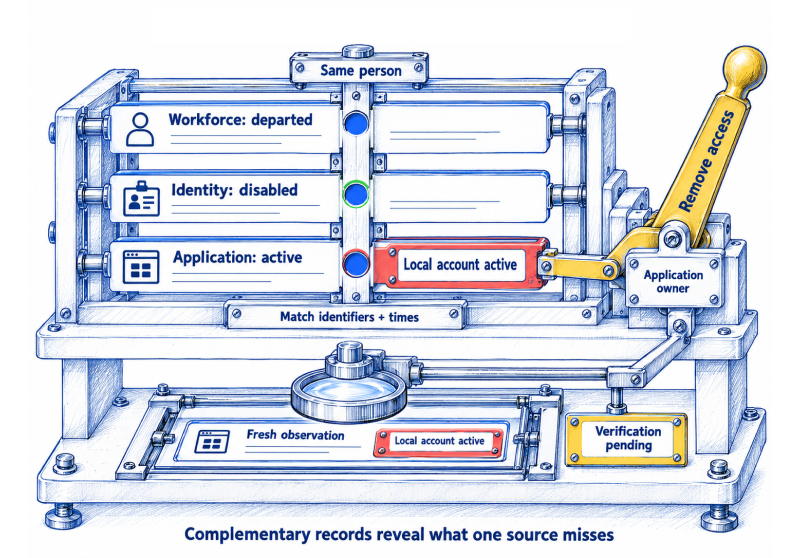
Compliance Automation: Make Your Integrations Count for Trusted Control Evidence
Integrations connect cloud, identity, endpoint and business systems to automate evidence collection and coordinate compliance workflows. They reduce repeated requests, support control assessments and route exceptions to accountable owners. The...
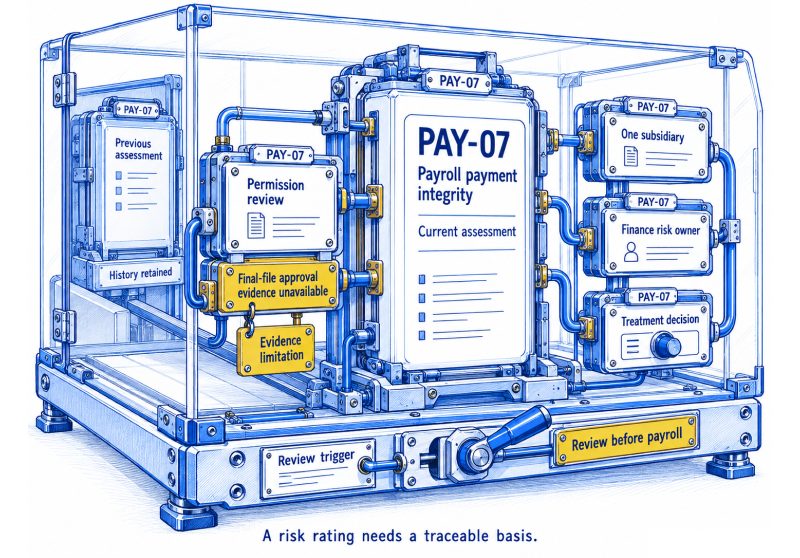
Build a Risk Register in 2026 With Clear Evidence and Traceable Business Decisions
A risk rating needs a clear basis and a record of the decision behind it. Build risk entries that connect business scenarios with evidence, ownership and review triggers, keeping current...
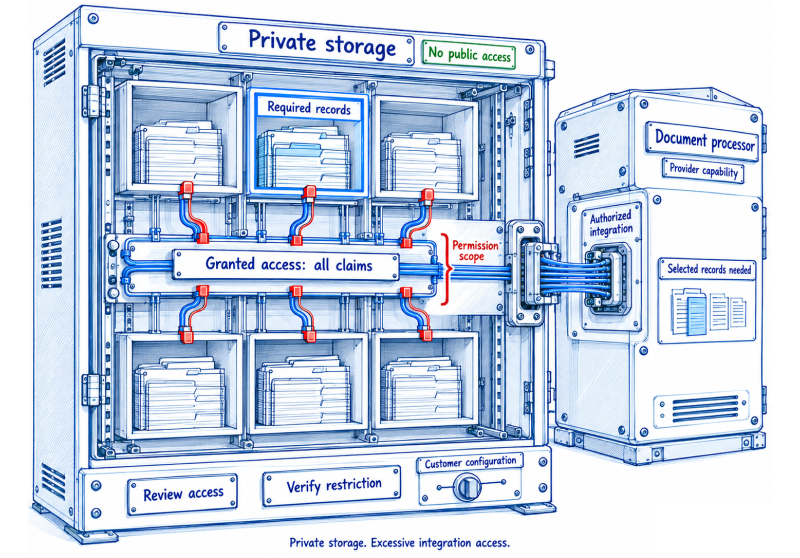
Cloud Risk Management in 2026: Map Ownership Across Services and Dependencies
Cloud risk extends beyond configuration settings. Map identity access, data flows and provider responsibilities across connected services to identify hidden exposure, assign ownership and test whether recovery dependencies hold up....
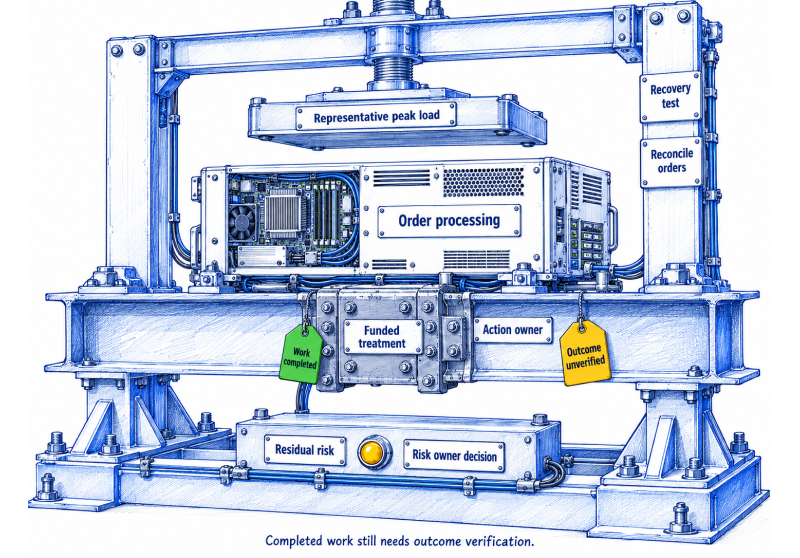
Risk Management Plan in 2026: Turn Decisions into Funded and Accountable Actions
Risk decisions need funding, ownership and follow-through. Build a risk management plan that connects response choices to accountable actions, tracks delivery and keeps remaining exposure visible as conditions change. A...
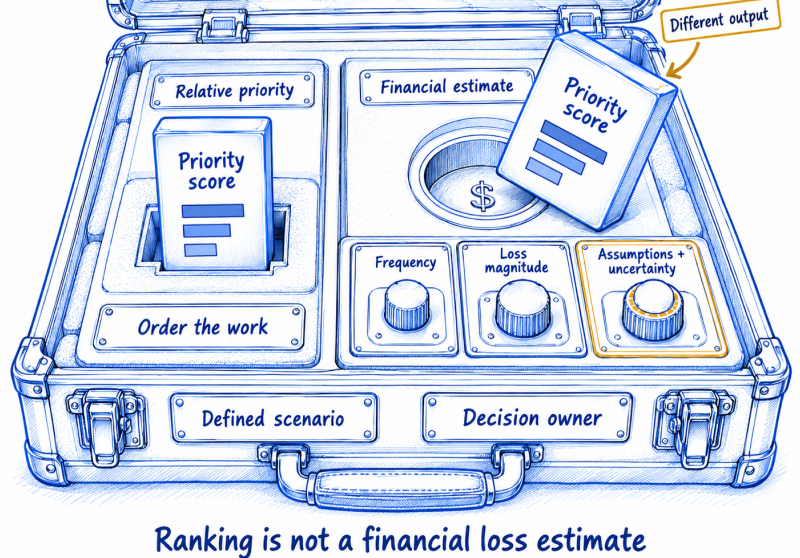
Cyber Risk Calculation Methods: Match the Output to the Decision
Different risk decisions need different outputs. Compare qualitative assessments, priority scores and quantitative loss estimates, and learn how to choose a method that makes assumptions, evidence and uncertainty clear to...
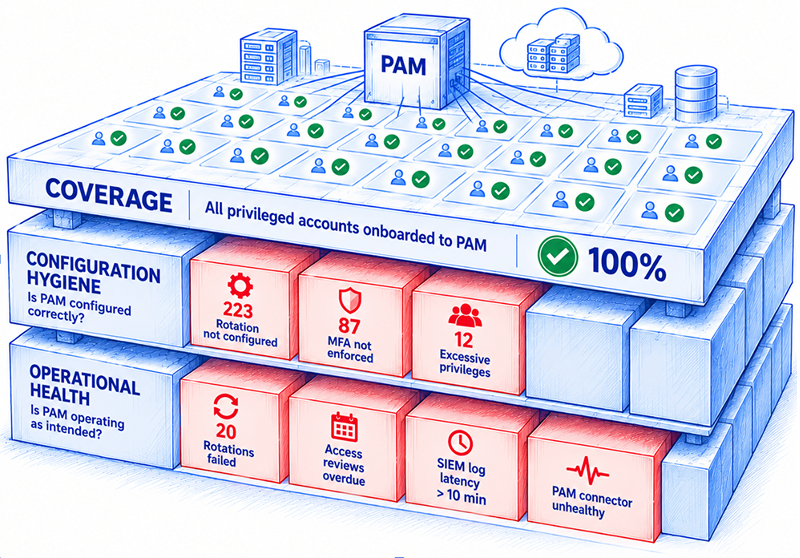
CBUAE C 1/2026: Monitoring and Testing Cybersecurity Controls

CBUAE C 1/2026 requires Licensed Financial Institutions to regularly monitor and test ICT and cybersecurity risk-mitigating measures. A practical approach is to define what each control is expected to achieve...
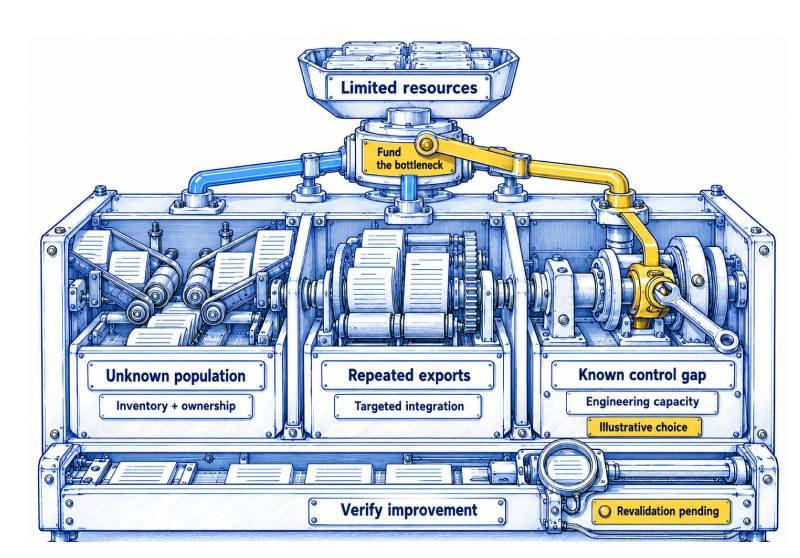
Security Governance on a Budget: Where Mid-Market Teams Should Invest First
Make limited security budgets count by focusing on critical services, reliable evidence and accountable action. Learn how mid-market teams can identify control gaps and decide where better data, expertise, automation...
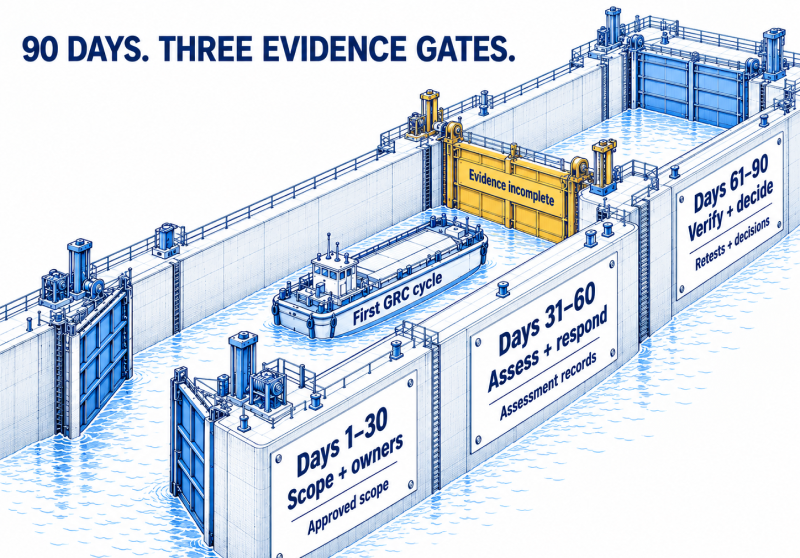
A 90-Day GRC Roadmap: From Scope and Ownership to Verified Controls Across Teams
Establish a first GRC voyage in 90 days, with clear scope, accountable owners and evidence that supports control decisions. Follow three practical phases to assess priority controls, verify remediation and...