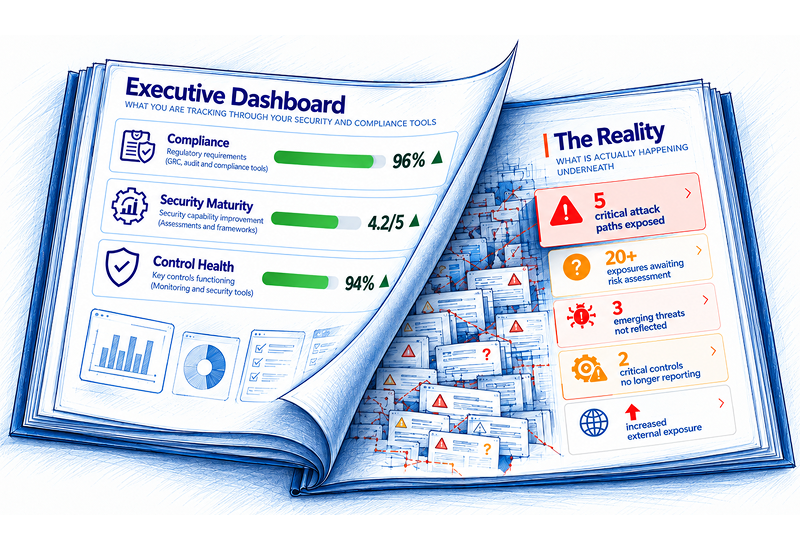
Vulnerability Management and Attack Surface Management: Two Views, One Program

Vulnerability Management and Attack Surface Management: Two Views, One Program

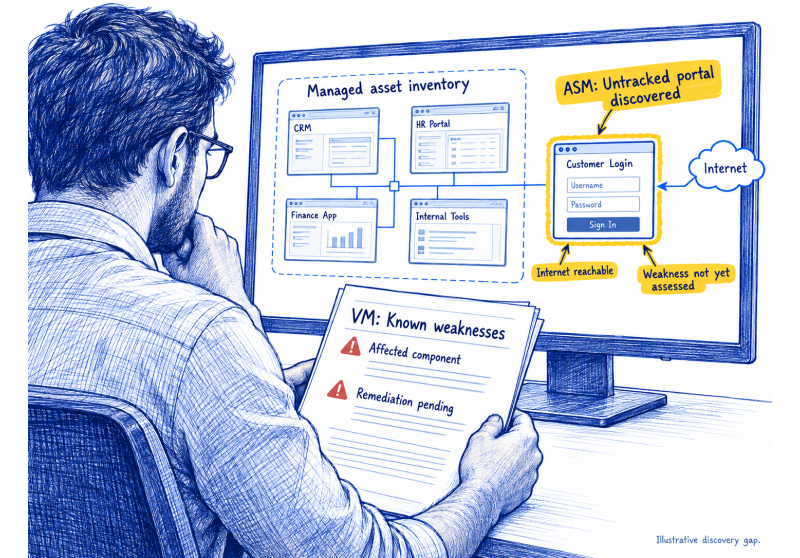
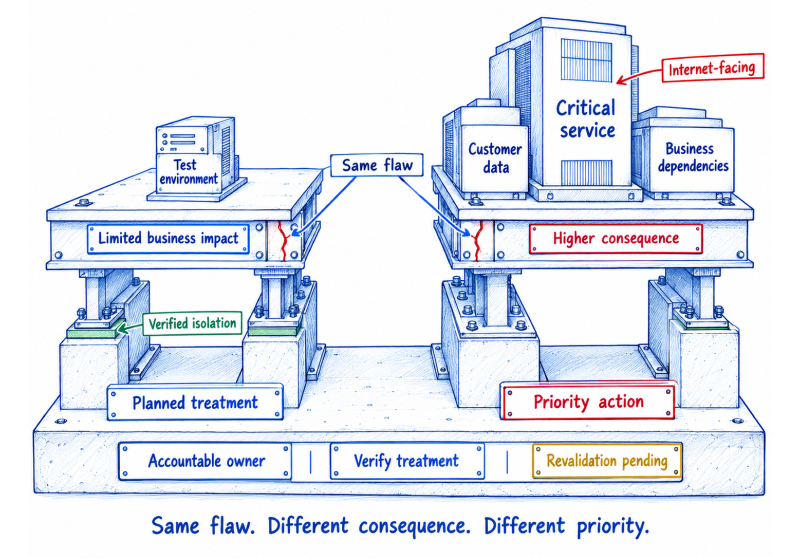
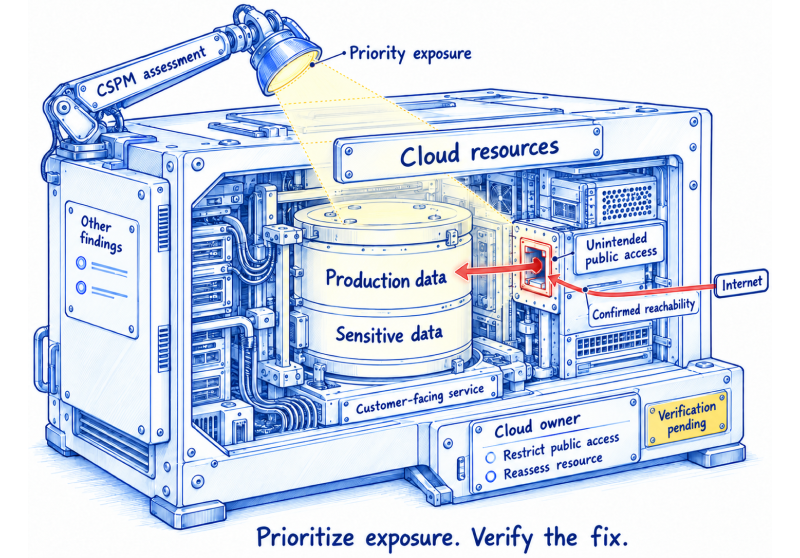
Vulnerability management confirms and treats known weaknesses; attack surface management shows where reachable assets and paths exist. Connect them to make exposure priorities actionable and verify that treatment worked. Vulnerability...

Categories: Cybersecurity, Exposure Management
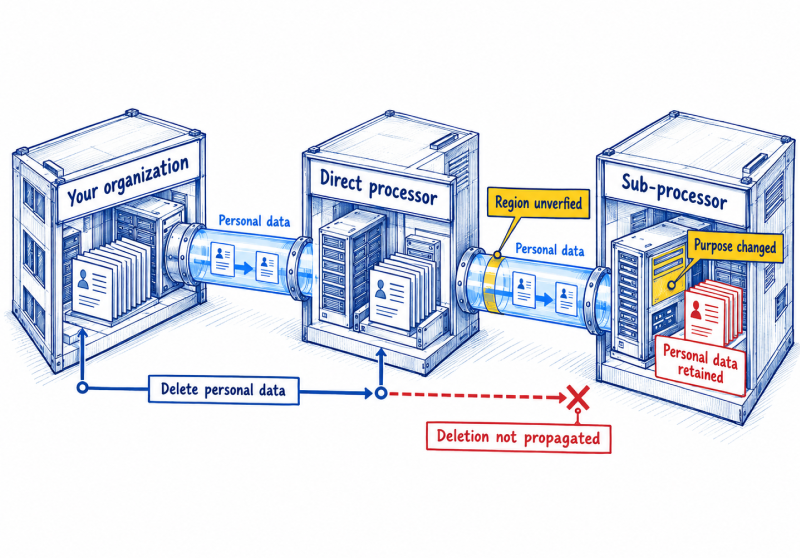
Sub-Processor Risk Management: Keep Privacy Controls Across Data Chains

Sub-Processor Risk Management: Keep Privacy Controls Across Data Chains

A direct vendor is only the first link in a personal-data chain. Build a program that keeps purpose, location, authorization, safeguards, and evidence connected as downstream processors change. Sub-processor risk...

Categories: GRC

Cybersecurity Control Impact Analysis: Find Control Failures Before They Spread

Cybersecurity Control Impact Analysis: Find Control Failures Before They Spread

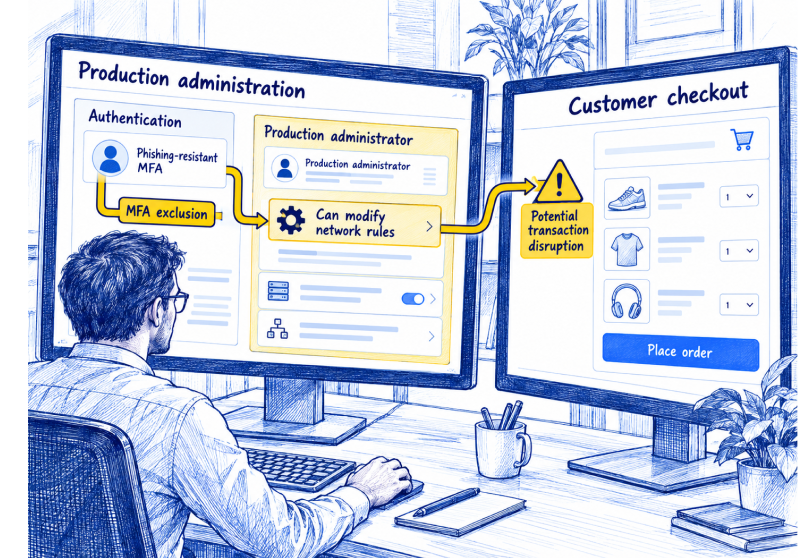
Understand what a weakened control exposes, which operations depend on it and how to verify that corrective action has restored protection. Cybersecurity control impact analysis traces a failed or weakened...

Categories: Cybersecurity, Risk Management
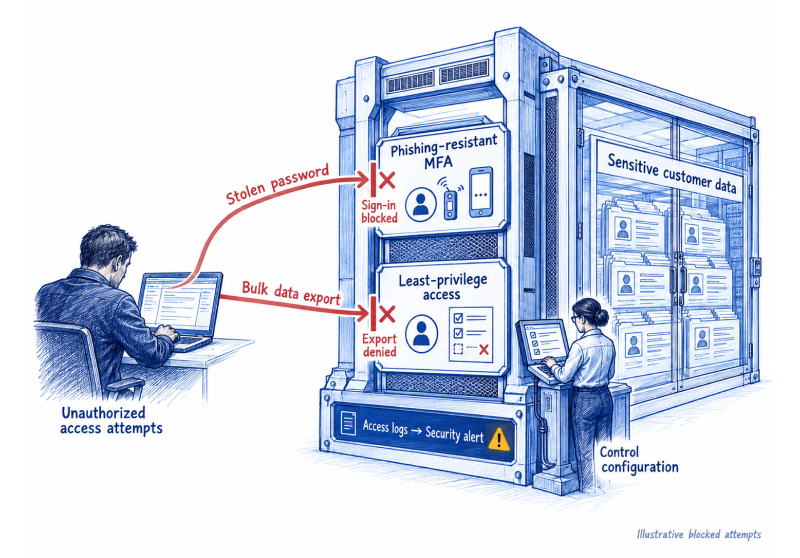
Data Breach Prevention: Build Controls That Protect Data Before Attackers Arrive

Data Breach Prevention: Build Controls That Protect Data Before Attackers Arrive

A practical guide to reducing the paths attackers can use to reach sensitive information.Build prevention around data, identity, and access decisions your teams can verify, not a checklist that looks...

Categories: Compliance, Cyber Risk, Cybersecurity
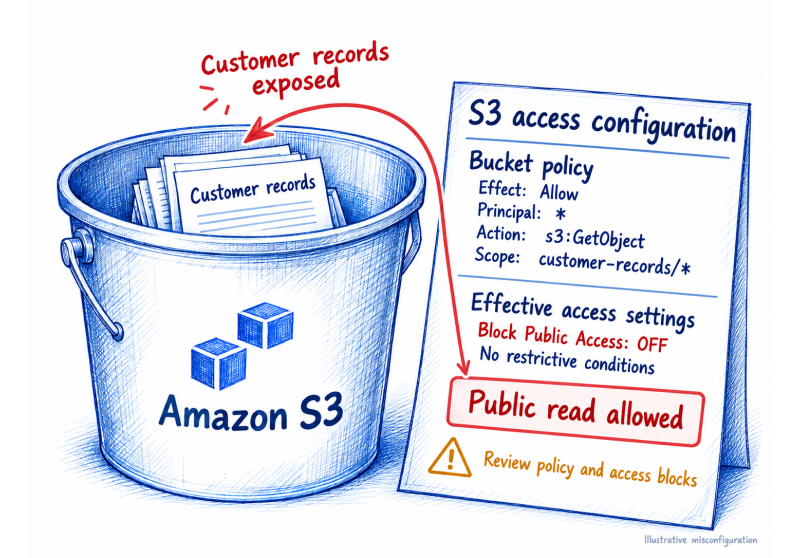
AWS Security Best Practices: Secure Multi-Account AWS Workloads With Guardrails

AWS Security Best Practices: Secure Multi-Account AWS Workloads With Guardrails

A practical guide to account boundaries, identity, guardrails, and operations in AWS.Build a secure foundation that lets workload teams move without relying on every account owner to remember every control....

Categories: Cloud Security, Cybersecurity, Risk Management
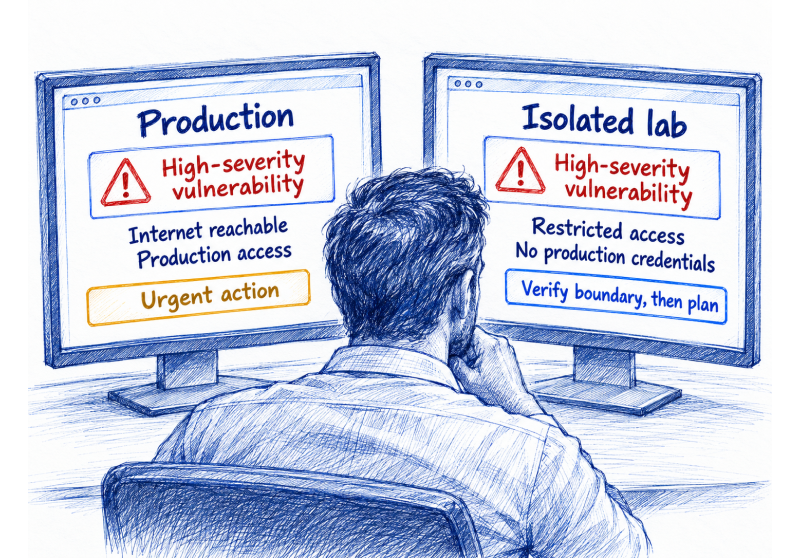
Risk-Based Vulnerability Management: Prioritize Exposure Beyond Scores

Risk-Based Vulnerability Management: Prioritize Exposure Beyond Scores

A practical guide for security and IT leaders deciding what to fix first.Use exploit evidence, real exposure, and business impact to create a defensible remediation queue. The backlog is a...

Categories: Cybersecurity, Risk Management
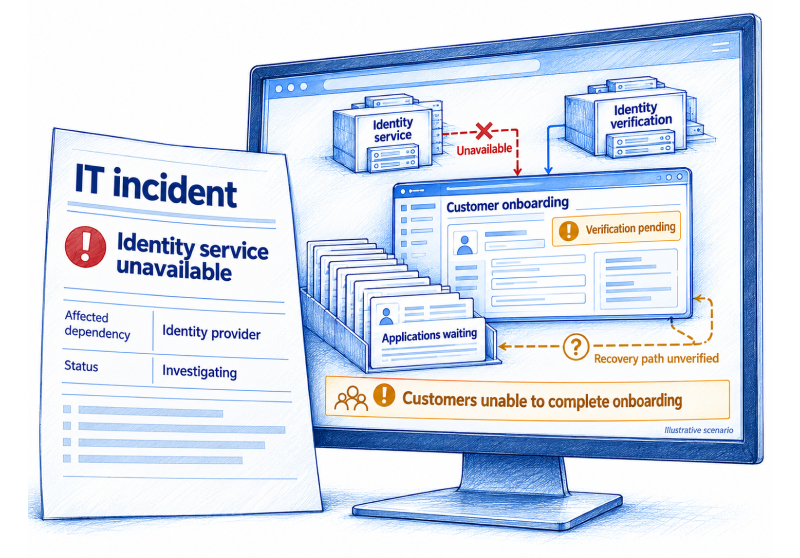
IT Risk Management in 2026: Connect Dependencies to Business Impact

IT Risk Management in 2026: Connect Dependencies to Business Impact

A practical guide for security, IT, and GRC leaders to identify concentration risk and improve portfolio decisions. IT risk management is harder to see when technology spans cloud platforms, vendors,...

Categories: Cybersecurity, Risk Management
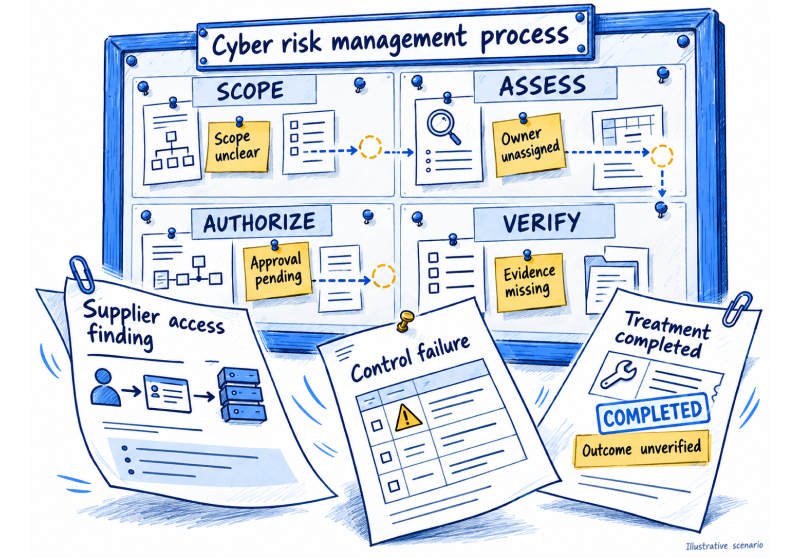
Cybersecurity Risk Management Process: A Practical Guide to Decisions

Cybersecurity Risk Management Process: A Practical Guide to Decisions

A cybersecurity risk management process should move from a defined business question to a decision, funded action, and evidence that the response worked.This guide gives security and GRC leaders a...

Categories: Cybersecurity, Risk Management
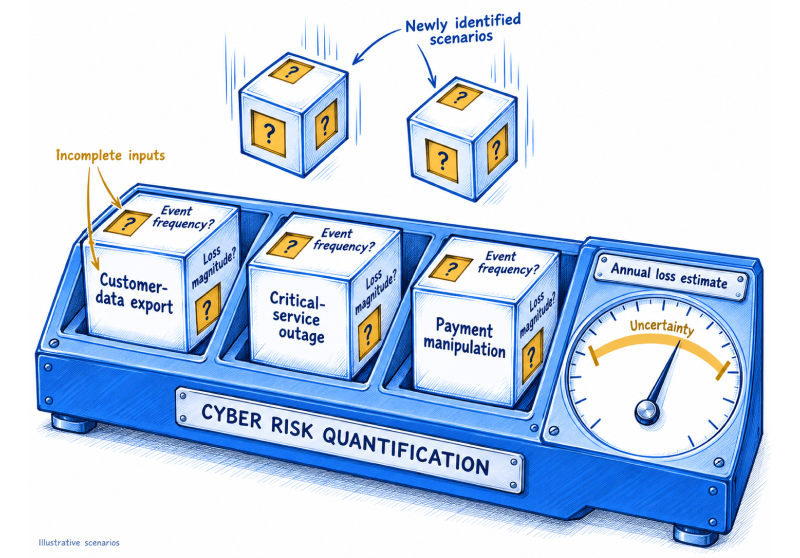
Quantitative Cyber Risk Analysis: Put Loss Ranges to Work in Security Decisions

Quantitative Cyber Risk Analysis: Put Loss Ranges to Work in Security Decisions

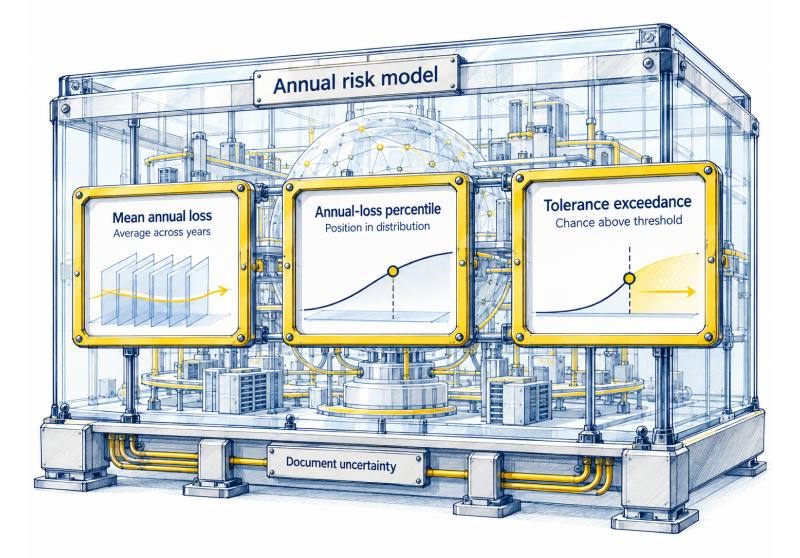
Quantitative cyber risk analysis can help leaders compare security choices, but a precise-looking number is only as sound as its scenario and inputs. This guide shows how to model loss...

Categories: Cybersecurity, Risk Management
Cybersecurity Risk Management Strategy: Define Priorities, Authority and Limits

Cybersecurity Risk Management Strategy: Define Priorities, Authority and Limits

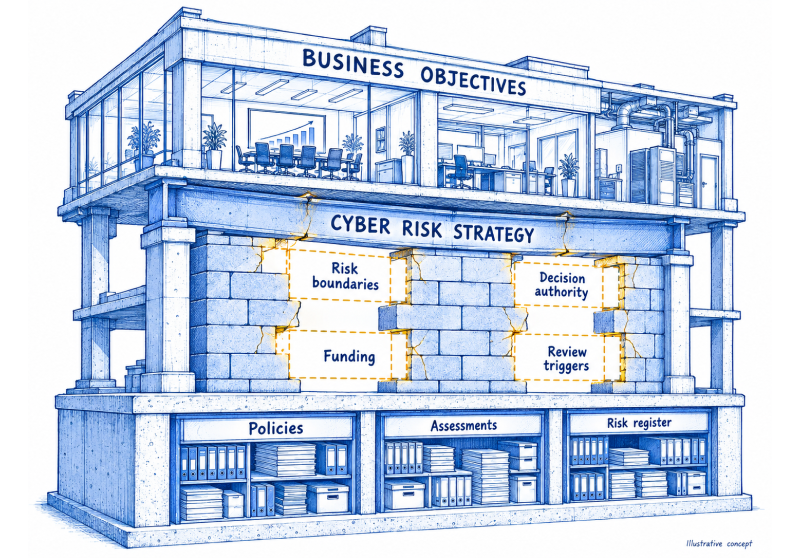
A cybersecurity risk management strategy should guide real choices about priorities, investment and acceptable exposure. This practical framework connects business objectives to decision authority, treatment and review. A cybersecurity risk...

Categories: Cybersecurity, Risk Management
Cybersecurity Risk Management Techniques: Choose the Right Method

Cybersecurity Risk Management Techniques: Choose the Right Method

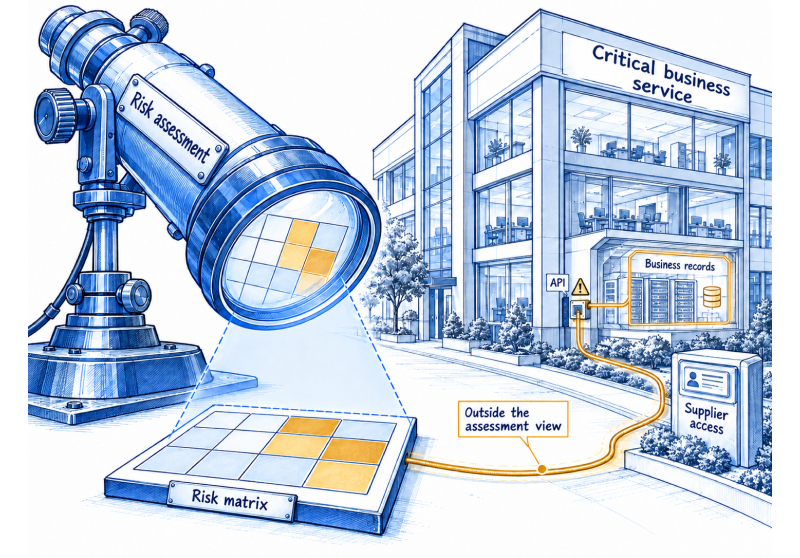
Different risk questions need different methods. Compare practical techniques, see how two methods reach different decisions on the same supplier scenario, and choose an approach that fits the evidence and...

Categories: Cybersecurity, GRC, Risk Management
Risk Mitigation Strategies: Comparing Treatment Choices and Trade-offs in Practice

Risk Mitigation Strategies: Comparing Treatment Choices and Trade-offs in Practice

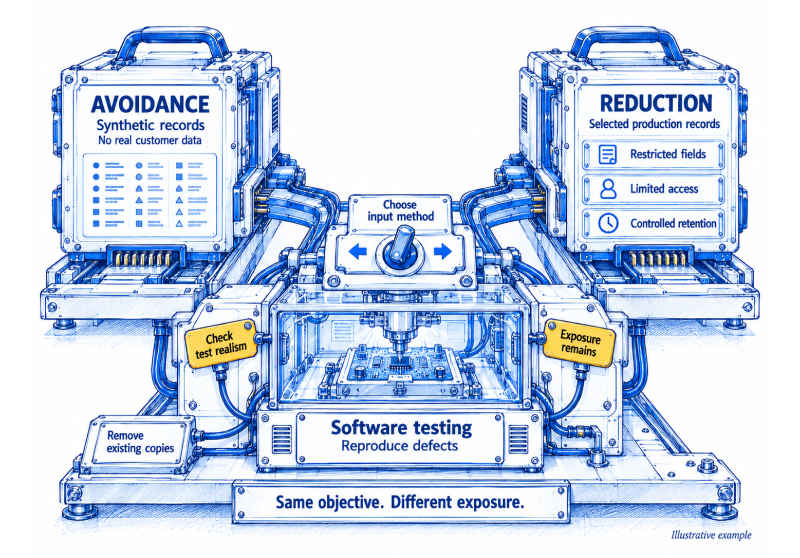
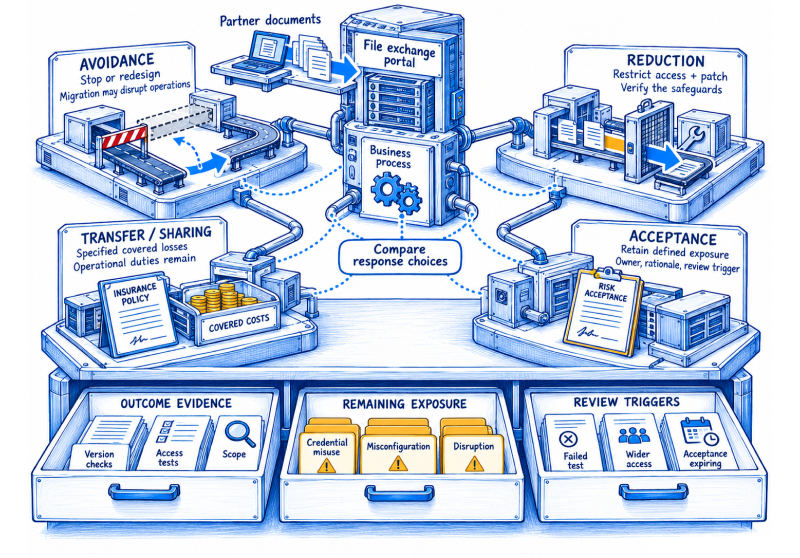
Risk mitigation is often used to mean reducing exposure, while risk treatment covers the full set of response choices. Learn how to compare avoidance, reduction, transfer and acceptance, then verify...

Categories: Cybersecurity, GRC, Risk Management
Inherent Risk vs Residual Risk: Use Control Evidence to Defend the Risk You Accept

Inherent Risk vs Residual Risk: Use Control Evidence to Defend the Risk You Accept

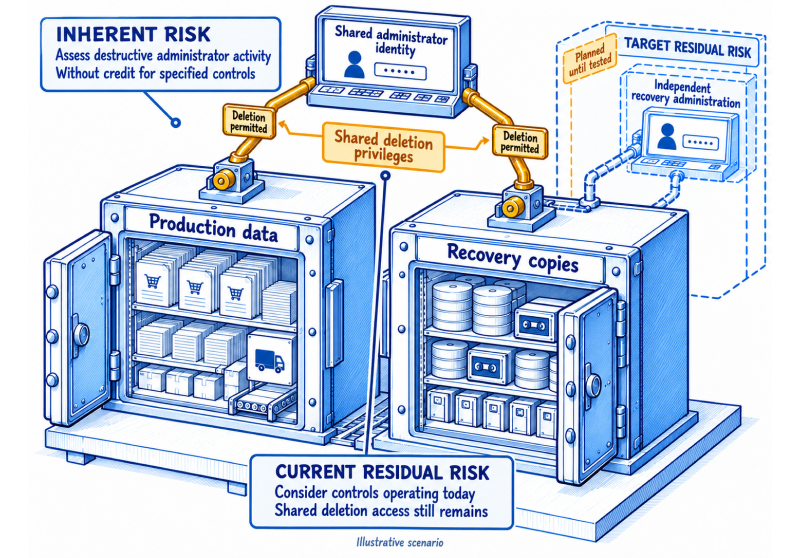
Inherent risk vs residual risk is a comparison between exposure without specified risk responses and exposure after those responses. The distinction helps leaders decide what protection is necessary, what risk...

Categories: Risk Management

Risk Management Framework in Practice From System Scope to Decisions You Can Defend

Risk Management Framework in Practice From System Scope to Decisions You Can Defend

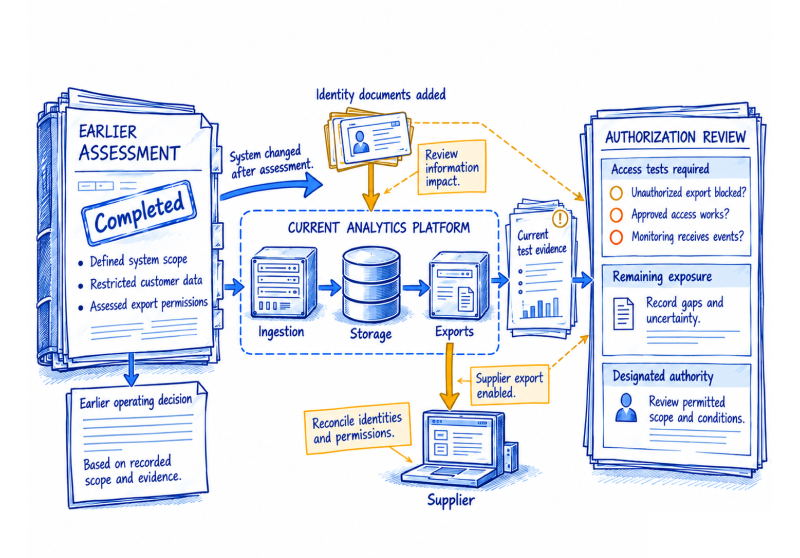
A risk management framework connects system scope, control evidence and accountable decisions. Applying NIST RMF means establishing why a system can operate, what exposure remains and which changes require that...

Categories: Risk Management

The UAE Risk Landscape Is Changing. Is Your Risk Strategy Keeping Up?

The UAE Risk Landscape Is Changing. Is Your Risk Strategy Keeping Up?

The article explains why UAE enterprises need to update risk assessments when threats, business dependencies, or control effectiveness change. It highlights how geopolitical uncertainty, cyber threats, and third-party disruptions can...

Categories: Risk Management

Risk Control Matrix: Connect Cybersecurity Risks to Controls and Useful Evidence

Risk Control Matrix: Connect Cybersecurity Risks to Controls and Useful Evidence

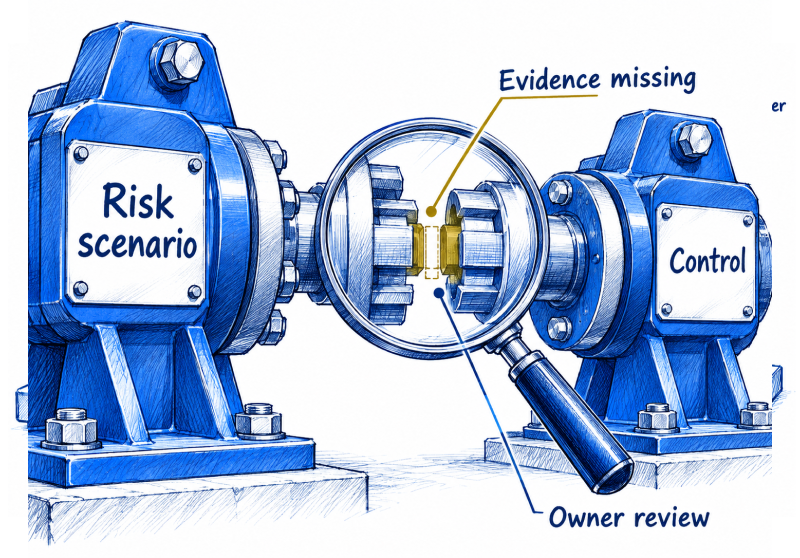
A risk control matrix makes clear how a defined business risk is addressed, who owns the response, and what evidence shows the control works. For cybersecurity and GRC teams, its...

Categories: Cybersecurity, GRC, Risk Management
Operational Risk Management in 2026: Keep Decisions Current as Operations Change

Operational Risk Management in 2026: Keep Decisions Current as Operations Change

Operational risk management helps leaders understand how everyday activity can disrupt critical services, and what to do before a weakness becomes a loss. A practical program connects risk scenarios to...

Categories: Cybersecurity, GRC, Risk Management
Attack Surface Management in 2026: Find Unknown Assets and Reduce Their Exposure

Attack Surface Management in 2026: Find Unknown Assets and Reduce Their Exposure

Attack surface management helps security teams discover assets and access paths their existing inventories miss. Learn how external and internal discovery, contextual prioritization and targeted remediation reduce exposure across changing...

Categories: Cybersecurity, Exposure Management
Business Impact Analysis in 2026: Connect Critical Services to Recovery Decisions

Business Impact Analysis in 2026: Connect Critical Services to Recovery Decisions

Business impact analysis helps organizations understand how disruption affects critical services and set recovery priorities. This article explains how to assess impacts over time, map dependencies, define realistic recovery targets...

Categories: Risk Management

Dynamic Risk Assessment: Keep Cyber Risk Decisions Current as Conditions Change

Dynamic Risk Assessment: Keep Cyber Risk Decisions Current as Conditions Change

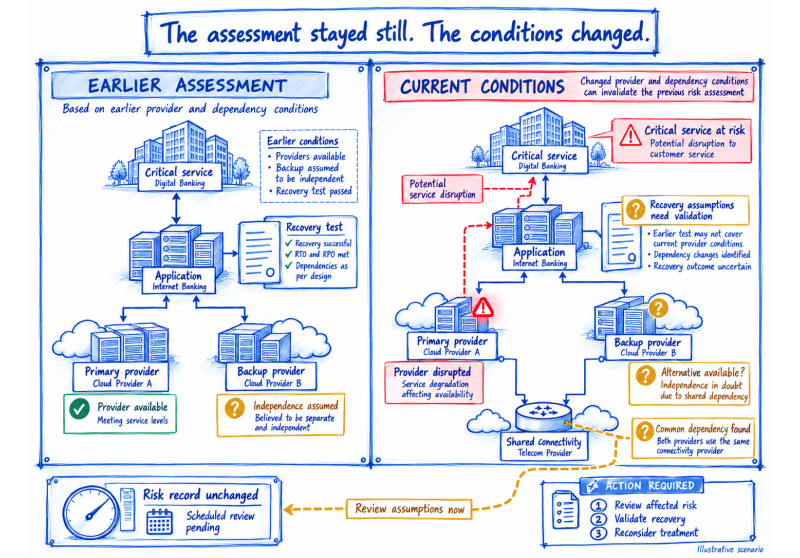
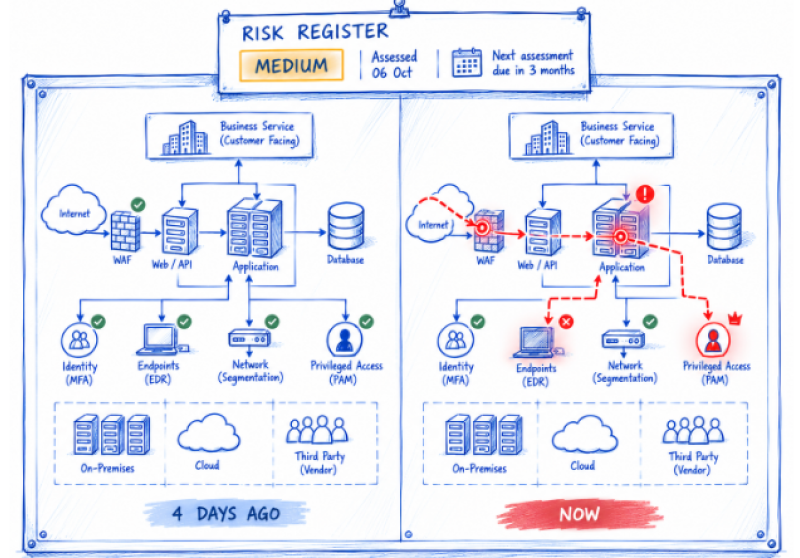
Cyber risk changes when the conditions behind an assessment change. Dynamic Risk Assessment connects material changes in assets, threats and controls to existing risks, helping teams revisit treatment and acceptance...

Categories: Cyber Risk

Quantitative Cyber Risk Assessment in 2026 for Better GRC Decisions

Quantitative Cyber Risk Assessment in 2026 for Better GRC Decisions

Quantitative cyber risk assessment helps teams decide which security treatments justify their cost. Defined scenarios, current evidence and explicit uncertainty make the estimates useful to security, finance and business owners....

Categories: Cybersecurity, Risk Management
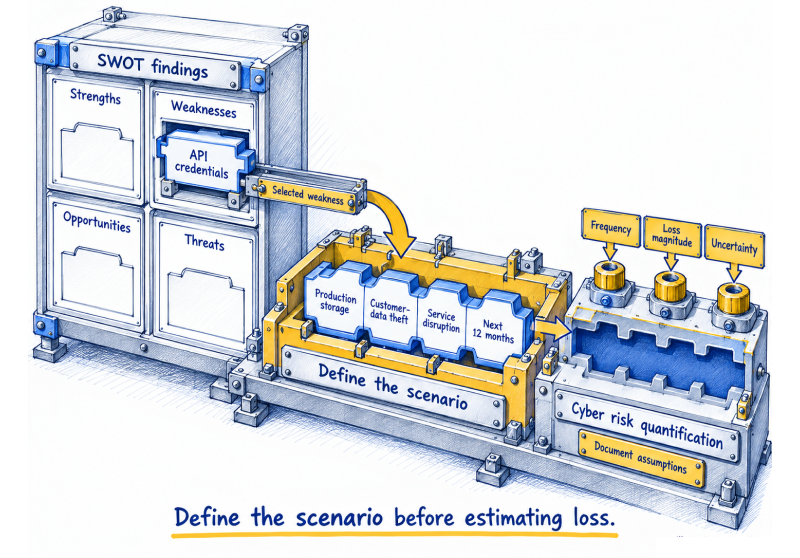
SWOT Analysis and Cyber Risk Quantification: A Practical GRC Strategy for 2026

SWOT Analysis and Cyber Risk Quantification: A Practical GRC Strategy for 2026

SWOT analysis can help security leaders identify strategic concerns, while cyber risk quantification can test how those concerns may affect the business. This article explains how to connect the two...

Categories: Cybersecurity, Risk Management
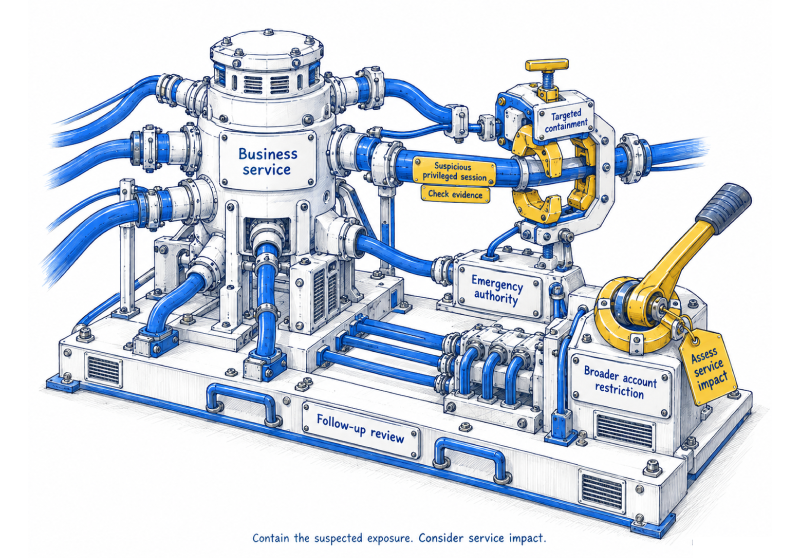
Human Factors in Incident Response in 2026: Make Safer Decisions Under Pressure

Human Factors in Incident Response in 2026: Make Safer Decisions Under Pressure

How security leaders can design roles, handoffs and decision safeguards that help people contain incidents without creating a second failure. Human factors in incident response are not a training topic...

Categories: Cybersecurity

Risk Scoring in 2026: Make Internal and External Risks Comparable Across Teams

Risk Scoring in 2026: Make Internal and External Risks Comparable Across Teams

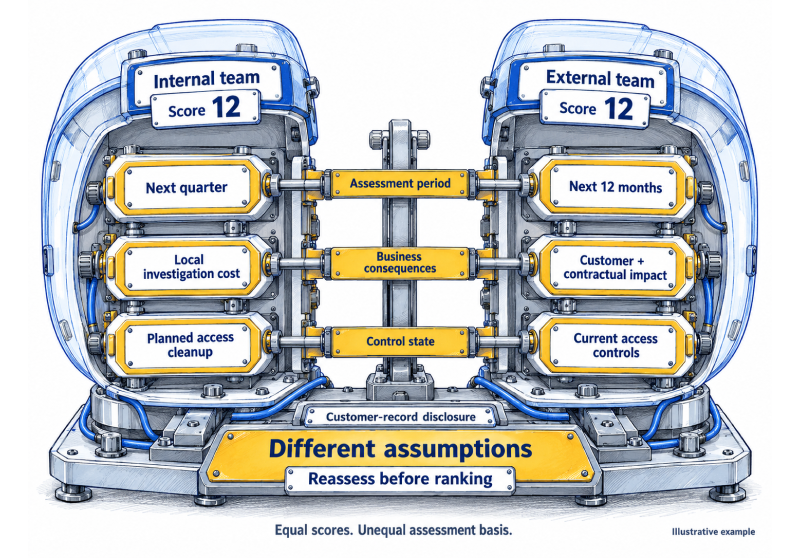
Learn how to calculate risk scores, reconcile conflicting ratings and compare internal failures with external threats without distorting management priorities. The method aligns scenarios, time horizons, impact criteria, control assumptions...

Categories: Cybersecurity, Risk Management
CERT-In’s 12-Hour Remediation Window: Why Faster Patching Is Not Enough

CERT-In’s 12-Hour Remediation Window: Why Faster Patching Is Not Enough

CERT-In’s 2026 vulnerability remediation guidance challenges how enterprises manage cyber exposure. Meeting shorter remediation windows requires continuous exposure intelligence, faster decisions, and verified risk reduction, not simply faster patch deployment....

Categories: Compliance

Risk Avoidance vs Risk Reduction in 2026: Choosing the Right Business Response

Risk Avoidance vs Risk Reduction in 2026: Choosing the Right Business Response

Compare the value of continuing an activity with the cost of withdrawing, and choose a response that addresses the specific exposure. Risk avoidance vs risk reduction asks a practical business...

Categories: Cybersecurity, GRC, Risk Management
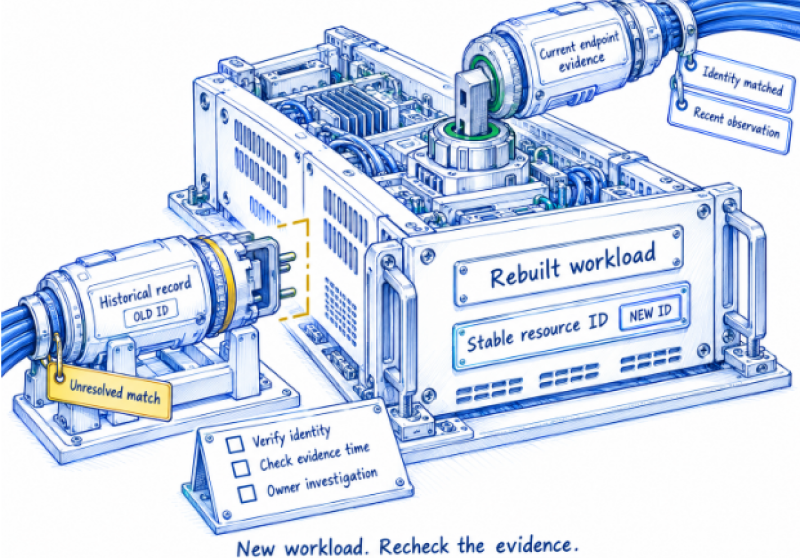
CAASM: Make Asset Visibility Useful for Security Decisions and Responses

CAASM: Make Asset Visibility Useful for Security Decisions and Responses

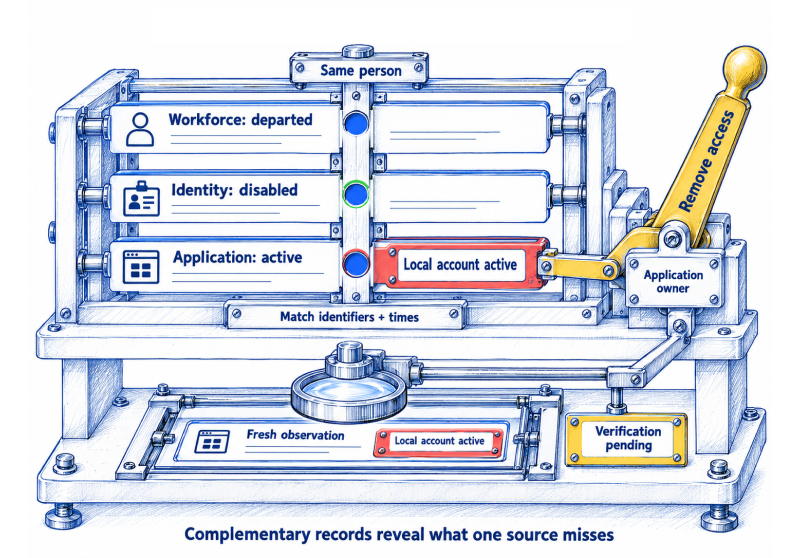
Cyber Asset Attack Surface Management connects fragmented asset records so teams can investigate exposure and security coverage. Its value depends on explainable matching, current evidence and decisions that reach an...

Categories: Exposure Management

Cyber Risk and Compliance Risk: Decide What Needs Action

Cyber Risk and Compliance Risk: Decide What Needs Action

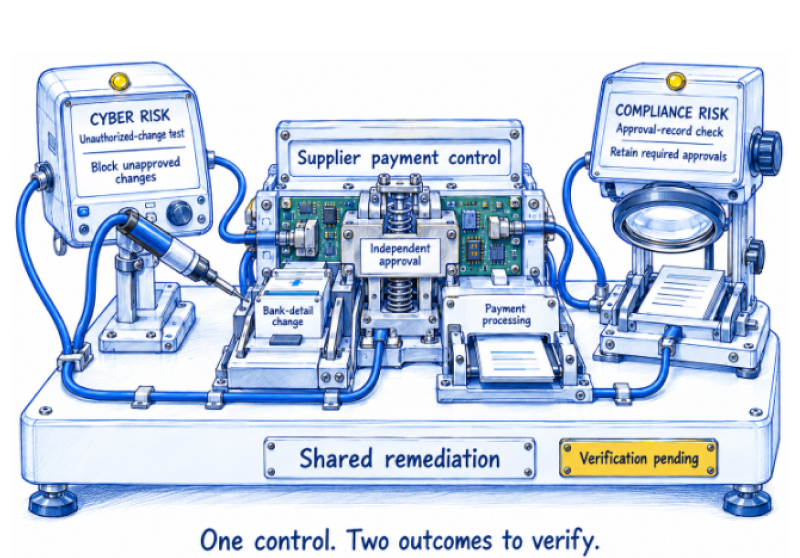
Cyber risk and compliance risk can share the same control weakness while requiring different decisions. Learn how mid-market teams can assess business harm and applicable obligations together, coordinate corrective action...

Categories: Compliance, Risk Management
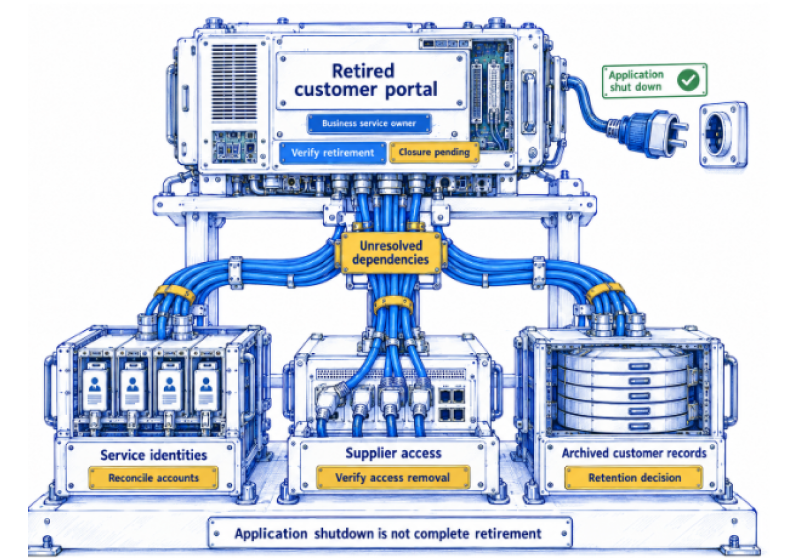
IT GRC: Keep Accountability Intact When Technology Changes

IT GRC: Keep Accountability Intact When Technology Changes

IT governance, risk management, and compliance (IT GRC) should help a CISO answer a difficult operational question: when technology changes, do the business's risk decisions and control assurances still hold?...

Categories: Risk Management

Financial Services Compliance: Can Your Evidence Support the Decision?

Financial Services Compliance: Can Your Evidence Support the Decision?

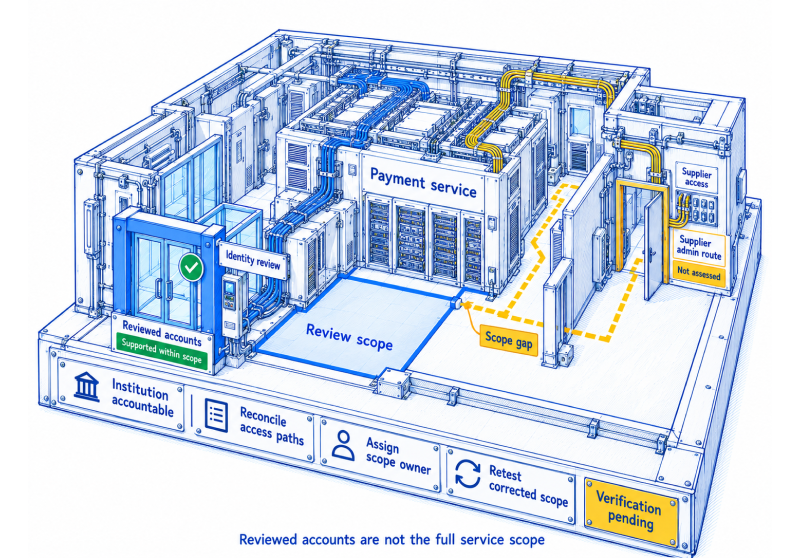
Financial services compliance needs evidence that supports decisions about critical services. Learn how to define control scope, assess supplier evidence, expose uncertainty and verify remediation while keeping institutional accountability clear....

Categories: Cybersecurity

Cybersecurity Risk Scoring: Make the Score Decision-Ready

Cybersecurity Risk Scoring: Make the Score Decision-Ready

A cybersecurity risk score should explain why an exposure matters and what action it requires. Learn how to combine threat signals, reachability, business impact and control evidence into clear priorities,...

Categories: Cybersecurity, Risk Management
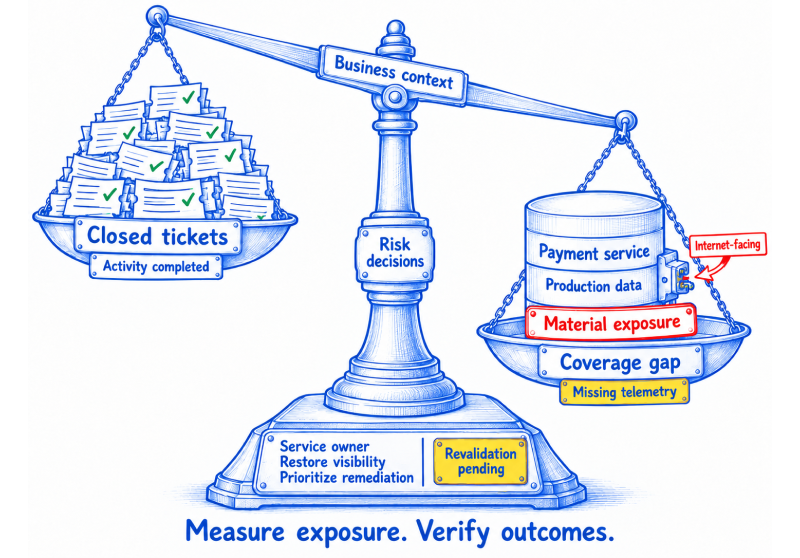
Cybersecurity Metrics in 2026: Link Control Evidence to Better Risk Decisions

Cybersecurity Metrics in 2026: Link Control Evidence to Better Risk Decisions

Useful cybersecurity metrics show where material exposure remains, who needs to act and whether corrective work reduced the risk. Learn how to define populations, keep exceptions visible and connect control...

Categories: Cybersecurity, GRC

Cloud Security Posture Management: Find and Fix What Matters

Cloud Security Posture Management: Find and Fix What Matters

Cloud security posture management helps teams find configuration gaps and understand which exposures matter most. Learn how to establish coverage, prioritize findings, assign owners and verify that remediation restores the...

Categories: Cloud Security, Risk Management
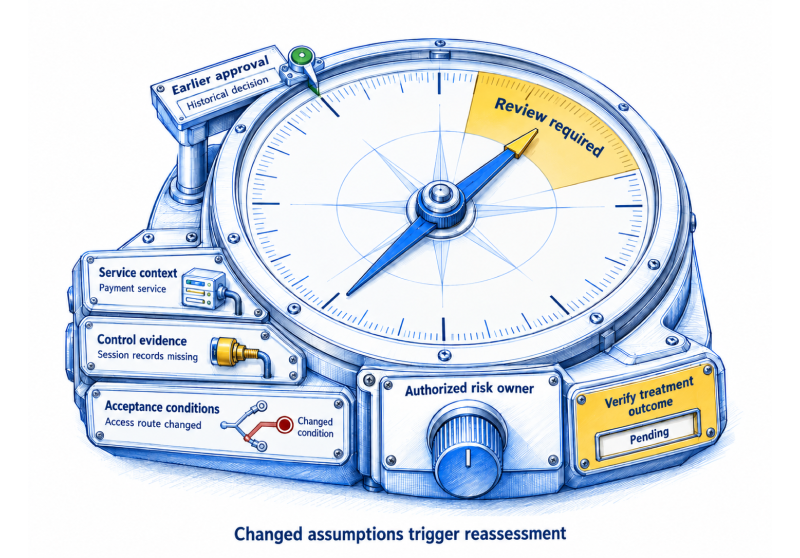
Enterprise GRC in 2026: Connect Cyber Risk, Evidence and Accountable Decisions

Enterprise GRC in 2026: Connect Cyber Risk, Evidence and Accountable Decisions

Effective enterprise GRC connects cyber risk to business services, current control evidence and accountable owners. Learn how to reassess decisions when conditions change, manage exceptions and verify treatment outcomes. A...

Categories: Cyber Risk, ISO 27001

Compliance Automation: Make Your Integrations Count for Trusted Control Evidence

Compliance Automation: Make Your Integrations Count for Trusted Control Evidence

Integrations connect cloud, identity, endpoint and business systems to automate evidence collection and coordinate compliance workflows. They reduce repeated requests, support control assessments and route exceptions to accountable owners. The...

Categories: Compliance

Build a Risk Register in 2026 With Clear Evidence and Traceable Business Decisions

Build a Risk Register in 2026 With Clear Evidence and Traceable Business Decisions

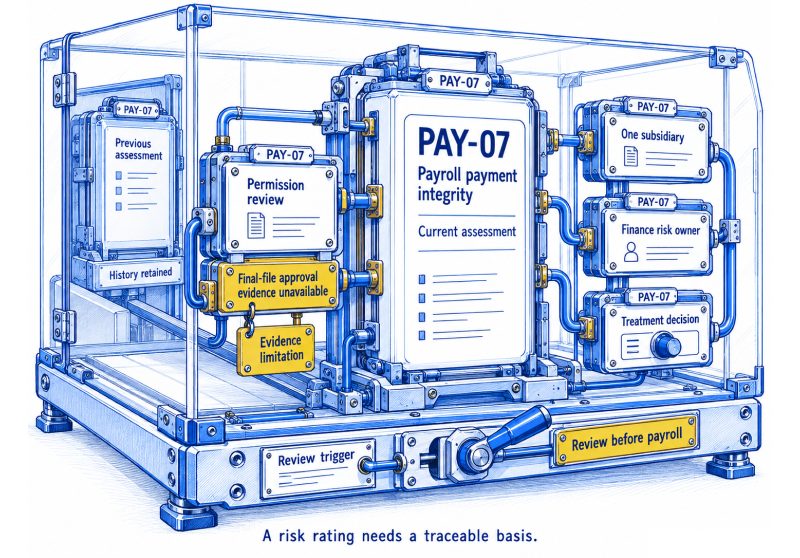
A risk rating needs a clear basis and a record of the decision behind it. Build risk entries that connect business scenarios with evidence, ownership and review triggers, keeping current...

Categories: Cybersecurity, GRC, Risk Management
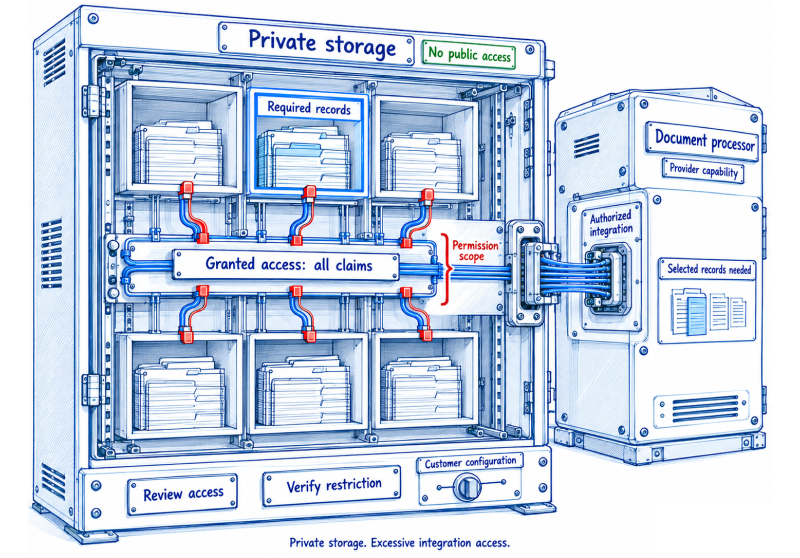
Cloud Risk Management in 2026: Map Ownership Across Services and Dependencies

Cloud Risk Management in 2026: Map Ownership Across Services and Dependencies

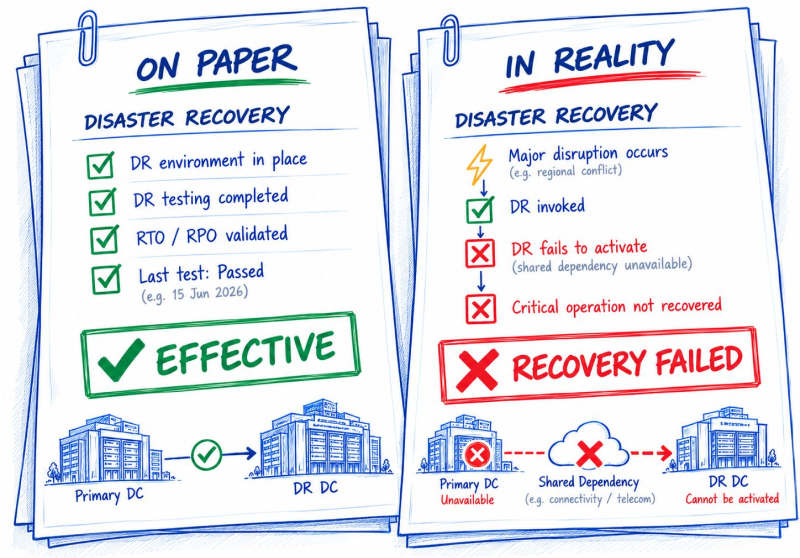
Cloud risk extends beyond configuration settings. Map identity access, data flows and provider responsibilities across connected services to identify hidden exposure, assign ownership and test whether recovery dependencies hold up....

Categories: Cloud Security, GRC, Risk Management
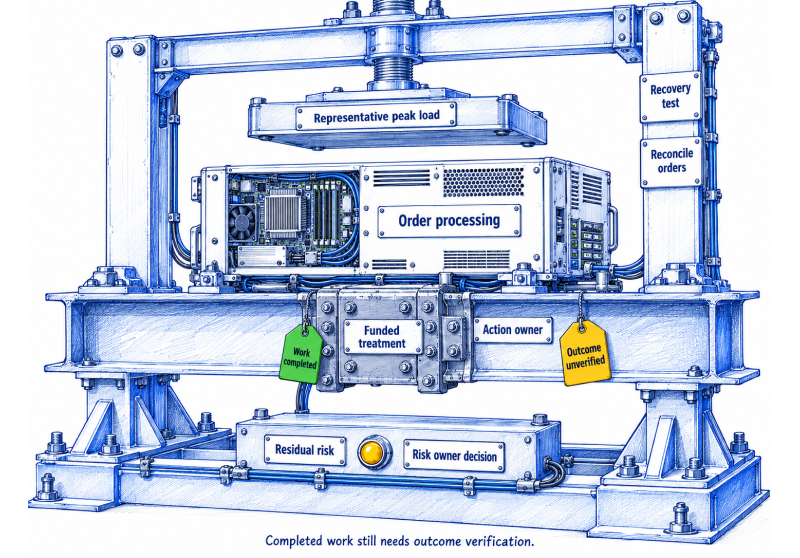
Risk Management Plan in 2026: Turn Decisions into Funded and Accountable Actions 

Risk Management Plan in 2026: Turn Decisions into Funded and Accountable Actions 

Risk decisions need funding, ownership and follow-through. Build a risk management plan that connects response choices to accountable actions, tracks delivery and keeps remaining exposure visible as conditions change. A...

Categories: Cybersecurity, GRC, Risk Management
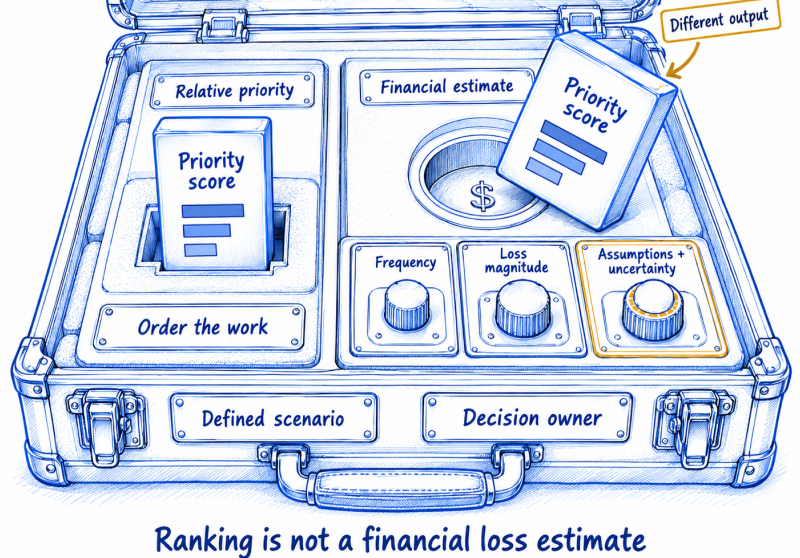
Cyber Risk Calculation Methods: Match the Output to the Decision

Cyber Risk Calculation Methods: Match the Output to the Decision

Different risk decisions need different outputs. Compare qualitative assessments, priority scores and quantitative loss estimates, and learn how to choose a method that makes assumptions, evidence and uncertainty clear to...

Categories: Cyber Risk, Risk Management
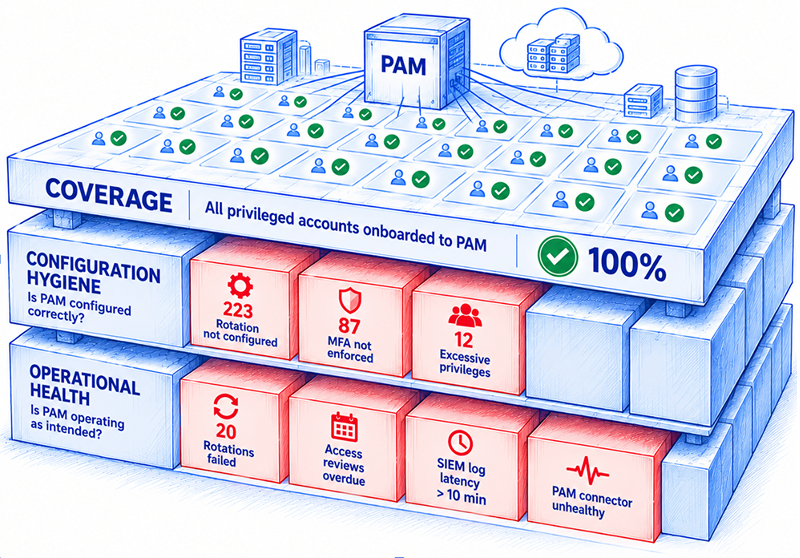
CBUAE C 1/2026: Monitoring and Testing Cybersecurity Controls

CBUAE C 1/2026: Monitoring and Testing Cybersecurity Controls

CBUAE C 1/2026 requires Licensed Financial Institutions to regularly monitor and test ICT and cybersecurity risk-mitigating measures. A practical approach is to define what each control is expected to achieve...

Categories: CBUAE

Security Governance on a Budget: Where Mid-Market Teams Should Invest First

Security Governance on a Budget: Where Mid-Market Teams Should Invest First

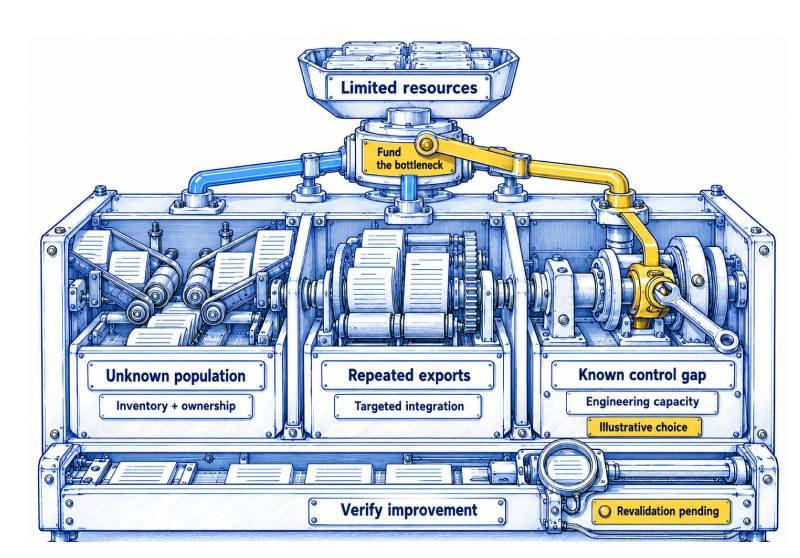
Make limited security budgets count by focusing on critical services, reliable evidence and accountable action. Learn how mid-market teams can identify control gaps and decide where better data, expertise, automation...

Categories: Governance

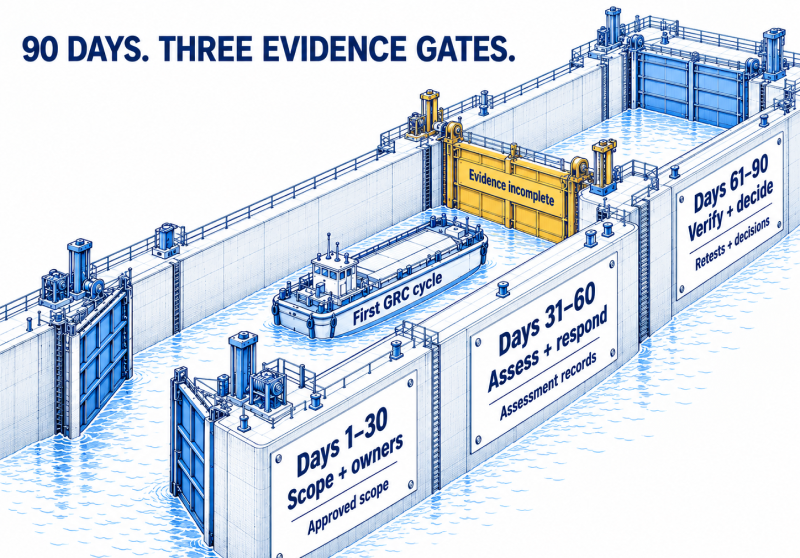
A 90-Day GRC Roadmap: From Scope and Ownership to Verified Controls Across Teams

A 90-Day GRC Roadmap: From Scope and Ownership to Verified Controls Across Teams

Establish a first GRC voyage in 90 days, with clear scope, accountable owners and evidence that supports control decisions. Follow three practical phases to assess priority controls, verify remediation and...

Categories: GRC

GRC Maturity That Holds Up Under Change: Align Evidence, Ownership and Decisions

GRC Maturity That Holds Up Under Change: Align Evidence, Ownership and Decisions

Help lean GRC teams support growing compliance demands with clear ownership, reliable evidence and selective automation. Reduce repeated follow-up, keep exceptions visible and verify remediation while measuring whether the team...

Categories: GRC

ISO 27001 Certification in 2026: Readiness, Audit Evidence and What Happens Next

ISO 27001 Certification in 2026: Readiness, Audit Evidence and What Happens Next

Prepare for ISO 27001 certification with a clear scope, traceable evidence and accountable control owners. Understand the audit stages, timeline and cost factors, and what it takes to maintain your...

Categories: ISO 27001

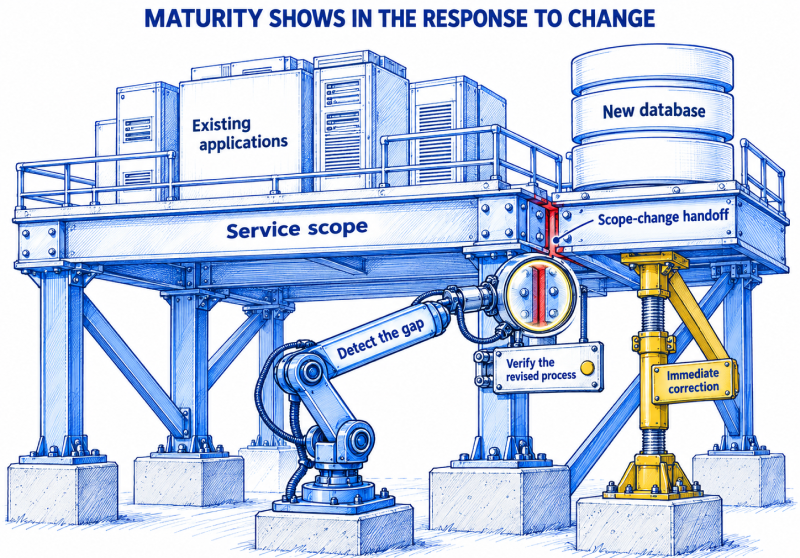
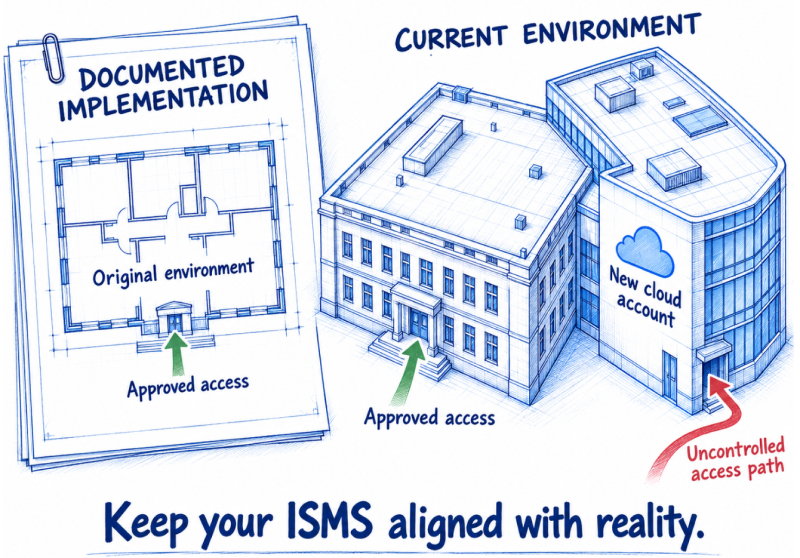
ISO 27001 in 2026: Keep Controls Aligned as Business Changes

ISO 27001 in 2026: Keep Controls Aligned as Business Changes

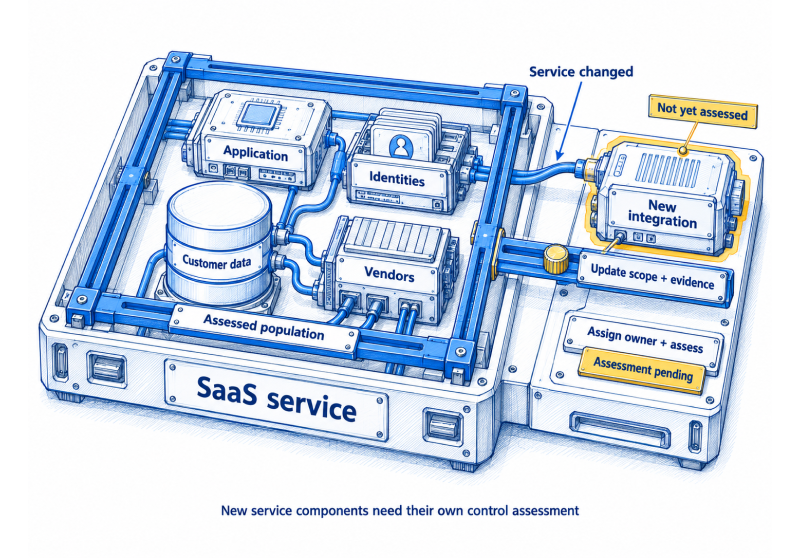
An effective ISO 27001 program keeps control scope, the Statement of Applicability and supporting evidence aligned as services, identities and suppliers change. Clear ownership, checks on coverage and effectiveness, and...

Categories: ISO 27001

ISO 27001 Change Management: From Approval to Verified Outcome

ISO 27001 Change Management: From Approval to Verified Outcome

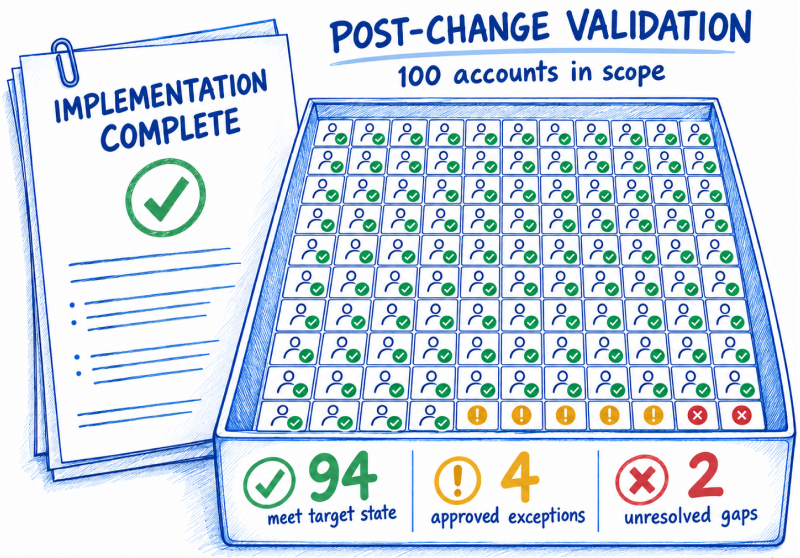
An approved change can still leave a security control in the wrong state. Connect ISO 27001 change management with post-change validation to verify control outcomes, resolve gaps and retain evidence...

Categories: ISO 27001

IT GRC: Keep Accountability Intact When Technology Changes

IT GRC: Keep Accountability Intact When Technology Changes

IT governance, risk management, and compliance (IT GRC) should help a CISO answer a difficult operational question: when technology changes, do the business's risk decisions and control assurances still hold?...

Categories: GRC

Compliance Monitoring in 2026: Detect Evidence Gaps and Verify Control Results

Compliance Monitoring in 2026: Detect Evidence Gaps and Verify Control Results

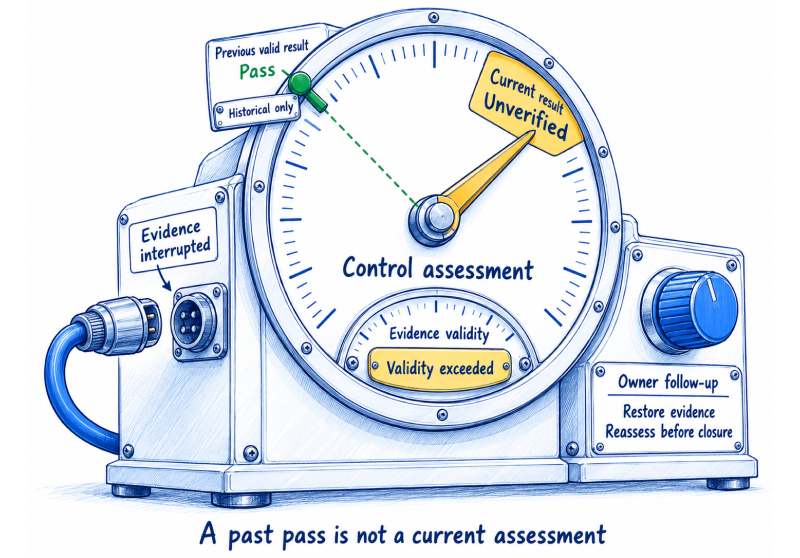
Compliance Monitoring in 2026: Detect Evidence Gaps and Verify Control Results A passing result is only useful when its coverage, evidence and test remain valid. Learn how to distinguish control...

Categories: Compliance

SaaS Compliance in 2026: A Checklist for Control Ownership and Clear Evidence

SaaS Compliance in 2026: A Checklist for Control Ownership and Clear Evidence

Build a SaaS compliance program around the services you deliver and the obligations that apply. Use this practical checklist to clarify cloud responsibilities, assign control owners and verify evidence as...

Categories: Compliance, GRC

Backup Checklist in 2026: Verify Recovery for Security and Compliance Teams

Backup Checklist in 2026: Verify Recovery for Security and Compliance Teams

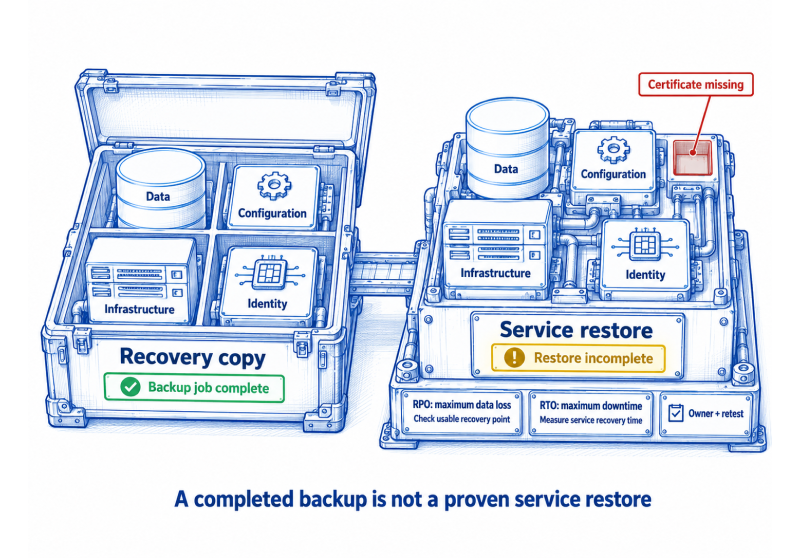
A successful backup job does not prove that a service can be restored. Use this checklist to define recovery coverage, set RPO and RTO targets, protect recovery copies and verify...

Categories: Compliance, Cyber Risk, Risk Management
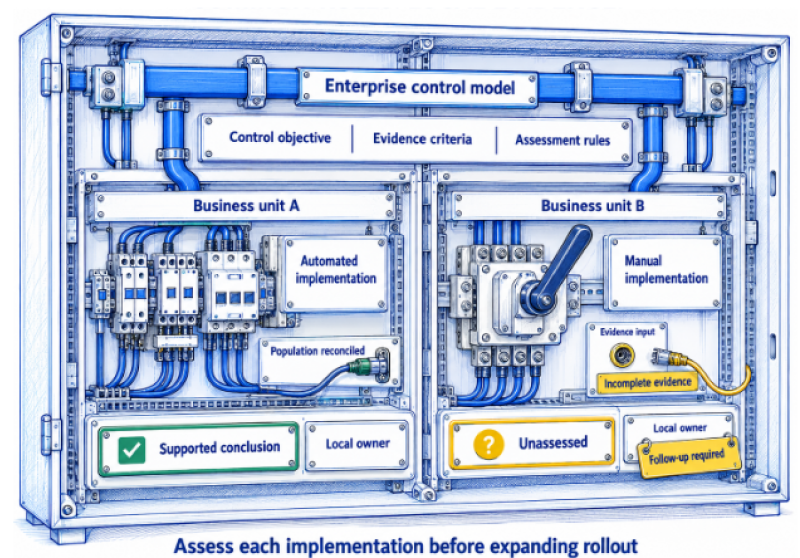
How to Roll Out Enterprise GRC: Prove the Model Before You Scale

How to Roll Out Enterprise GRC: Prove the Model Before You Scale

Enterprise GRC needs consistent assessments across business units while preserving local responsibilities and obligations. Establish clear ownership, reliable evidence and a complete pilot control cycle before expanding, so each rollout...

Categories: Compliance, GRC, Risk Management
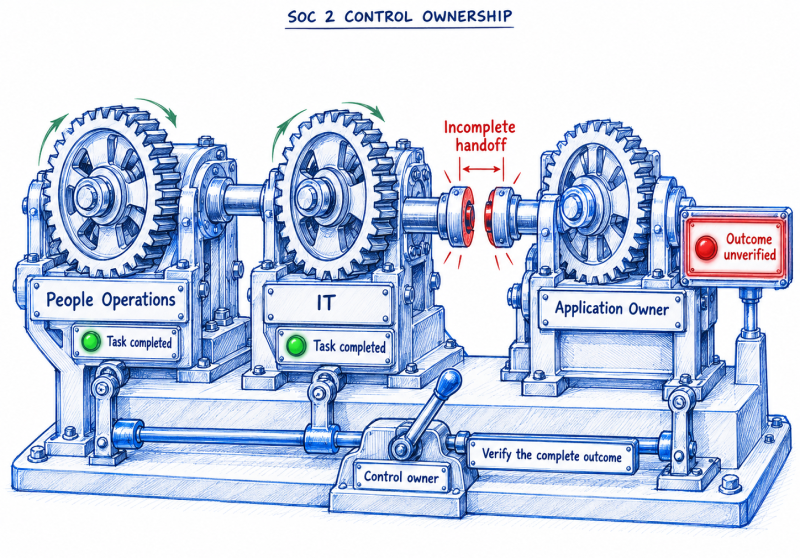
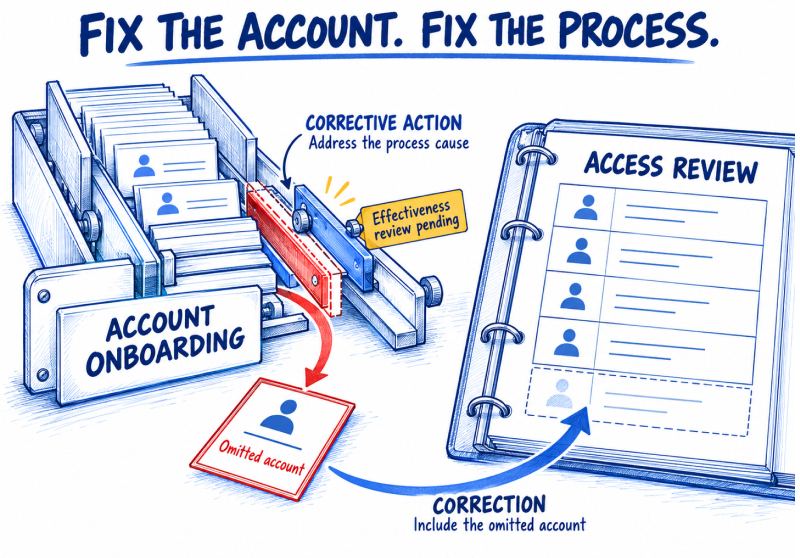
SOC 2 Control Ownership: Define Clear Roles and Validate Evidence Without a CISO

SOC 2 Control Ownership: Define Clear Roles and Validate Evidence Without a CISO

Build a practical SOC 2 control list with clear owners, reliable evidence and complete handoffs across teams. Learn how to manage responsibilities without a CISO, address missed controls and verify...

Categories: Compliance, GRC

ISO Security Standards in 2026: Which Ones Matter for Your Organization?

ISO Security Standards in 2026: Which Ones Matter for Your Organization?

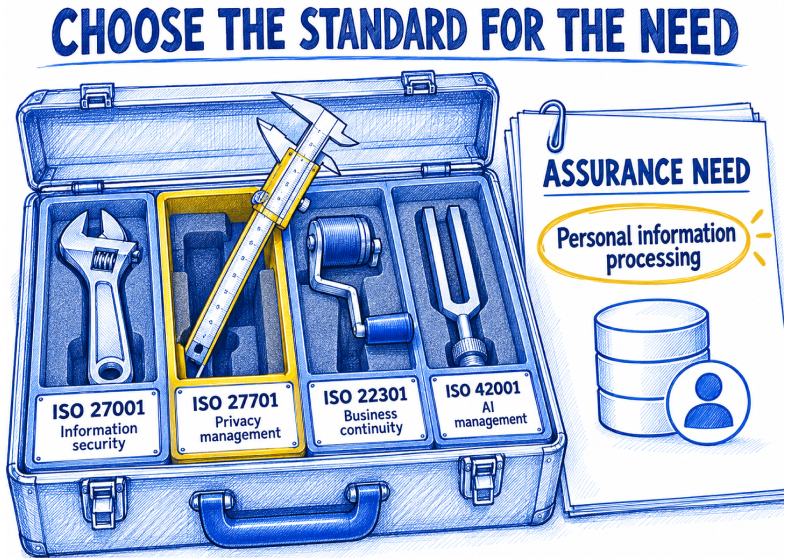
Choose ISO security standards based on your business needs, responsibilities and the assurance stakeholders expect. Compare security, privacy, cloud, continuity and AI standards, and understand where certification, guidance and shared...

Categories: Compliance, GRC, ISO 27001
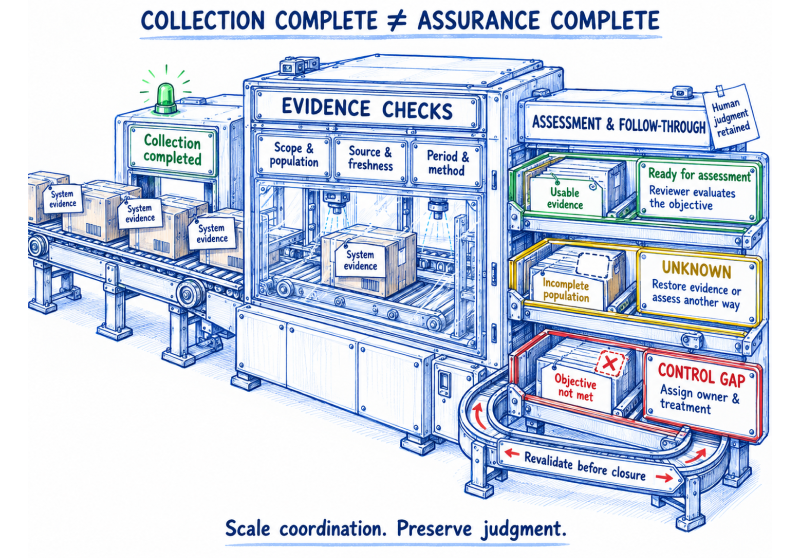
How Lean GRC Teams Can Scale Compliance Without Adding Headcount

How Lean GRC Teams Can Scale Compliance Without Adding Headcount

Help lean GRC teams support growing compliance demands with clear ownership, reliable evidence and selective automation. Reduce repeated follow-up, keep exceptions visible and verify remediation while measuring whether the team...

Categories: GRC

CBUAE Cybersecurity Compliance Checklist 2026: 10 Things CISOs Should Do Now

CBUAE Cybersecurity Compliance Checklist 2026: 10 Things CISOs Should Do Now

The Central Bank of the UAE (CBUAE) Operational Risk Management Regulation C 1/2026, effective from 14 September 2026, introduces important ICT and cybersecurity requirements for Licensed Financial Institutions. It requires...

Categories: CBUAE

What Is Continuous Assurance in Cybersecurity?

What Is Continuous Assurance in Cybersecurity?

Organizations invest heavily in security tools, compliance programs, and risk management processes. Yet many security leaders still struggle to answer a simple question: How do we know our controls are...

Categories: Cybersecurity

Why Compliance Doesn’t Equal Resilience

Why Compliance Doesn’t Equal Resilience

Introduction — When the Cloud Shakes, Compliance Crumbles When AWS’s US-east-1 region went dark, so did thousands of companies. These weren’t reckless startups or poorly managed systems; they were organizations...

Categories: Compliance

Understanding RBI’s FREE-AI Framework – India’s Blueprint for Ethical AI Governance

Understanding RBI’s FREE-AI Framework – India’s Blueprint for Ethical AI Governance

Introduction There are two sides to a coin and AI is no exception. AI’s versatility is what makes it useful across a vast array of use cases. And yet, it...

Categories: AI

DPDP Act & Rules 2025: The Compliance Readiness Checklist 

DPDP Act & Rules 2025: The Compliance Readiness Checklist 

As India accelerates toward becoming a digital-first economy, regulatory frameworks are increasingly shaping how enterprises manage data, AI, and security operations. At the heart of this transformation lies the Digital...

Categories: Compliance

Why Has Risk Management Become Process Theater and How Do We Fix It?

Why Has Risk Management Become Process Theater and How Do We Fix It?

Introduction — The Performance of Protection In too many organizations, risk management has become a performance rather than a practice. Every quarter, teams scramble to refresh risk registers, hold a...

Categories: Risk Management

Automating Security Questionnaires: How to Streamline Third-Party Risk Assessments

Automating Security Questionnaires: How to Streamline Third-Party Risk Assessments

Third-party vendors play a critical role in modern business operations, but they also expand exposure to unpredictable risks. These risks often do not come under the enterprise purview and hence...

Categories: Cloud Security

Unifying Remediation and Compliance with Integrated Incident Response

Unifying Remediation and Compliance with Integrated Incident Response

When it comes to responding to incidents, time is of the essence. The first few minutes often bring chaos—analysts must quickly switch between tools, evaluate the scope of impact, and...

Categories: Compliance

The Rise of Adversarial AI Attacks & AI Security Best Practices to Stop them

The Rise of Adversarial AI Attacks & AI Security Best Practices to Stop them

It’s an undeniable fact that organizations of all sizes and industries have adopted AI at a colossal scale. While AI is revolutionizing how businesses operate, it also poses major challenges...

Categories: AI

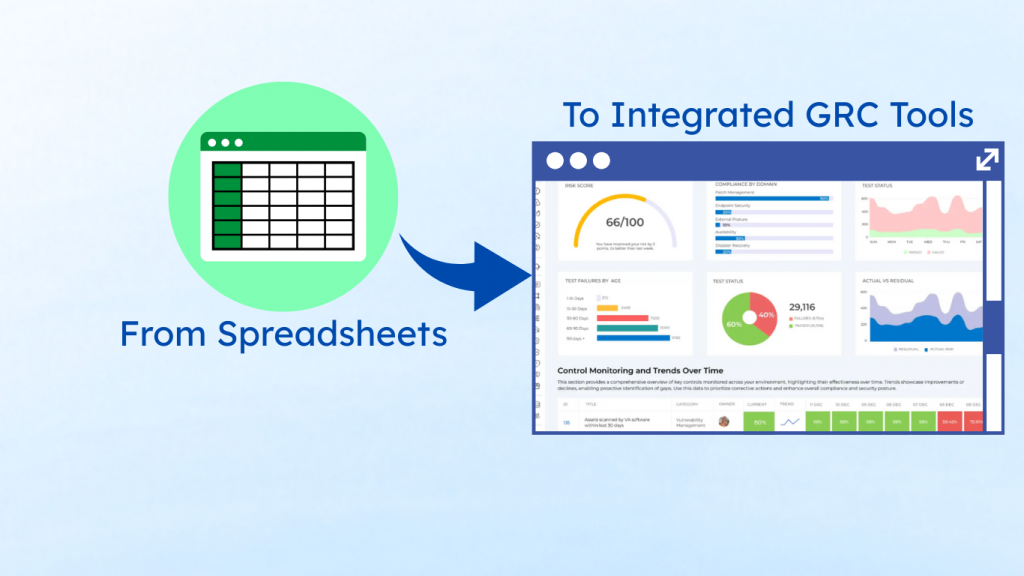
5 Reasons You Need to Move from Spreadsheets to GRC Tools for Compliance Management

5 Reasons You Need to Move from Spreadsheets to GRC Tools for Compliance Management

For years, spreadsheets have been the go-to tool for managing governance, risk, and compliance (GRC). They’re familiar, easy to set up, and cost nothing more than a license most businesses...

Categories: GRC

The Definitive Guide to Automated Controls Testing

The Definitive Guide to Automated Controls Testing

Every 39 seconds, a cyberattack strikes somewhere in the world (University of Maryland). At the same time, regulators are tightening rules across industries, from finance to healthcare. Leaders can no...

Categories: Cybersecurity

Turning Risk Registers from Static Records into Living Intelligence

Turning Risk Registers from Static Records into Living Intelligence

For years, the risk register has been a key tool in governance, risk, and compliance (GRC) programs. But in most organizations, it still sits in spreadsheets or static forms that...

Categories: Risk Management

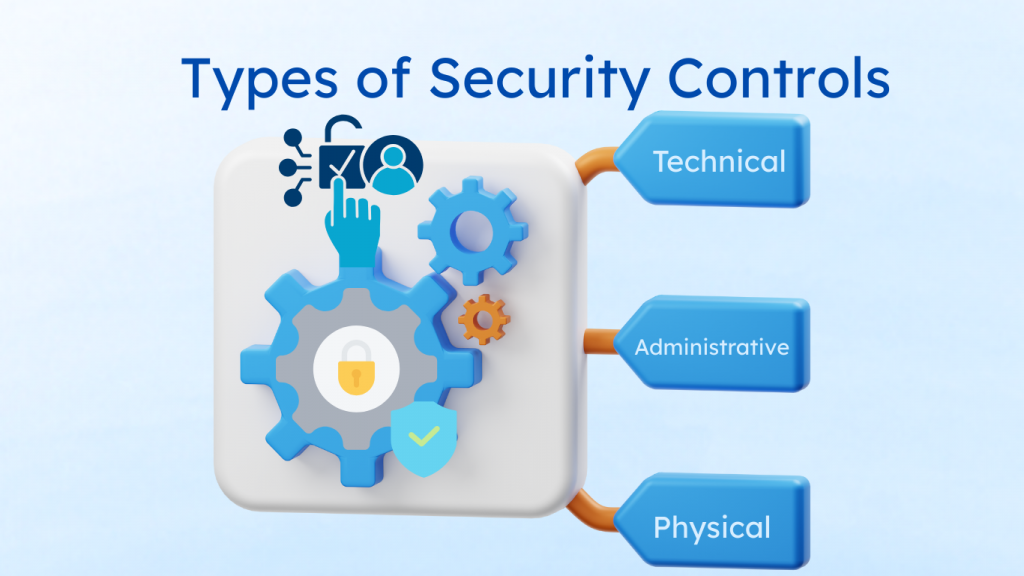
Understanding the Different Types of Security Controls (and Why They Matter)

Understanding the Different Types of Security Controls (and Why They Matter)

Security controls come in many forms and levels of complexity. Organizations implement them based on their own risks, needs, and processes. But is it enough to set them up once...

Categories: Cyber Risk

The Evolution of PCI DSS: From v3.2.1 to v4.0

The Evolution of PCI DSS: From v3.2.1 to v4.0

The Payment Card Industry Data Security Standard (PCI DSS) has long served as the global benchmark for safeguarding cardholder data and reducing the risk of breaches. First introduced in 2004,...

Categories: Governance

Third-Party Risk Metrics: How to Track and Report

Third-Party Risk Metrics: How to Track and Report

Third-party data breaches are more commonplace than ever. The majority of high-stakes data breaches in recent years have been caused by one missing link in the vendor management workflow. Take...

Categories: Risk Management

Setting Up a GDPR Compliance Monitoring and Audit Program: Steps and Checklist

Setting Up a GDPR Compliance Monitoring and Audit Program: Steps and Checklist

Achieving GDPR compliance is only the beginning, maintaining it is the real challenge. The General Data Protection Regulation (GDPR) demands that organizations not only put privacy controls in place but...

Categories: Compliance

How Cybersecurity Asset Management Improves Risk-Based Alerting and Threat Response

How Cybersecurity Asset Management Improves Risk-Based Alerting and Threat Response

Too often, security tools treat all assets as equal. A critical alert on a decommissioned test server carries the same weight as one on a core financial system. A suspicious...

Categories: Cybersecurity

Automated Access Reviews: Strengthening Security, Simplifying Compliance

Automated Access Reviews: Strengthening Security, Simplifying Compliance

Access reviews play a key role in meeting security and regulatory standards. But many companies still handle them manually, creating risk and complexity. According to The State of Access Review...

Categories: Compliance

CERT-In’s 2025 Cyber Audit Policy: What It Means for India’s Security Ecosystem

CERT-In’s 2025 Cyber Audit Policy: What It Means for India’s Security Ecosystem

On July 25, 2025, the Indian Computer Emergency Response Team (CERT-In) launched a major update to its cybersecurity audit guidelines. These new rules aim to move India’s security posture from...

Categories: Governance

Silent Threats, Loud Consequences: Why Most Breaches Start with a Missed Signal

Silent Threats, Loud Consequences: Why Most Breaches Start with a Missed Signal

Introduction: The Breach That Wasn’t Loud — Until It Was The most dangerous breaches often don’t begin with a bang.They start with a blink—missed, ignored, or filed away for “later.”...

Categories: Cybersecurity

From CMDB to Risk Engine: Turning Asset Data into Security Decision

From CMDB to Risk Engine: Turning Asset Data into Security Decision

In May 2024, one of the most significant cloud breaches in recent memory made headlines: attackers infiltrated over 160 customer environments in the Snowflake ecosystem, affecting companies like AT&T and...

Categories: Cyber Risk

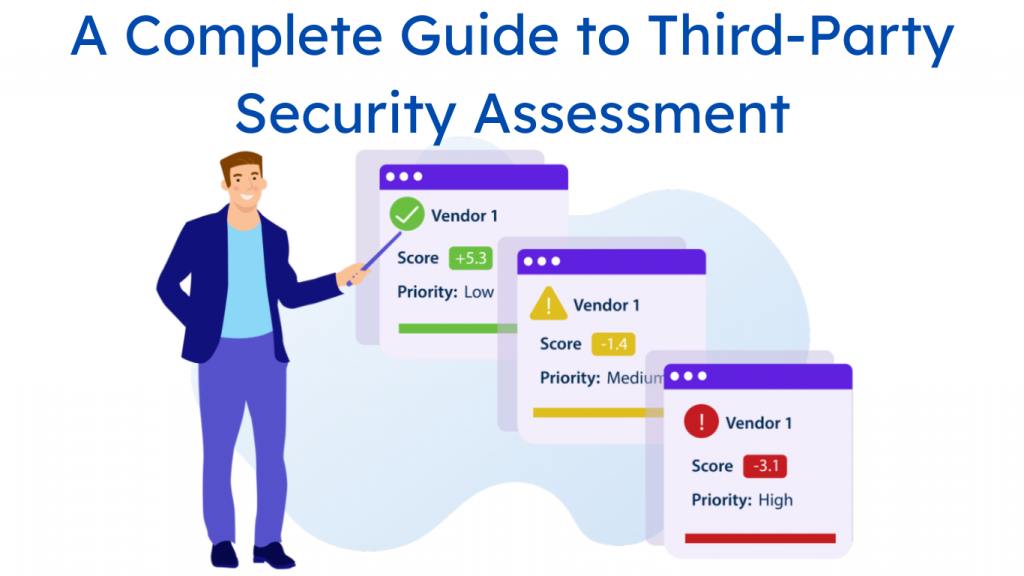
A Complete Guide to Third-Party Security Assessment

A Complete Guide to Third-Party Security Assessment

Third-party data breaches are on the rise.  Attackers increasingly target vendors, contractors, and SaaS providers; not just because they’re easier to breach, but because they often have direct access to...

Categories: Cyber Risk

Is Your Security Stack Missing True Visibility?

Is Your Security Stack Missing True Visibility?

You’ve invested in top-tier tools—firewalls, SIEMs, XDRs, MDRs, and real-time threat intel feeds. On paper, your security stack looks solid. You’ve done everything right. But tools only work if they...

Categories: Cyber Risk

Combating Alert Fatigue for SOC Teams with Impact-Based Risk Prioritization

Combating Alert Fatigue for SOC Teams with Impact-Based Risk Prioritization

Security Operations Centers (SOCs) protect modern businesses from cyber threats. But instead of battling a lack of information, SOC teams often drown in it. Every day, analysts face thousands of...

Categories: Cyber Risk

Connecting Risk and Remediation with Integrated Incident Response

Connecting Risk and Remediation with Integrated Incident Response

In 2023, attackers exploited a known vulnerability in MOVEit Transfer—a popular file transfer tool used by governments, banks, and large enterprises. Even after the vulnerability became public, many organizations failed...

Categories: Risk Management

Are You Boardroom-Ready? A CISO’s Guide to Cyber Risk Quantification and Security Maturity Assessment

Are You Boardroom-Ready? A CISO’s Guide to Cyber Risk Quantification and Security Maturity Assessment

Introduction: Why “Boardroom-Ready” Matters More Than Ever Not long ago, cybersecurity was seen as a technical silo—an IT function buried deep in the infrastructure, discussed mainly in jargon and dashboards...

Categories: Cyber Risk

Top 10 Early Warning Signs of Insider Threats Every Company Should Know

Top 10 Early Warning Signs of Insider Threats Every Company Should Know

Insider threats are one of the most underestimated cybersecurity risks facing organizations today. While companies often focus on defending against external attackers, the real danger might be operating quietly from...

Categories: Cybersecurity

Modernizing Third-Party Risk Management with Continuous Monitoring

Modernizing Third-Party Risk Management with Continuous Monitoring

Introduction: The Evolution of Third-Party Risk Management Businesses today rely on third-party vendors for everything from cloud services to data processing. These partners enable scale and speed—but also open the...

Categories: Risk Management

The Complete Guide to Data Center Security and Compliance (with an actionable checklist)

The Complete Guide to Data Center Security and Compliance (with an actionable checklist)

Hybrid data centers have become the backbone of modern enterprise IT. These environments integrate on-premises infrastructure with public and private cloud platforms, offering agility, control, and performance. But as architecture...

Categories: Compliance

What is a Risk and Controls Matrix? A Beginner’s Guide

What is a Risk and Controls Matrix? A Beginner’s Guide

Every organization, big or small, faces uncertainty. It could be a data breach waiting to happen, a missed regulatory deadline, or risks that emerge from a third-party vendor. The hard...

Categories: Risk Management

Designing a Comprehensive Risk Mitigation Strategy: From Assessment to Action

Designing a Comprehensive Risk Mitigation Strategy: From Assessment to Action

In February 2023, Karmak, a leading business software provider in the trucking industry, was hit by a ransomware attack. Thanks to a well-prepared incident response plan, the company acted fast....

Categories: Cyber Risk

Cyber Risk in Banking: Evolving Threats and Adaptive Risk Management

Cyber Risk in Banking: Evolving Threats and Adaptive Risk Management

Banks today work in a fast-moving, always-connected digital world. With every new API, cloud platform, third-party service, remote employee, or customer-facing app, they expand their digital presence, and their exposure...

Categories: Cyber Risk

GRC Automation for Hybrid Infrastructure

GRC Automation for Hybrid Infrastructure

Most companies today aren’t operating in just one environment. They’ve got systems running in the cloud, some in private data centers, and often a good chunk still sitting on on-premises...

Categories: GRC

Cyber Risk Management Goals for a Zero-Trust World

Cyber Risk Management Goals for a Zero-Trust World

As cyber threats grow in sophistication and scale, traditional security models that once protected corporate networks are no longer sufficient. Businesses today face ransomware attacks, insider threats, supply chain compromises,...

Categories: Cyber Risk

The GRC Metrics That Actually Matter

The GRC Metrics That Actually Matter

Governance, Risk, and Compliance (GRC) functions have evolved from reactive compliance checkpoints into proactive strategic enablers. However, this evolution brings a new challenge—how do you prove the value of GRC...

Categories: GRC

How to Prepare for a SOC 2 Type II Audit in Half the Time

How to Prepare for a SOC 2 Type II Audit in Half the Time

83% of enterprise buyers require SOC 2 compliance before vendor onboarding—making it not just a regulatory checkbox, but a mission-critical enabler of business growth and a gatekeeper for market access....

Categories: Compliance

What to Include in a High-Impact Compliance Report (With Examples)

What to Include in a High-Impact Compliance Report (With Examples)

Think of a compliance report like a routine health check-up for your organization. It might not be the most exciting appointment on the calendar, but it’s essential. Just as a...

Categories: Compliance

10 Common Gaps in Enterprise Risk Assessments—and How to Close Them

10 Common Gaps in Enterprise Risk Assessments—and How to Close Them

Many organizations treat risk assessments as annual checklists, missing the dynamic threats that truly matter. This guide dives into the top 10 gaps that weaken enterprise risk assessments—from inconsistent scoring...

Categories: Risk Management

GRC Platform Selection Guide: What to Look for Based on Your Maturity Level

GRC Platform Selection Guide: What to Look for Based on Your Maturity Level

The GRC (Governance, Risk, and Compliance) technology landscape is vast. It touches nearly every part of a company’s operations—from policy management and control alignment to risk tracking and data classification....

Categories: GRC

Cyber Security Regulatory Compliance in India: What You Need to Know

Cyber Security Regulatory Compliance in India: What You Need to Know

Introduction: When Compliance Blocks Market Entry Sometimes, a region’s regulatory compliance rules block businesses from entering a market. That’s exactly what happened with WhatsApp Pay in India. Despite having hundreds...

Categories: Cybersecurity, Governance

Cybersecurity Risk Assessment in Banking: A Strategic Guide with Risk Matrix Templates

Cybersecurity Risk Assessment in Banking: A Strategic Guide with Risk Matrix Templates

Banks today operate in a high-stakes environment, managing sensitive financial data, digital customer interactions, and a growing portfolio of online services. These innovations, while necessary, have dramatically increased their exposure...

Categories: Cybersecurity

The Need for Hybrid GRC Integrations

The Need for Hybrid GRC Integrations

“Just connect the API.” It’s something that we commonly hear in GRC automation—and one of the least useful if you're dealing with legacy systems. Many Governance, Risk, and Compliance (GRC)...

Categories: GRC

Risk Management vs Compliance Management: Which Should Be Your Priority?

Risk Management vs Compliance Management: Which Should Be Your Priority?

Stuck Between Risk and Compliance? That’s the Real Risk. Discover why treating them as rivals is holding your organization back—and how smart teams use both to fuel resilience and agility....

Categories: Risk Management

How Compliance Fatigue Undermines Security

How Compliance Fatigue Undermines Security

Compliance fatigue is real—and it’s putting your security at risk.When checklists replace critical thinking, organizations become vulnerable. Learn how to move beyond box-ticking and build a security culture that stays...

Categories: Compliance

Moving Beyond Static Risk Management Frameworks to Continuous Control Monitoring

Moving Beyond Static Risk Management Frameworks to Continuous Control Monitoring

In the Banking, Financial Services, and Insurance (BFSI) sector, many organizations still rely on traditional risk management frameworks like the Three Lines of Defense (3LOD). These models worked well in...

Categories: CCM

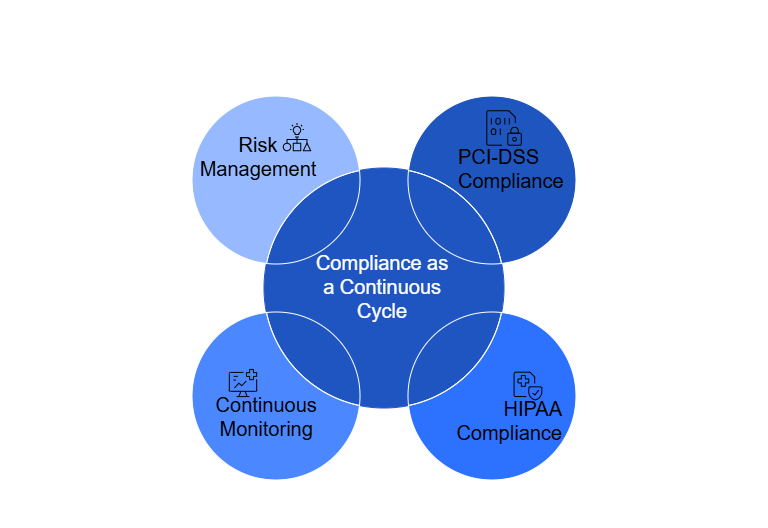
Compliance as a Continuous Cycle: Maintaining PCI-DSS, HIPAA, & More

Compliance as a Continuous Cycle: Maintaining PCI-DSS, HIPAA, & More

Compliance isn't just about meeting regulatory requirements; it's about safeguarding your organization from risks that can cost millions. Yet, many companies still approach compliance as a one-time project, leaving them...

Categories: Governance

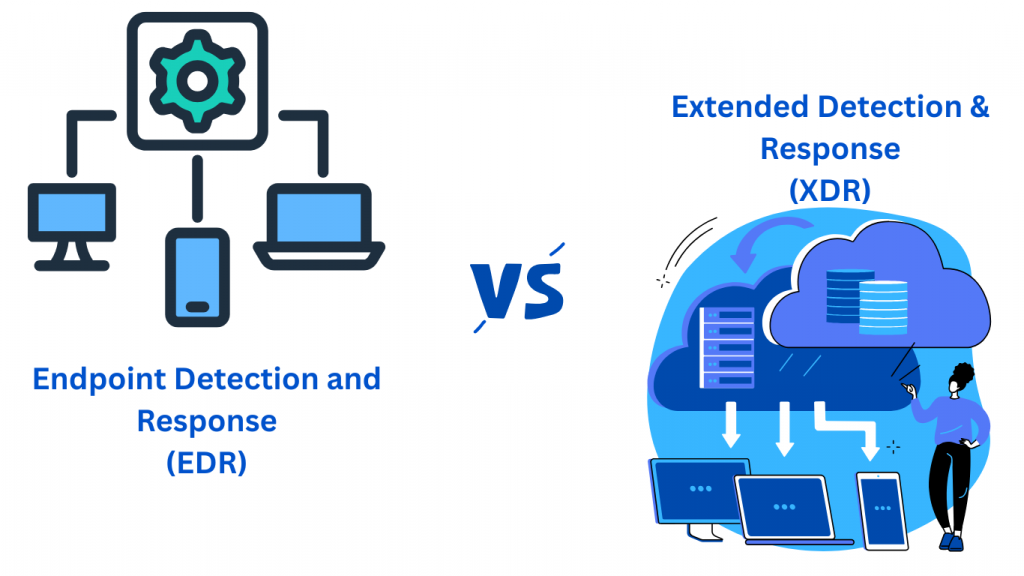
From EDR to XDR: Evaluating Tool Efficacy in Risk Assessments

From EDR to XDR: Evaluating Tool Efficacy in Risk Assessments

Cyber threats are faster, stealthier, and more coordinated than ever — and your tools need to keep up. This article dives into the real difference between EDR and XDR, how...

Categories: Risk Management

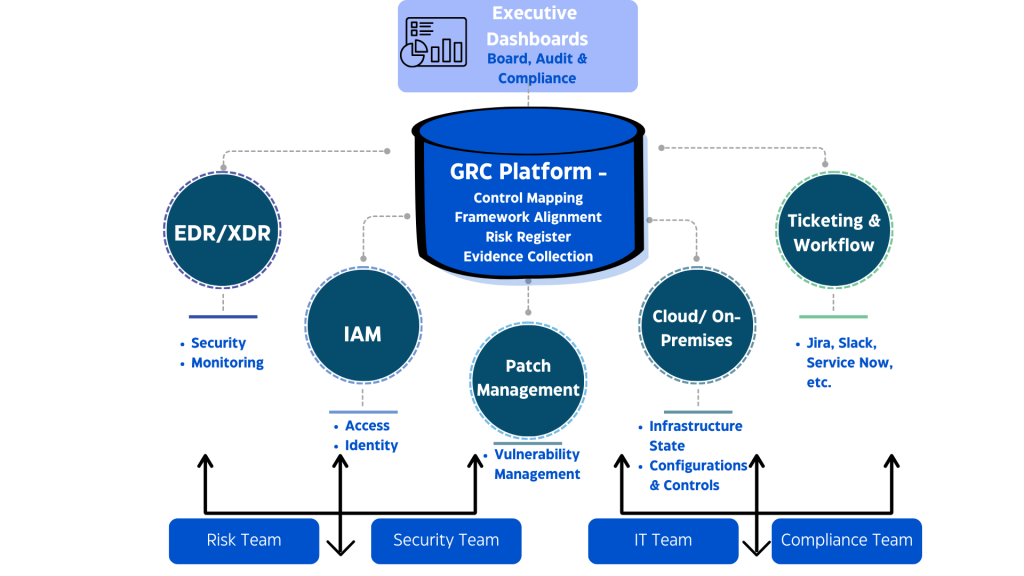
The Tech Stack for Ongoing Compliance: Integrations that Matter

The Tech Stack for Ongoing Compliance: Integrations that Matter

Your team ships code every day. But your audit still runs once a year. In between, things break. Evidence gets lost. Risk data lives in ten different places. Most companies...

Categories: Compliance

Building a Risk-Aware Culture: The Human Element in Security

Building a Risk-Aware Culture: The Human Element in Security

Protection starts with people. And, if you have not recognized this yet, you are overlooking the human element in security. In fact, humans are the weakest link in security, not...

Categories: Cyber Risk

Navigating Multiple Frameworks: ISO 27001, SOC 2, GDPR, and Beyond

Navigating Multiple Frameworks: ISO 27001, SOC 2, GDPR, and Beyond

Imagine trying to find your way through a maze where many paths look the same, but each has different rules. Organizations face this challenge when complying with multiple security and...

Categories: Compliance

Quantifying Cyber Threats: Advanced Techniques for Risk Identification

Quantifying Cyber Threats: Advanced Techniques for Risk Identification

This article explores the best ways to identify and manage cyber risks. By using techniques like scenario modeling, machine learning analytics, and threat correlation, companies can turn cybersecurity into a...

Categories: Cyber Risk

The ROI of Real-Time Compliance: Cost Savings and Risk Reduction

The ROI of Real-Time Compliance: Cost Savings and Risk Reduction

Ignoring compliance is not just a legal risk. It is a financial mistake. But there is a better way. Let’s dive into it! Many companies see compliance as a burden....

Categories: Compliance

Conducting a Holistic Risk Audit: Key Steps & Best Practices

Conducting a Holistic Risk Audit: Key Steps & Best Practices

Most organizations approach risk audits the way they approach an annual health check-up—routine, compliance-driven, and often surface-level. If nothing appears broken, it’s business as usual. But just as hidden health...

Categories: Risk Management

Continuous Compliance Demystified: From Checklists to Real-Time Insights

Continuous Compliance Demystified: From Checklists to Real-Time Insights

Did you know that nearly 67% of businesses reported an increase in data privacy violations in 2024 compared to the previous year?. That's a clear sign that traditional compliance methods...

Categories: Compliance

Measuring Organizational Risk Maturity: An In-Depth Framework Overview

Measuring Organizational Risk Maturity: An In-Depth Framework Overview

Cyber threats aren’t slowing down. Every day, security teams are fighting fires, trying to keep up with evolving risks, compliance demands, and resource constraints. But here’s the question: Do you...

Categories: Risk Management

Top 10 Vulnerability Management Metrics you need to be tracking

Top 10 Vulnerability Management Metrics you need to be tracking

Every CISO and cybersecurity leader faces the same challenge. You invest in advanced vulnerability management (VM) tools, run regular scans, and patch the critical vulnerabilities your system detects. On paper,...

Categories: Cyber Risk

SEBI CSCRF: The Ultimate Guide for SEBI-Regulated Entities

SEBI CSCRF: The Ultimate Guide for SEBI-Regulated Entities

Cyber threats are rising, and SEBI’s Cybersecurity and Cyber Resilience Framework (CSCRF) sets strict mandates to protect financial entities. With a March 31, 2025 deadline, firms must act now to...

Categories: Compliance

GRC Silos Cost More Than You Think – Here’s Why

GRC Silos Cost More Than You Think – Here’s Why

Governance, Risk, and Compliance (GRC) functions often operate in silos, leading to inefficiencies, higher costs, and increased regulatory risks. Disjointed processes create blind spots, delay incident response, and make compliance...

Categories: GRC

AI Compliance Frameworks: Why They Matter and What You Need to Know

AI Compliance Frameworks: Why They Matter and What You Need to Know

With AI transforming industries at an unprecedented pace, the risks of bias, privacy violations, and regulatory non-compliance are skyrocketing. Global regulations like the EU AI Act, NIST AI RMF, ISO/IEC...

Categories: Compliance

ISO 27001:2022 Update – Are You Ready for the New Compliance Requirements?

ISO 27001:2022 Update – Are You Ready for the New Compliance Requirements?

The latest ISO 27001:2022 update brings critical changes to information security, risk management, and compliance requirements. With a stronger focus on cyber resilience, supply chain security, and evolving threats, organizations...

Categories: ISO 27001