Featured
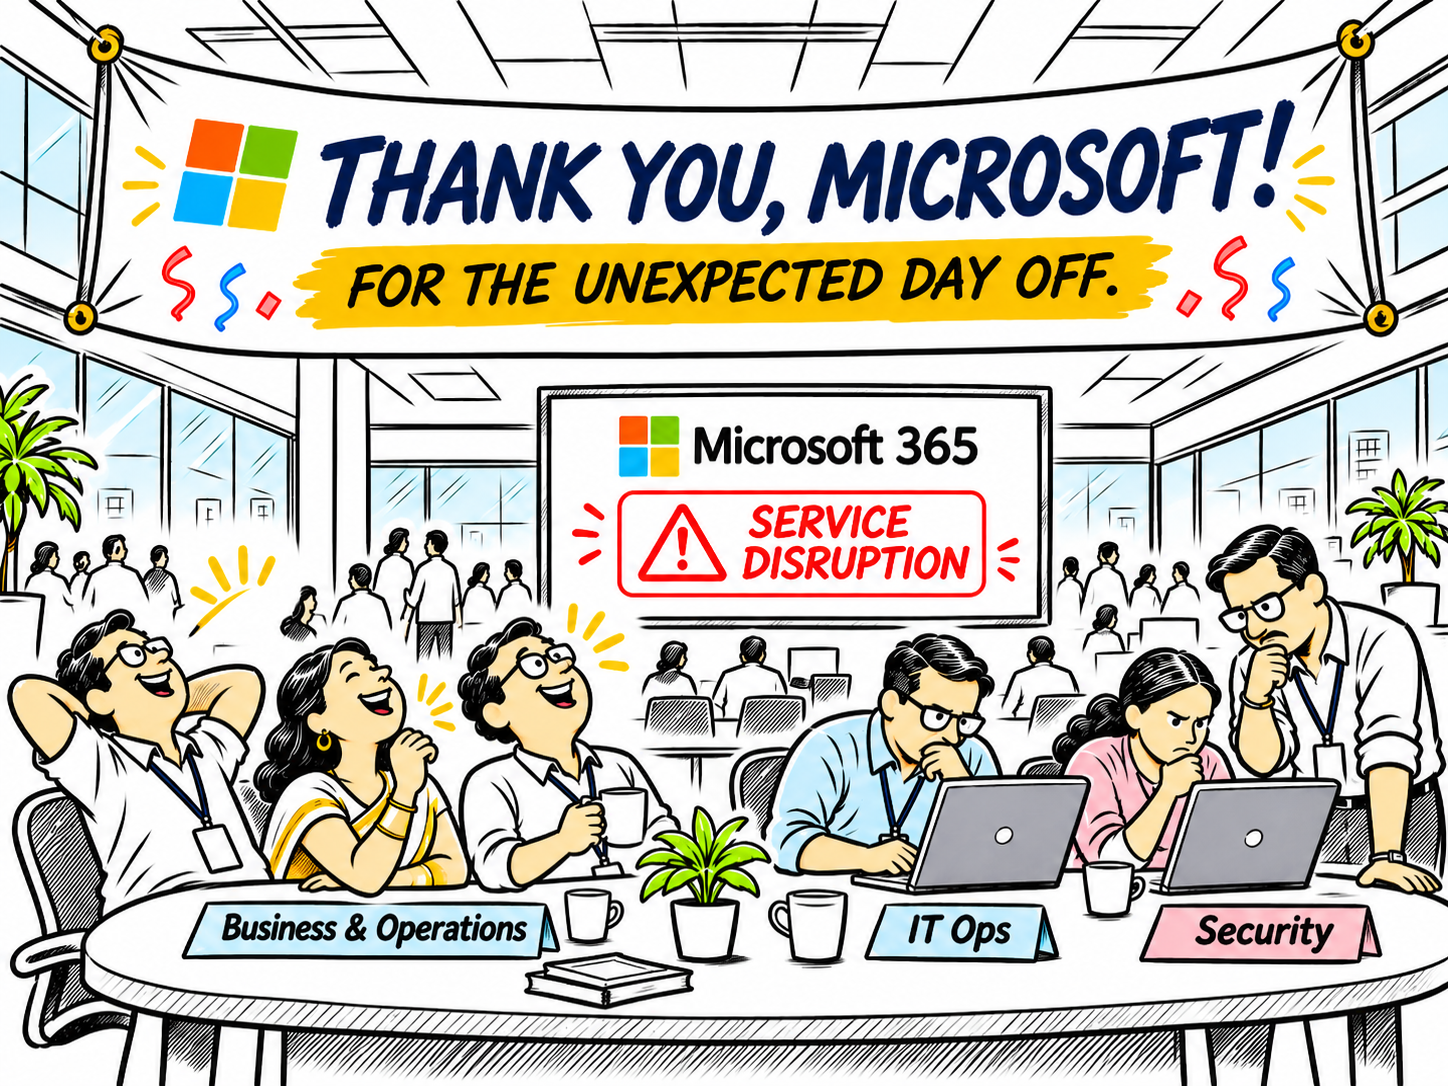
Microsoft 365 Outage: The Hidden Risks You Overlooked

The Microsoft 365 outage exposed hidden risks in disaster recovery, third-party dependencies and cloud concentration revealing why operational resilience requires more than infrastructure availability. On November 12–13, 2026, Microsoft 365 experienced a significant service disruption, affecting a platform widely used by enterprises for communication and collaboration. Beyond service availability, the outage exposed a more fundamental question: How well do organizations understand their dependencies on critical technology...
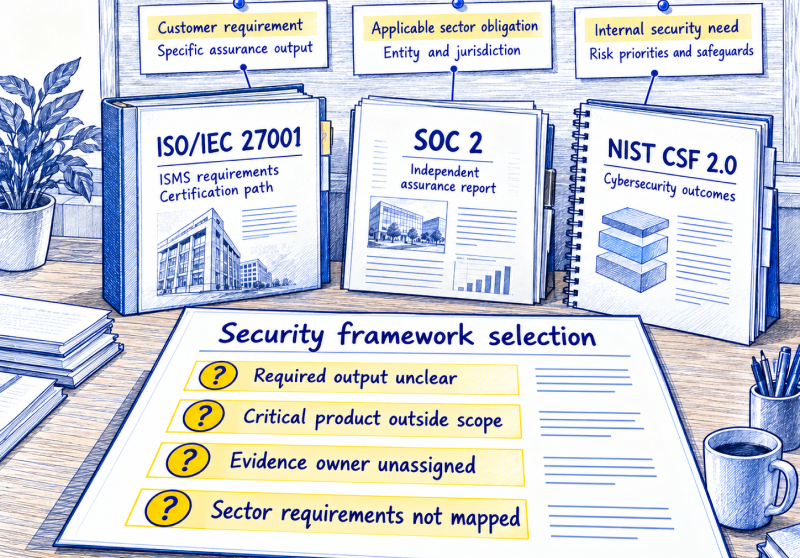
Choosing a Security Framework for Risk, Compliance, and Business Needs

A security framework helps organizations structure cybersecurity priorities, but selecting the right approach depends on business risks, applicable obligations and stakeholder expectations. Clear scope, accountable owners and suitable evidence make...
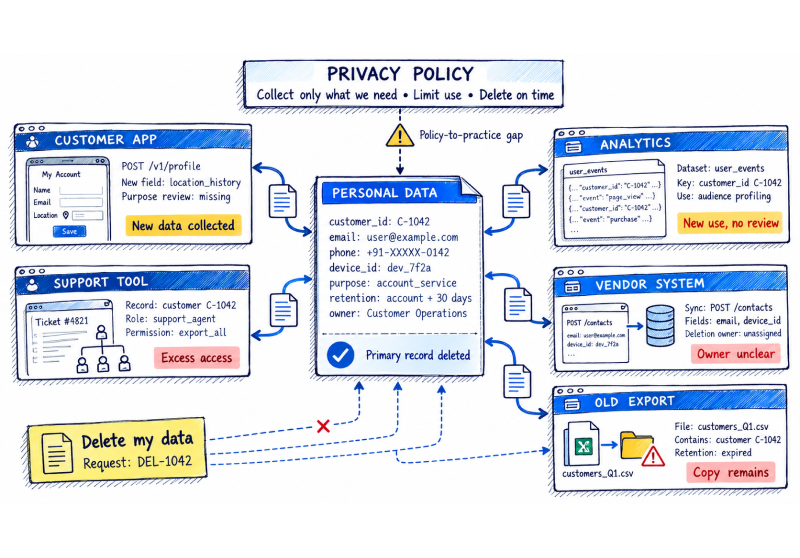
Data Privacy Compliance: Put Personal Data Controls Into Daily Practice at Scale

Data privacy compliance depends on whether stated purposes, actual data use and safeguards stay aligned as products and systems change. Trace each activity through access, rights requests, retention and deletion,...
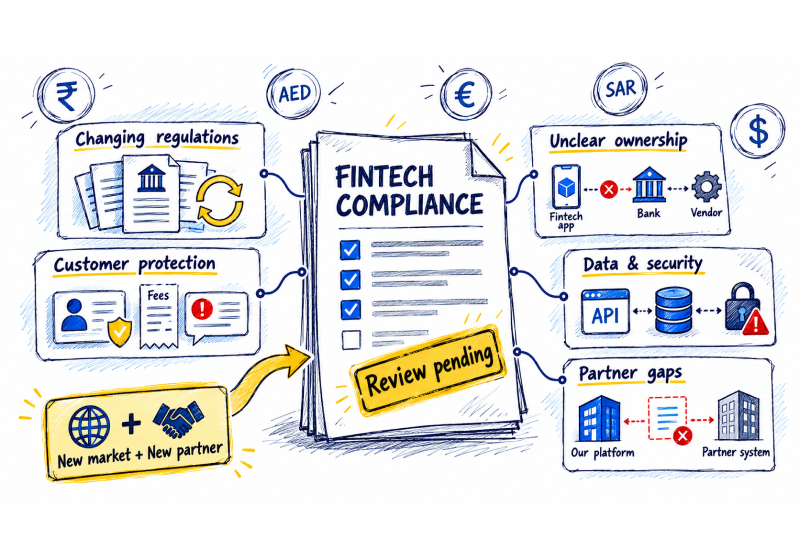
Fintech Compliance: A Practical Model for Regulated Digital Finance Operations
Fintech compliance depends on what a product does, which entities deliver it, and where customers, money, and data move. Mapping obligations across customer journeys clarifies control ownership and partner responsibilities....
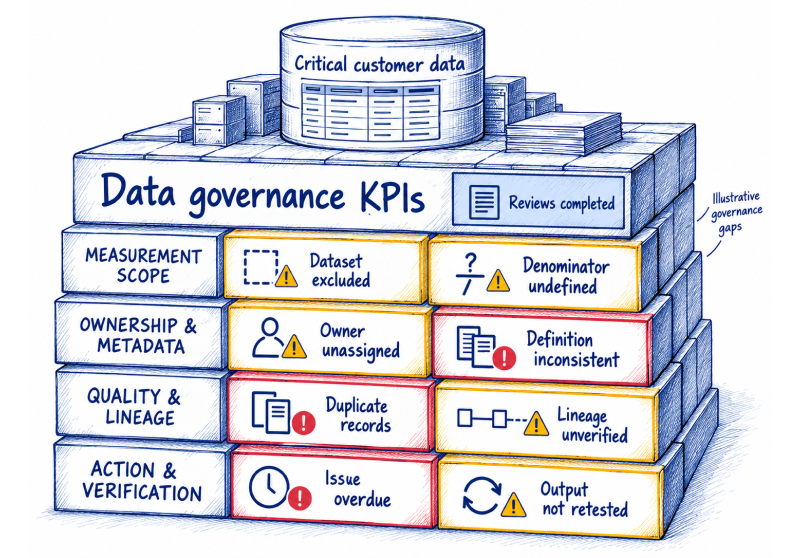
Data Governance Metrics: KPIs for Quality, Ownership, and Trusted Data Decisions
Data governance earns trust when teams can show where important data comes from, who is accountable, and whether it is fit for a defined use. A small set of well-defined...
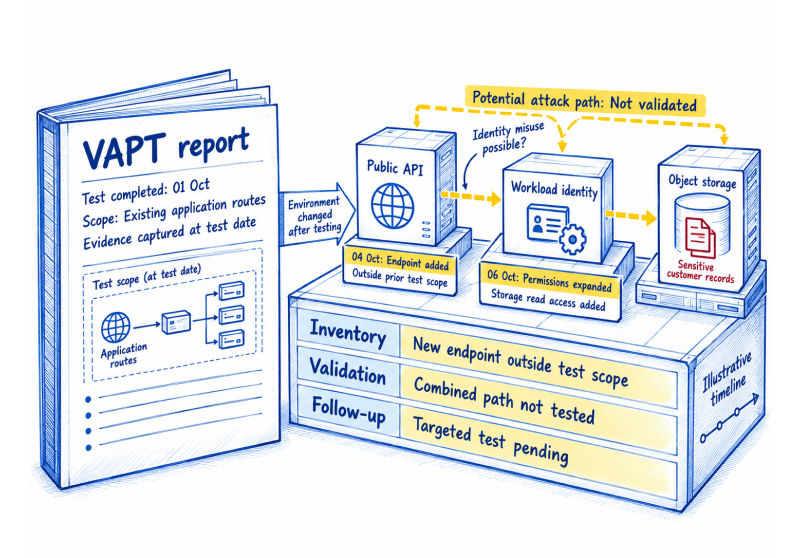
Cloud Security VAPT: Test Changing Attack Paths and Verify Remediation Outcomes
Cloud environments change with every deployment, identity update and configuration shift.Scanning can find weaknesses; scoped testing shows whether they combine into a usable path.Build VAPT as a safe validation loop...
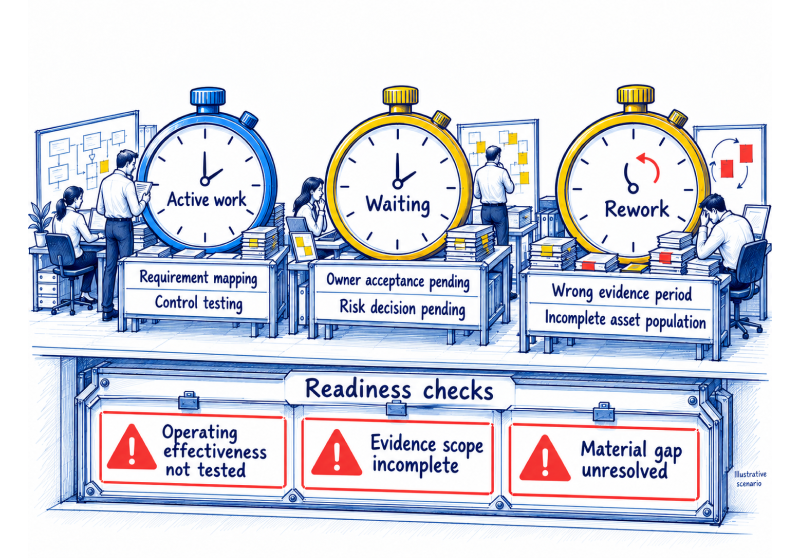
Time to Compliance: How CISOs Speed Audit Readiness and Measure Business Value
Time to compliance helps CISOs understand where audit preparation stalls and how to reduce avoidable delays. Clear milestones, accountable owners, and validated evidence reuse make readiness more predictable. Measuring preparation...
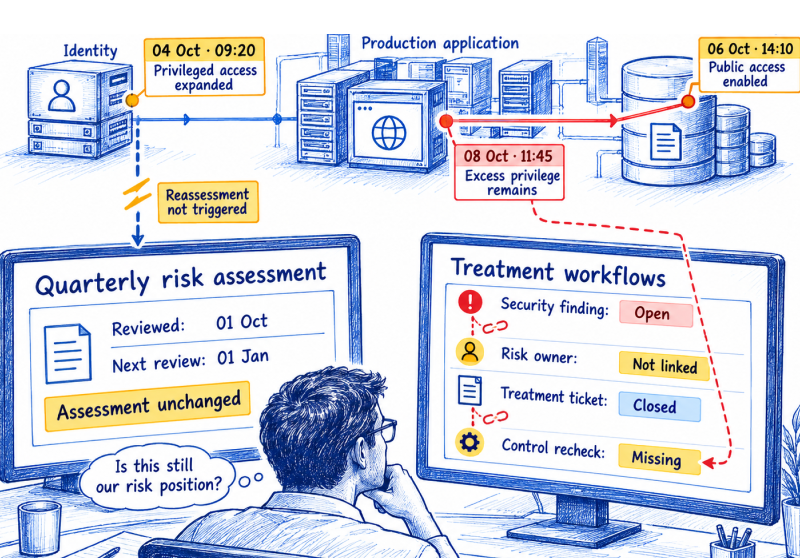
Risk Management Automation: Connect Evidence to Timely and Accountable Decisions
Risk management automation connects current operational evidence with structured risk assessments, monitoring, and accountable decisions. By reducing manual collection and follow-up, organizations can identify meaningful changes earlier while retaining human...
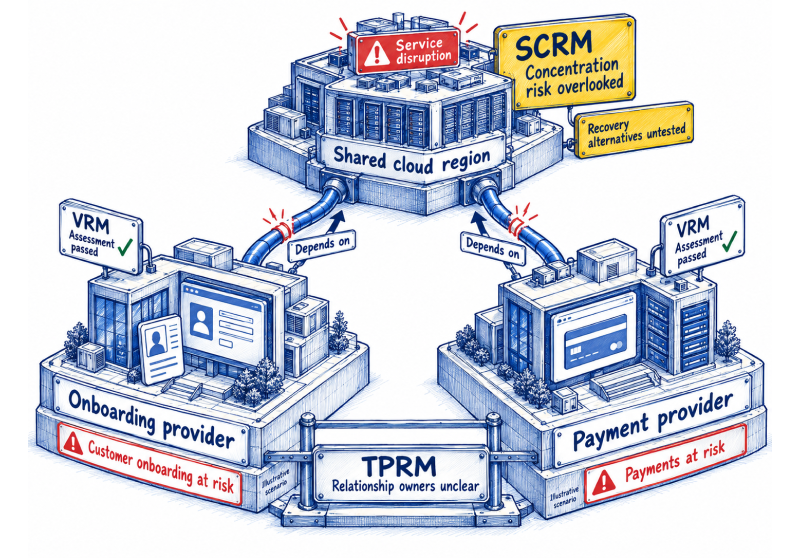
SCRM vs TPRM vs VRM: Understand External Risks and Shared Supplier Dependencies
SCRM, TPRM, and VRM address different layers of external business risk, from individual suppliers to interconnected supply chains. Understanding their scope and governance responsibilities helps organizations assess exposure, manage dependencies,...
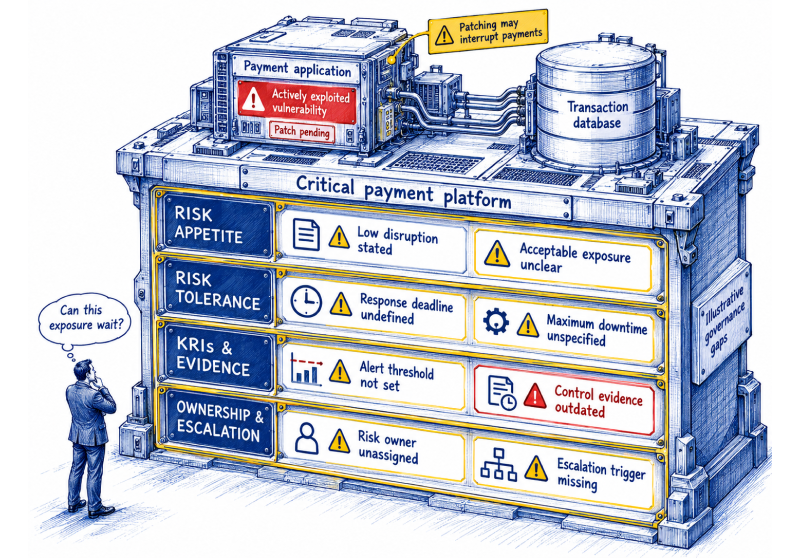
Risk Appetite vs Risk Tolerance: Set Clear Limits and Track Cyber Risk Exposure
Risk appetite, risk tolerance, and risk capacity shape how organizations assess and manage cybersecurity risks. Establishing measurable thresholds, monitoring KRIs, and evaluating control effectiveness help organizations prioritize exposure, make informed...
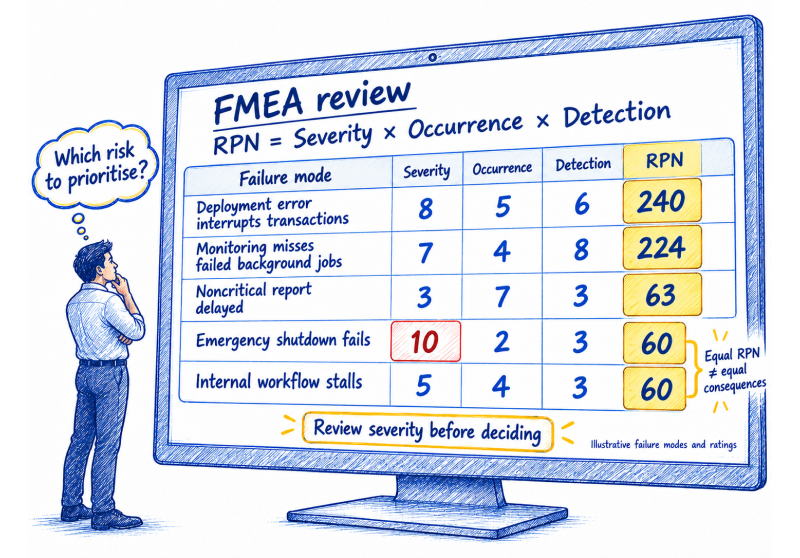
How to Calculate RPN in FMEA: Formula, Scoring Criteria and Practical Examples
Risk Priority Number (RPN) helps teams compare potential failures through their severity, likelihood of occurrence, and difficulty of detection. Consistent scoring, practical examples, and regular reassessment make FMEA more useful...
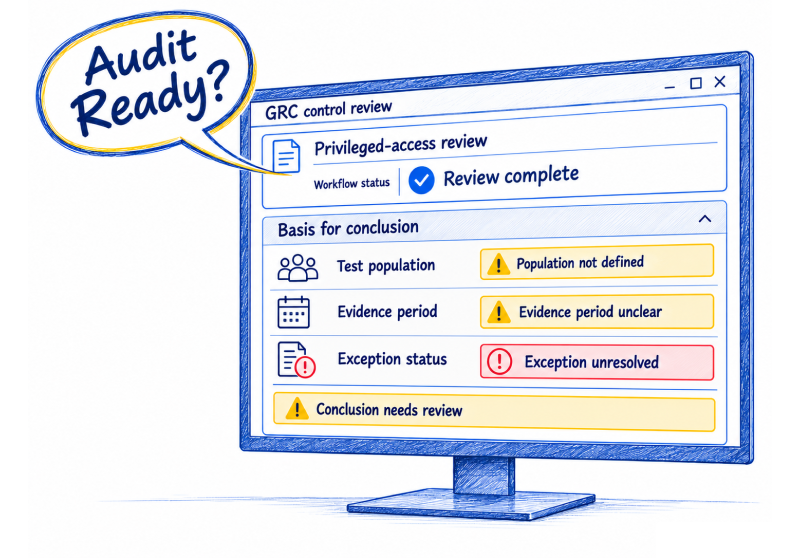
How to Evaluate a GRC Platform for Audit Quality Before Making a Buying Decision
A platform can support a defensible audit trail, but it cannot guarantee a high-quality audit. Use a realistic demonstration, written acceptance criteria and an exit test to assess fit. When...
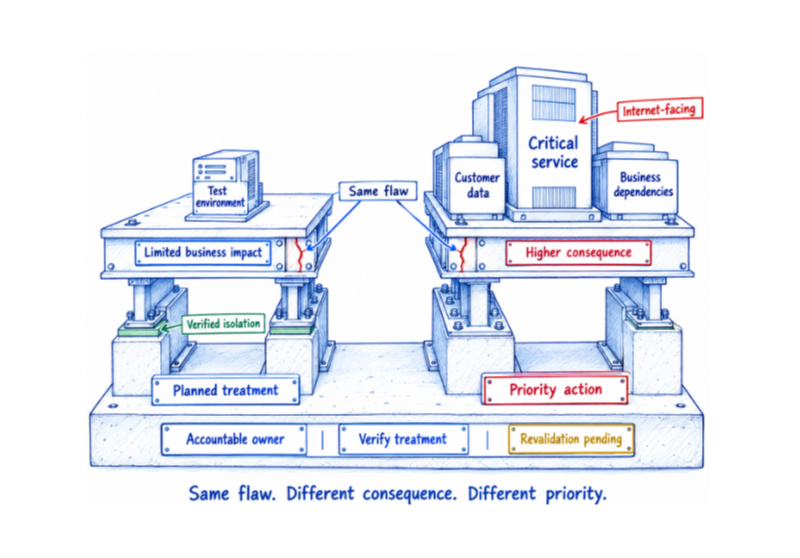
Cybersecurity Risk Scoring: Making Scores Useful for Security and Risk Decisions
A cybersecurity risk score should explain why an exposure matters and what action it requires. Learn how to combine threat signals, reachability, business impact and control evidence into clear priorities,...