Uncategorized
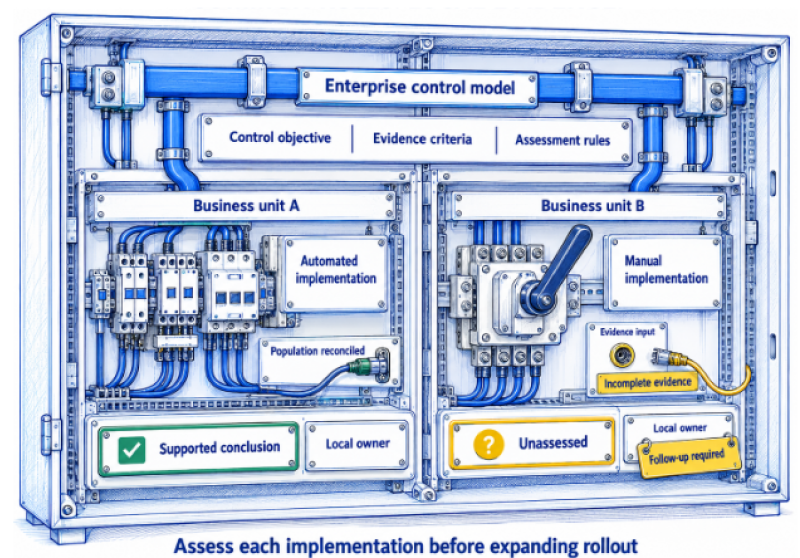
How to Roll Out Enterprise GRC: Prove the Model Before You Scale

Categories: Uncategorized
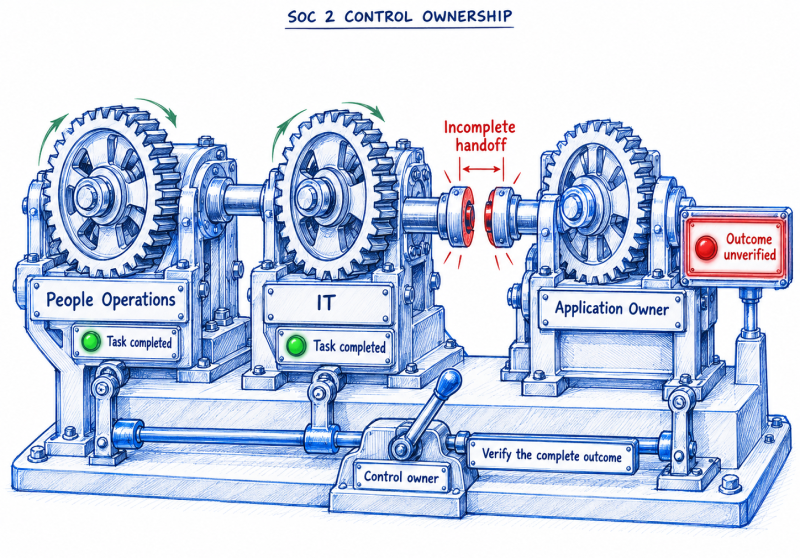
SOC 2 Control Ownership: Define Clear Roles and Validate Evidence Without a CISO
Categories: Uncategorized
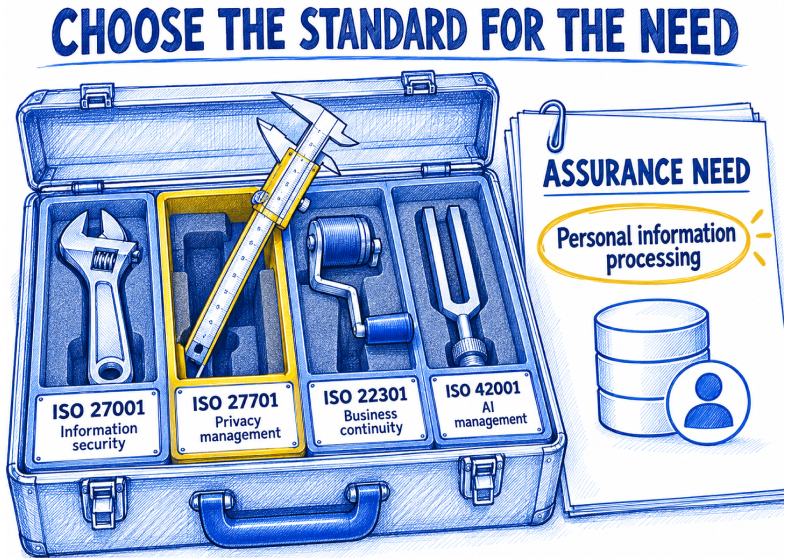
ISO Security Standards in 2026: Which Ones Matter for Your Organization?

Categories: Uncategorized
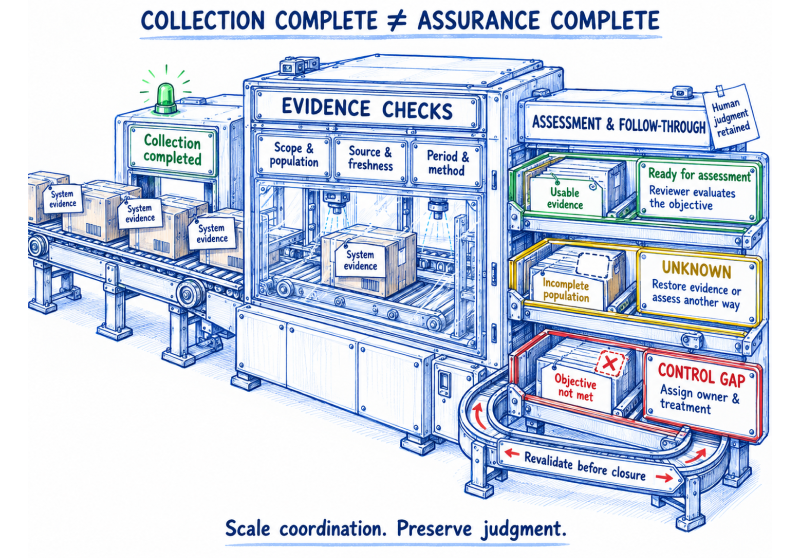
How Lean GRC Teams Can Scale Compliance Without Adding Headcount
Categories: Uncategorized
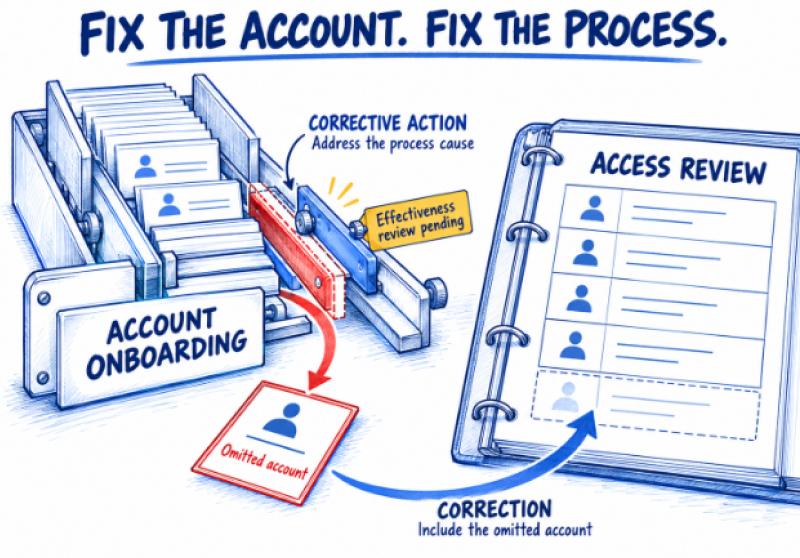
ISO 27001 Certification in 2026: A Practical Readiness Guide
Categories: Uncategorized
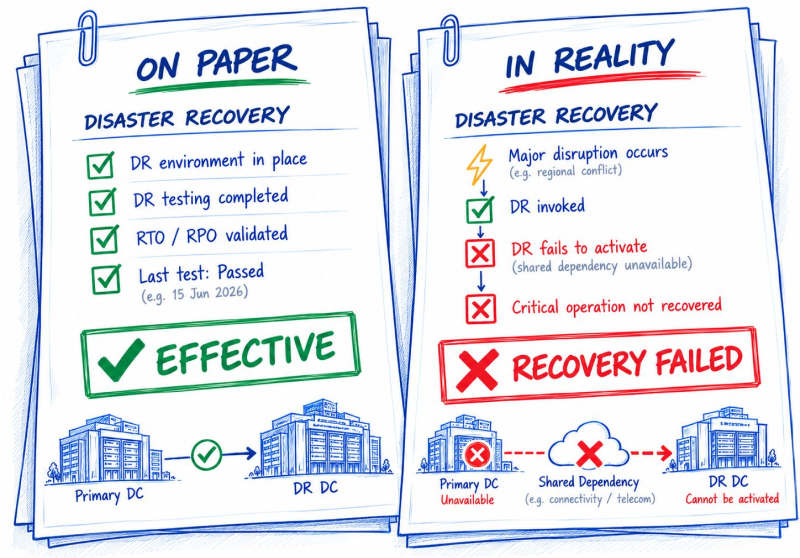
CBUAE Cybersecurity Compliance Checklist 2026: 10 Actions for CISOs

Categories: Continuous Control Monitoring, GRC, Remediation, Uncategorized
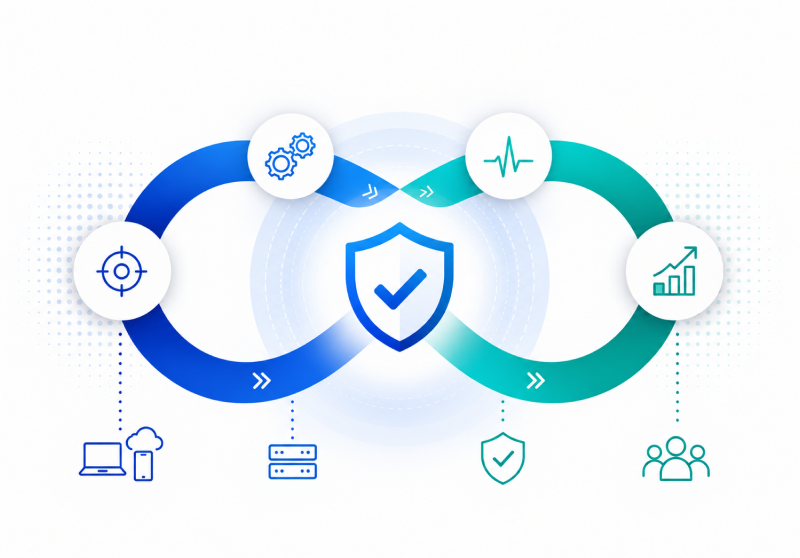
What Is Continuous Assurance in Cybersecurity?
Categories: Uncategorized

Why Compliance Doesn’t Equal Resilience

Categories: Uncategorized
Understanding RBI’s FREE-AI Framework for Responsible AI Governance
Categories: Uncategorized
DPDP Act & Rules 2025: The Compliance Readiness Checklist
Categories: Uncategorized

Unifying Remediation and Compliance with Integrated Incident Response
Categories: Uncategorized

The Rise of Adversarial AI Attacks & AI Security Best Practices to Stop them
Categories: Uncategorized