← Back to Blog
GRC
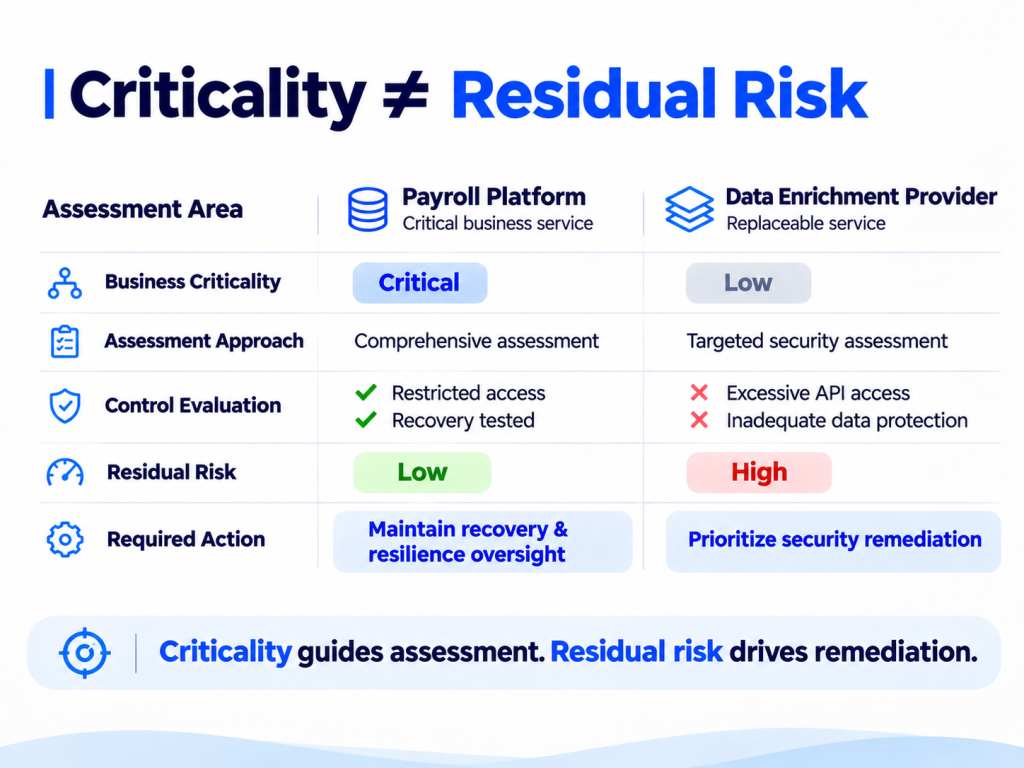
Vendor Cybersecurity Questions That Test Scope, Evidence and Exposure

A vendor cybersecurity inquiry should establish what the supplier will do, which data and systems it can access, and how the business depends on its services. Ask targeted questions, request...
Categories: Continuous Control Monitoring, Exposure Management, GRC
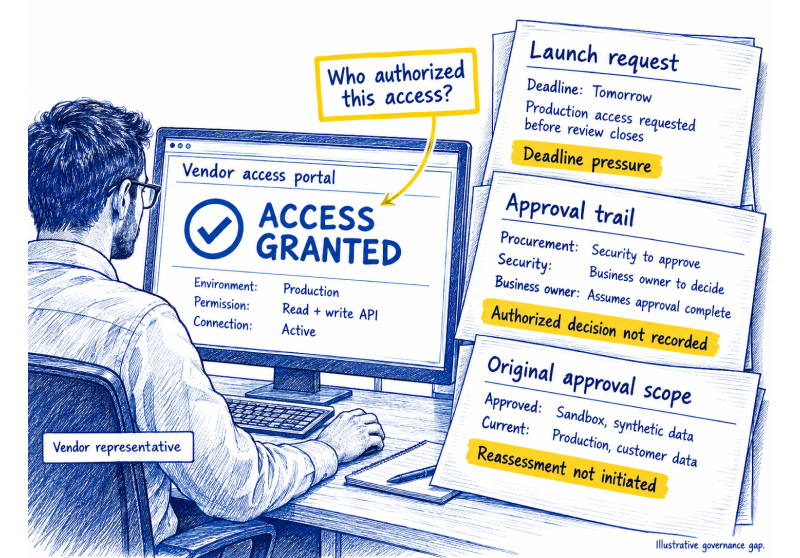
Why Your Vendor Management Policy Must Guide Decisions Through Change

A vendor management policy sets the rules for approving suppliers, accepting exceptions and responding when relationships change. This guide explains how to define decision authority, approval conditions, reassessment triggers and...
Categories: GRC
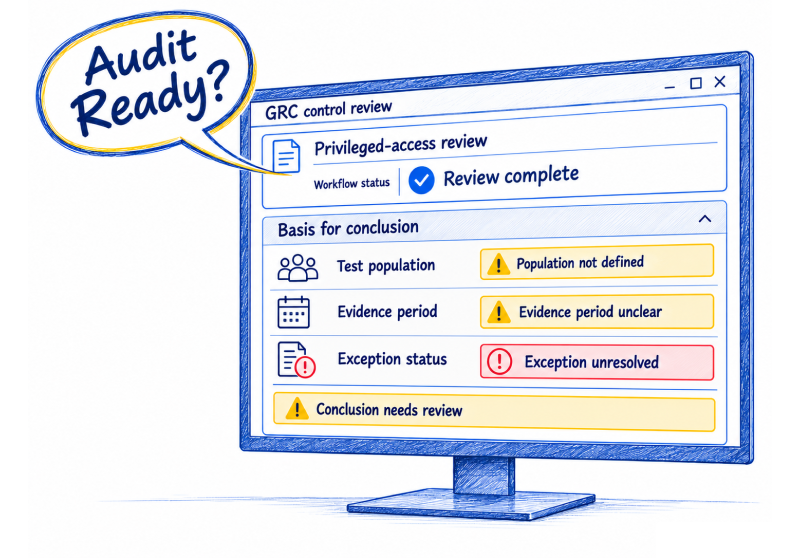
How to Evaluate a GRC Platform for Audit Quality Before Making a Buying Decision
A platform can support a defensible audit trail, but it cannot guarantee a high-quality audit. Use a realistic demonstration, written acceptance criteria and an exit test to assess fit. When...
Categories: GRC
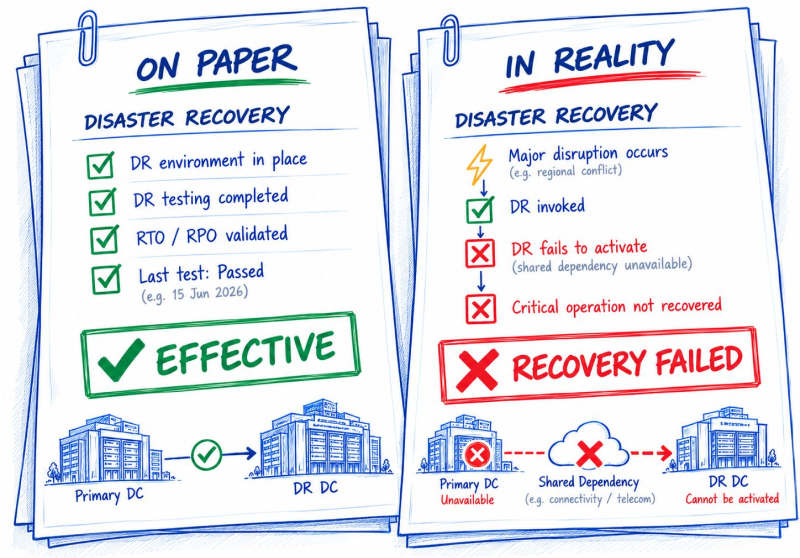
CBUAE Cybersecurity Compliance Checklist 2026: 10 Actions for CISOs

The Central Bank of the UAE (CBUAE) Operational Risk Management Regulation C 1/2026, effective from 14 September 2026, introduces important ICT and cybersecurity requirements for Licensed Financial Institutions. It requires...
Categories: Continuous Control Monitoring, GRC, Remediation, Uncategorized