GRC Maturity That Holds Up Under Change: Align Evidence, Ownership and Decisions
Help lean GRC teams support growing compliance demands with clear ownership, reliable evidence and selective automation. Reduce repeated follow-up, keep exceptions visible and verify remediation while measuring whether the team has capacity to scale.
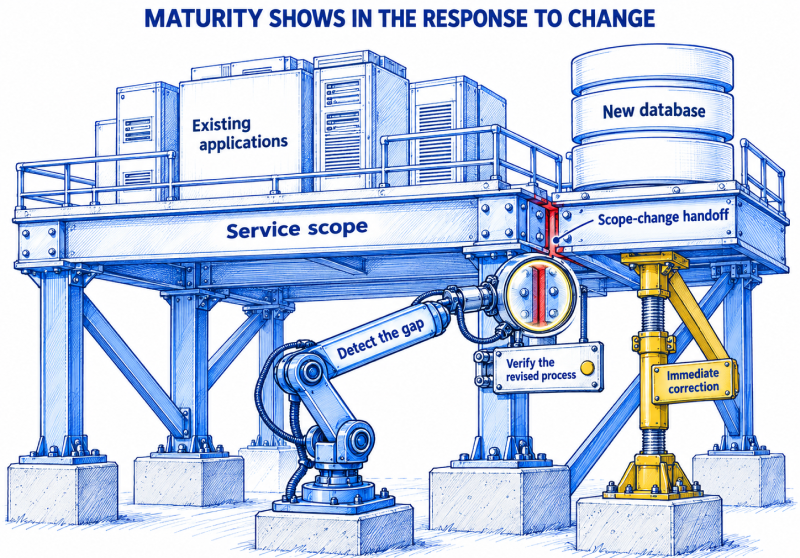
A recovery process can look mature until a new application joins the service. Policies are approved, backup jobs succeed and the reporting dashboard stays green. The application’s data is missing from the recovery scope.
The assessment should ask why the omission survived onboarding, monitoring and management review. Fixing one backup configuration addresses the immediate gap. Improving GRC maturity means making that kind of gap easier to detect, assign and resolve the next time the service changes.
A useful GRC maturity assessment examines the reliability of those decisions. It should produce a defensible capability profile and an improvement plan that gives management clear resource decisions, with evidence showing whether the changes worked.
What GRC maturity should tell a leader
GRC maturity describes how consistently an organization governs its objectives, handles uncertainty and meets its obligations. For security leaders, the practical question is whether risk and control decisions remain reliable across teams, systems and changes.
This guide focuses on the cybersecurity and operational-control part of GRC. An enterprise assessment must also include relevant legal, ethical, financial and other business obligations. A security dashboard cannot represent all of them.
Keep three assessments separate:
Maturity: can the organization perform, sustain and improve a practice reliably?
Control performance: does a specific control meet its objective for the population and conditions tested?
Compliance: are the applicable requirements satisfied within their defined scope?
A mature process can discover a failed control. A successful test on one system can coexist with weak governance elsewhere. Report those facts together without converting one into proof of the other.
Choose a model before assigning scores
There is no single GRC maturity scale that every organization must use. Choose a model that fits the assessment purpose and retain its definitions if you intend to compare results over time.
OCEG’s GRC Capability Model addresses integrated governance, risk and compliance. The US Department of Energy’s C2M2 evaluates cybersecurity practices across domains using maturity indicator levels. NIST CSF 2.0 offers cybersecurity outcomes, Current and Target Profiles, and Tiers describing the rigor of risk governance and management. Its four Tiers should not be relabeled as this article’s five-stage scale.
The working scale below is an editorial assessment aid. It is not an official OCEG, NIST or C2M2 model, a certification scheme or a regulatory requirement.
Stage
Evidence needed for the assessed practice
Improvement focus
1 Reactive
Actual cases show improvised execution or unresolved responsibility.
Establish scope, an owner and a usable procedure.
2 Defined
Approved responsibilities and methods exist; consistent execution is not demonstrated.
Make the documented practice workable across the scope.
3 Repeatable
Records from the selected period show consistent execution and follow-up.
Check completeness and introduce reliable measures.
4 Measured
Defined measures are reconciled to scope and used to direct action.
Test whether changes trigger timely reassessment.
5 Adaptive
Records show reassessment after relevant changes, verified action and sustained improvement.
Maintain the capability and investigate recurring weaknesses.
For this working scale, assign the highest stage supported by the relevant earlier-stage practices. Agree what “consistent” means for the scope before testing it. A single successful case does not establish repeatability.
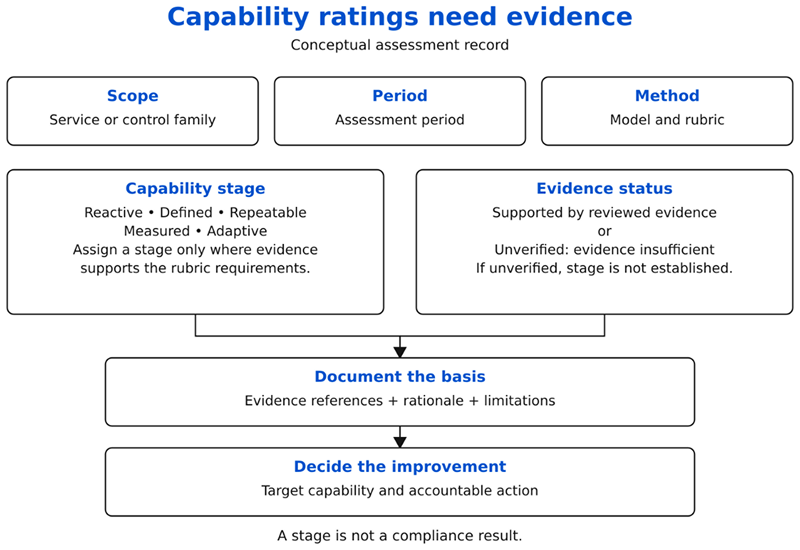
Unverified is a separate assessment status. Use it when evidence is insufficient. Explain what is missing and who will resolve it. If the demonstrated problem is failure to retain required evidence, record that as a finding as well. Lack of information must not quietly disappear into a numeric average.
Assess five capabilities separately
These five capabilities provide a practical view of how a security-focused GRC program operates. Adapt them to the chosen model rather than treating them as an exhaustive enterprise framework.
Control definition and scope. Establish the objective, applicable obligations, covered population and expected behavior. Check how inventories are reconciled and exclusions approved.
Ownership and authority. Identify the operator, accountable control owner and authorized risk decision-maker. Test whether the assigned people can obtain evidence, direct correction and escalate blocked decisions.
Evidence and evaluation. Check source reliability, population completeness, review methods and retention. Define acceptable evidence age against the activity and risk; a historical recovery test and a current configuration check serve different purposes.
Risk decisions and exceptions. Trace the rationale, affected service, residual exposure, approver and review date. Verify alternative measures rather than treating approval as proof of protection.
Change and improvement. Follow changes to services, suppliers, assets and obligations into revised assessments. Check whether corrective actions are verified and recurring causes reach management.
Report the result by capability and service. A strong central process does not establish the same capability in an acquired subsidiary or a newly deployed cloud environment.
Run an assessment that another reviewer can reproduce
Define the boundary and decision
Start with a critical service or a clearly defined control family. Record the entities, systems, obligations, assessment period and exclusions. Name the decision the assessment should support, such as funding service-onboarding improvements or resolving overdue risk decisions.
Assign a sponsor with authority over resources. Have control owners supply evidence and an assessor challenge its sufficiency. For material claims, use a reviewer outside the activity being assessed where practical. A facilitated self-assessment remains a self-assessment; it is not independent assurance.
Agree evidence thresholds before the interviews
Specify what would support each rating and how evidence will be selected. Combine interviews and documents with operating records, source checks and relevant change events. Include known failures and exceptions in the review.
Choose the period and sample against the activity’s frequency, variability and significance. Document the selection rationale and its limits. A selected sample can expose a weakness; it does not prove that every instance worked.
Trace one obligation through to a decision
For recovery, connect the service requirement to its supporting data and systems, backup arrangements, operating results and recovery exercise. Establish who evaluates a shortfall and who decides what to do about the resulting exposure.
Then examine a recent application onboarding or configuration change. Did it update the recovery population? Was omitted coverage detected? Did the correction restore the intended capability, or merely close a ticket?
Calibrate and retain the assessment
For each capability, retain the proposed stage, evidence references, scope, period, rationale and limitations. Record conflicting evidence and the resolution of reviewer disagreements. Use the same rubric on a small shared case before different assessors score separate services.
Do not average ordinal stages into a precise-looking enterprise rating without a documented purpose and method. Show critical weak or unverified areas alongside any summary. Compare like scopes and disclose changes in the method or assessed population.
Worked example of a recovery scope gap
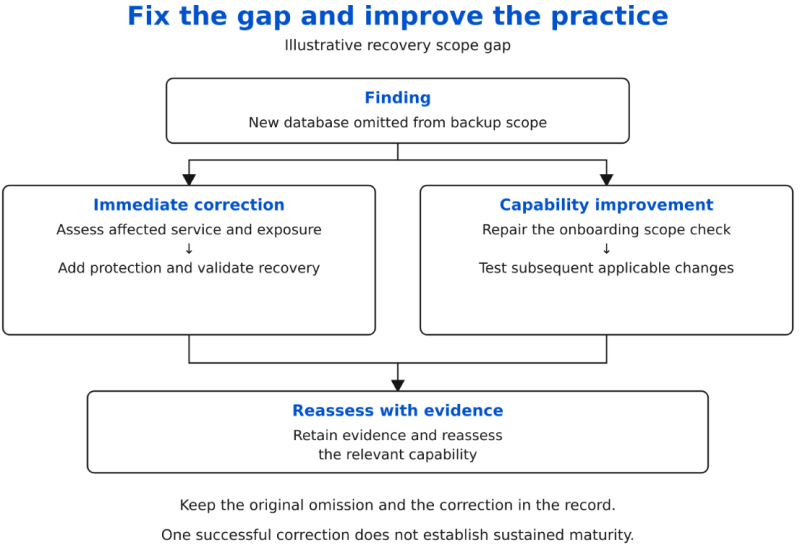
Consider an illustrative customer service with an established backup process. A newly added database is absent from the backup policy. Successful jobs for the older systems keep the dashboard green.
The assessor reconciles the service inventory with the backup population and identifies the omission. The issue affects coverage, but the maturity finding concerns how the organization manages scope changes.
Documented onboarding instructions may support a Defined rating for that practice. If operating records show that the required scope check was missed, they do not support a Repeatable rating merely because the rest of the backup process is well run. Other capabilities should retain their own evidence-based ratings.
The service owner assesses the business consequence with the risk owner. The platform team adds the database to protection, checks the resulting jobs and performs an appropriate recovery validation. Any temporary deviation remains recorded with its rationale, alternative measures and review date.
The improvement owner also fixes the onboarding handoff. The team retains the original omission and tests subsequent applicable changes against the revised scope check. Only that follow-through can support a claim that the practice improved. One successful correction is evidence of correction, not sustained maturity.
Turn findings into an investment decision
Choose target capability against service importance, obligations, exposure and the cost of maintaining the practice. The highest stage everywhere is not a useful default. A chosen target cannot excuse an unmet mandatory requirement.
Sequence work by dependency. An unreliable asset population undermines coverage reporting. Missing decision authority prevents escalation. An unclear evidence standard makes additional integrations difficult to interpret.
Every material improvement should record the affected scope, current weakness, target behavior, accountable owner, resources, due date and verification method. For a scope gap, the target could be that applicable onboarding events consistently reconcile service inventories with the control population. Verify it using later events, not the existence of an updated procedure alone.
Track indicators with explicit definitions: critical services with unreconciled populations; overdue actions by severity; expired exceptions; and repeated findings after claimed closure. For rates, retain the numerator, denominator, source and time window. Check whether the underlying cases support the trend before claiming reduced risk.
Give management the decisions it needs to make: which exposure remains, what is blocking improvement, who has authority to act and what resources are required. Reassess on relevant change triggers as well as an agreed review cadence.
Where GRC engineering and SPOG.AI fit
GRC engineering makes the connections between obligations, control activities, operational populations, evidence and decisions usable in day-to-day work. It also needs source-quality checks, versioned mappings and visible data-collection failures. Reusing evidence across requirements is appropriate only where its scope, period and purpose support each assessment.
SPOG.AI’s GRC capabilities connect requirements, controls, evidence, ownership and business context. Its continuous control monitoring supports selected assessments using connected operational sources, while its security maturity capabilities support identifying weaknesses and tracking improvement initiatives.
Confirm the available connectors, mapping rules, assessment configuration, historical records and treatment of manual activities. Connected telemetry cannot establish every governance decision or supply independent assurance. Management remains responsible for the model, risk decisions and conclusions drawn from the evidence.
Request a demo to explore how SPOG.AI connects maturity findings with accountable improvement.
Make the next assessment test a real improvement
Start with a material weakness that crosses a team boundary. Establish the evidence, correct the immediate exposure and assign the underlying process improvement. Revisit subsequent relevant events to determine whether the practice holds.
The result should explain which capability improved, where it applies and what evidence supports the claim. That is a more useful basis for management action than a higher score without a demonstrated change.
Corrected hero alt text GRC assessment illustration showing governance, risk and compliance practices. If stage names remain, describe the corrected scale accurately.
Frequently asked questions
GRC maturity describes how reliably an organization governs objectives, manages uncertainty and meets obligations. An assessment examines whether relevant practices are defined, consistently executed, evaluated and improved within a stated scope.
No single scale applies to every program. Organizations can use established models or a defined internal rubric. State the model, scope and method, and do not present internal stage names as an official industry standard.
NIST CSF 2.0 Tiers characterize the rigor of cybersecurity risk governance and management. They are not interchangeable with an internal five-stage GRC scale. CSF Profiles describe current and target cybersecurity outcomes.
Maturity concerns the reliability and improvement of a capability. Compliance concerns applicable requirements within a defined scope. A strong maturity rating does not prove compliance or remove mandatory obligations.
Use documented responsibilities, operating records, relevant change cases, source checks and decision records. Match evidence to the scope and assessment period. Interviews alone should not establish sustained execution.
Record an unverified status, specify the missing evidence and assign follow-up. Do not infer success or failure from missing information alone. A demonstrated failure to retain required records can also be a finding.
Averages can hide critical weaknesses and give ordinal stages misleading precision. Prefer capability and service profiles. If a summary is required, document the aggregation method and display material weak or unverified areas beside it.
Set a review cadence against risk and operational change. Reassess affected capabilities after significant service, supplier, system, organizational or obligation changes. No universal assessment frequency is prescribed by this guide.
No. It records a decision about a deviation. Assess the affected scope, residual exposure and alternative measures, and retain the approver and review or expiry date. Approval does not establish that the control meets its objective.
SPOG.AI connects operational evidence, controls, ownership and business context to support selected assessments and improvement tracking. Coverage depends on connected sources and configured assessments. Management retains responsibility for the maturity model, judgments and risk decisions.
With 8.5+ years in B2B SaaS, I’ve led demand generation and GTM initiatives across global markets (US, UK, Europe, Africa), helping companies move from fragmented marketing efforts to structured, revenue-focused growth engines.