Continuous Control Monitoring
Why Passing an Audit Does Not Prove Ongoing Compliance
An audit can confirm that security controls met assessed requirements during a defined period. But system changes can...


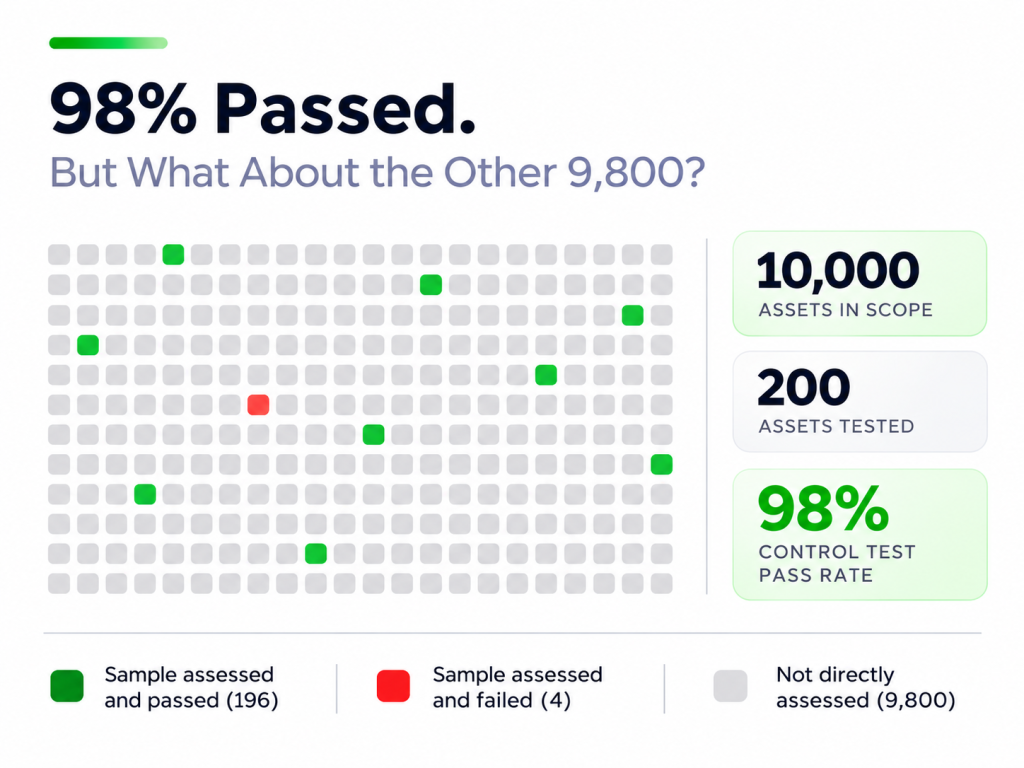
Consider an organization with 5,000 endpoints. During a quarterly assessment, 50 endpoints are selected to verify whether specific security requirements are being met. All 50 pass, and the assessment reports no exceptions. While this provides evidence about the selected endpoints, it does not directly establish the control state of the remaining 4,950 systems. A 100% pass rate across a 1% sample does not mean the entire environment is compliant, although properly designed statistical sampling may support broader conclusions within defined confidence limits.
The second limitation is time. Even if a control satisfies its requirements during an assessment, configurations may change, security agents may stop functioning or new systems may be introduced before the next review.
Together, these limitations create two gaps in security assurance: a population gap, where failures may exist outside the tested sample, and a time gap, where controls may deteriorate between assessments. Critical systems may therefore remain without required protections while management continues relying on assessment results that no longer reflect current conditions.
Continuous Control Monitoring (CCM) helps address these gaps by regularly evaluating existing operational evidence across the applicable environment. Rather than relying entirely on periodic assessments, organizations gain broader and more current visibility into their security controls.
CCM uses evidence already generated by enterprise security and IT platforms, including configurations, system status, logs and operational activity, to evaluate defined control requirements.
For example, instead of manually checking endpoint protection on a sample of devices, an organization can reconcile its asset inventory with its endpoint security platform to determine which systems have the required protection deployed, whether policies are correctly configured and whether agents are reporting as expected.
Where reliable evidence is available, this evaluation can cover the entire applicable population. It can also be repeated as new information becomes available, allowing security teams to identify configuration changes, disconnected agents and other operational failures without waiting for the next formal assessment.
The benefit goes beyond finding more exceptions. Broader and more frequent evaluation helps security teams detect control failures earlier, investigate their causes and take corrective action before those failures persist for extended periods.
However, CCM depends on the quality of the evidence it receives. Incomplete inventories, disconnected systems and stale telemetry can leave gaps in monitoring. Assets without sufficient evidence must therefore remain unverified rather than being assumed compliant.
Control testing and CCM both contribute to security assurance, but they rely on different forms of evidence and support different conclusions.
| Dimension | Traditional Control Testing | Continuous Control Monitoring |
|---|---|---|
| Primary purpose | Validate control requirements and expected behavior | Evaluate observable control conditions |
| Population | Often sample-based | Potentially the full applicable population |
| Frequency | Typically periodic | Recurring or event-driven |
| Evidence | Reviewed records, test procedures and deliberately executed scenarios | Existing configurations, logs, telemetry and operational activity |
| Strength | Validates control behavior under defined conditions | Provides broader and more current visibility into control health |
| Limitation | Sample coverage and intervals between assessments | Evidence completeness and conditions not observed |
These differences are not absolute. Control testing can also be automated and performed frequently. What matters is whether the available evidence establishes the required outcome or whether additional testing is needed to demonstrate it.
Consider an organization that processes 500 employee departures during a quarter. Its security policy requires access to be disabled within 24 hours of termination.
During its quarterly assessment, the audit team reviews 25 selected departures. All meet the requirement, and no exceptions are identified.
The organization also uses CCM to compare termination records from its HR system with account-deactivation timestamps from its identity management platform. Across the same quarter, sufficient evidence is available for 480 departures, and monitoring identifies eight instances where access removal exceeded the permitted timeframe.
| Measurement | Periodic Control Testing | Continuous Control Monitoring |
|---|---|---|
| Applicable population | 500 | 500 |
| Records evaluated | 25 | 480 |
| Evaluation frequency | Quarterly | Daily |
| Delayed access removals identified | 0 | 8 |
| Records not directly evaluated | 475 | 20 |
Illustrative figures. The 25 sampled departures are included in the monitored population and contain none of the eight identified failures.
The assessment correctly establishes that the selected departures met the requirement, but it does not demonstrate compliance across the entire population. CCM identifies failures across a broader set of records and can detect them closer to the time they occur.
The 20 departures without sufficient evidence remain unverified, while applications outside the connected identity systems may require additional checks.
CCM evaluates control conditions using evidence generated through normal operations. But a control can be deployed, correctly configured and reporting as healthy without having encountered the event it is designed to prevent or detect.
Take Endpoint Detection and Response (EDR) technology. CCM can establish whether agents are deployed, communicating with the management platform, running the required policies and receiving current detection content. These checks provide evidence of deployment, configuration and operational health, but they do not necessarily demonstrate whether the EDR will detect or prevent a particular attack technique.
If that technique has not occurred, existing telemetry may contain no evidence of the control’s response. To find out how the EDR would behave, the security team can deliberately execute a controlled attack simulation and observe whether it detects the activity, generates the expected alert and prevents or contains the action where required.
This is where the two approaches differ. CCM evaluates control health using existing operational evidence, while scenario-based control testing deliberately generates evidence to validate how a control behaves under specified conditions.
A successful simulation provides assurance about the tested technique and environment, not every possible attack. Both approaches are therefore needed to build a more complete understanding of control effectiveness.
Organizations should first identify the controls applicable to their assets, identities, applications and business services. Where reliable operational evidence exists, CCM can evaluate control conditions across the connected population and identify deviations as they emerge. Where the evidence cannot establish the intended security outcome, deliberate testing can provide the additional validation required.
Findings should remain traceable to the affected systems and supporting evidence, allowing control owners to investigate weaknesses, prioritize remediation and verify corrective actions. Management reporting should also distinguish confirmed failures from missing or stale evidence so that incomplete visibility is not mistaken for satisfactory control performance.
SPOG.AI supports Continuous Control Monitoring by connecting defined control requirements with operational evidence from enterprise security and IT technologies. The platform evaluates control coverage, configuration compliance and operational health across connected systems, helping organizations identify weaknesses that may remain outside traditional assessment samples.
By linking control findings with assets, vulnerabilities, business services and risk indicators, SPOG.AI also helps security teams understand the potential business impact of identified weaknesses and prioritize remediation.
For a related discussion, read Control Coverage vs. Control Effectiveness: Measure Reach and Results.
Traditional sample-based, periodic control testing provides valuable assurance, but its conclusions are limited by the systems evaluated and the conditions tested. Continuous Control Monitoring helps close the visibility gaps by evaluating existing operational evidence across a broader population and more frequently.
Monitoring alone, however, cannot always establish how a control will respond to a situation it has never encountered. Deliberate scenario-based testing provides that additional validation, making the two approaches complementary rather than interchangeable.
The future of security assurance is not testing less. It is knowing more, more often.
An audit can confirm that security controls met assessed requirements during a defined period. But system changes can...
Seven critical PHP vulnerabilities pose risks of remote code execution and service disruption. While patching is essential, which...
An approved policy can coexist with an unprotected business-critical system. The governance failure begins when leadership treats approval,...