Frameworks
Getting Started With Cyber Risk Quantification: Key Concepts Explained
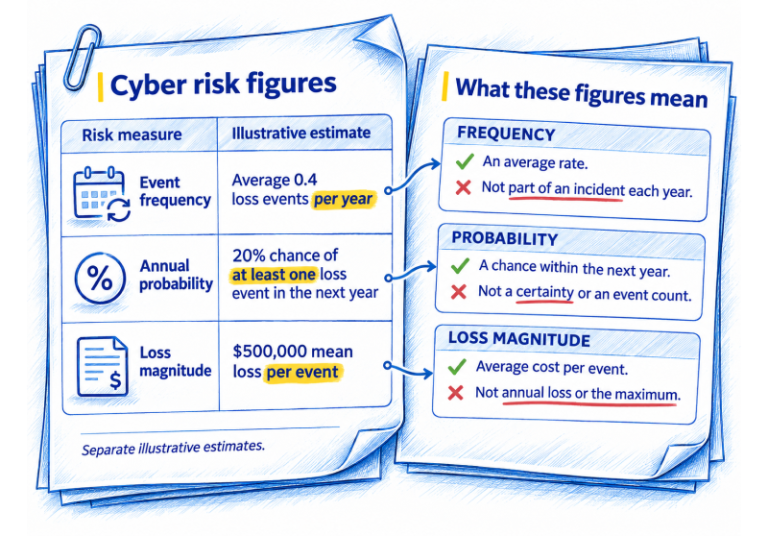
Cyber risk quantification expresses possible cyber losses in numerical terms, often money, for a defined scenario and period....
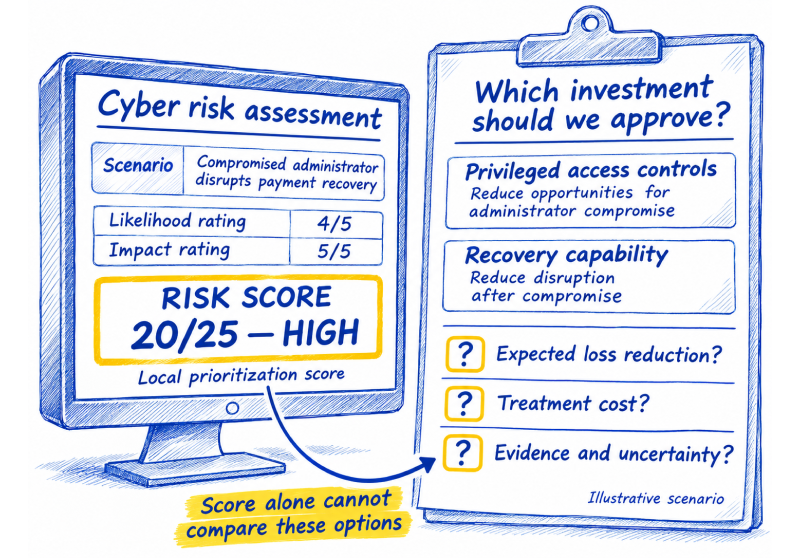
A qualitative assessment can be more defensible when evidence is thin or a decision is urgent. Quantitative analysis is worth the effort when leaders must compare treatments or allocate capital. A score helps only when its scale and limits are clear.
Many programs combine light portfolio screening with deeper analysis for consequential decisions. Method choice is therefore a governance decision as well as an analytical one.
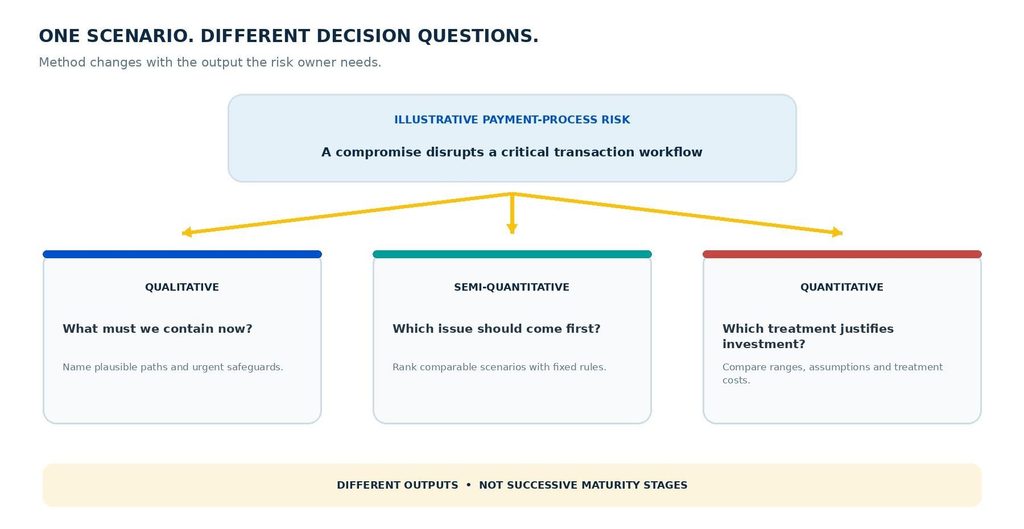
Ask what someone needs to decide: contain an active exposure, rank a backlog, accept a temporary exception, select a control investment, set risk appetite or explain a scenario to executives. Each question calls for a different output. A priority order can help allocate analyst time; it cannot by itself show expected loss avoided by a proposed investment.
Define the scenario before comparing approaches: affected process, initiating event, path to harm, consequences, horizon and relevant safeguards. “Ransomware risk” is too broad. “A compromised administrator prevents payment-platform recovery this quarter” can be assessed and revisited.
NIST’s IR 8286 series, finalized in December 2025, connects cyber risk analysis with enterprise objectives and communication. It distinguishes qualitative, semi-quantitative and quantitative methods, and says the method should fit the context. NIST IR 8286 Rev. 1 · NIST IR 8286A Rev. 1
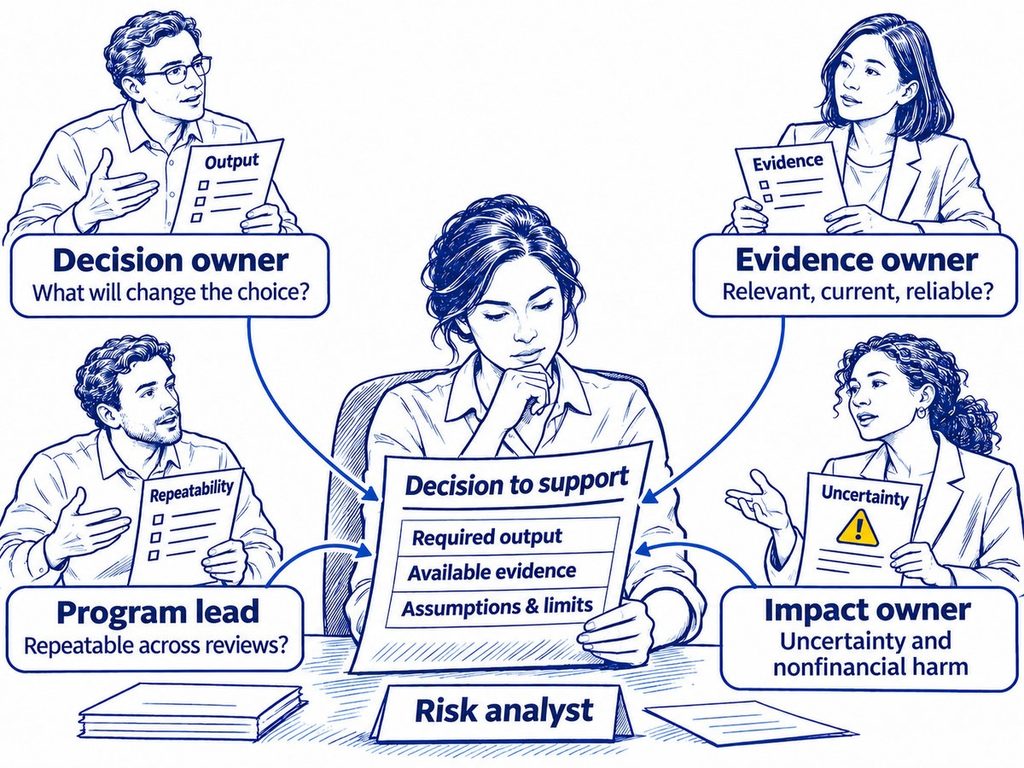
Use four tests to keep analysis proportionate and its limits visible.
If a team needs a fast triage, a concise evidence-based category may be enough. If it must rank comparable work, a defined scoring rule can help. If leaders need to compare investment choices or understand loss exposure, they may need estimates expressed in meaningful units and ranges. Do not build a model simply because a dollar figure looks persuasive.
Identify usable internal incident and near-miss records, exposure data, control evidence, recovery results, business-impact inputs, threat intelligence and informed estimates. Judge each source for relevance, coverage, age and reliability. Missing evidence should remain visible; a sophisticated model cannot repair ungrounded assumptions.
Quantitative analysis can structure a difficult question with incomplete data, but uncertainty must remain explicit. NIST notes that results depend on input accuracy and model validity; semi-quantitative scales remain local rankings, not comparable measurements across contexts.
A recurring portfolio process needs stable scenario definitions, category criteria, ownership and review rules. An investment analysis may justify more detailed modeling, sensitivity tests and specialist review. Set the minimum record required for each approach so another analyst can understand what was measured, what was assumed and what would cause reassessment.
Some consequences are difficult to monetize, including safety, legal obligations, customer trust or strategic disruption. Keep these visible alongside financial estimates. Do not force every impact into a dollar value or compress unlike outcomes into one score merely to simplify a dashboard.
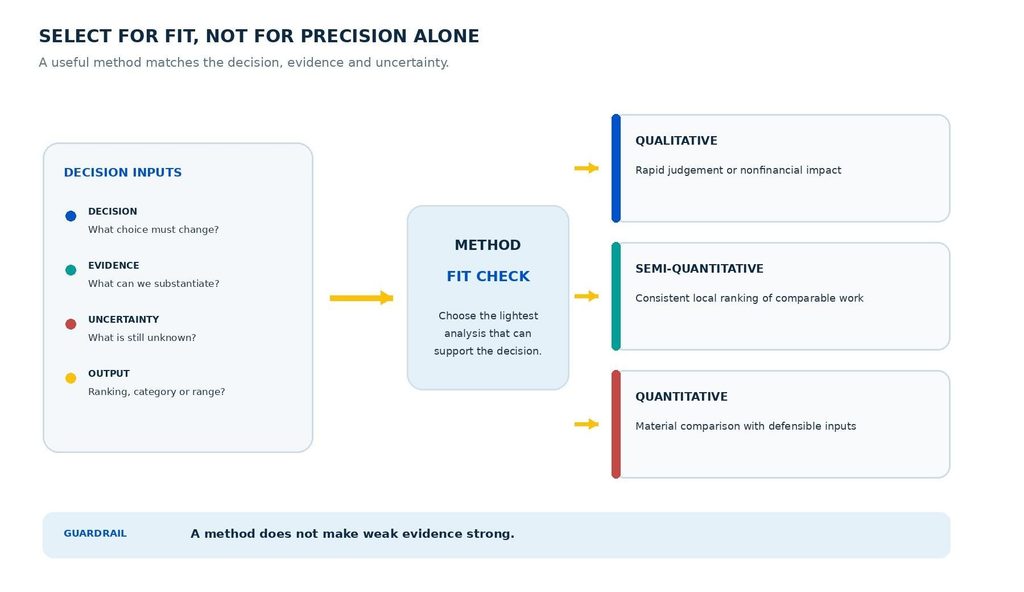
Use the method whose output answers the question, and retain its limitations with the result.
| Decision need | Useful approach | Keep clear |
|---|---|---|
| Rapid review or early-stage assessment | Qualitative categories with explicit criteria and evidence | A label such as “high” is a judgment, not a probability or loss estimate. |
| Relative ordering of comparable issues | Semi-quantitative scoring with fixed definitions and governance | The score supports local prioritization; it does not imply proportional risk. |
| Comparing material treatment or investment options | Quantitative analysis with defined scenarios, ranges and assumptions | A model estimates outcomes; it does not predict a specific incident or guarantee savings. |
| Broad portfolio plus a few high-consequence decisions | Hybrid approach: consistent screening, deeper analysis where it can change action | Preserve how each assessment was produced; do not mix unlike scores. |
A numerical score does not automatically make an assessment quantitative. Multiplying “likelihood 4” by “impact 5” creates a local ranking rule unless those values represent measured quantities with justified relationships. Define how the score drives action, test it against known cases and preserve the component ratings so reviewers can challenge them.
The method label also matters. FAIR is a structured model for analyzing information risk; Monte Carlo is a simulation technique that can explore uncertain inputs within a model. NIST IR 8286 provides guidance for integrating cyber risk into enterprise risk management, not a universal scoring formula. These terms are related, but they are not interchangeable choices in a single model menu.
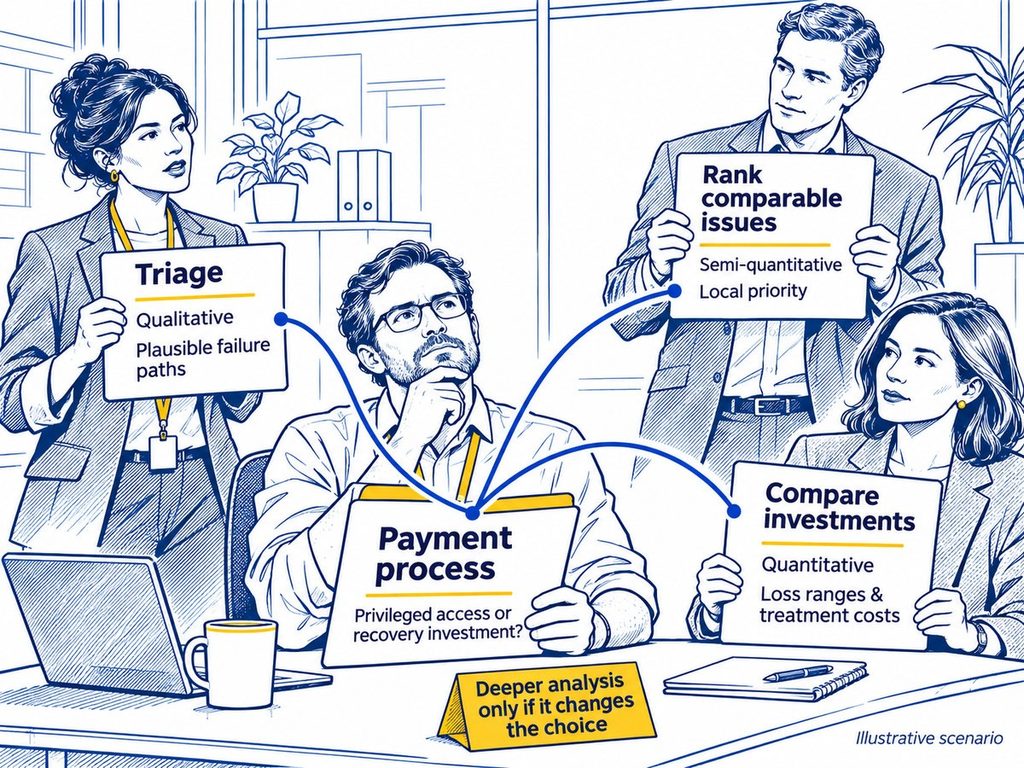
Consider a team deciding whether to improve privileged access controls or expand recovery capability for a payment process. It can begin with a qualitative assessment to identify the plausible failure paths and immediate safeguards. A semi-quantitative rule may help compare that scenario with similar open issues across the portfolio. If the decision involves significant spend, a quantitative model may then compare the expected effect and cost of each treatment, provided the team can state defensible ranges for frequency, interruption and recovery.
Do not calculate a financial estimate just to “graduate” from an earlier assessment. If new evidence will not change the decision, keep the simpler method. If one uncertain input drives the result, improve that input or compare credible alternatives.
Before scaling a method, document its purpose, scope, assumptions, data sources, definitions, owners, approval authority and reassessment triggers. Record material disagreements and overrides. Test whether similar scenarios receive consistent treatment and whether the output changes a decision.
Reassess when the scenario, architecture, exposure, controls, business impact or threat conditions change. A closed ticket does not prove risk fell; verify the control’s scope and effect on likelihood or consequence. Keep prior results to distinguish changed conditions from changed scoring rules.
A compact decision record should capture the alternatives considered, the threshold for action, the chosen treatment, its accountable owner and the date the estimate expires. That record lets a later reviewer see whether the exposure changed—or whether the organization simply changed how it scored the same facts.
SPOG.AI’s GRC solution connects risk records with requirements, controls, evidence and ownership. Its Continuous Control Monitoring solution can provide operational evidence about selected control coverage and effectiveness. Exposure Management connects exposure priorities with business context. These capabilities can inform an assessment record; they do not select a quantification model or generate validated loss estimates.
Select a method by the decision it must support, the reliability of its evidence and the uncertainty leaders need to see. Keep qualitative judgments honest, semi-quantitative scores local, and quantitative estimates tied to explicit scenarios and assumptions. Test one decision first, record what would change the result and expand only when the analysis improves the choice.

Cyber risk quantification expresses possible cyber losses in numerical terms, often money, for a defined scenario and period....
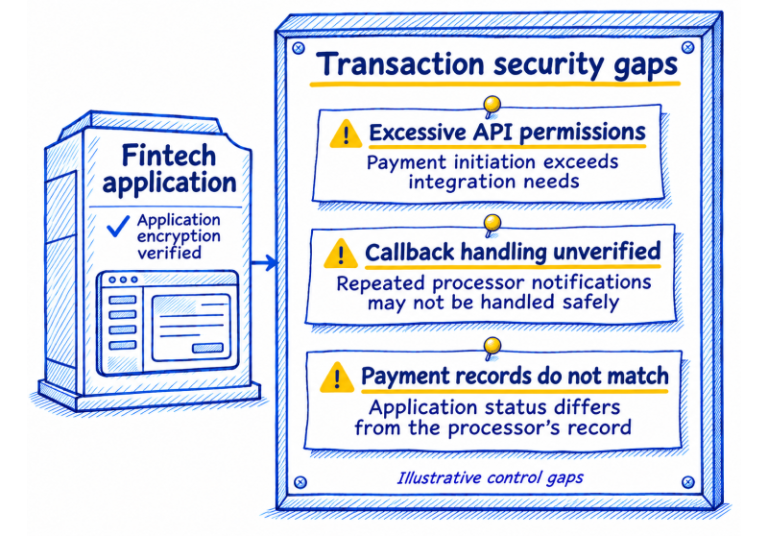
Fintech startup security must protect money, identity and financial data across live workflows enterprise buyers depend on. A...
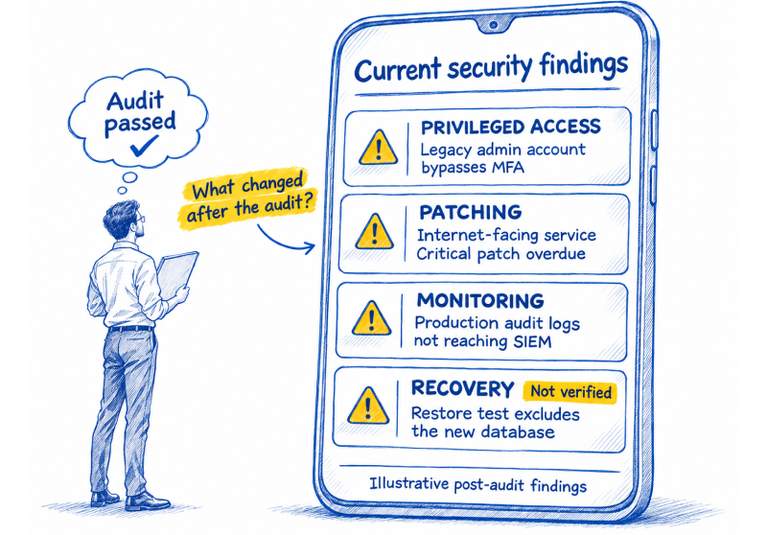
Balancing security and compliance to prevent cyberattacks requires more than passing an audit or buying another security tool....