Security Governance on a Budget: Where Mid-Market Teams Should Invest First
Make limited security budgets count by focusing on critical services, reliable evidence and accountable action. Learn how mid-market teams can identify control gaps and decide where better data, expertise, automation or remediation capacity will deliver the most value.
A customer asks whether every administrator has multifactor authentication. The identity dashboard looks healthy. Answering the question still takes days because nobody has reconciled its account list with cloud administrators, application accounts and local access.
The company owns security tools. It lacks a reliable way to establish the complete answer and act on the exceptions.
For mid-market teams, that distinction determines where the next security investment should go. Another reporting tool may accelerate evidence collection while leaving missing accounts unresolved. Inventory work, a named owner or targeted remediation may deliver more value.
Security governance on a budget means directing limited resources toward trustworthy decisions and verified action. Build the process around important services, applicable obligations and controls your team can operate consistently.
What effective security governance should deliver
Security governance establishes what the organization expects, who is accountable and how leaders determine whether security measures are working. A lean process should identify important services and obligations, the controls protecting them, supporting evidence, failure owners and authority to accept remaining risk.
NIST Cybersecurity Framework 2.0 provides an organizing structure that includes governance. Its Small Business Quick-Start Guide supports organizations beginning their cybersecurity risk management work. Tailor implementation to your environment. The practical test is whether the process produces decisions that people can implement and review.
1. Start with obligations and critical services
Establish which legal entities, services, locations and customer commitments are in scope. Separate applicable legal and regulatory requirements, contractual commitments, voluntary assurance objectives and internal security expectations.
Record why each requirement applies, its accountable owner, relevant scope and deadline. Where applicability is uncertain, obtain qualified advice before building extensive control mappings.
ISO/IEC 27001 defines requirements for an information security management system. SOC 2 is an examination and reporting service concerning controls at a service organization. They address different assurance needs and should not be treated as interchangeable certifications.
Identify services whose disruption, compromise or data loss would materially affect the business. Include supporting infrastructure, privileged identities, applications and important supplier dependencies. A production administration gap may warrant attention before documentation improvements for a low-impact system. Budget constraints do not remove mandatory obligations.
2. Define a manageable control set
Select an initial control set based on material risks and applicable obligations. Candidate areas include privileged access, endpoint protection, vulnerability treatment, recovery and incident response. The correct starting set depends on the organization.
CIS Implementation Group 1 provides a foundation of essential cyber hygiene. Treat it as a starting reference, then assess whether exposure and obligations require additional safeguards. For each selected control, create a record another person can operate.
Control record field
What to specify
Objective
The outcome the control must achieve.
Population
Accounts, assets, services or transactions covered.
Evidence sources
Systems and records used for assessment.
Test method
How coverage and operational outcomes are checked.
Timing
Collection interval, review frequency and change triggers.
Evidence validity
Completeness checks and acceptable evidence age.
Accountability
Operator, control owner and reviewer.
Failure response
Remediation, escalation and interim safeguards.
Exception rules
Authorized approver, conditions and expiry.
Closure criteria
Evidence required to verify the outcome.
Keep the record concise, but make limitations explicit. An identity export excluding local administrators cannot represent the complete privileged account population.
3. Reuse evidence only where it fits
A single access review may support several assurance needs. Before reuse, check that relevant systems and accounts are included, dates or periods are represented, the test addresses the expected outcome and additional approvals or procedures are covered.
An authentication settings export does not establish that every application enforces those settings. A completed access-review task does not establish that rejected access was removed. Retain the source record, collection time, test method, reviewer conclusion and remediation evidence.
The efficiency comes from operating a dependable control once and tracing its evidence accurately across requirements.
4. Separate coverage from operational effectiveness
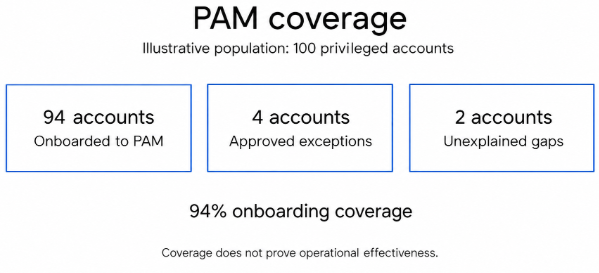
Consider an illustrative population of 100 privileged accounts: 94 are onboarded to PAM, four have approved exceptions and two have unexplained onboarding gaps. PAM onboarding coverage is 94%. Exception approval does not increase that figure.
Next, test whether PAM operates as required for the accounts it covers. Depending on the objective, tests may include password rotation, access policy enforcement and governed access paths. An onboarded account can still fail an operational test.
Assessment dimension
Question it answers
Coverage
Does the control include its intended population?
Configuration
Are required settings and policies in place?
Operation
Do relevant functions work as expected?
Exceptions and gaps
What remains outside the expected state, and why?
Evidence confidence
Is the assessment based on complete and current information?
If collection fails or evidence becomes too old, label the result stale or unknown. Do not automatically carry a previous pass forward. Report important failures individually: a high aggregate percentage can conceal an account with broad production privileges.
5. Assign decisions to people with authority
A GRC coordinator organizes evidence and tracks actions. System and business owners must still perform remediation and make accountable risk decisions.
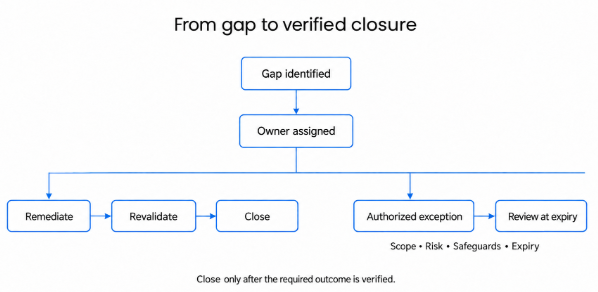
Identify the control owner accountable for the outcome, the remediation owner performing the fix, the business risk owner accountable for consequences, the authorized exception approver and the reviewer checking closure evidence. A small organization may combine roles; use second-person review for material approvals and closures where practical.
An exception record should include scope, reason, residual risk, compensating measures, owner, approval and expiry. Define earlier review triggers such as increased privileges, a service change or failure of a compensating measure. Internal approval cannot waive an applicable legal obligation.
Close a finding when revalidation demonstrates the required outcome. Ticket completion alone is insufficient.
6. Fund the bottleneck that prevents progress
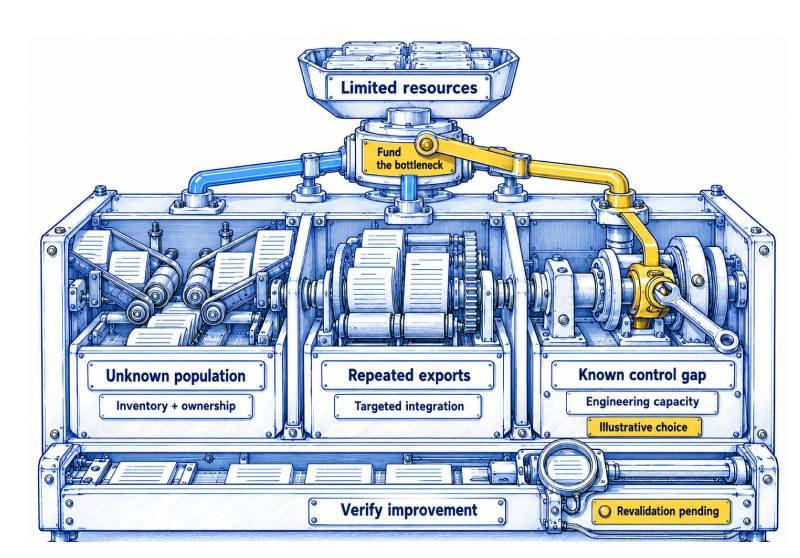
Follow one important control from evidence collection to closure. Identify where the process breaks before buying another tool.
Observed problem
First investment
Evidence of improvement
Unknown population
Inventory reconciliation and ownership
Unmatched records investigated; blind spots explicit.
Repeated exports
Targeted integration or scheduled collection
Evidence arrives; collection failures detected.
Unassigned findings
Ownership and escalation
Findings reach accountable owners within agreed times.
Disputed applicability
Specialist scoping advice
Documented decision and rationale.
Unresolved known gaps
Engineering capacity or safeguard
Revalidation confirms improvement.
Reports without decisions
Management review design
Decisions, owners and deadlines followed through.
Fund the work that changes the decision or outcome. Mapping maintenance, integration support and investigation consume capacity even when collection is automated. If detection outpaces resolution, expanding monitoring can increase the backlog. Address ownership and remediation capacity alongside detection.
7. Pilot automation against a known failure
Choose a control with meaningful risk, an identifiable population and an owner able to act. Establish the manual baseline across collection, reconciliation, review, follow-up and closure.
Test whether automation collects required evidence, reconciles the population, detects a known gap, identifies stale or missing data, routes the finding, preserves an exceptional decision and rechecks the state after remediation.
Agree acceptance criteria before the pilot: completeness, accuracy, traceability, maintenance effort and decision usefulness. A demonstration must explain failures and uncertainty as clearly as passing results.
8. Compare the full operating cost
Use the same scope and planning period. Include license, implementation, integrations, maintenance, internal operating effort and specialist support. Compare a controlled manual process, existing platform features and a dedicated GRC platform against the same requirements.
A spreadsheet can support an early process where access, versioning and accountability are managed. Repeated reconciliation errors, lost approvals and untraceable changes indicate a need for stronger support.
Define specialist deliverables, handover and continuing responsibilities. Do not build a business case from promised percentage savings alone; measure the work your organization performs.
9. Report decisions and exposure to leadership
For priority services, report material failures, evidence blind spots, business consequences, current safeguards, remaining exposure, accountable owners, proposed actions and decision deadlines.
Track time to assign findings, overdue remediation, expired exceptions and stale evidence. Measure efficiency separately: faster evidence preparation does not establish reduced security risk. Choose a review cadence suited to risks and obligations, and escalate immediate material failures when they arise.
How SPOG.AI can support this approach
SPOG.AI’s published materials describe connecting requirements, controls and operational evidence, identifying coverage gaps, governing exceptions and supporting accountable remediation. Evaluate these capabilities against your own systems and scope.
Bring one priority control, its expected population and a known gap to the demonstration. Ask to see evidence, ownership, exception decisions and the post-remediation check. Confirm supported integrations and ongoing operating effort.
Book a SPOG.AI demo to evaluate one priority control across your existing environment.
Make the next investment defensible
Start with an important service and a control whose outcome matters. Establish the population, validate evidence, assign decision rights and test what happens when the control fails. Use that experience to choose better data, automation, expertise or remediation capacity. Sustainable governance makes the choices explicit and verifies whether investment achieved its purpose.
Frequently asked questions
It defines security expectations, accountability, evidence review and risk decision authority, connecting business priorities with security control oversight.
Start with priority services, reuse suitable evidence and assign operational work to system owners. Automate validated checks while confirming capacity to handle findings.
Prioritize applicable obligations and material business risks. The starting set depends on service criticality, exposure, data sensitivity and existing safeguards.
No. A controlled register and existing reports can support an initial process. A platform becomes relevant when evidence volume, reconciliation and tracking exceed sustainable manual capacity.
Yes, where scope, dates and tested outcomes fit each requirement. Mapping alone does not establish sufficiency.
Approval records a risk decision. It does not prove the primary safeguard is deployed or working. Report exceptions separately and assess compensating measures.
Coverage measures inclusion. Effectiveness assesses whether the control achieves its expected outcome. A covered asset can fail an operational test.
Someone with the required delegated authority. The accountable risk owner must understand exposure, conditions and review requirements.
Compare the same scope and tasks before and after automation, including collection, reconciliation, review, follow-up and maintenance.
Material exposure, affected services, evidence limitations, accountable owners and decisions requiring authority or funding. Keep important failures visible alongside aggregate metrics.
With 8.5+ years in B2B SaaS, I’ve led demand generation and GTM initiatives across global markets (US, UK, Europe, Africa), helping companies move from fragmented marketing efforts to structured, revenue-focused growth engines.