A 90-Day GRC Roadmap: From Scope and Ownership to Verified Controls Across Teams
Establish a first GRC voyage in 90 days, with clear scope, accountable owners and evidence that supports control decisions. Follow three practical phases to assess priority controls, verify remediation and give leadership a clear view of unresolved risk.
A board asks whether a critical service is adequately protected. The GRC team has policies, assessment responses, and completed tickets. Yet nobody can show which controls covered the service, what was tested, or which gaps still require a decision.
That is the problem a first GRC implementation cycle should solve.
A 90-day GRC roadmap should establish an evidence-backed way to govern a defined scope: identify applicable requirements, assign control ownership, evaluate operation, and act on the results. Its value is the ability to make a defensible decision about a priority service.
By day 90, leadership should be able to answer:
What is in scope, and what remains outside this assessment?
Which priority controls are working, failing, or unverified?
Who owns the remaining exposure?
What action, funding, or risk decision is needed next?
This roadmap focuses on cybersecurity and technology GRC. Enterprise governance may also require financial, legal, privacy, conduct, and other specialist workstreams.
What can a GRC program achieve in 90 days
With an executive sponsor, available control owners, and access to relevant systems, one quarter can establish a first operating cycle for a manageable scope.
It cannot guarantee certification, regulatory compliance, or enterprise-wide assurance. Required assessment periods, major remediation, procurement, and organizational change may extend beyond the quarter.
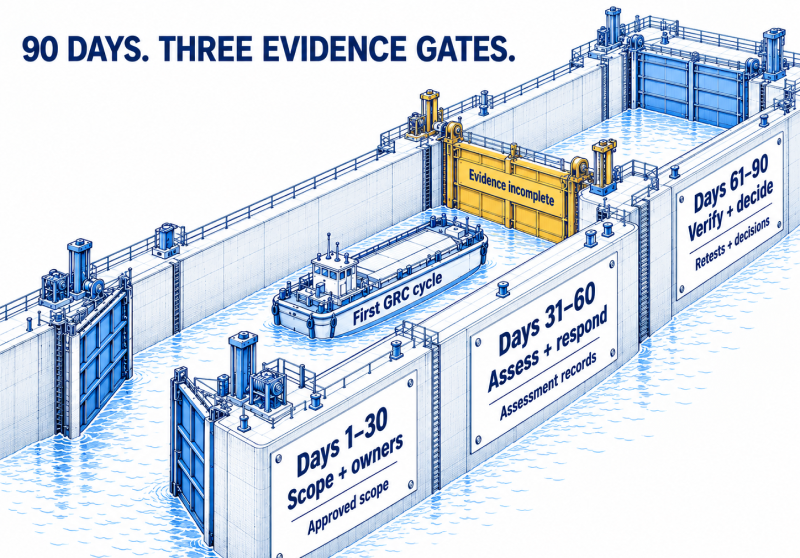
The dates organize the work. The gates determine whether the work is credible.
If a gate remains incomplete, record the blocker, its consequence, and the person responsible for resolving it. Work can continue elsewhere, but the unresolved area must remain visible.
Days 1 to 30: Define the scope and the decisions
Establish the mandate
Start with the business decision driving the program. Examples include approving a service launch, addressing a material audit finding, or demonstrating oversight of a critical supplier. The executive sponsor should approve:
The first-cycle objective and boundary.
Available operating-team capacity.
Risk acceptance and escalation authority.
The leadership review date.
The GRC lead coordinates the program. Operational teams own the controls they operate; authorized risk owners decide whether remaining exposure is acceptable.
Build an applicability and risk baseline
Identify the legal entities, services, systems, data, locations, and third parties within the boundary. Record dependencies outside it where they affect the assessment.
Create a requirements register with the source, applicability rationale, obligation owner, and relevant deadline. Legal or compliance specialists should resolve uncertain regulatory applicability.
Then describe priority risk scenarios. “Weak access management” is too broad. “A departed administrator retains access to the production payment service” gives the team a consequence and a testable control objective.
Select the first control set using:
Applicable obligations and deadlines.
Potential business harm.
Known findings and incidents.
Changes to services or dependencies.
Uncertainty about control operation.
Available evidence helps plan assessment efforts. Its absence must not cause a material risk to disappear from the priorities.
For organizations using NIST CSF 2.0, Current and Target Profiles can help describe the present position and prioritize desired cybersecurity outcomes. They provide a planning structure rather than a certification result.
Turn priority controls into assessable records
Field
What to record
Objective
Behavior or outcome the control must achieve
Requirement
Applicable obligation and mapping rationale
Population
Services, assets, identities or transactions covered
Ownership
Operator, reviewer and decision authority
Assessment
Method, frequency, period and acceptance criteria
Evidence
Authoritative sources and known limitations
Response
Escalation, remediation and exception rules
Separate design adequacy, implementation coverage, and operating effectiveness. A well-written procedure can be poorly deployed. A deployed control can fail during operation.
Day-30 gate: The sponsor approves the scope and priorities. Each priority control has an objective, accountable owner, and assessment plan. Missing populations or evidence sources are assigned as explicit blockers.
Days 31 to 60: Establish evidence and response
Define what evidence must demonstrate
Choose assessment methods that fit the objective. Reviewing configuration may establish a setting; assessing whether the control operated over time may also require transaction records, interviews, or testing.
NIST SP 800-53A provides a formal control-assessment methodology. Its examine, interview, and test methods are useful reference points when designing assessments appropriate to the organization.
For each assessment, record:
Population and period assessed.
Evidence source and extraction time.
Method, including sample selection where applicable.
Expected result and observed result.
Reviewer, conclusion, and limitations.
A sample supports a conclusion about the assessed sample. Broader conclusions require a justified selection method and adequate coverage. A current snapshot also does not establish uninterrupted operation throughout an earlier period.
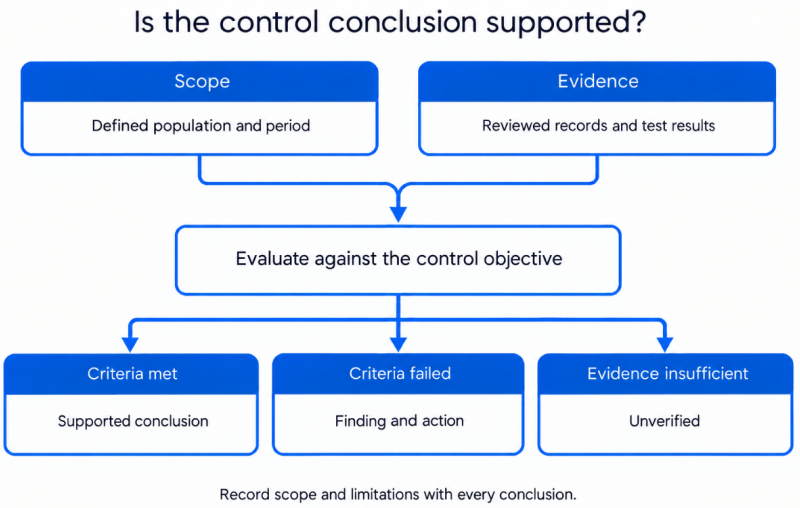
Use clear assessment outcomes:
Met: sufficient evidence supports the defined criteria.
Not met: evidence demonstrates a failure against the criteria.
Unverified: evidence is insufficient to conclude.
Not applicable: exclusion is justified and approved.
These are proposed working labels. Adapt them to the required assessment scheme.
Worked example Removing access when someone leaves
Illustrative scenario. The objective is to remove a departing worker’s access to in-scope production services within the organization’s approved deadline.
Assessment element
Practical approach
Population
Departures during the period, including relevant contractors
Reconcile departures to access records and compare removal timestamps with the deadline
Failure
Access remains active or was removed late
Evidence gap
An application cannot provide account status or removal history
Closure
Confirm removal and assess whether the process failure could recur
Disabling the central identity account may leave local or independently managed accounts active. The assessment must follow the service’s actual access paths.
A missing application export creates an assurance gap. It does not prove access was retained, but it prevents a complete conclusion.
Caption: A control conclusion depends on both the observed result and sufficient evidence about the intended population.
Create a response process that preserves risk decisions
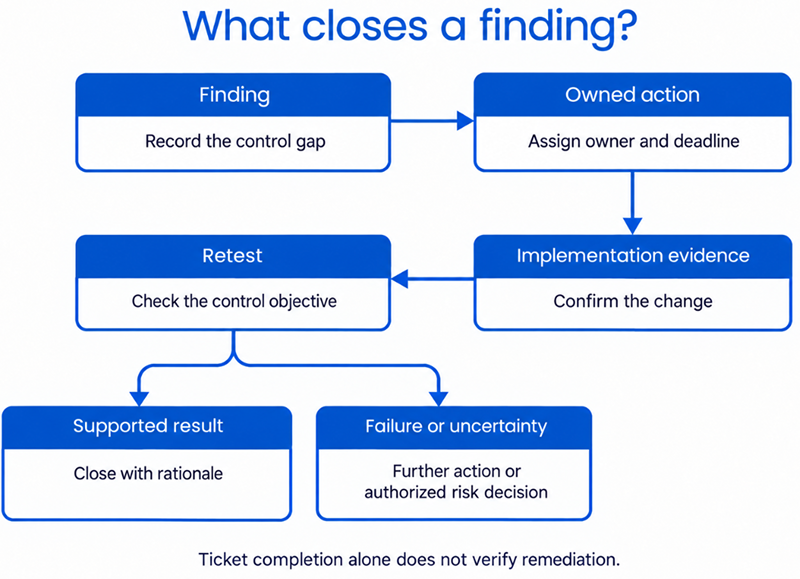
A finding should identify the affected service, control objective, consequence, accountable owner, deadline, and required verification. Keep three records connected:
Finding: what failed or could not be established.
Remediation action: what will change.
Risk decision: how remaining exposure will be treated.
Where an exception is permitted, record its scope, rationale, compensating measures, approver, owner, expiry, and review triggers. Test the compensating measures where relevant.
An approval records a decision about exposure. It does not make a failed control pass or waive a mandatory obligation.
A technical ticket should close only when its completion evidence is available. Closing the associated finding may require a separate retest.
Automate a validated process
Connect evidence sources after the population, assessment logic, and response responsibilities are clear. Check each connection for:
Coverage of the intended scope.
Correct account and asset matching.
Permissions and extraction completeness.
Refresh frequency and failed collections.
Preservation of review-period evidence.
An unavailable feed should make assurance visibly uncertain. It must not silently preserve a healthy result.
Day-60 gate: Priority controls have completed their planned assessment cycle, or have a documented reason why they could not. Material findings have owners and response decisions. Unverified areas remain visible.
Days 61 to 90: Challenge the conclusions and govern the next cycle
Review the path from requirement to decision
Ask a reviewer outside the control’s daily operation to challenge selected conclusions. Where team size limits independence, document the limitation and arrange appropriate oversight. Include:
A control reported as effective.
A control with a previous failure.
An approved exception.
An area with incomplete evidence.
A recently changed service or dependency.
Trace the requirement, population, evidence, assessment, finding, and decision. Check whether the conclusion actually follows from the record.
For completed remediation, verify the changed state and whether the original failure mechanism has been addressed. One successful retest may support a limited conclusion; sustained effectiveness may require further observation.
Report what leadership needs to decide
Avoid an overall compliance percentage that hides critical failures or unknown scope.
Reporting view
Definition
Decision supported
Assessment coverage
Assessed population ÷ identified in-scope population
Further assessment
Test results
Met, not met, unverified; assessment period
Controls needing attention
Evidence status
Missing, stale, incomplete, unavailable
Unreliable assurance
Open findings
Severity, service, age, owner, deadline
Intervention or funding
Exceptions
Scope, measures, expiry, exposure
Continued acceptance
Verified remediation
Retested actions and conclusion
Supported closure
State the denominator and its limitations. An incomplete inventory limits the confidence of any coverage percentage.
Show approved exceptions separately. If a reporting method excludes them from a calculation, disclose that rule and retain a view of the full population.
Each material item should end with a requested decision, a decision owner, and a date.
Agree the next operating cycle
Leadership should approve the next scope, unresolved priorities, resources, and review schedule.
Set review frequency according to the control, obligation, and rate of change. Also define event triggers such as a new service, acquisition, supplier change, incident, or material control failure.
Day-90 gate: Leadership has reviewed the evidence-backed position, decided how to treat material exposure, and approved the next cycle. Areas still lacking assurance remain explicitly unresolved.
Where SPOG AI supports the roadmap
SPOG.AI’s published GRC offering describes connections between requirements, controls, operational evidence, ownership, and exceptions. Its Continuous Control Monitoring offering describes assessment of control coverage and effectiveness using operational evidence.
These capabilities can support evidence review and accountable follow-up once the organization has defined its scope and assessment criteria. The available sources, mappings, refresh intervals, and workflows should be confirmed for the implementation.
Explore SPOG.AI’s GRC capabilities or book a demo using one priority service and its control evidence as the starting point.
What success looks like after day 90
A useful first quarter produces a defensible view of a defined scope: what was assessed, what the evidence supports, what remains uncertain, and who owns the next decision.
Extend coverage using that working process. Revisit conclusions when services change. Review accepted exposure before exceptions expire. Verify completed remediation.
The program becomes durable when operating teams produce evidence routinely and leadership uses it to make decisions.
Frequently asked questions
It is a staged plan for establishing governance, risk, and compliance practices within a defined scope. It connects applicable requirements, control ownership, assessment evidence, findings, and decisions.
A timeline alone cannot establish compliance. The result depends on applicable obligations, existing practices, scope, remediation needs, and required evidence periods.
An approved scope, requirements baseline, priority risk scenarios, named control owners, and assessment plans. Unresolved dependencies should have owners and deadlines.
An executive sponsor provides authority and resources. The GRC lead coordinates the program, operational teams own controls, and authorized risk owners make risk decisions.
Prioritize controls connected to material obligations, significant business consequences, known failures, and changing services. Evidence availability informs the assessment plan, but should not override risk importance.
Evidence must support the control objective for the relevant population and period. Depending on the control, this may include configuration, activity records, transaction samples, interviews, and test results.
Approval records an authorized decision about a deviation. It does not establish effectiveness or waive a mandatory obligation. Remaining exposure and compensating measures still require oversight.
Yes, where it supports each requirement’s scope, criteria, and period. A mapping alone does not establish that the requirements are equivalent.
Assessment coverage, control results, evidence limitations, material findings, exceptions, and verified remediation. Each metric needs a clear definition and a connection to a decision.
After defining the population, assessment logic, evidence standard, and response ownership. Validate collection completeness and refresh behavior before using automated results for assurance.
Technology writer and content strategist with 5+ years of experience, including work for a US-based B2B SaaS client and a cybersecurity solution. I create cybersecurity and GRC content, product documentation, and user guides that help technical teams and business leaders understand security capabilities and workflows. Currently working on Confluence documentations on vulnerability management, ITSM, incident management, and continuous control monitoring, alongside SEO and AEO content, and technology partner database development.