ISO 27001 in 2026: Keep Controls Aligned as Business Changes
An effective ISO 27001 program keeps control scope, the Statement of Applicability and supporting evidence aligned as services, identities and suppliers change. Clear ownership, checks on coverage and effectiveness, and regular exception reviews help security and GRC teams identify gaps and maintain an ISMS that reflects current business risks.
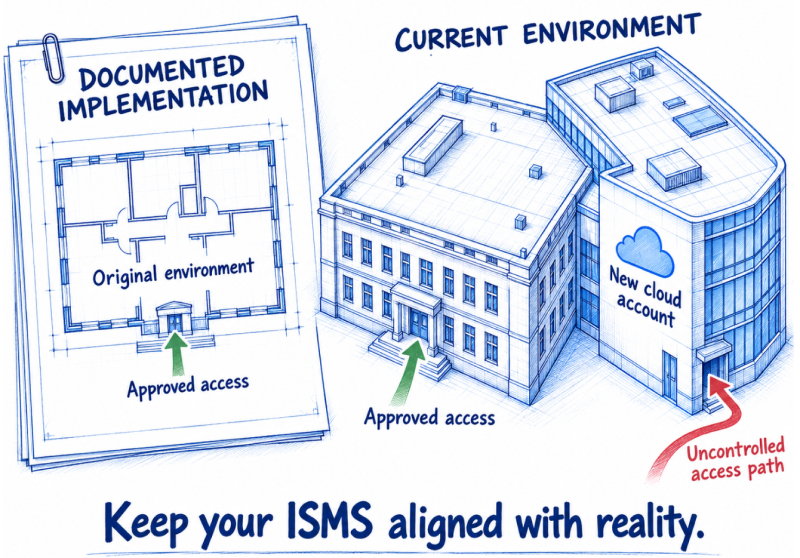
The documentation has not changed. The environment has.
This is the practical challenge for ISO 27001 in 2026: keeping an established information security management system (ISMS) aligned with the services, identities, suppliers and risks the organization manages today.
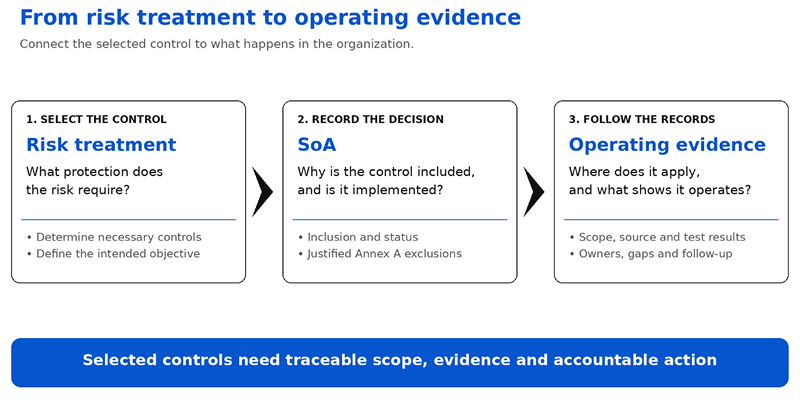
The priority is to connect the controls selected through risk treatment with their actual scope, operating evidence, accountable owners, and unresolved gaps.
Which ISO 27001 version applies in 2026?
ISO/IEC 27001:2022, with Amendment 1:2024, is the current published edition. There is no separate ISO/IEC 27001:2026 edition.
The transition deadline for accredited ISO/IEC 27001:2013 certifications was 31 October 2025. Organizations maintaining certification should confirm their certificate’s current edition, validity, and scope with the issuing certification body.
The 2022 revision aligned Annex A with ISO/IEC 27002:2022 and introduced clause 6.3 on planning changes to the ISMS. Its reference set contains 93 controls across four groups:
Annex A group
Controls
Examples of areas covered
Organizational
37
Governance, suppliers, incident management, and continuity
People
8
Employment responsibilities, awareness, and reporting
Physical
14
Facilities, physical access, and equipment
Technological
34
Access, configuration, monitoring, development, and data protection
The reduction from 114 controls does not represent 21 security practices that organizations can discard. Controls were reorganized, merged, and updated.
The 2024 amendment adds a requirement to determine whether climate change is relevant to organizational context and a note about related interested-party requirements. It does not add Annex A controls.
These facts establish the baseline. The more consequential question is whether your implementation remains accurate as the business changes.
1. Keep control scope current
A control can continue working on its original population while new assets remain outside it.
Control scope means the assets, accounts, services or activities that a particular control should cover within the ISMS. Review this population as the environment changes.
Endpoint protection may be healthy on enrolled devices, but recently acquired devices may never have enrolled. A privileged access workflow may operate correctly for known administrators while new cloud roles bypass it. Backup jobs may succeed for configured systems while a new critical service remains unprotected.
This is why coverage needs a reliable denominator: which assets, accounts, services, or activities should the control cover?
For each priority control, establish:
The service and risk it supports.
The population that should be covered.
The source used to identify that population.
The expected control state.
The owner responsible for investigating differences.
Then define events that trigger review. Examples include a new cloud account, SaaS service, supplier, acquisition, privileged role, or material system change.
This does not mean rewriting the SoA whenever an account is created. Keep detailed operational inventories linked to the control implementation. Review the SoA when the change affects applicability, implementation status, or the rationale recorded there.
2. Keep the SoA aligned with current control implementation
The Statement of Applicability (SoA) records necessary controls, their inclusion rationale, implementation status and justified Annex A exclusions. Review these entries when business or technical changes affect the decisions they describe.
Keep detailed asset and account inventories linked to the relevant implementation records. A new account may require an inventory update without changing the SoA. A change in control applicability, implementation status or rationale may also require a SoA update.
For each applicable control, maintain a clear connection between the SoA entry, its owner, implementation and supporting evidence. This helps keep the documented decisions aligned with how controls operate today.
3. Distinguish coverage, health, and effectiveness
Coverage, health, and effectiveness are practical assessment dimensions, not three formal categories prescribed by ISO 27001. They reveal different weaknesses:
Question
What it establishes
Example
Coverage
Does the control reach the intended population?
Are all in-scope privileged accounts included?
Health
Are the mechanisms supporting the control operating?
Are required password rotation jobs completing?
Effectiveness
Does the control achieve its defined objective under the conditions tested?
Can unauthorized privileged access still occur?
A deployed tool does not answer all three.
For example, a PAM inventory can show which accounts are onboarded. Job records can show whether rotation is succeeding. Testing access outside the approved route can reveal whether the intended restriction actually holds.
The test should match the objective. A successful backup job establishes something different from a successful restore. Enabled logging establishes something different from a tested detection and response path.
Also distinguish failed from unknown. If an evidence feed is stale or a critical population cannot be reconciled, the result lacks sufficient support. It should not silently remain green.
4. Treat exceptions as governed decisions
An exception is an ongoing risk decision with defined boundaries. Record its scope, rationale, accountable risk owner, approver, alternative measures where relevant, and review or expiry date. Keep approved deviations distinguishable from unexplained gaps.
Review which exceptions remain valid, which have expired and which depend on assumptions that have changed. Where protection depends on an alternative measure, retain evidence that it operates as intended.
Repeated exceptions affecting the same control should inform risk assessment and management review. Leadership may need to address a recurring dependency, ownership gap or resource constraint.
Example following a new cloud account through to closure
Consider a new production cloud account supporting a customer-facing application. This is an illustrative scenario, not a reported customer result.
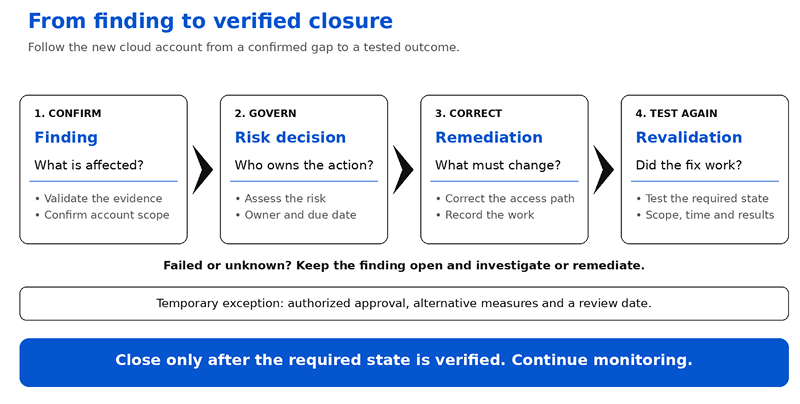
The account appears in the cloud inventory but is missing from the population used to assess privileged access. The team confirms that it falls within the existing ISMS scope and that the selected access controls apply. It updates the operational inventory and checks whether the SoA still accurately describes the implementation.
Validation finds a direct administrator access path outside the approved privileged access workflow. The security team records the finding, links it to the application and affected identities, and assesses the consequence of unauthorized access. The application owner and risk owner agree on remediation, ownership, and a due date under the organization’s procedure.
Where immediate correction could disrupt the service, the authorized risk owner decides whether temporary alternative measures are acceptable. Any exception records its scope, approver, measures, and review date. It remains visible as a deviation from the intended state.
After the access path is corrected, the team tests authorized access through the intended workflow and verifies that access outside it is blocked. It retains the account scope, test time, and results before closing the finding. The next assessment includes the new account, preventing the same population gap from recurring.
5. Give management review decisions, not just percentages
A dashboard showing “controls implemented” is an incomplete basis for leadership oversight.
For critical services, management needs to understand:
Which material control gaps remain.
Which results are unknown because evidence is incomplete.
Which exceptions are approaching or exceeding their review dates.
Which remediation efforts require resources or escalation.
Whether repeated failures indicate a weakness in the process itself.
A coverage percentage should identify its population and measurement time. Trends should use consistent definitions or explain changes in scope.
If a service expands, coverage can fall even when every previously protected asset remains protected. That is valuable information: the organization has grown faster than the control’s reach.
For example, if the same onboarding gap affects several critical services, management may need to fund an automated enrollment check, assign responsibility for reconciling inventories, or escalate overdue remediation.
What do the 11 new controls mean for ongoing operations?
The controls introduced in the 2022 revision remain relevant, but “new” describes their relationship to the earlier reference set. It does not mean the practices were invented in 2022.
They cover:
Area
Controls introduced in the 2022 revision
Intelligence, cloud, and continuity
Threat intelligence; information security for use of cloud services; ICT readiness for business continuity
Physical protection
Physical security monitoring
Configuration and data protection
Configuration management; information deletion; data masking; data leakage prevention
Monitoring and engineering
Monitoring activities; web filtering; secure coding
For applicable areas, examine the implementation rather than just the mapping.
For cloud services, consider how security responsibilities and controls operate through acquisition, use, change, and exit. For configuration management, compare actual states with approved baselines. For monitoring, examine critical-system coverage, feed health, and whether alerts reach an accountable response process.
A mapped control is a reference. Evidence and review establish whether its implementation remains appropriate.
Where continuous control monitoring helps
Continuous control monitoring can help teams assess selected controls as operational evidence changes. It is particularly useful where assets, identities, configurations, and technical states change between scheduled reviews.
It still depends on:
Defined objectives and acceptable states.
Accurate scope and asset relationships.
Reliable evidence sources.
Appropriate assessment frequency.
Owners who act on findings.
ISO 27001 does not require a particular continuous monitoring platform or real-time testing of every control. Select a monitoring and testing approach proportionate to the risk and the nature of the control.
SPOG.AI connects operational evidence with controls, affected assets, risk context, ownership, exceptions and remediation. This helps security and GRC teams maintain visibility into control coverage, evidence freshness, unresolved gaps and accountable actions as the environment changes. Available coverage depends on connected systems, evidence sources and configured assessments.
What to review next
Start with one critical service. Confirm the population each priority control should cover, whether the evidence is current enough to support a decision, and who owns any gaps or unknown results. Set the next review date and revisit these conclusions sooner if services, identities, suppliers or control implementations change.
In 2026, a useful ISO 27001 program can explain more than which controls were selected. It can explain how those controls operate as the organization changes, what remains uncertain, and who is responsible for the next action.
For audit preparation and external audit stages, review the requirements for ISO 27001 certification. For validating the security outcome of a specific change, apply ISO 27001 change management practices.
See how SPOG.AI connects control evidence, risk, and remediation.
Request a demo at spog.ai/demo.
Frequently asked questions
No. ISO/IEC 27001:2022, with Amendment 1:2024, is the current published edition. “ISO 27001 in 2026” refers to applying and maintaining the standard during 2026.
The transition deadline for accredited ISO/IEC 27001:2013 certifications was 31 October 2025. Organizations should check their certificate’s current edition, validity, and scope with the issuing certification body.
Annex A contains 93 controls: 37 organizational, eight people, 14 physical, and 34 technological controls. The reduced count reflects reorganization, merging, and updates rather than a reduction in required security coverage.
Organizations determine necessary controls through risk treatment and compare them with Annex A to avoid omissions. The Statement of Applicability records necessary controls, inclusion rationale, implementation status, and justification for excluded Annex A controls.
Review it when changes affect necessary controls, applicability, implementation status, or inclusion and exclusion rationale. Keep operational inventories updated separately and linked to the relevant control implementation.
It added a requirement to determine whether climate change is relevant to organizational context and a note that relevant interested parties may have climate-related requirements. It did not add Annex A security controls.
No particular platform is required. Organizations define appropriate monitoring and evaluation methods. Continuous control monitoring can support selected controls where reliable operational evidence is available.
Coverage asks whether a control reaches its intended population. Effectiveness asks whether it achieves its defined objective under the conditions assessed. A tool can cover an asset while being configured or operated in a way that fails the objective.
Review exceptions on their scheduled review or expiry date, and sooner when affected services, access, dependencies or risks change. Confirm that the rationale remains valid and any alternative measures still operate as intended. Repeated exceptions affecting the same control should inform risk assessment and management review.
Management review should receive material control gaps, results unsupported by sufficient evidence, overdue exceptions, recurring failures and remediation requiring resources or escalation. Coverage figures should identify the assessed population and measurement time. Record resulting decisions, accountable owners and follow-up dates.
Technology writer and content strategist with 5+ years of experience, including work for a US-based B2B SaaS client and a cybersecurity solution. I create cybersecurity and GRC content, product documentation, and user guides that help technical teams and business leaders understand security capabilities and workflows. Currently working on Confluence documentations on vulnerability management, ITSM, incident management, and continuous control monitoring, alongside SEO and AEO content, and technology partner database development.