Vulnerabilities
Seven Critical PHP Vulnerabilities: Risks, Protection and Mitigation
Seven critical PHP vulnerabilities pose risks of remote code execution and service disruption. While patching is essential, which...


A financial services company completes its annual audit with no major findings. Backup records and sampled restoration tests support the assessed recovery controls. Six weeks later, a storage migration moves several payment-processing workloads to a new environment. Backup jobs still report success, but the migrated workloads have not undergone post-change restoration testing.
The audit was not necessarily flawed. The problem arises when leadership assumes its conclusions still apply to systems that have changed.
An audit evaluates defined criteria, systems and periods. A SOC 2 Type II examination assesses specified controls over a period, while ISO/IEC 27001 certification concerns the information security management system within its certified scope. Neither automatically proves that controls remain effective after infrastructure changes or that every applicable regulatory obligation has been met.
Auditors use procedures such as sampling, interviews, document reviews and testing. Their conclusions are limited by the assessed scope and evidence.
An audit can be valid even when current operational resilience remains unverified.
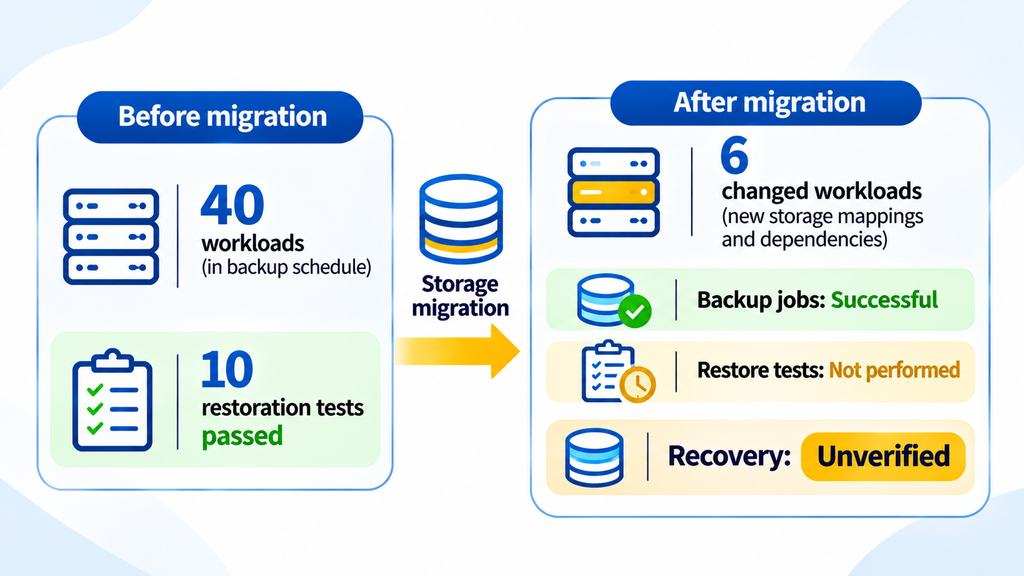
Consider an illustrative recovery review covering 40 business-critical workloads. Before migration, all 40 were included in the documented backup schedule, and 10 representative restoration exercises had met their defined objectives. After migration, six workloads use different storage mappings and recovery dependencies. Their backup jobs remain green, but none has a verified restoration result under the new configuration.
The earlier tests remain valid for what they examined. They cannot establish recoverability for the six changed workloads. Equally, missing tests do not prove recovery will fail. The outcome remains unverified. The control owner must identify affected systems and required recovery objectives. The authorized risk owner must decide how to manage the uncertainty until recovery is verified.
Backup success confirms job execution. Recovery effectiveness requires evidence that services can be restored within agreed objectives.
A reliable compliance statement identifies the applicable requirement, affected systems, evidence period, test scope, exceptions and accountable owner.
| Observed signal | Required assurance action |
| Audit pass | Retain assessed criteria, scope, period and qualifications |
| Storage or platform migration | Identify affected workloads and changed dependencies |
| Successful backup job | Confirm execution without assuming recoverability |
| Missing post-change restoration evidence | Report the affected recovery outcome as unverified |
| Failed restoration test | Investigate, remediate and retest |
| Approved interim exception | Document authority, safeguards, scope and expiry |
| Successful recovery retest | Update assurance for the tested configuration and scope |
Missing evidence and failed controls require different responses. Unavailable monitoring data limits what can be concluded; a failed restoration test demonstrates that the tested recovery objective was not achieved. Reporting these conditions separately helps management distinguish uncertainty from confirmed failure.
For a financial institution, unverified recovery is more than a technical concern. If migrated payment systems cannot be restored within agreed recovery objectives, the result may be prolonged transaction disruption, customer impact and increased operational risk. The previous audit may remain valid, but leadership could be making current risk decisions using evidence from an environment that no longer exists.
Management may also invest in additional backup capacity while overlooking the more urgent need to validate changed restoration paths. The appropriate response is a qualified assurance statement and a controlled recovery exercise, not an automatic declaration of noncompliance.
The control owner defines scope, acceptance criteria and evidence requirements. Technical teams identify dependencies, perform corrective work and conduct recovery tests. The business risk owner evaluates interim exposure within delegated authority, while independent assurance challenges whether the evidence supports the reported conclusion.
An exception should record affected workloads, rationale, compensating measures, approval authority, review date and expiry. Where binding obligations apply, internal risk acceptance cannot turn noncompliance into compliance.
Closing a migration ticket confirms a completed task, not a verified recovery outcome.
Before relying on earlier assurance conclusions, security and risk leaders should verify five conditions:
These checks help leadership determine whether earlier assurance remains reliable or requires further validation.
Ongoing compliance does not require repeating a full audit every day. Monitoring and testing frequency should reflect control objectives, environmental changes and the consequences of failure.
Backup execution can be monitored frequently, while restoration effectiveness requires appropriate testing, particularly after material changes. Governance activities such as risk acceptance and management review still require human judgment.
The same assurance problem extends beyond recovery. New privileged accounts, cloud configuration changes or newly acquired applications can alter control coverage without changing an approved policy or historical audit result.
The NIST Risk Management Framework includes ongoing control assessment and reporting through its Monitor step. ISO/IEC 27001 requires organizations to maintain and continually improve their information security management systems.
Continuous monitoring provides current evidence for defined conditions; it does not independently establish compliance with every obligation.
Maintaining assurance after an audit requires visibility into changed systems, current control evidence and unresolved risks. SPOG.AI connects these activities through its Governance, Risk & Compliance, Continuous Control Monitoring and Remediation capabilities.
Its GRC capabilities connect requirements, controls, evidence, ownership and exceptions. CCM supports visibility into defined control conditions across connected sources, while Remediation workflows help coordinate investigation, corrective action and validation.
In the migration scenario, this connected approach can help teams identify affected workloads, flag missing recovery evidence, assign validation responsibilities and track unresolved exposure.
SPOG.AI does not replace restoration testing. It helps organizations manage the evidence, responsibilities and decisions required for ongoing assurance, subject to connected-source coverage, configured scope and tests actually performed.
The board does not need to question a valid past audit. It needs to understand what has changed since then, which controls require fresh evidence and who is accountable for unresolved risks. An audit provides assurance for the conditions assessed. Maintaining compliance requires organizations to recognize material changes and verify whether earlier conclusions remain supportable.
Seven critical PHP vulnerabilities pose risks of remote code execution and service disruption. While patching is essential, which...
An approved policy can coexist with an unprotected business-critical system. The governance failure begins when leadership treats approval,...
Two critical NGINX HTTP/2 vulnerabilities pose remote code execution risks. Understand which systems are affected, how existing security...