Continuous Control Monitoring
Security Questionnaires: Respond with Accurate, Verifiable Answers
Security questionnaires help buyers understand how a supplier protects the data, systems and services involved in a proposed...
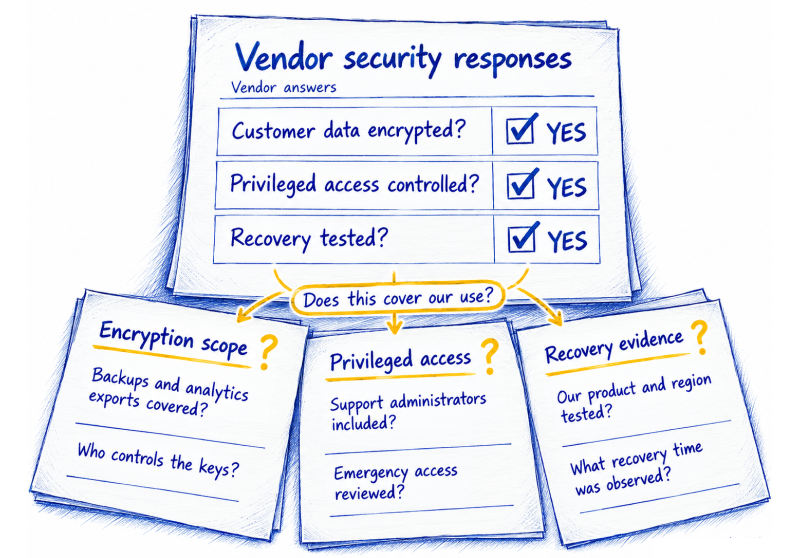
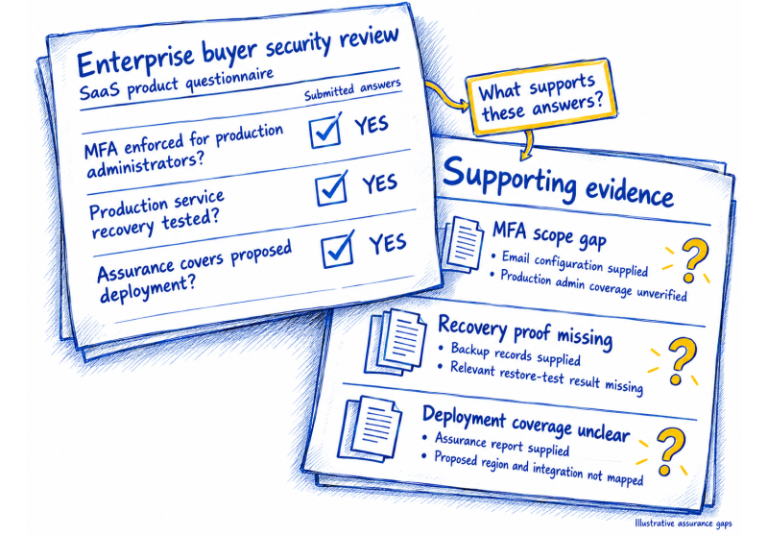
A long questionnaire can still leave the decision-maker guessing. “Yes, we encrypt data” does not show which data, where encryption applies, who controls the keys or whether the statement covers the environment your team will use.
Treat the inquiry as a short evidence interview, not a test of how many controls a vendor can name. The aim is to identify what is known, what remains uncertain and what condition would change the decision before the supplier receives data or access.
Before drafting questions, record the vendor’s purpose, data, connected systems, access, locations, downstream providers and dependent business process. One supplier can create different exposure across deployments, so assess the specific use rather than the company name alone.
This starting point keeps the request proportionate. A vendor with no sensitive data and no system access may need a brief baseline. A cloud platform integrated with production, customer records or privileged identities calls for deeper inquiry into the controls that protect that specific path.
NIST’s July 2026 due-diligence guide for information and communications technology suppliers identifies provenance, resilience, foundational cybersecurity practices, foreign ownership, control or influence, and supply-chain tiers as factors to consider. The guide supports informed due diligence; it is not a universal legal checklist for every organization or purchase. NIST SP 1326
A question earns its place when the answer can change a decision. State the claim, its boundary, acceptable evidence and the action if evidence is missing. A second reviewer should be able to reproduce the assessment.
Replace “Do you have a recovery plan?” with a request for the latest exercise covering the product, included systems and data, observed recovery time, open gaps and corrective owner. This asks for proof tied to your dependency, not a general policy statement.
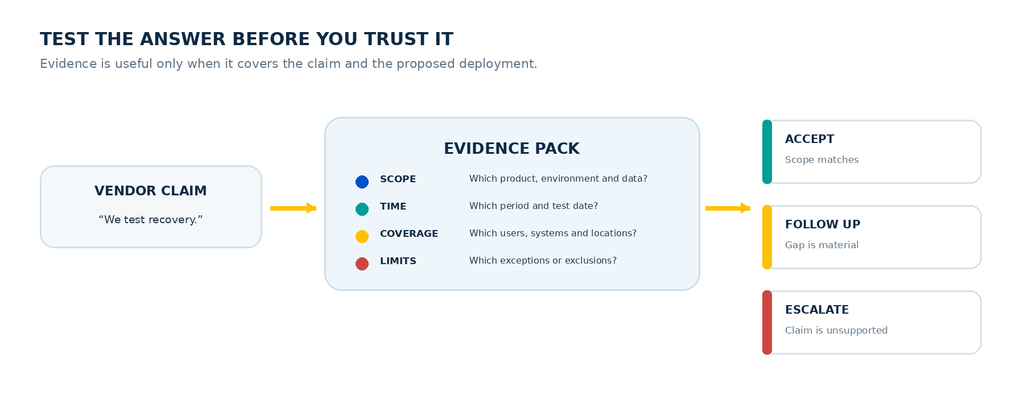
Ask the vendor to identify the evidence, date, scope, owner, exclusions and relevant findings. A current report may still be irrelevant if it covers a different product, region or operating model.
Use a small set of question areas as a starting point, then adapt them to the relationship. Do not send every supplier the same list simply because a template exists.
Ask what information the vendor receives, generates, stores or can view, and which systems, regions and downstream providers are involved. Request a data-flow view for your deployment. Confirm whether support staff or analytics features can access or reuse the data, and how the vendor follows retention and deletion instructions.
Ask how the vendor grants, reviews and removes employee or subcontractor access to your systems and information. For privileged access, request approval rules, authentication safeguards, session logging and a recent review sample. Find out how emergency access is approved and checked afterward.
Ask how the vendor finds, prioritizes and fixes vulnerabilities, including items that miss its targets. Request a redacted example showing a finding’s severity, affected component, owner and closure evidence. For software products, ask how it tracks third-party components and communicates material changes.
Ask who declares an incident, how the vendor identifies affected customers and what it can share as facts develop. Confirm notice channels, escalation contacts, cooperation expectations and update cadence. Request an exercise record or anonymized review showing how it coordinated containment and customer communication.
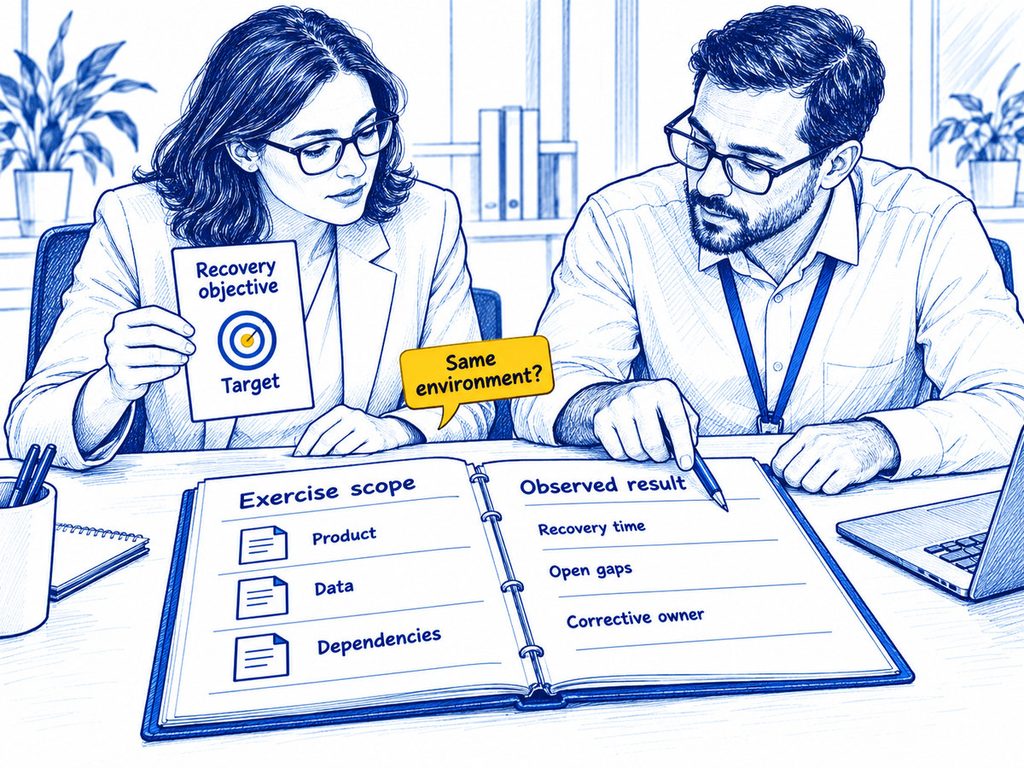
Ask which recovery objectives apply and whether an exercise tested the same architecture, data and dependencies. Request its date, scope, observed result, open gaps and corrective owner. A recovery-time objective is a target, not proof of restoration. If replacement is difficult, ask about workarounds or transition options.
Ask which subcontractors host, process or support the product, what role each plays and how material changes are reported. For technology, ask about component origin and traceability when relevant to your threat model. NIST SP 1326’s tier and provenance factors can help scope deeper inquiry; they do not require a full supply-chain audit for every purchase.
Check that evidence is current, covers the relevant product and deployment, and identifies exceptions. Read the scope of an assurance report or certification: its cover page cannot show whether the tested controls include your data path or whether a weakness remains open.
If a vendor cannot share a full report, ask for a scoped summary, redacted extract, independent attestation or live control review. Record what remains unverified. Confidentiality may limit the format, but it does not resolve the risk question.
Treat “not applicable” as a claim: ask why the control does not apply and what alternative safeguard addresses the risk. For “yes,” ask how the control operates and what the latest test found.
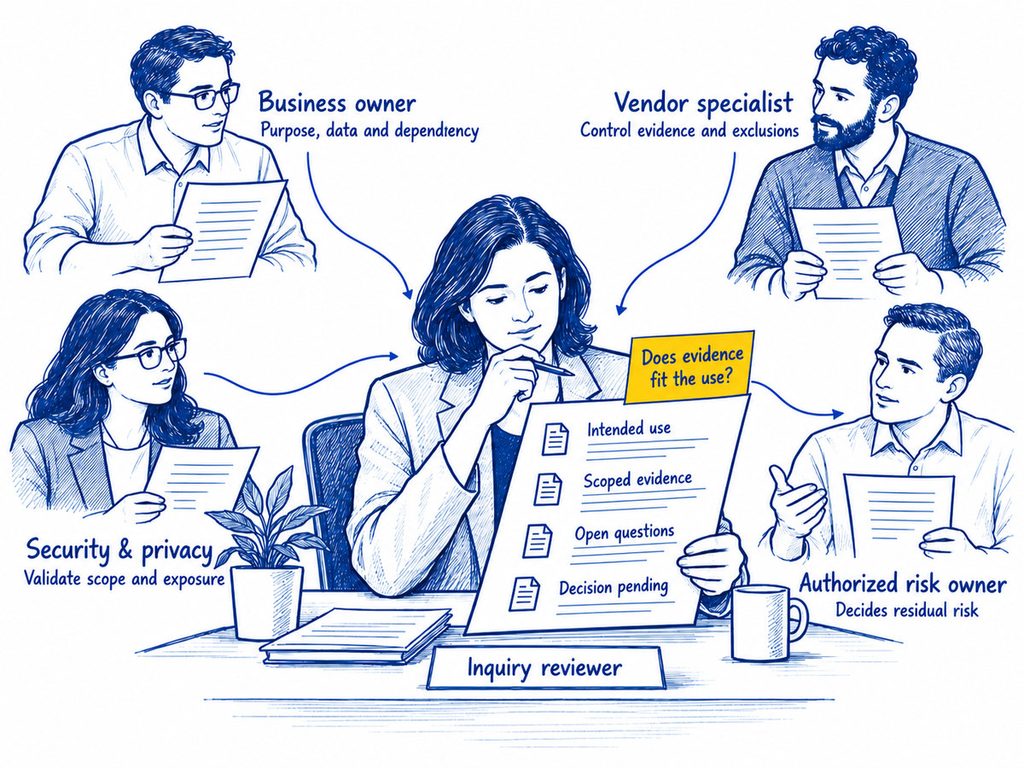
Close the inquiry with a documented disposition: proceed, proceed with conditions, defer pending evidence or decline. Record the business owner, evidence reviewed, unresolved gaps, compensating measures, authorized risk owner and review date. A questionnaire score alone should not approve a relationship or conceal a high-impact exception.
If the vendor cannot meet an expectation, ask what it can change, by when and how the change will be verified. Where the organization accepts residual exposure, the appropriate authority—not the questionnaire reviewer by default—should approve the exception. Put material commitments into contract terms and assign an internal owner to monitor them.
An answer is time-bound by its scope. New data use, expanded access, a product redesign, a material subcontractor change, a security incident or a shift in business dependency may invalidate the original conclusion. Define which events require notice, who validates the change and which questions need to be repeated.
Keep this loop practical: the business owner confirms whether the use changed, security and privacy review the affected controls, procurement or legal checks commitments, and the risk owner decides whether existing conditions remain adequate. Reassessing only on an annual calendar can leave a material change unexamined between cycles.
Vendor responses become more useful when teams can link them to internal risks, control owners and actions. SPOG’s GRC solution connects requirements, controls, evidence and ownership. Its Continuous Control Monitoring solution supports assessment of defined controls using operational evidence, while Exposure Management connects exposure with business, control and workflow context. These capabilities can support the organization’s review record; they do not independently verify a supplier’s claims or replace authorized risk decisions.
For broader relationship governance, see SPOG’s vendor risk management best practices. This inquiry guide stays focused on what to ask, what evidence makes an answer meaningful and how the answer should affect the decision.
A vendor cybersecurity inquiry should begin with the supplier’s intended role and end with a clear decision. Ask for evidence that matches the deployment, probe exclusions and unresolved findings, and state who owns the next action. The strongest question set is not the longest one; it is the one that makes a material uncertainty visible before the organization accepts it.


Security questionnaires help buyers understand how a supplier protects the data, systems and services involved in a proposed...

A vendor management policy sets the rules for approving suppliers, accepting exceptions and responding when relationships change. This...
Enterprise buyers expect SaaS startups to demonstrate how they protect customer data, identities, and business operations not just...