Data Classification Policy: Align Data Handling With Risk and Control Evidence
Define labels that guide access, sharing and disposal. This article explains how to apply them across data copies, assign decisions and connect handling controls to applicable framework requirements.
A data classification policy defines how information is categorized and the handling rules each category requires. It should help someone decide whether an export can enter a support workspace, which recipients may receive it and when the copy must be removed.
In 2026, those decisions extend across cloud platforms, SaaS applications, logs, backups and AI workflows. A dataset protected in production can become exposed through a troubleshooting attachment or development copy. The policy needs to follow those uses.
The practical question is whether the classification changes what happens to the information. Start with a manageable set of labels, define the required handling and test one data flow before expanding the program.
Separate confidentiality from other protection needs
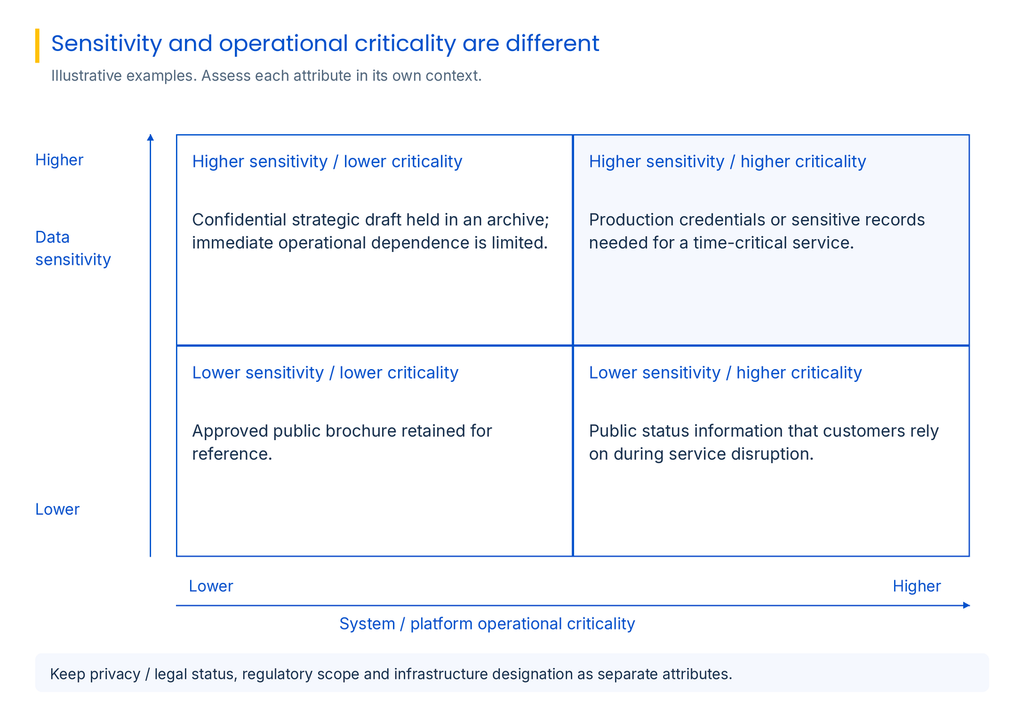
Record confidentiality, integrity and availability requirements. A public status page may contain no confidential information while still requiring protection against unauthorized changes and timely restoration. A confidential design document may need strict disclosure controls without supporting a time-critical operation.
Keep privacy status, contractual restrictions and regulatory applicability as additional attributes. Personal data does not automatically belong in one universal tier. Its sensitivity, context and applicable obligations determine the safeguards.
The four labels below describe confidentiality. Integrity requirements, recovery needs and infrastructure designation remain separate so a low confidentiality label cannot erase an important operational dependency.
Choose labels with explicit handling rules
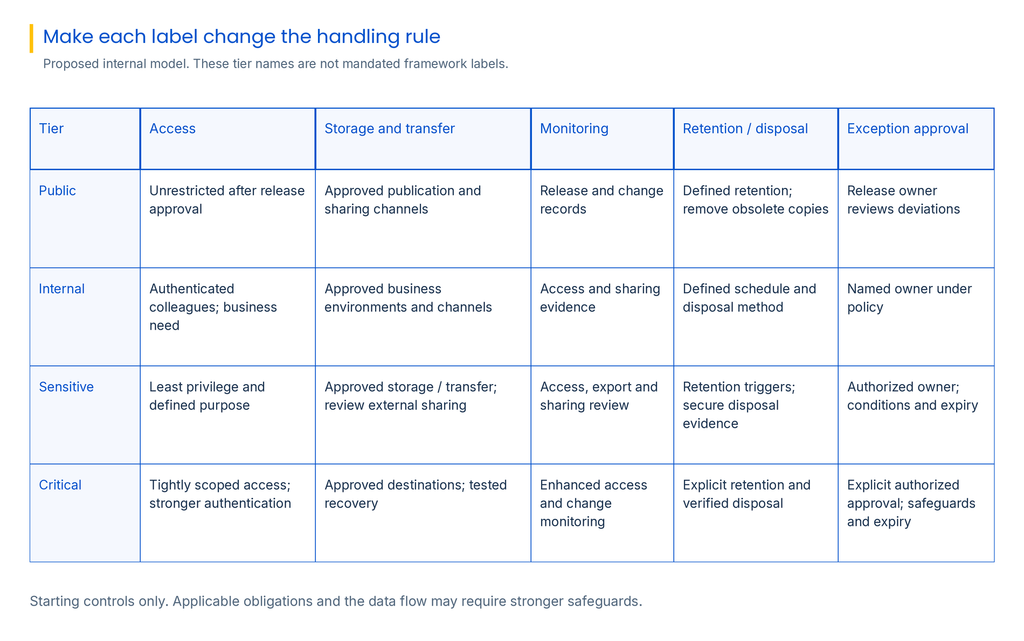
Public information is approved for unrestricted disclosure. Internal information is intended for routine authorized business use. Confidential information could cause material harm if disclosed without authorization. Restricted information requires the strongest disclosure controls because exposure could cause severe harm, such as revealing authentication secrets or particularly sensitive records.
These names are an internal model, not prescribed labels for every framework. Use established organizational terminology where it already supports clear decisions.
Apply baseline controls across tiers. Protect management access, validate approved publication, maintain integrity and define retention and disposal. Set encryption requirements through the security standard, including encryption in transit for business systems and at rest for nonpublic datasets, with controlled exceptions.
For Internal data, require approved storage and authenticated access; sharing outside the organization needs an approved business route. Confidential data requires least-privilege access, approved encrypted transfer and owner approval for external recipients. Restricted data needs explicitly authorized recipients and destinations, stronger authentication, monitored access and restricted export capabilities.
The policy must specify who can authorize exceptions, their duration and compensating safeguards. Approval cannot waive binding obligations. Retention follows purpose, legal requirements and records schedules, rather than increasing automatically with confidentiality.
Follow copies and transformations
Start with high-consequence domains such as customer records, employee information, intellectual property and authentication material. Identify the owner, source, purpose, processing locations, known copies, external recipients and retention trigger.
Copies inherit the source classification unless an authorized review establishes a different requirement. Removing a name may leave identifiers or combinations that identify a person. Masking and pseudonymization do not automatically make data public or anonymous.
Aggregation can also increase sensitivity. A collection of individually harmless records may reveal customer behavior or confidential business patterns. Reassess derived outputs before changing their handling.
Labels may not survive CSV exports, screenshots, APIs or transfers between applications. Define an alternative control where metadata cannot travel, such as an approved destination restriction and a recorded handling instruction. Test that boundary explicitly, including destinations outside the source application’s label-enforcement coverage.
A support export needs a safer destination
This fictional example illustrates the policy in use. It does not describe a SPOG customer or a measured incident.
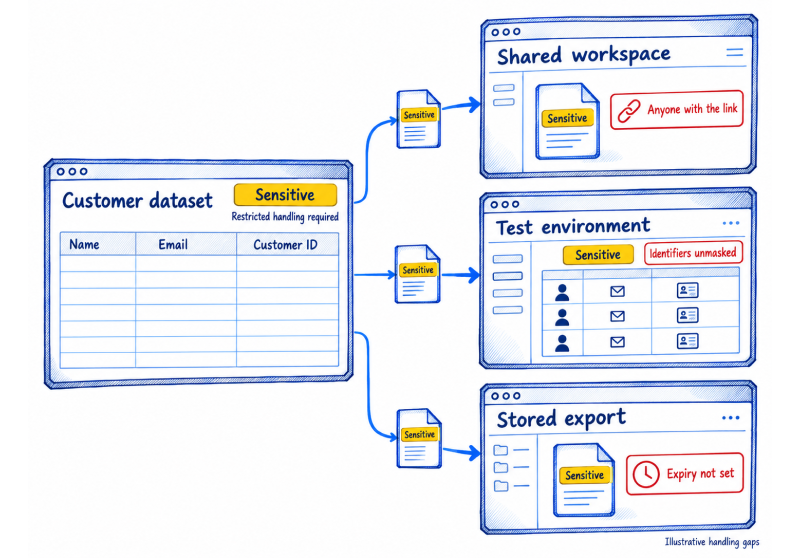
A support team prepares a troubleshooting export from a Confidential customer dataset. The export contains email addresses and transaction references. A developer proposes placing a copy in a test environment. Review finds that the intended collaboration workspace permits guest sharing and the test environment does not need identifiable customer records.
The data owner declines both destinations for the original export. Support uses an approved protected workspace with named recipients and a defined deletion date. Engineering creates a synthetic test dataset that reproduces the relevant transaction structure without customer identifiers or copied free-text content.
Verification checks that a guest account cannot access the support export, confirms the authorized recipients and tests expiry behavior. The team checks application recovery and version-history settings so removing the visible file is not mistaken for complete erasure. Where backup copies persist, the retention schedule and restoration procedures address their continued protection and eventual expiry.
The reviewer records the transfer decision, access test and disposal checks. The synthetic dataset receives its own classification review. The production source remains Confidential; the controlled transformation allows testing without distributing the customer export.
Assign classification decisions and review triggers
The business data owner approves classification and permitted use. Technical custodians implement storage, access and disposal controls. Security maintains minimum protection requirements; privacy, legal and records teams determine obligations within their remit. Users follow handling instructions and report incorrect labels.
For shared datasets, name one accountable owner and identify the custodians. Train people using actual decisions: sending an attachment, exporting a report or entering information into an AI assistant. Unclassified information should follow a defined protective default pending review.
Review classifications when purpose, content, recipients, systems or obligations change. A downgrade needs documented justification and approval. Reclassification must address existing copies and controls, not merely update the source label.
Map the data classification policy to applicable requirements
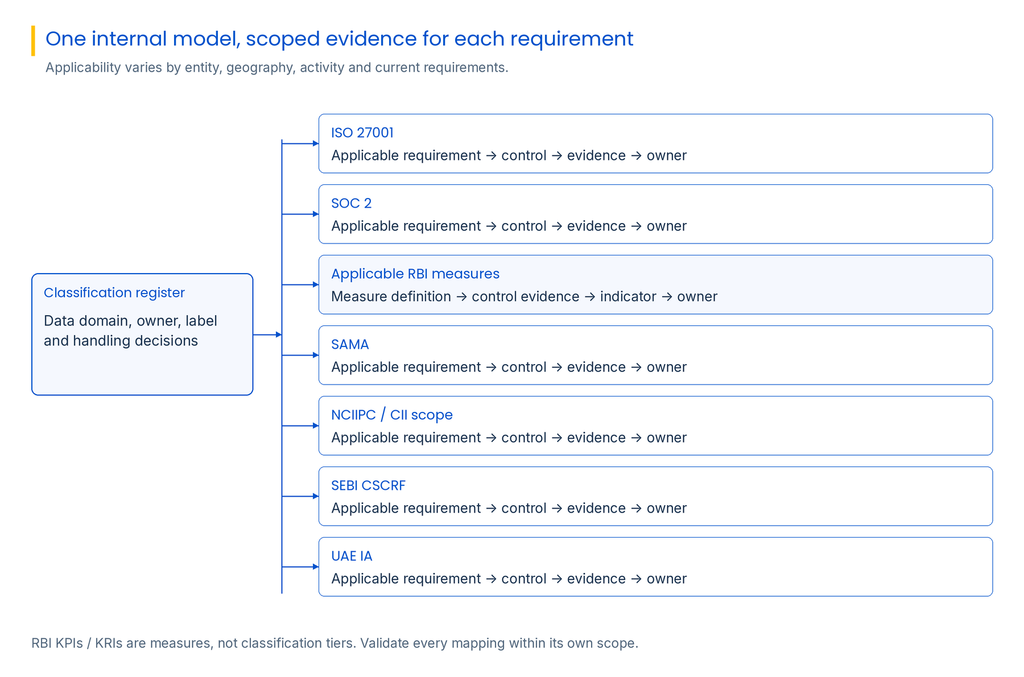
One internal model can support several assurance needs. For each mapping, record the applicable instrument, entity scope, relevant requirement, implementing control and evidence. The following examples guide that work; they are not a complete compliance crosswalk.
ISO 27001: Connect the classification approach to information security risk treatment and handling controls within the ISMS scope. ISO/IEC 27001:2022 remains the published edition, with its 2024 amendment. Your organization defines its labels and documents how protection needs are addressed.
SOC 2: Map handling controls to the system description, commitments and relevant Trust Services Criteria. Where confidentiality is included, evidence should support protection and disposal of information designated confidential. SOC 2 is an attestation engagement, not certification of a label scheme.
SAMA: For applicable member organizations, Cyber Security Framework section 3.3.3 includes ownership, custodianship, classification, labeling and handling in asset management. Section 3.3.6 links application data protection to the agreed classification scheme. Map owner records and application restrictions accordingly.
RBI KPIs and KRIs: Treat indicators as measures, not classification labels. Define the applicable RBI direction separately. Suggested internal measures include owner coverage, overdue reviews and failed disposal checks; these examples are not prescribed RBI thresholds.
NCIIPC: Where critical information infrastructure requirements apply, retain infrastructure designation separately from confidentiality. Connect relevant information handling to the assets and operations within that scope.
SEBI CSCRF: For in-scope regulated entities, map the classification register, protection controls and evidence to the applicable CSCRF requirements and clarifications, retaining the entity category and requirement version.
UAE IA: Map information handling and supporting controls to the applicable UAE Information Assurance requirements and organizational scope. A shared internal label does not establish equivalence between jurisdictions.
Test handling rather than label presence
Sample a data flow from creation through sharing and disposal. Inspect an authorized access and a denied attempt. Check whether export restrictions work, whether transformed copies retain sensitive content and whether disposal covers relevant versions and recovery locations.
Review overdue classifications, unexplained downgrades, unauthorized shares and failed disposal tests with the responsible owners. Record both the failed rule and the corrective action. A large number of labels says little about protection without these checks.
SPOG’s GRC solution connects requirements, controls, operational evidence and accountability. Its Continuous Control Monitoring solution supports coverage and effectiveness assessment and revalidation. These capabilities can support oversight where relevant evidence is connected; data owners still decide classification, and technical controls must enforce handling.
A useful data classification policy lets a support analyst choose an acceptable destination and lets a reviewer verify the result. Expand the inventory after those decisions work for a representative flow.
Frequently asked questions
It defines information categories, decision responsibilities and handling rules across the data lifecycle.
Use the smallest workable set. Public, Internal, Confidential and Restricted are one possible model.
The business data owner approves classification with security, privacy and records advice where needed.
No. Intellectual property can be confidential without identifying anyone; personal data also requires context-specific protection.
No. Publication approval, integrity, administrative access and operational recovery may still matter.
Normally yes, until an approved review justifies different handling after transformation or changed context.
Only after checking remaining content, re-identification risk and obligations. Masking alone does not establish anonymity.
Apply a documented protective default and route it to an owner for classification.
Review material changes in content, purpose, recipients or obligations. Document approvals and address existing copies.
GRC connects requirements, ownership and control evidence. Data owners determine labels, while technical systems enforce the handling rules.
With 8.5+ years in B2B SaaS, I’ve led demand generation and GTM initiatives across global markets (US, UK, Europe, Africa), helping companies move from fragmented marketing efforts to structured, revenue-focused growth engines.