Continuous Control Monitoring
Security Questionnaires: Respond with Accurate, Verifiable Answers
Security questionnaires help buyers understand how a supplier protects the data, systems and services involved in a proposed...
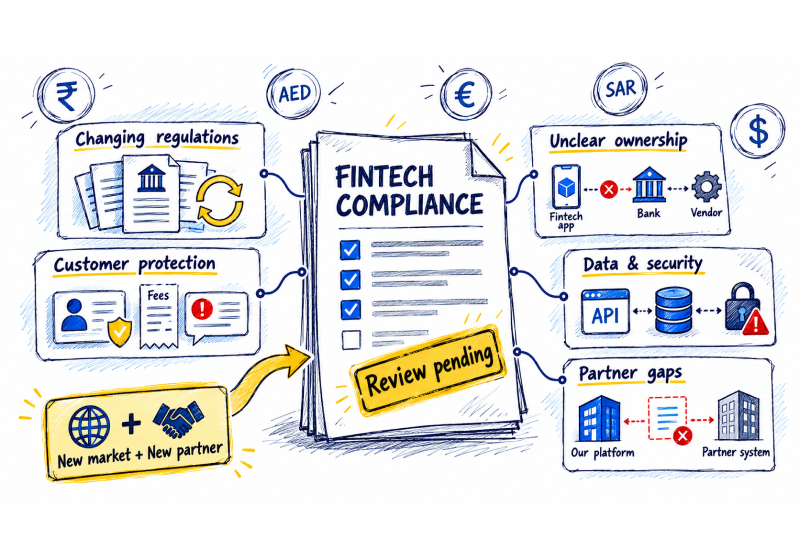
A fintech product enters a new market or adds a partner, but its compliance map still reflects an earlier operating model. The gap is often a mismatch between what the product now does, which entity performs each activity, and who can show that required controls work.
A useful fintech compliance program starts with activity and customer journey. It makes the regulated role, control owner, partner boundary and evidence path visible wherever money, data or a customer decision moves.
“Fintech” describes a broad market, not a single regulated activity. A company may provide a payment interface, originate credit through a regulated lender, hold customer funds, arrange insurance, process investment instructions, or supply technology to a financial institution. Those roles do not automatically carry the same legal duties. Applicability depends on jurisdiction, product design, legal entities, contractual arrangements and the actual flow of funds and decisions. A compliance inventory that starts and ends with the company name will miss those distinctions.
That boundary is more operational than semantic. In India, the Reserve Bank of India’s Digital Lending Directions, 2025 apply to specified regulated entities and set requirements for their arrangements with Lending Service Providers (LSPs). They call for clear contractual allocation of roles, due diligence, periodic review and monitoring; outsourcing does not remove the regulated entity’s responsibility. In the European Union, the Digital Operational Resilience Act (DORA) has applied to in-scope financial entities since 17 January 2025 and includes a register of ICT third-party arrangements. These are jurisdiction- and entity-specific examples, not a universal checklist for every fintech.
This view prevents teams from assuming a partner contract transfers accountability or assigning regulated-entity obligations to a technology provider without checking the applicable rules. Ask who performs each activity, under whose authority, and what must be controlled or evidenced.
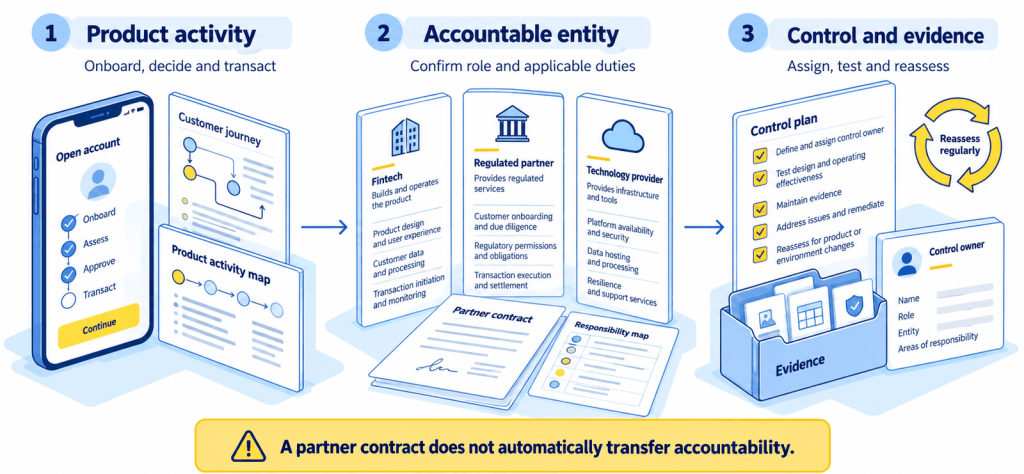
Map the actual product before mapping laws to controls. Follow a customer from first contact through onboarding, decision, funds movement, account management, complaints and exit. Add the systems and partners at each stage; the app is not necessarily the legal or operational boundary.
At each step, capture four things:
This is an operating map, not a legal opinion. The accountable compliance function or counsel determines applicability; the map gives product, engineering, security and operations a shared interpretation.
Test the handoffs where one team assumes another has completed a control. That is where a policy library often provides little assurance.
Where customer due diligence applies, assign who collects identity data, verifies it, resolves exceptions, screens relevant lists and decides escalations. For anti-money laundering (AML) and counter-terrorist financing (CFT), customer identification, ongoing monitoring and suspicious-activity escalation are distinct control activities. A successful identity check does not prove that the right risk decision was made or alerts were resolved.
The Financial Action Task Force’s 2025 update on virtual assets and virtual asset service providers (VASPs) notes gaps in licensing, identifying VASP activity and managing offshore exposure. Digital-asset fintechs should establish where activity occurs and which entity controls it; do not project virtual-asset rules onto unrelated products.
Check what customers see at decision points: prices, fees, repayment terms, eligibility, limitations and complaint routes. If an interface presents multiple offers, define who controls ranking logic, how changes are approved and how the displayed choice can be reconstructed later.
The RBI’s 2025 Digital Lending Directions provide a current example for covered Indian lending arrangements: where multiple lenders’ offers are presented, the directions set expectations for transparent comparison and unbiased presentation. That requirement is specific to the stated context. The control lesson is to test the live journey and retain evidence of what customers actually saw, not only a policy requiring disclosure review.
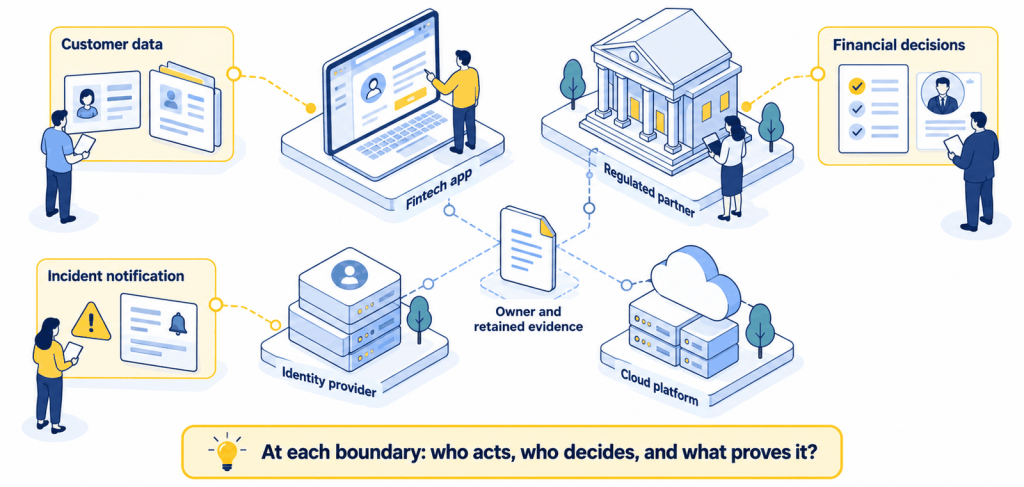
Fintech products rely on identity systems, APIs, cloud infrastructure, payment rails and data processors. Define each dependency’s role, access boundaries, incident path, recovery responsibility and exit plan. A questionnaire cannot show how a dependency is configured in your environment or whether recovery works.
DORA’s register requirement is a useful reminder for in-scope EU financial entities to maintain a structured view of contractual ICT arrangements. It does not make every fintech or every supplier automatically subject to DORA. For cybersecurity governance, map the entity’s applicable duties to the systems and arrangements it relies on, then test the control outcomes that matter: access, change management, monitoring, incident escalation, backup and restoration.
An annual review can miss changes such as a new market, underwriting model, distribution partner, data use or critical workload. Set triggers for compliance review before launch or contract change. Ask what activity changed, which entities and jurisdictions are affected, what interpretation needs review, which controls or disclosures change, and what proves readiness.
Keep records proportionate: a small change may need an owner and approval, while a new credit flow may need legal interpretation, partner review, updated disclosures, control tests and a launch decision. Record conditions so accepted risk is distinguishable from an overlooked issue.
This makes regulatory change operational without pretending that software can interpret law automatically. A governance platform can help connect mapped requirements, controls, evidence, owners and remediation work. SPOG.AI’s GRC solution supports shared visibility across framework alignment, accountability, evidence and remediation. Its Continuous Control Monitoring solution can support assessment of mapped cybersecurity controls using current operational evidence. Neither replaces legal advice, financial-crime monitoring, or a regulated entity’s own accountability.
A useful compliance review informs a decision before customers or partners experience a failure. Product leaders need launch conditions, deviation authority and re-review triggers. Security and engineering need the required control state and proof. Compliance needs a traceable link from requirement to activity and accountable entity.
Start with a journey that crosses an organizational boundary. Document roles, requirements, controls, evidence and change triggers; validate it with compliance and workflow owners. Reuse it at the next material product or partner change. Fintech compliance is more durable when teams can see responsibility and test handoffs as the operating model shifts.


Security questionnaires help buyers understand how a supplier protects the data, systems and services involved in a proposed...

A vendor cybersecurity inquiry should establish what the supplier will do, which data and systems it can access,...

A vendor management policy sets the rules for approving suppliers, accepting exceptions and responding when relationships change. This...