Continuous Control Monitoring
Security Questionnaires: Respond with Accurate, Verifiable Answers
Security questionnaires help buyers understand how a supplier protects the data, systems and services involved in a proposed...
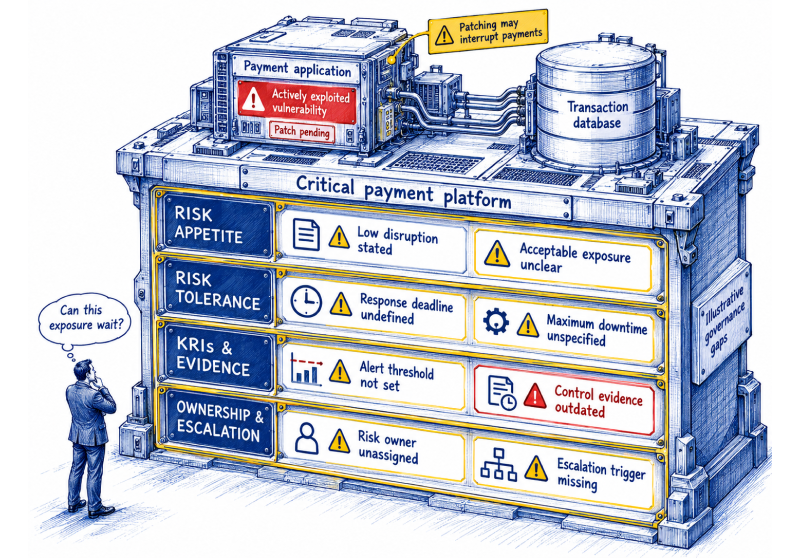
A critical vulnerability is discovered in an enterprise application. Security recommends urgent action, while operations warns that patching could interrupt service. Should leadership accept the exposure temporarily? The answer requires agreed risk limits, not just a severity score.
Risk appetite establishes that overall willingness; risk tolerance makes it actionable through specific boundaries. Alongside risk capacity and Key Risk Indicators (KRIs), both support accountable decisions.
Risk appetite is the type and amount of risk an organization is willing to accept while pursuing business objectives. It informs decisions about technology adoption, cybersecurity investment, third parties, and operational resilience.
A bank, for example, may have a low appetite for risks that compromise customer information or disrupt payments, while accepting carefully controlled risks associated with launching digital services. Its appetite statement might say: “We maintain a low appetite for material customer-data exposure and interruption of critical services, while accepting managed risks associated with approved innovation.”
An approved, regularly reviewed statement aligns investments, security priorities, and escalation decisions.
Risk tolerance defines acceptable levels of risk or variation within a particular activity, objective, or scenario. It translates broad appetite statements into measurable operating boundaries.
For example, an organization with a low appetite for disruption might require an approved response to actively exploited critical vulnerabilities on internet-facing production systems within a specified period. Other tolerances may concern maximum service downtime, overdue control failures, critical third-party dependencies, or unresolved high-risk exceptions.
Tolerances depend on business impact and context. A vulnerability in an isolated test system may be acceptable for longer than the same weakness in a payment platform. Acceptance cannot override legal or regulatory obligations. Risk tolerance is meaningful only when teams can verify whether actual exposure remains within its limits and know when to escalate.
| Dimension | Risk appetite | Risk tolerance |
|---|---|---|
| Question | How much risk are we willing to take? | Where are the limits in this scenario? |
| Level | Strategic, enterprise-wide | Operational, activity-specific |
| Expression | Broad direction and priorities | Thresholds, conditions, or ranges |
| Ownership | Board and senior leadership | Authorized managers and risk owners |
| Example | Low appetite for payment disruption | No critical exposure beyond an approved response deadline |
Appetite sets the direction; tolerance provides the trigger for action. An organization may accept the uncertainty of cloud adoption but set strict limits for publicly exposed sensitive data and unprotected critical workloads.
Risk capacity is the maximum risk an organization can withstand without threatening essential objectives or viability. It differs from what leadership is willing to accept.
Consider a digital payments provider. Its appetite for payment disruption may be low; its tolerance may specify maximum downtime and treatment deadlines; its capacity reflects the disruption it could absorb before essential operations become unsustainable. If an actively exploited vulnerability affects payment infrastructure, leaders should evaluate all three, not just the technical severity.
Capacity includes financial resilience, operational continuity, and the ability to withstand reputational damage; strength in one does not guarantee strength in another.
Credible risk assessments underpin appetite and tolerance. Common methods include:
Missing endpoint coverage or failed access restrictions can raise residual exposure above an approved limit. Understanding inherent risk versus residual risk supports more defensible acceptance decisions.
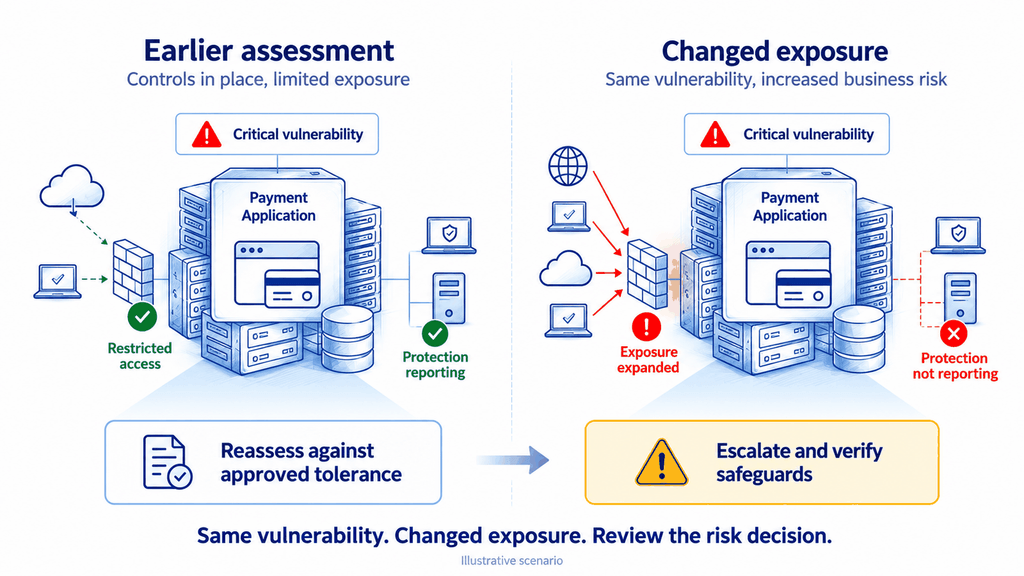
KRIs are measures that signal changes in risk exposure and show when predefined limits may be at risk. They turn risk policy into something teams can observe and act upon. Indicators include overdue critical exposures, declining control coverage, and high-risk third-party dependencies without verified safeguards.
Each KRI needs reliable data, a threshold, an owner, a review frequency, and an escalation response. Leading indicators, such as declining control coverage, support early action; lagging indicators, such as security-related downtime, measure realized consequences.
| Governance element | Illustrative rule |
|---|---|
| Appetite | Low appetite for threats to critical applications |
| Tolerance | No actively exploited critical exposure may remain without an approved treatment decision and appropriate interim safeguards beyond 24 hours |
| KRI | Count of qualifying exposures beyond that deadline |
| Monitoring | Continuous collection; daily review and event-driven escalation |
| Response | Escalate to the authorized risk owner, implement appropriate safeguards, and reassess residual risk |
The 24-hour period is illustrative, not a universal regulatory requirement. An approved treatment decision does not necessarily mean the vulnerability has been resolved or that residual risk is within tolerance.
A favorable KRI is meaningful only if asset visibility, vulnerability data, and control evidence are sufficiently complete.
KRIs track exposure; Key Performance Indicators (KPIs) track process performance. A KPI may show 95% of critical vulnerabilities treated within an SLA, while a KRI identifies one remaining actively exploited weakness on a business-critical application. Strong operational performance therefore does not guarantee acceptable residual risk. Leaders need both views.
A workable governance process follows six steps:
When patching threatens critical operations, the designated risk owner may authorize a time-bound exception with compensating safeguards. Material tolerance breaches must escalate to the appropriate authorized risk owner or governance body. Approval does not itself reduce risk or restore compliance with tolerance. Exceptions require documentation, expiry dates, and review.
Common challenges include vague appetite statements, fragmented risk data, context-free indicators, outdated control evidence, and unclear ownership. Connect thresholds to critical services, verify safeguard performance, and assign escalation responsibility. Finding counts alone cannot show which exposures exceed tolerance.
Defining appetite and approving tolerance remain governance responsibilities. Applying those decisions requires current evidence of exposures, critical assets, business dependencies, and control effectiveness.
SPOG.AI brings together signals from security and IT systems with asset and governance context through its Unified Risk and Exposure Management approach. It relates findings to affected services, evaluates supported controls, and helps prioritize material exposures.
This evidence can inform residual-risk reviews and reveal when earlier risk assumptions no longer hold. Authorized leaders remain responsible for thresholds and risk acceptance.
Explore how SPOG.AI supports risk visibility and control assurance: Book a Demo
Risk appetite defines willingness to take risk, tolerance specifies actionable limits, and capacity describes what the organization can withstand. KRIs make those boundaries observable, while reliable control evidence helps determine whether residual exposure remains acceptable. Together, clear governance and current operational context enable more consistent cyber risk decisions.


Security questionnaires help buyers understand how a supplier protects the data, systems and services involved in a proposed...

A vendor cybersecurity inquiry should establish what the supplier will do, which data and systems it can access,...

A vendor management policy sets the rules for approving suppliers, accepting exceptions and responding when relationships change. This...